
Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 day ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 matheuzsecurity/imperius
Make an Linux Kernel rootkit visible again.
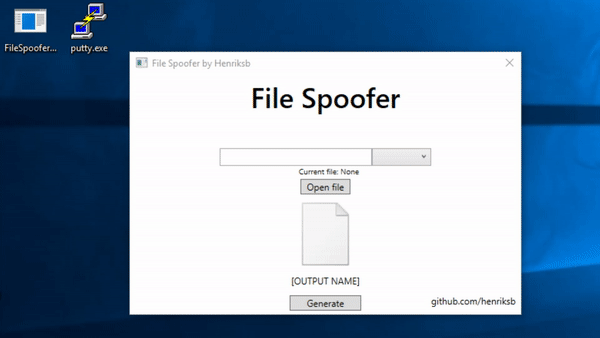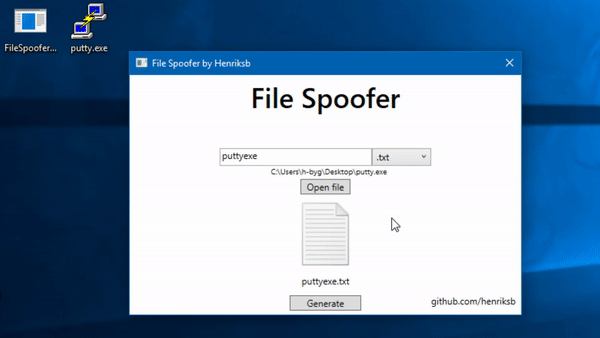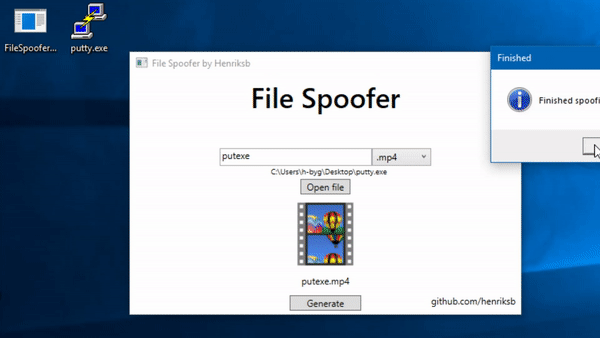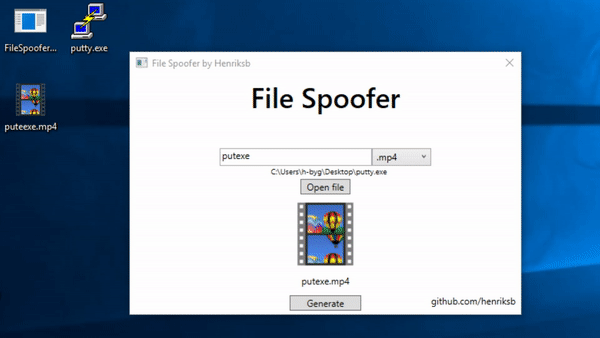 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 gmh5225/fakeenclave
Proof-of-concept that abuses Windows Enclave to implement anti-tamper and anti-cheat evasion techniques at the driver level.
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 ajayrandhawa/cryptolocker
CryptoLocker is open source files encrypt-er. Crypto is developed in Visual C++. It has features encrypt all file, lock down the system and send keys…
 demining/log4j-vulnerability
Educational analysis of the Log4Shell (CVE-2021-44228) vulnerability, detailing its exploitation in a cryptocurrency mining campaign with IoCs, MITRE…