

Apkx-Hunter
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
android-securityinformation-gatheringmachine-learning+7
94
syscallx-18113/apkx-hunterC-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
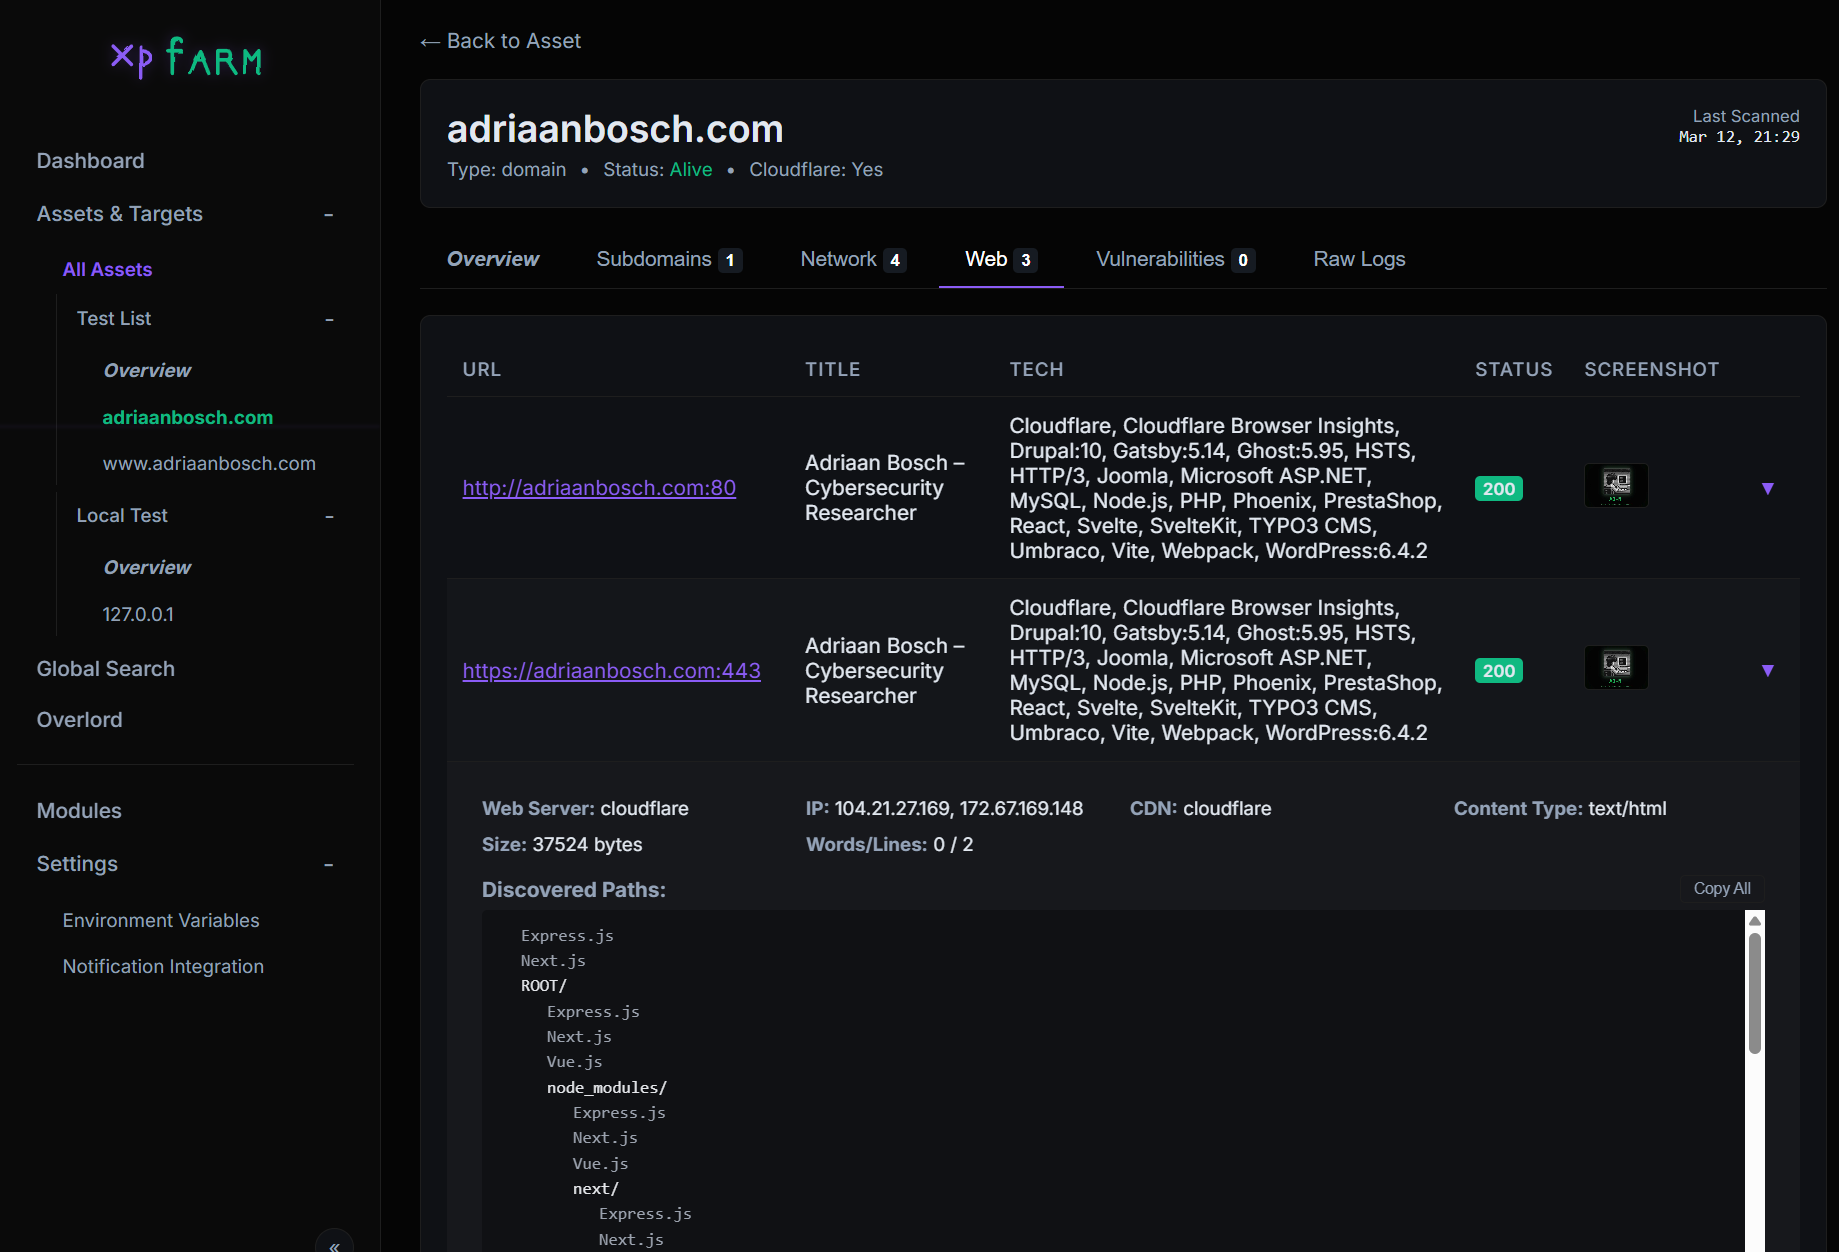 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 al0ne/linuxcheck
Linux应急处置/信息搜集/漏洞检测工具,支持基础配置/网络流量/任务计划/环境变量/用户信息/Services/bash/恶意文件/内核Rootkit/SSH/Webshell/挖矿文件/挖矿进程/供应链/服务器风险等13类70+项检查
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
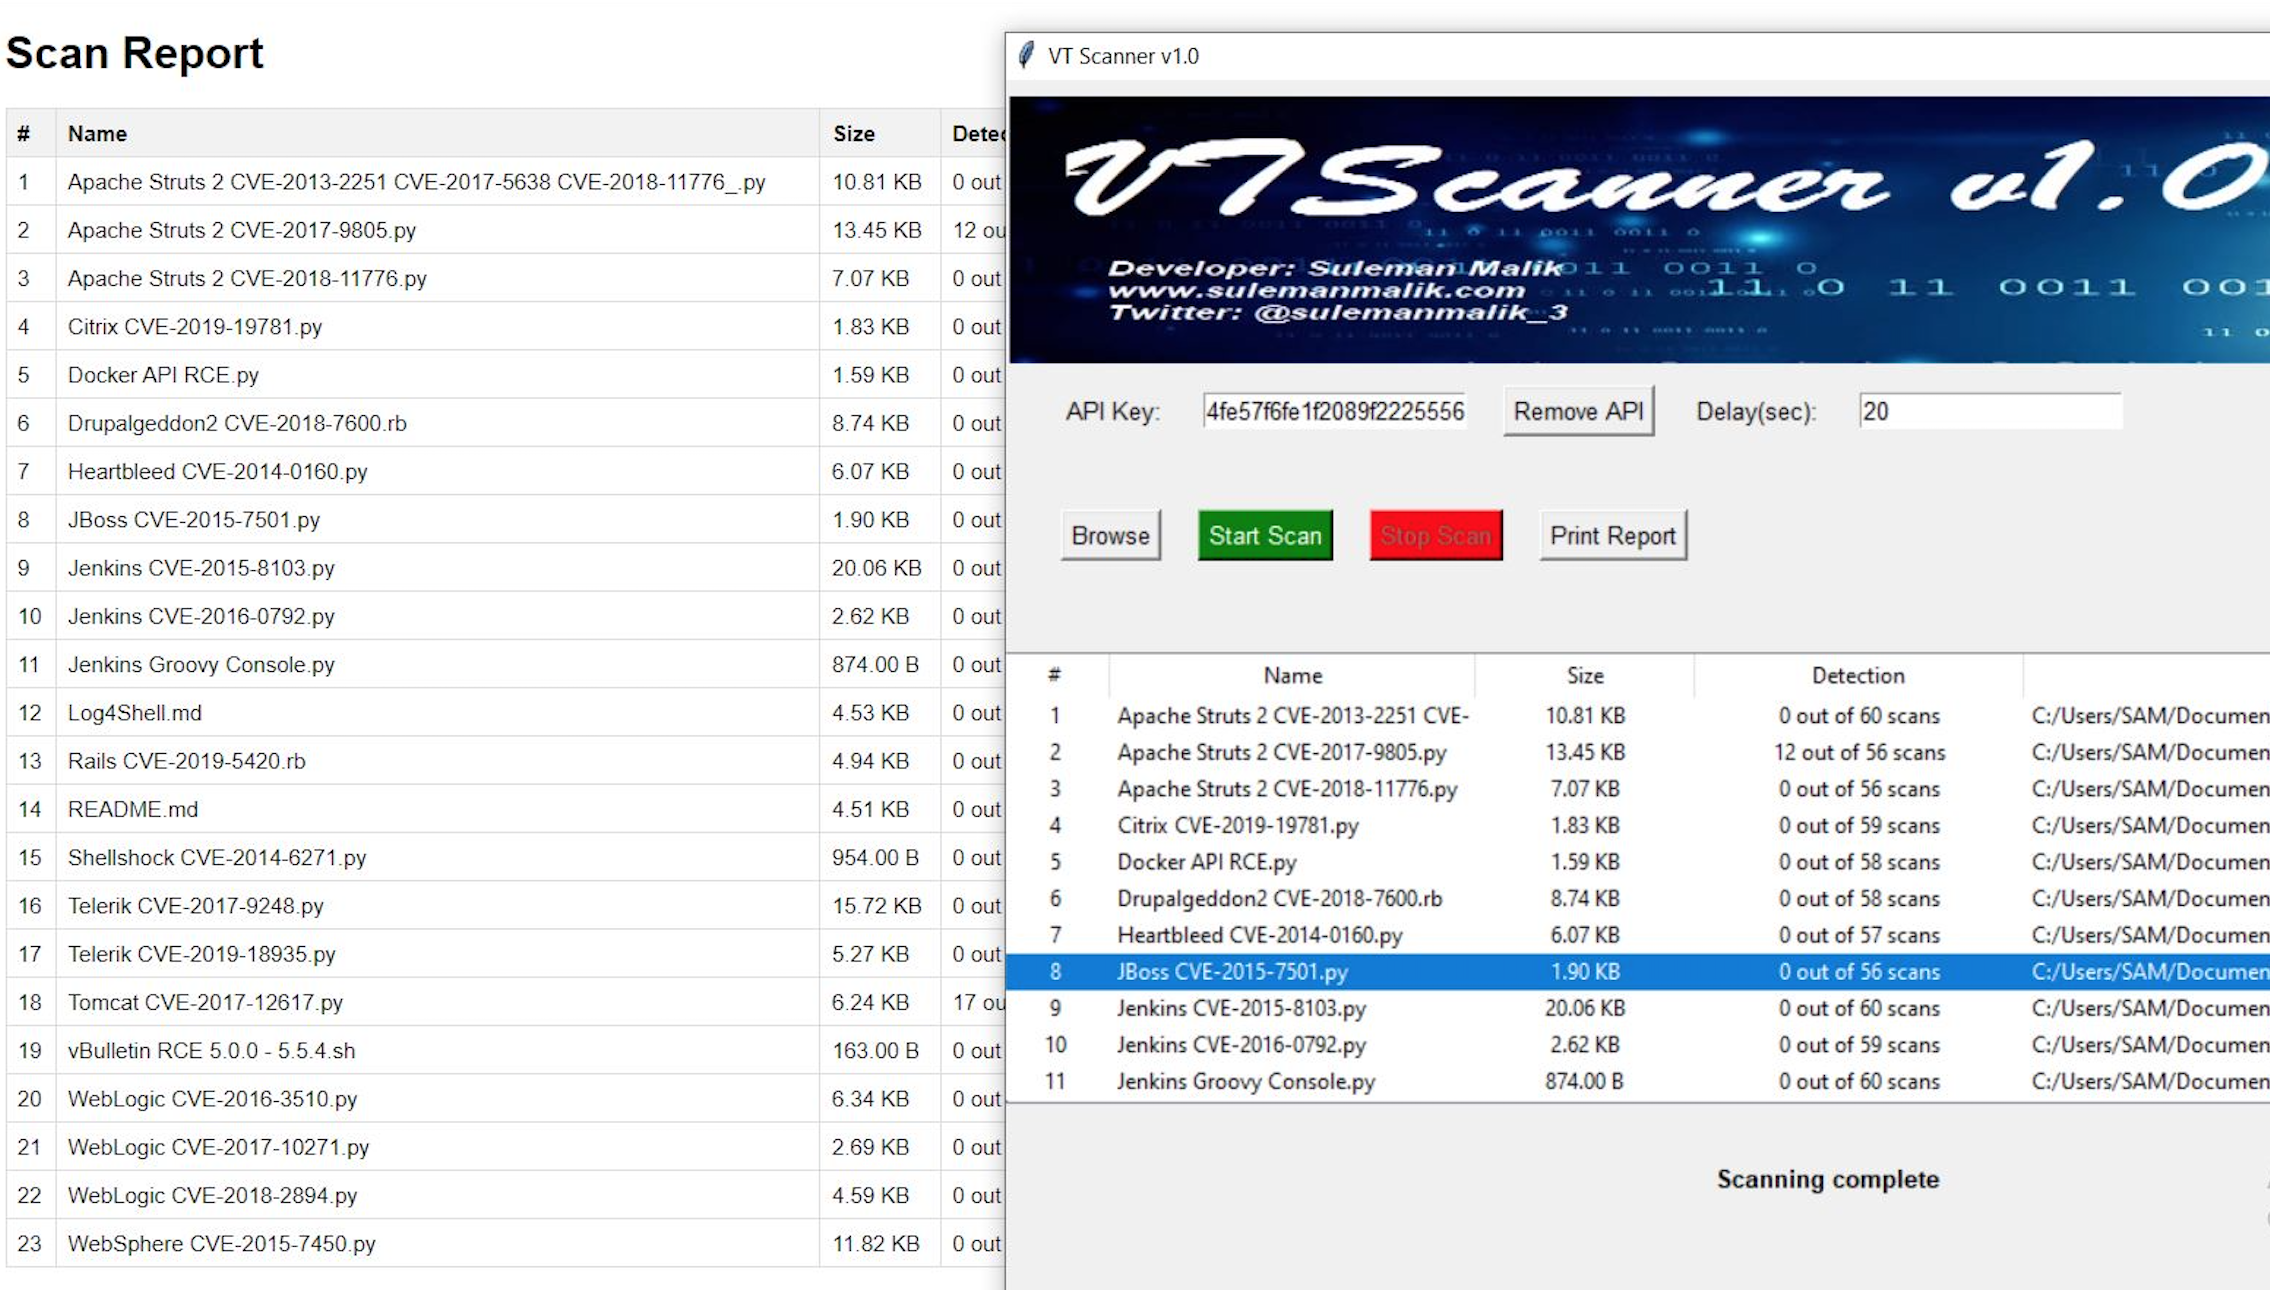 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
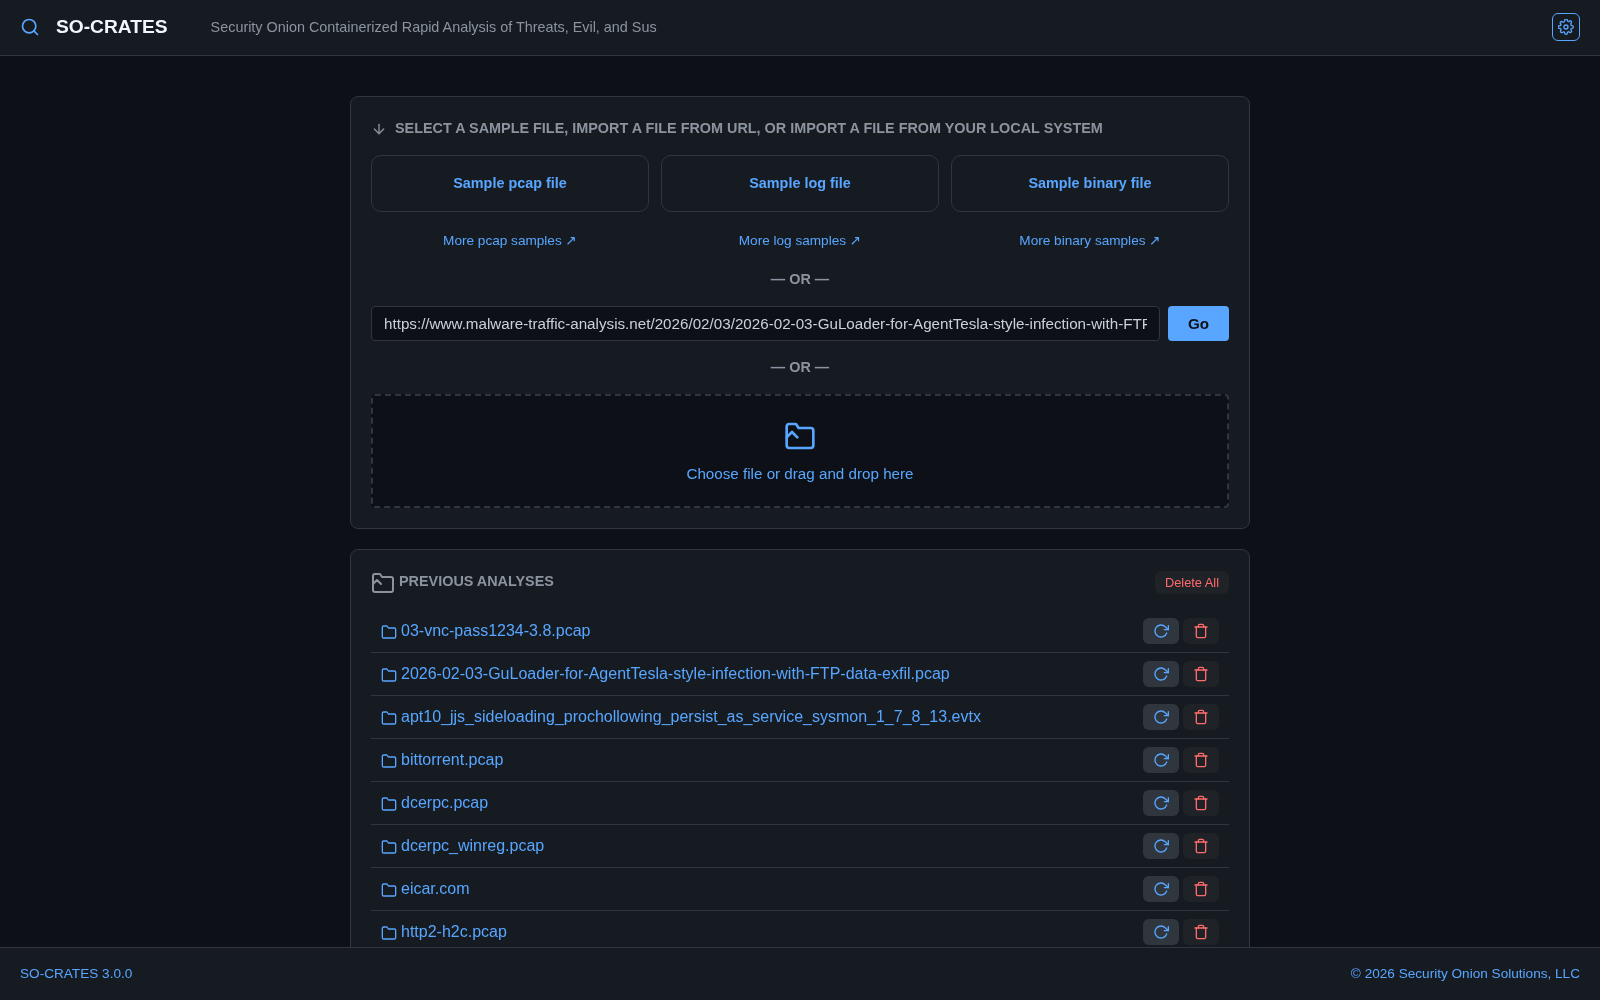 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
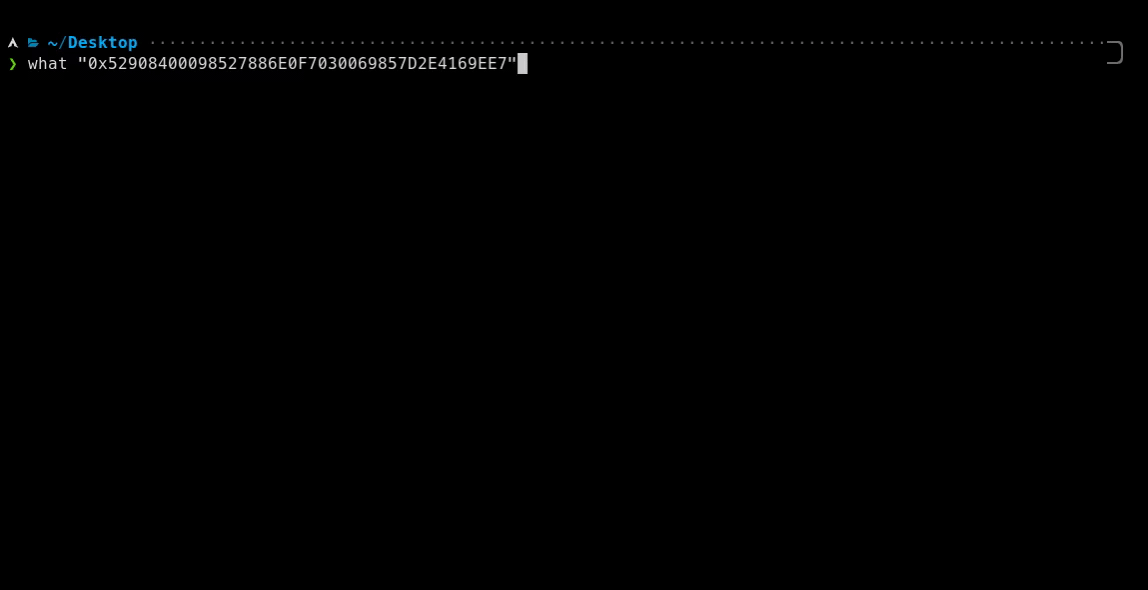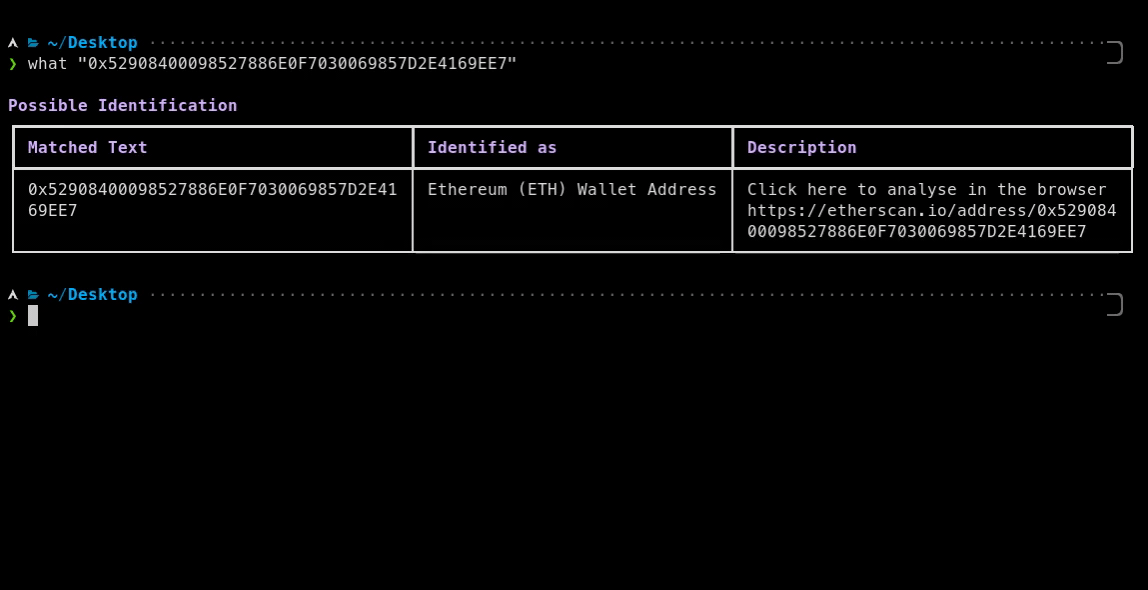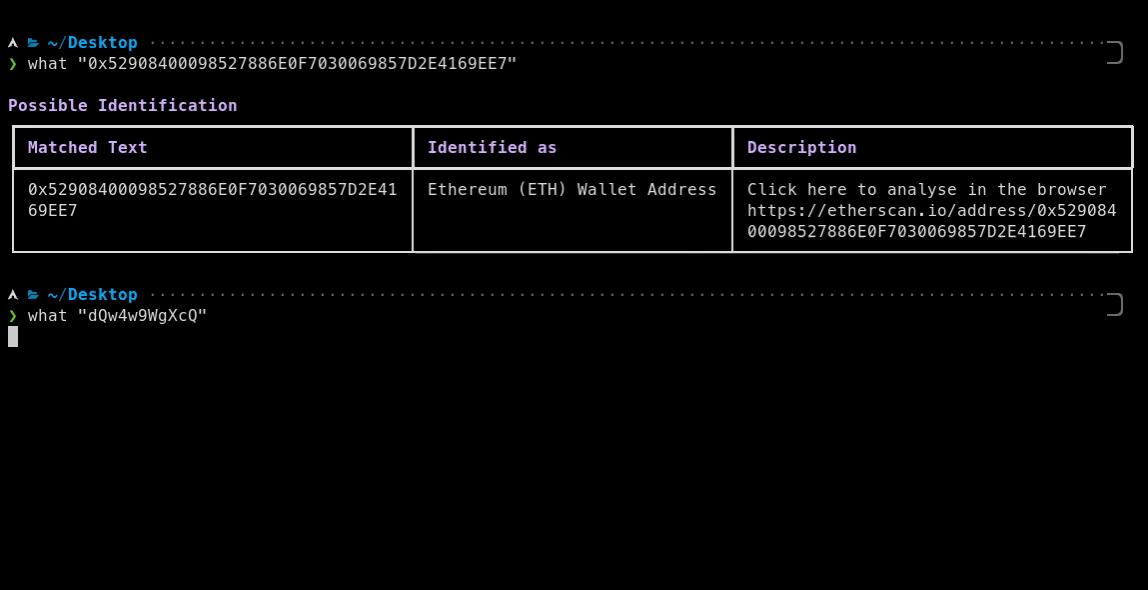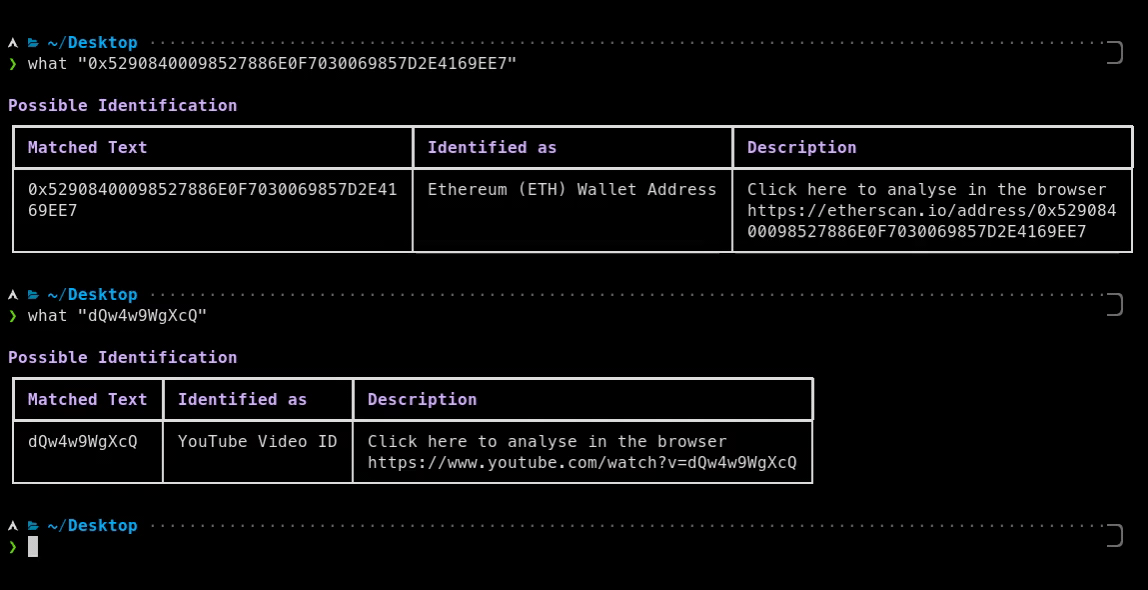 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 withsecurelabs/doublepulsar-c2-traffic-decryptor
A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
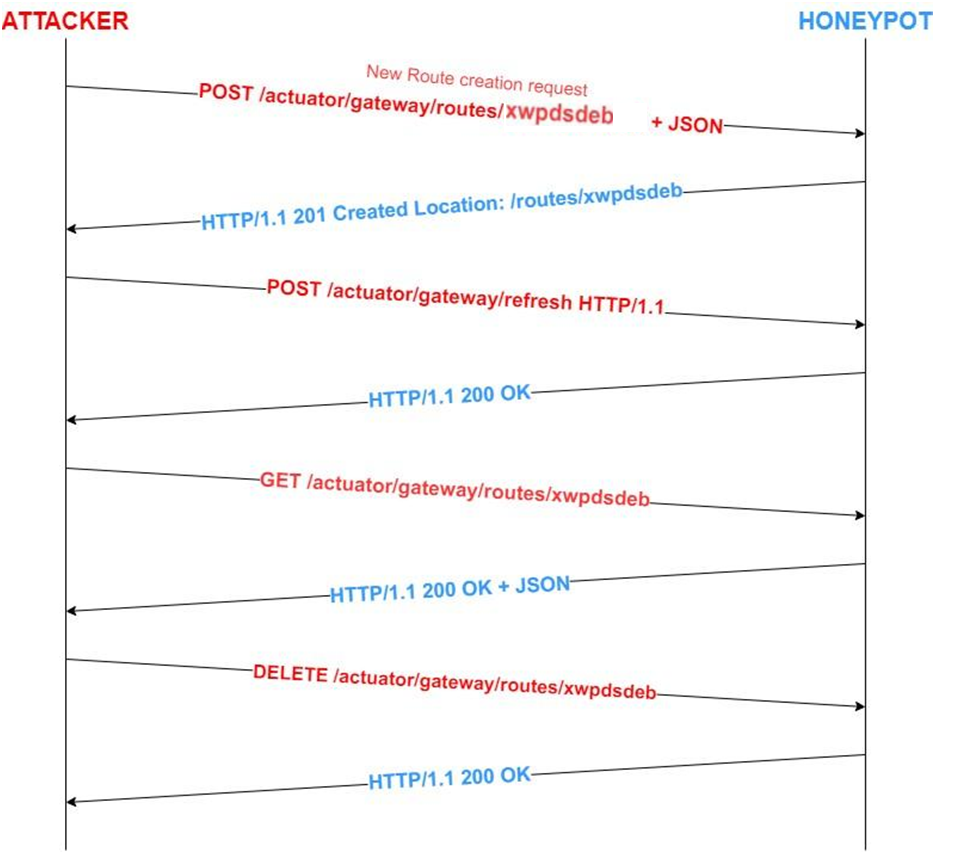 sumitpathania03/cve-2022-22947
Detailed technical analysis and proof-of-concept for CVE-2022-22947, a Spring Cloud Gateway SpEL injection leading to RCE, including step-by-step…