
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
Manalyze preview

Manalyze

GitHubjusticerage/manalyze

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

binary-analysismalware-analysisreverse-engineering+2
1.1k
1 month ago
pe-bear preview

pe-bear

GitHubhasherezade/pe-bear

Portable Executable reversing tool with a friendly GUI
binary-analysisforensicsmalware-analysis+3
3.8k17 days ago
PETriage preview

PETriage

GitHubuky007/petriage

PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.

anomaly-detectionbinary-analysisdigital-forensics+5
132 months ago
ceasta preview

ceasta

GitHubngwg/ceasta

disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…

ai-assisted-reversingbinary-analysisbinary-exploitation+6
13811 days ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1642 days ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
2.1k1 day ago
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

binary-analysisexploit-frameworksioc-management+5
1.1k11 months ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

binary-analysisexploit-frameworksmalware-analysis+2
3161 day ago
spectrIDA-Reverse_Engineering_Stack preview

spectrIDA-Reverse_Engineering_Stack

GitHubggfuchsi-oss/spectrida-reverse_engineering_stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
ai-assisted-reversingbinary-analysisctf+8
633 months ago
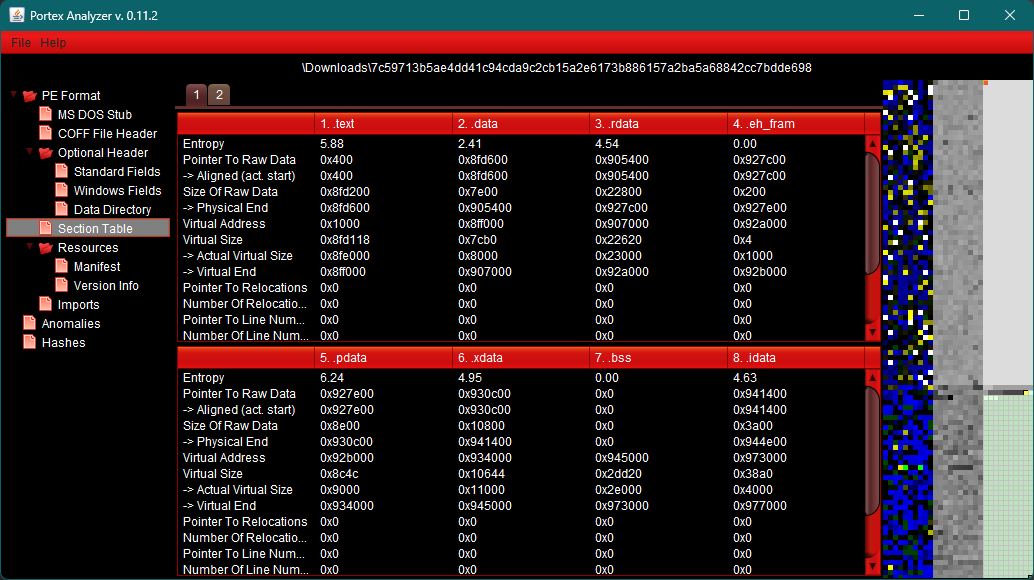
PortexAnalyzerGUI preview

PortexAnalyzerGUI

GitHubstruppigel/portexanalyzergui

Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
binary-analysisforensicshash-analysis+3
1511 year ago
telfhash preview

telfhash

GitHubtrendmicro/telfhash

Symbol hash for ELF files

binary-analysisforensicshash-analysis+1
1174 years ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

ai-assisted-reversingbinary-analysisbinary-exploitation+7
23 days ago
