Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

binary-analysisbinary-exploitationctf+8
89
25 days ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.

binary-analysisdynamic-code-analysisfirmware-analysis+3
539 days ago
Detect-CVE-2024-0762 preview

Detect-CVE-2024-0762

GitHubtadash10/detect-cve-2024-0762

Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature

firmware-analysisincident-responsemalware-analysis+3
2 years ago
workshop_firmware_reverse_engineering preview

workshop_firmware_reverse_engineering

GitHubemproof-com/workshop_firmware_reverse_engineering

Workshop on firmware reverse engineering

binary-analysiseducationembedded-systems-security+6
4510 years ago
kunglao-agent preview

kunglao-agent

GitHubamd2g2zz/kunglao-agent

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

ai-assisted-reversingandroid-securitybinary-analysis+8
314 days ago
uefi_bootkit_softlanding preview

uefi_bootkit_softlanding

GitHubares-sys/uefi_bootkit_softlanding

First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…

defensive-toolsdigital-forensicsfirmware-analysis+5
1 month ago
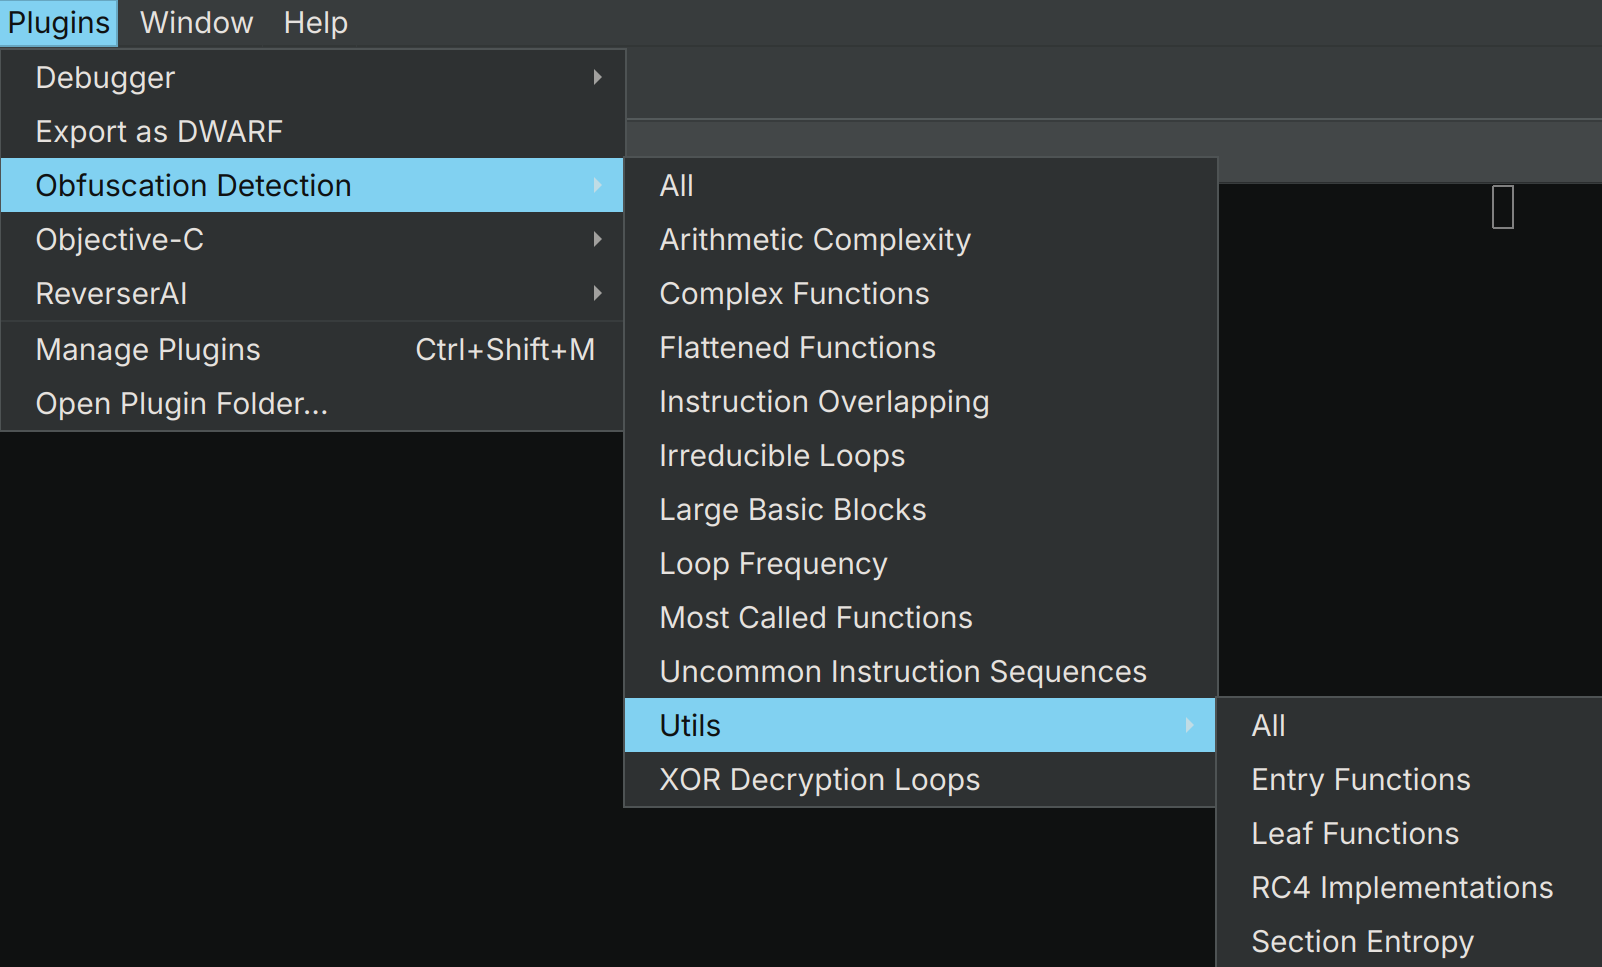
obfuscation_detection preview

obfuscation_detection

GitHubmrphrazer/obfuscation_detection

Binary Ninja plugin to identify obfuscated code and other interesting code constructs

binary-analysisfirmware-analysismalware-analysis+2
6774 months ago
idahunt preview

idahunt

GitHubnccgroup/idahunt

idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro

binary-analysisembedded-systems-securityfirmware-analysis+4
3943 years ago
telnet-iot-honeypot preview

telnet-iot-honeypot

GitHubphype/telnet-iot-honeypot

Python telnet honeypot for catching botnet binaries

iot-securitymalware-analysisnetwork-security+1
3134 years ago
kaiju preview

kaiju

GitHubcmu-sei/kaiju

CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…

binary-analysisfirmware-analysismalware-analysis+2
1476 months ago
IoT-Implant-Toolkit preview

IoT-Implant-Toolkit

GitHubarthastang/iot-implant-toolkit

Toolkit for implant attack of IoT devices

binary-analysisembedded-systems-securityexploitation+8
1358 years ago
die-in-browser preview

die-in-browser

GitHubxoreaxlmbdx/die-in-browser

Static binary analysis with Detect It Easy — 100% in your browser, no uploads.

binary-analysisfirmware-analysishash-analysis+3
702 months ago
AutoPiff preview

AutoPiff

GitHubsplintersfury/autopiff

Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…

binary-analysisexploitationfirmware-analysis+4
677 months ago
010-Editor-Template preview

010-Editor-Template

GitHubjas502n/010-editor-template

Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…

binary-analysisdata-recoverydigital-forensics+4
445 years ago
Umay preview

Umay

GitHubmucoze/umay

IoT Malware Similarity Analysis Platform

iot-securitymalware-analysisreverse-engineering+1
434 years ago
my-little-honeypot preview

my-little-honeypot

GitHubpandipanda69/my-little-honeypot

Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

command-and-controliot-securitymalware-analysis+2
179 years ago
UEFI-Security-Research-Howyar-SysReturn-NetCopy preview

UEFI-Security-Research-Howyar-SysReturn-NetCopy

GitHubthemalwareguardian/uefi-security-research-howyar-sysreturn-netcopy

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

binary-analysisembedded-systems-securityexploitation+6
212 days ago
DeadDialect preview

DeadDialect

GitHubengrbilal992/deaddialect

A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.

binary-analysiscryptographydefensive-tools+7
65 months ago
Previous12Next