Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

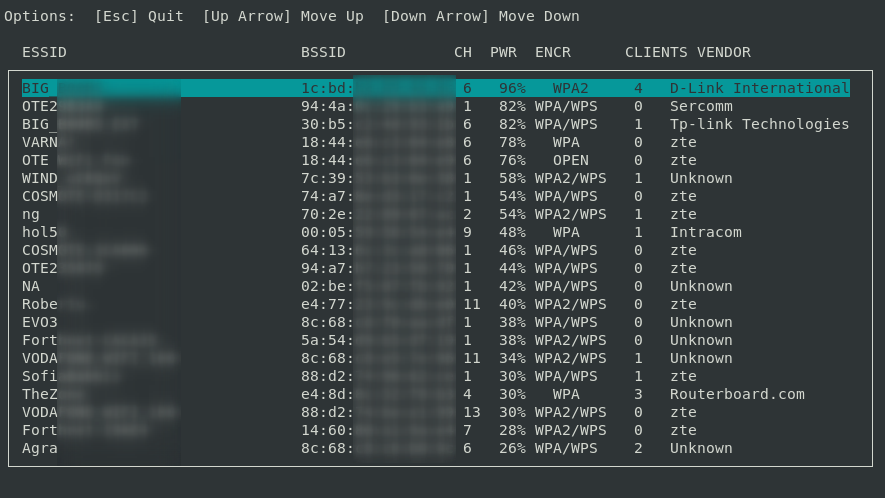
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

Proof-of-concept exploit and YARA detection rules for CVE-2025-59528, a remote code execution vulnerability in Flowise, intended for authorized…

Demonstrates Log4Shell (CVE-2021-44228) exploitation with LDAP server, malicious JNDI payload, and vulnerable Spring Boot application for security…

Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…

A tool to retrieve malware directly from the source for security researchers.

Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…

Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…

An strace-like program for the Windows 'native' API

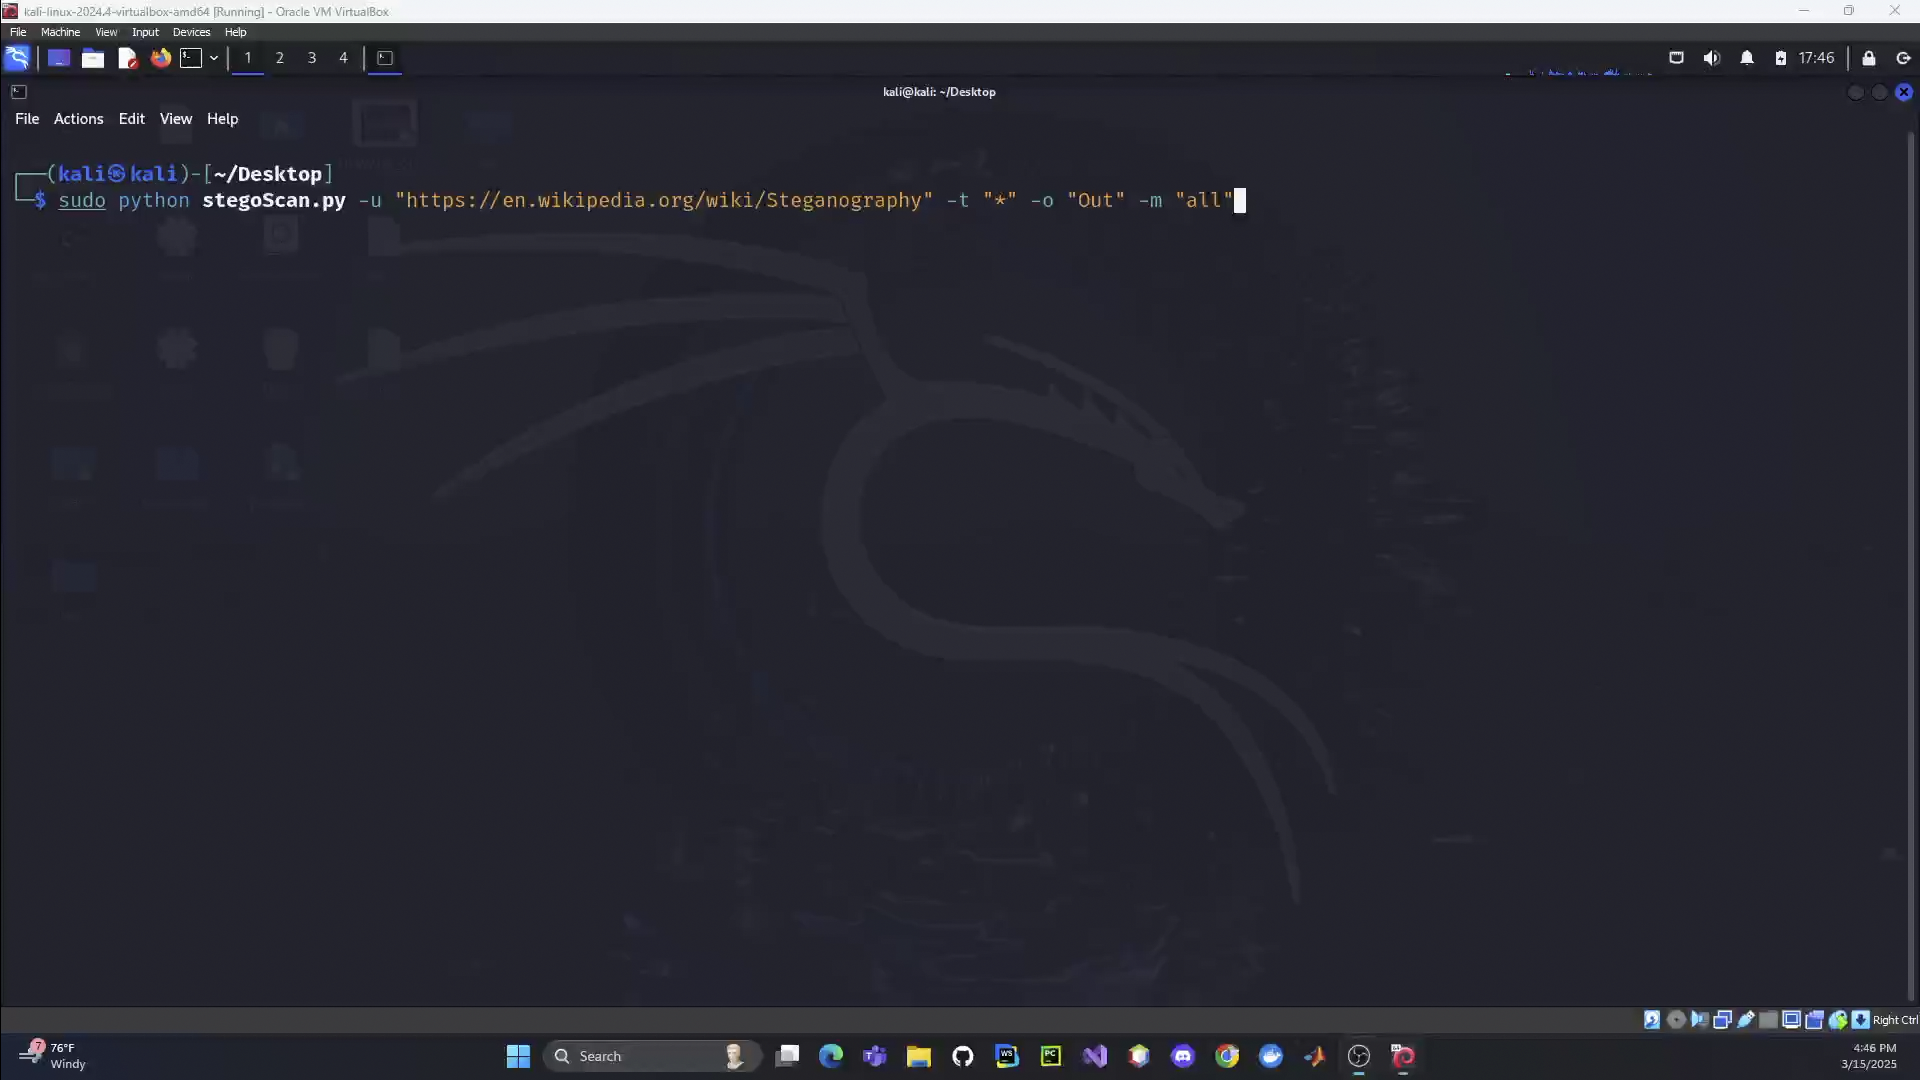
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…

Crawlector is a threat hunting framework designed for scanning websites for malicious objects.

MAPS cloud scanner and response parser for Microsoft Defender research.

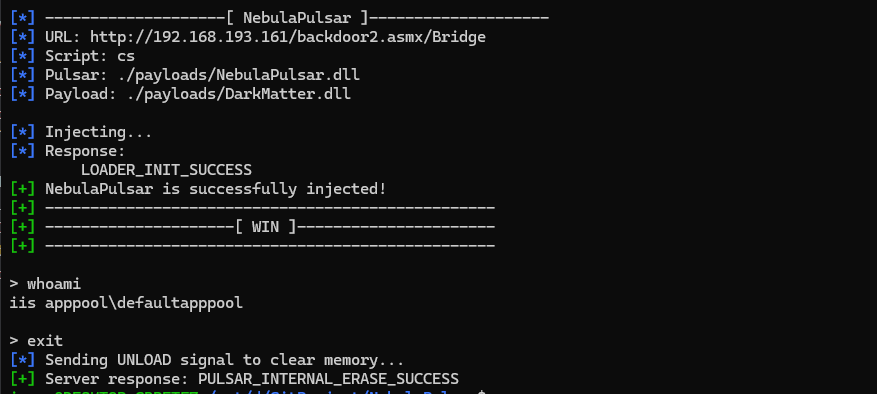
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…

An API hooking framework for intercepting and monitoring Windows applications

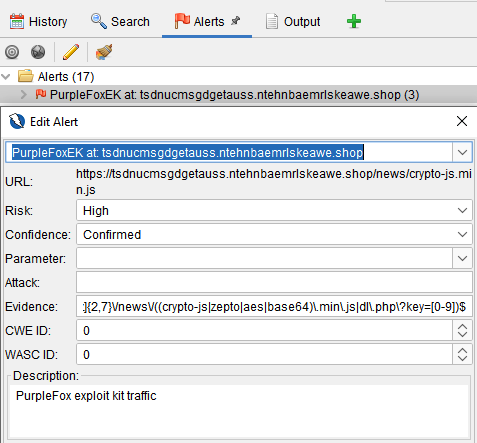
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…

Proof-of-concept exploits for CVE-2024-41453 and CVE-2024-41454 demonstrating stored XSS and malicious file upload vulnerabilities in ProcessMaker 4…

Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows

Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.