
 malwaretech/tinyxpb
Windows XP 32-Bit Bootkit
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
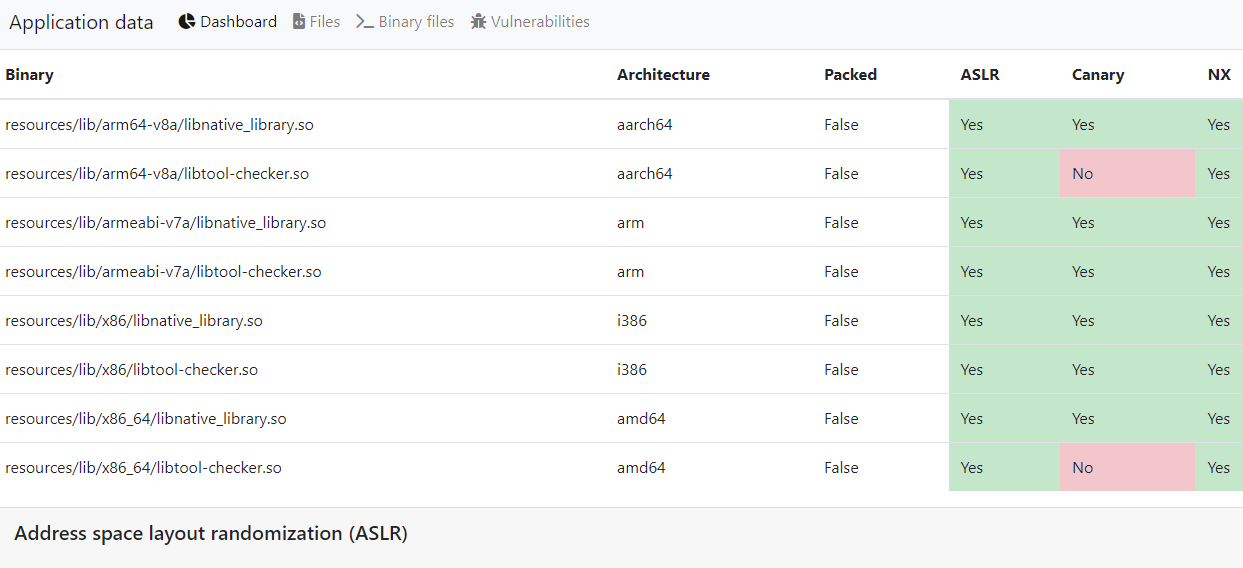 stefan2200/aparoid
Static and dynamic Android application security analysis
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
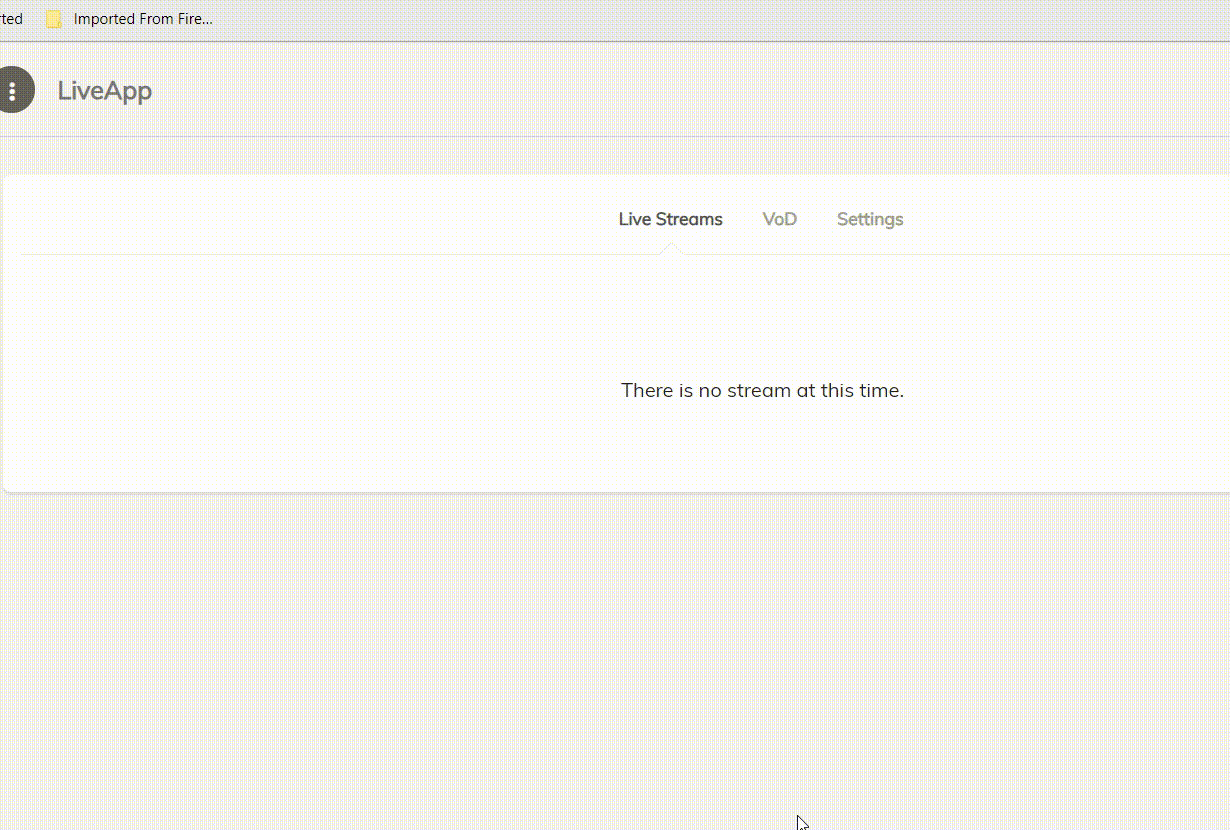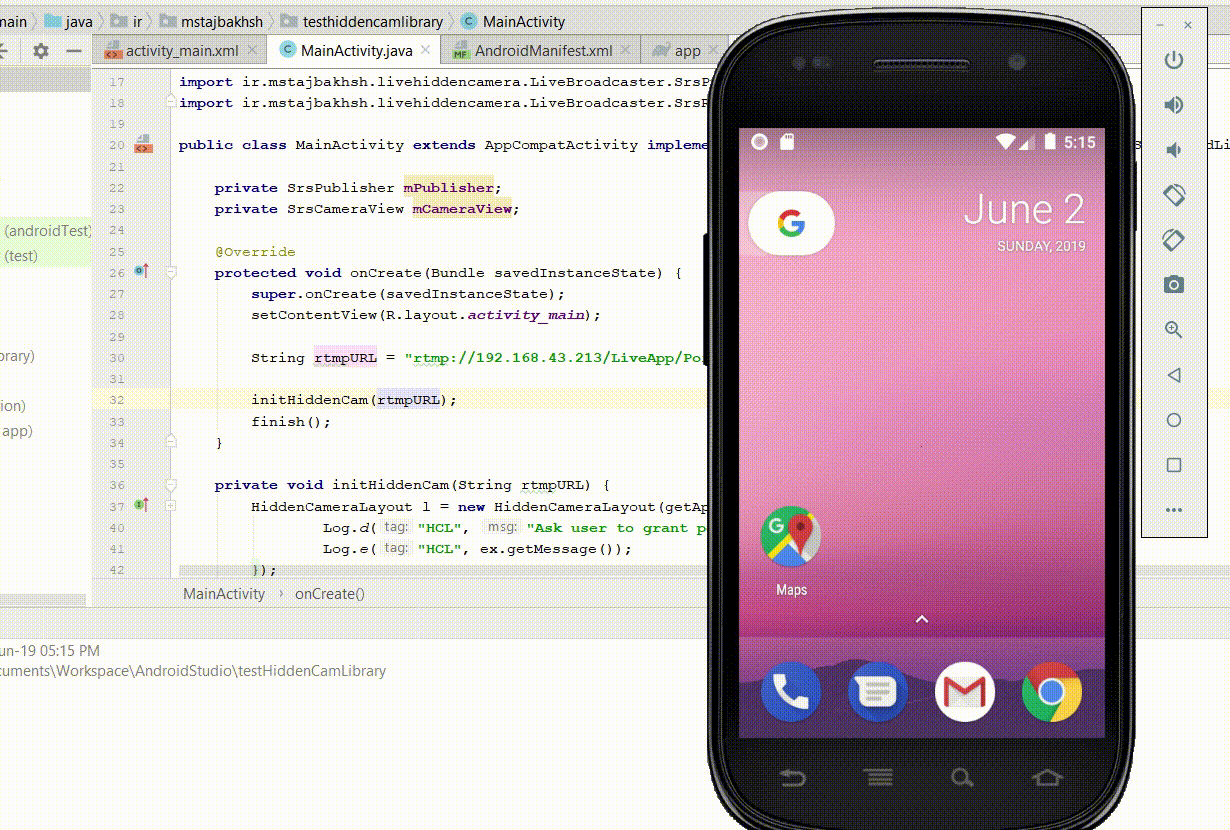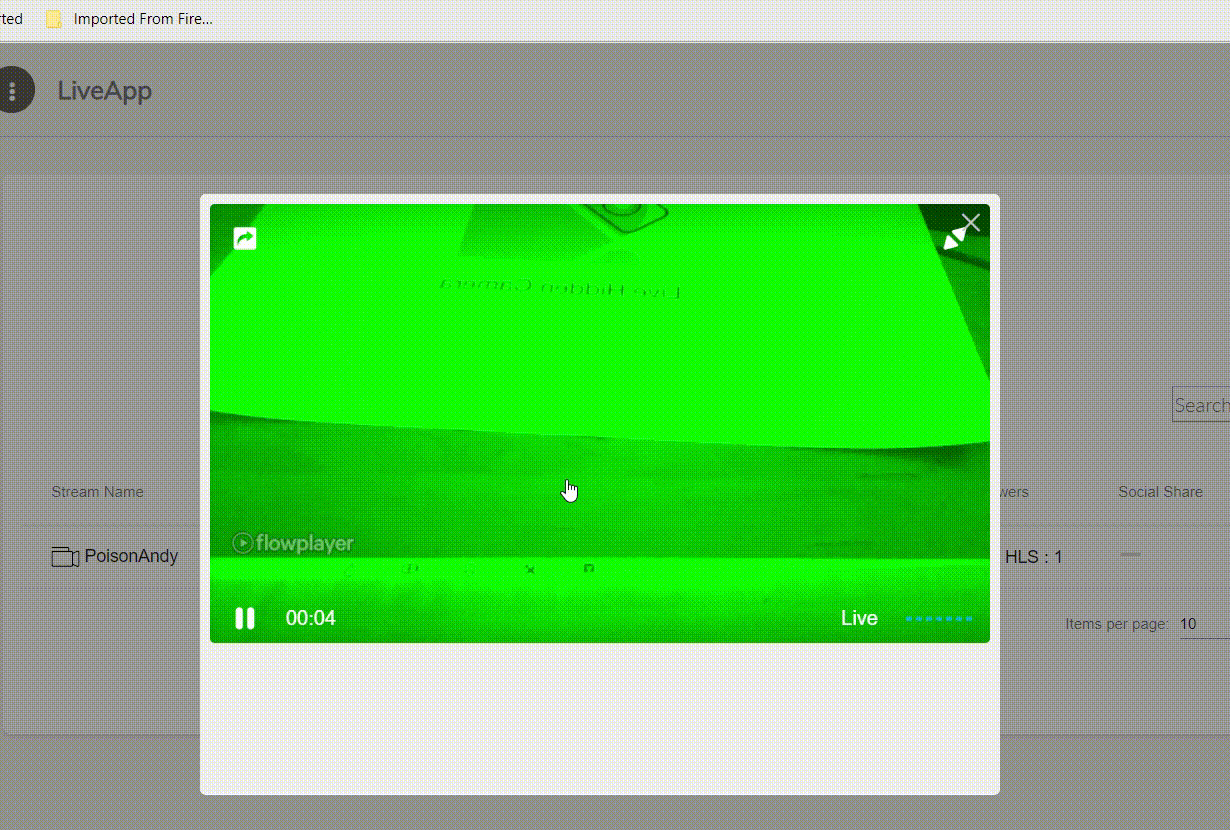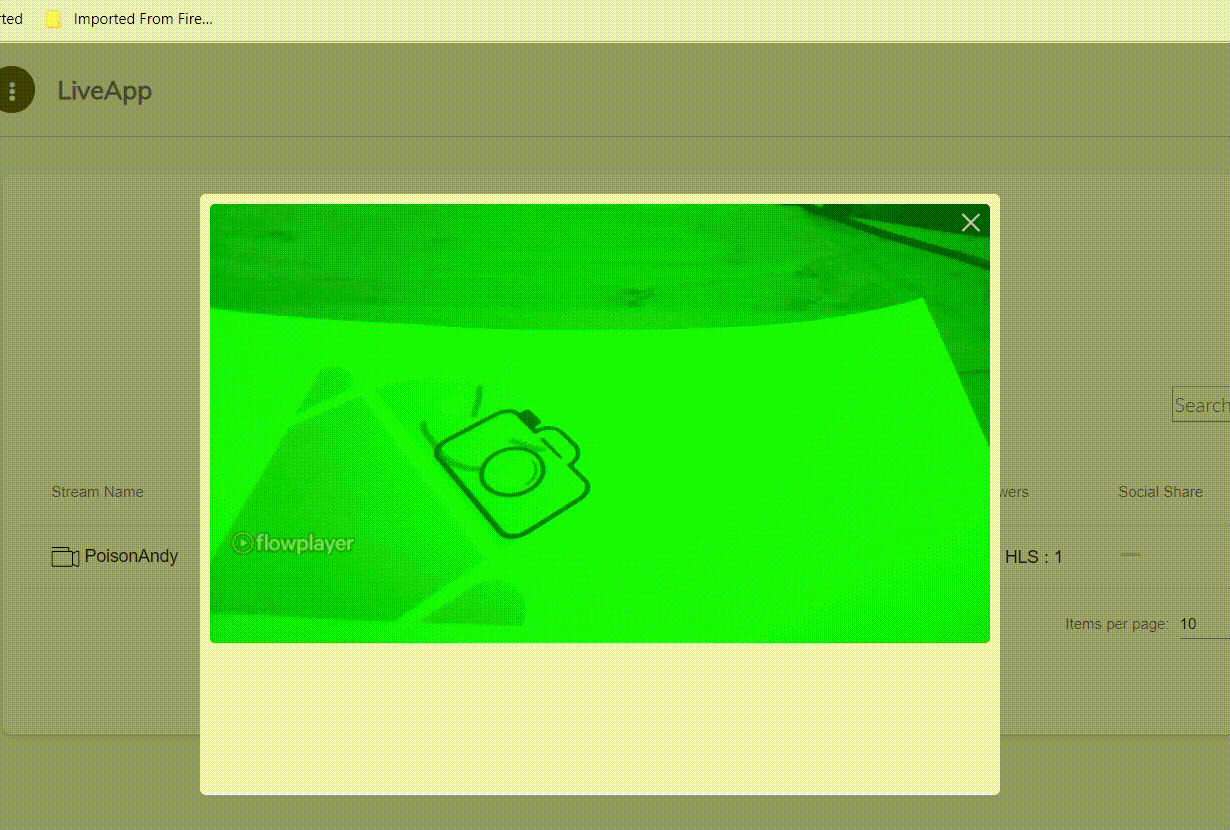 mirsamantajbakhsh/livehiddencamera
Live Hidden Camera is a library which record live video and audio from Android device without displaying a preview.
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
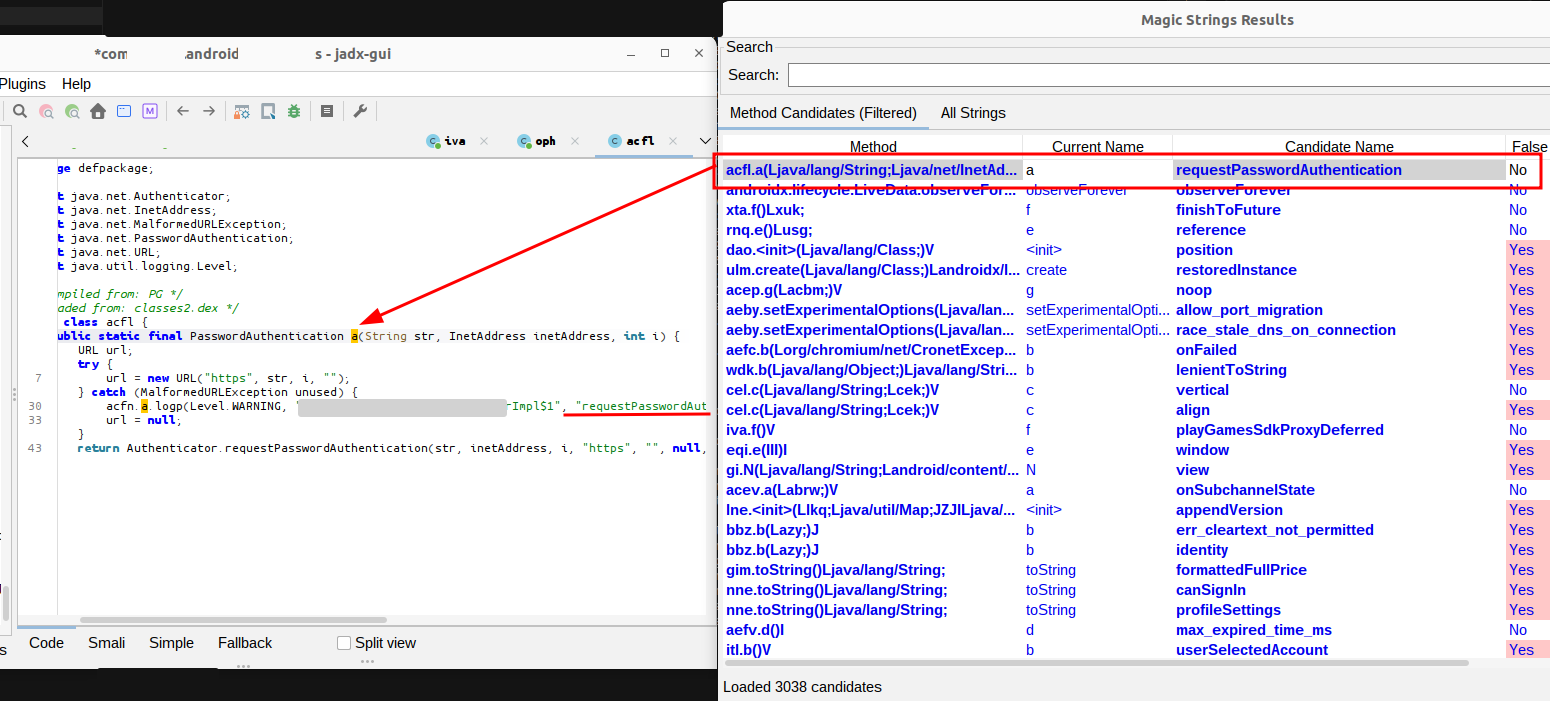 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.