
Fix-Apple-Mail-CVE-2020-9922
 wowfunhappy/fix-apple-mail-cve-2020-9922
Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
binary-exploitationexploitationforensics+3
3
wowfunhappy/fix-apple-mail-cve-2020-9922Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
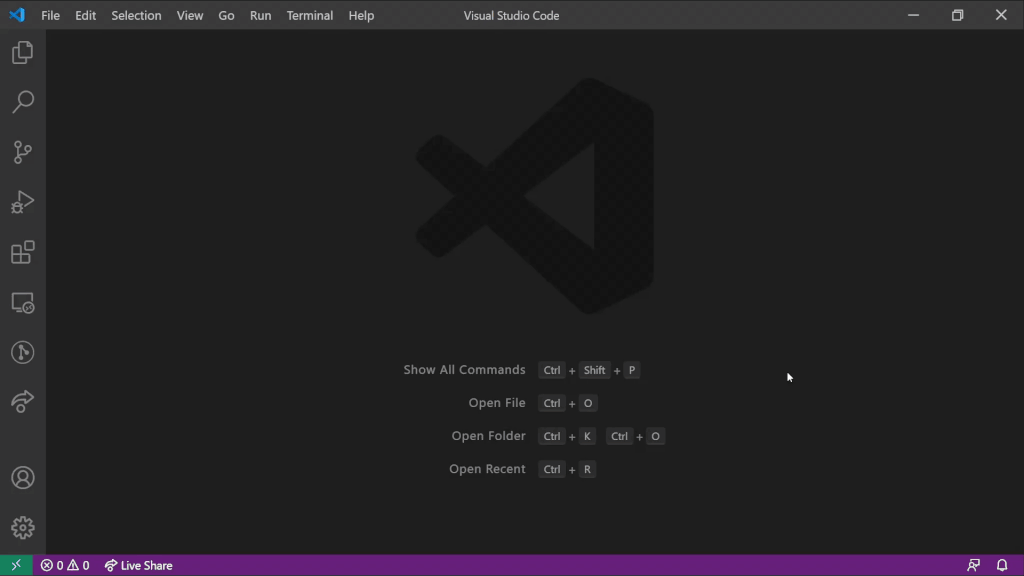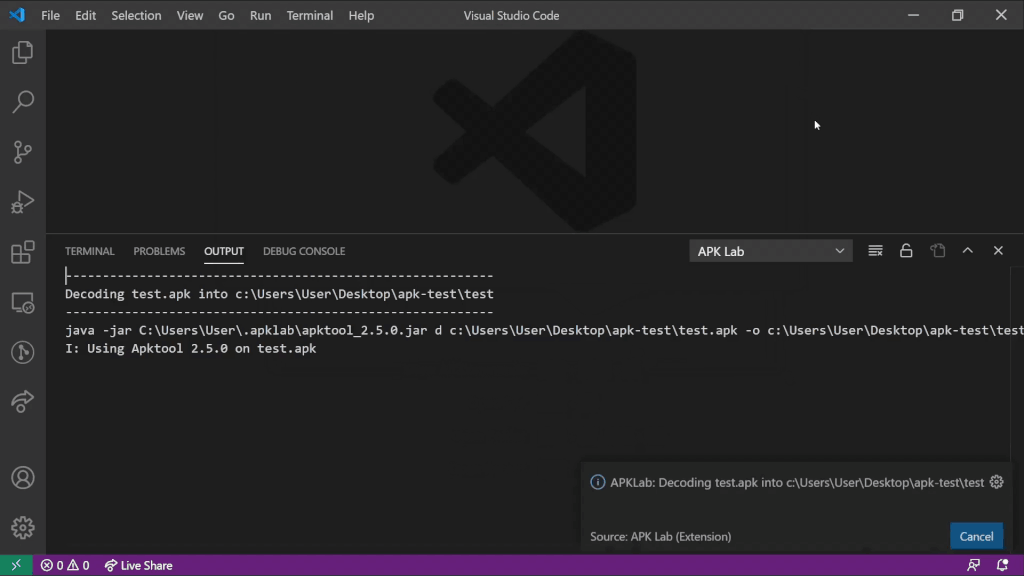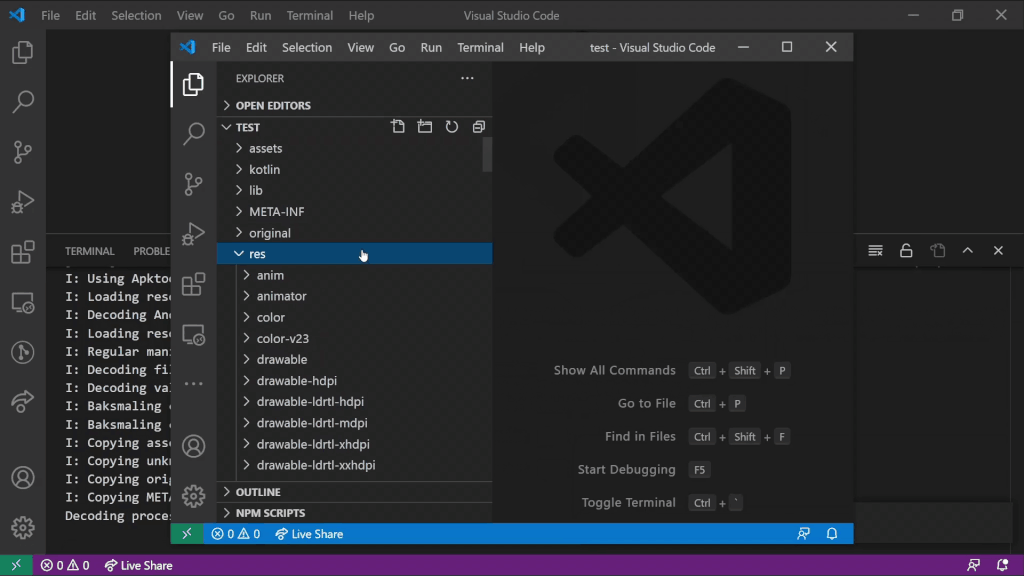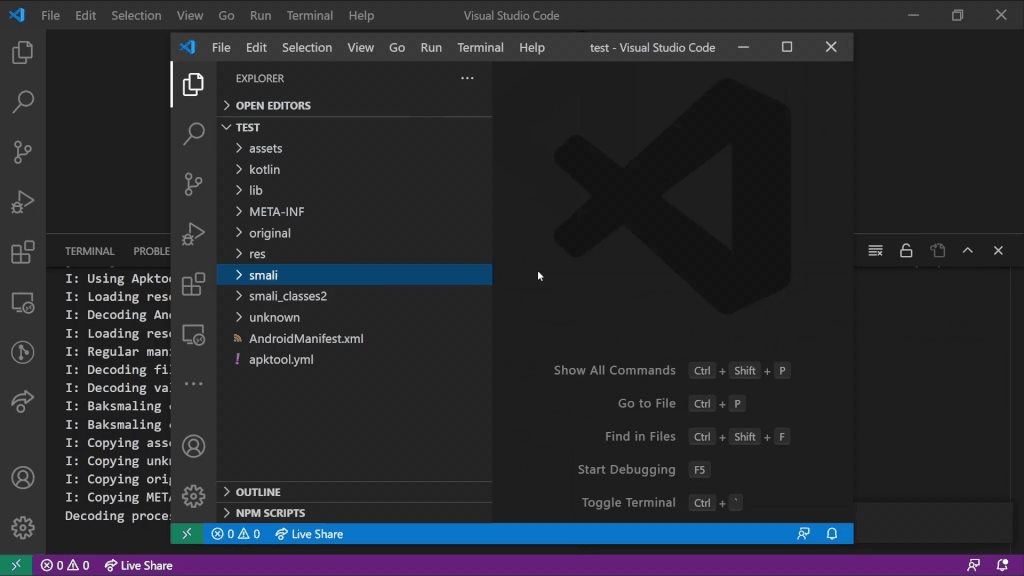 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
 calebfenton/simplify
Android virtual machine and deobfuscator
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
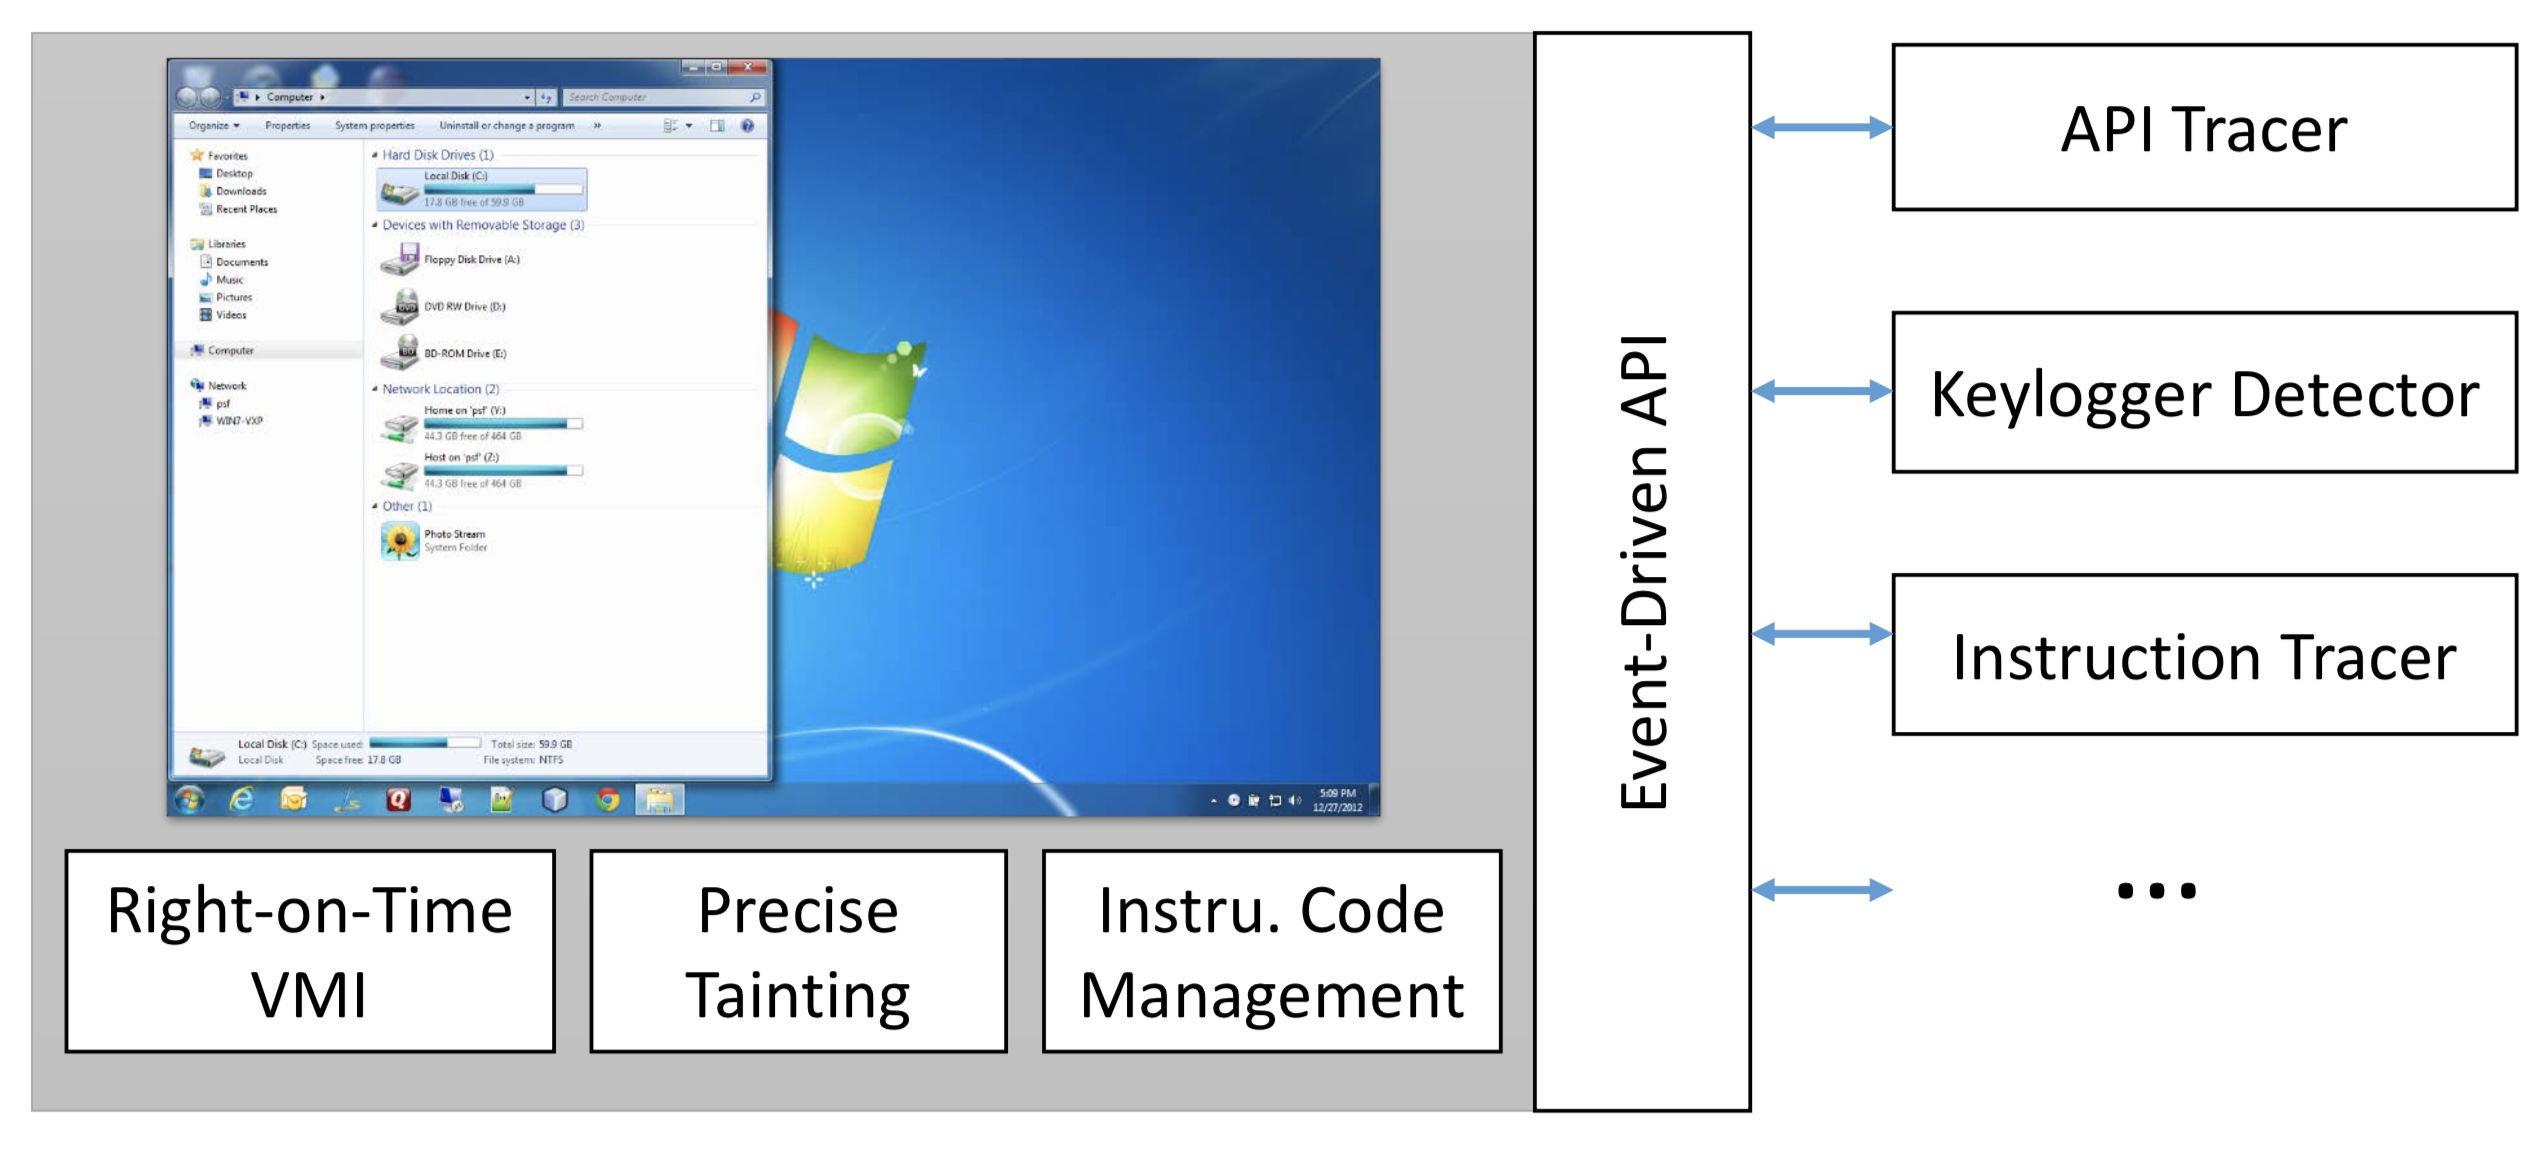 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 cecio/usbvalve
Expose USB activity on the fly
 vxunderground/malwaresourcecode
Collection of malware source code for a variety of platforms in an array of different programming languages.
 mr-un1k0d3r/redteamccode
Red Team C code repo
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
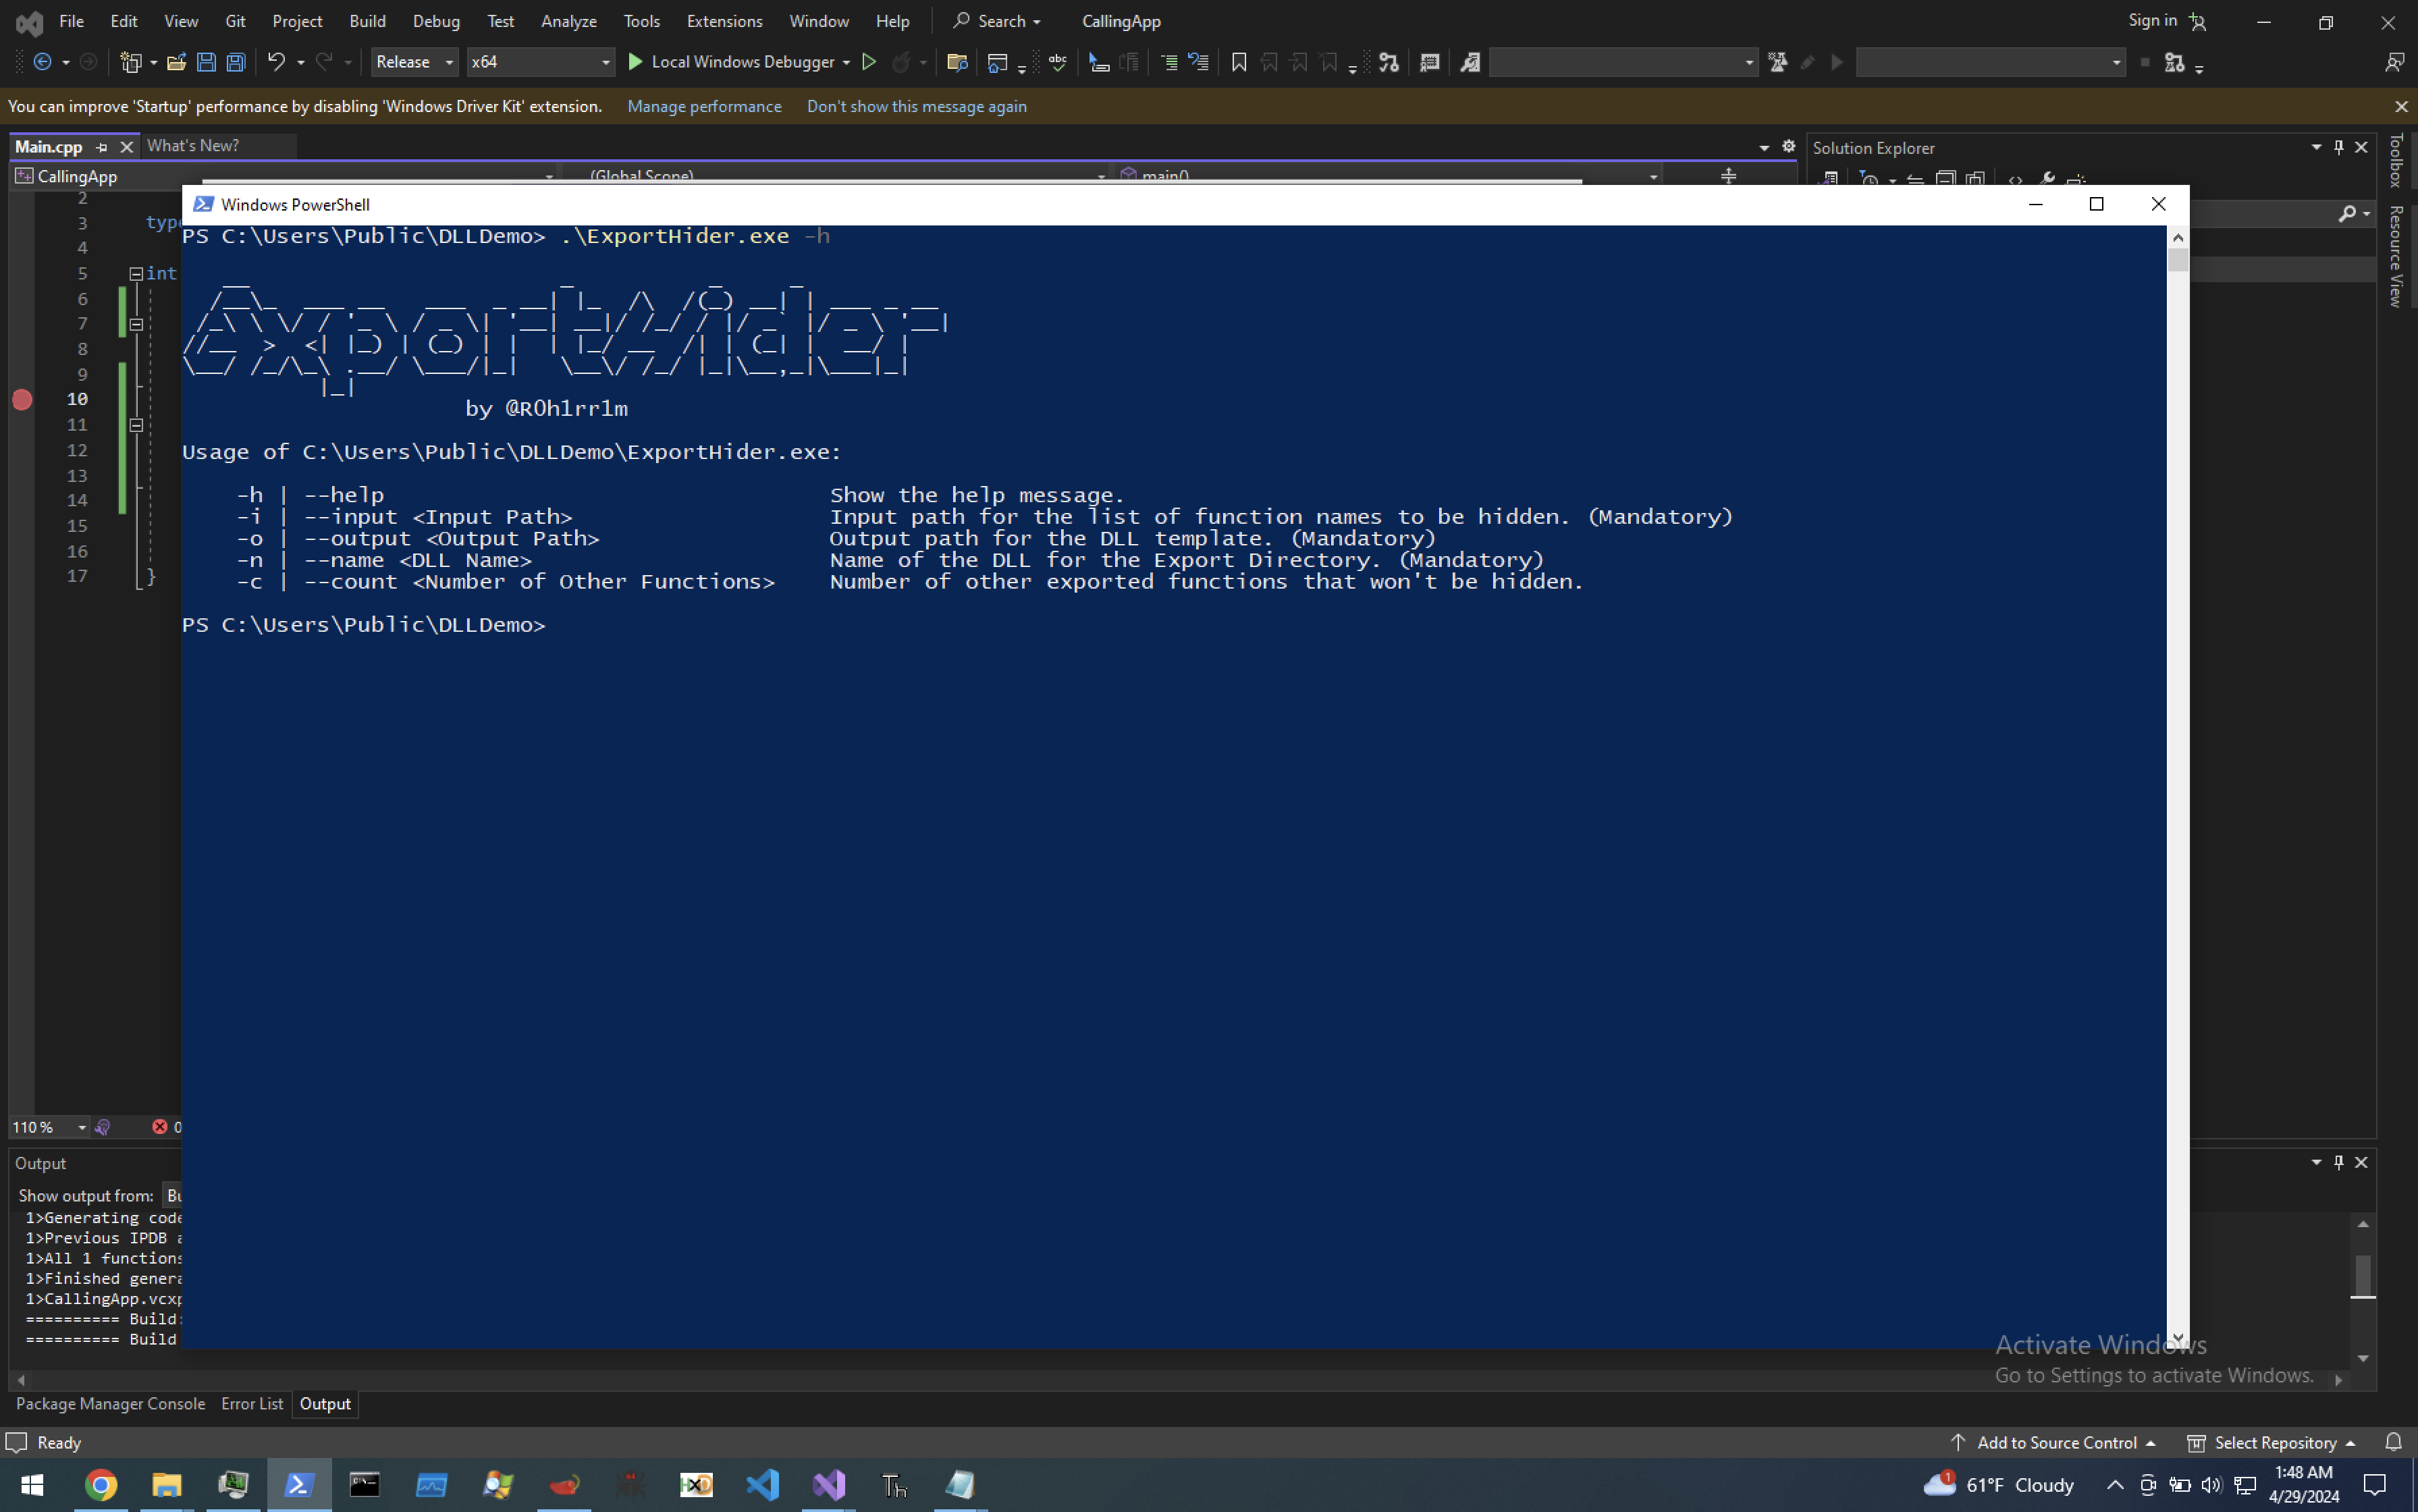 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 chef-cft/inspec_cve_2019_15224
Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 monnappa22/limon
Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
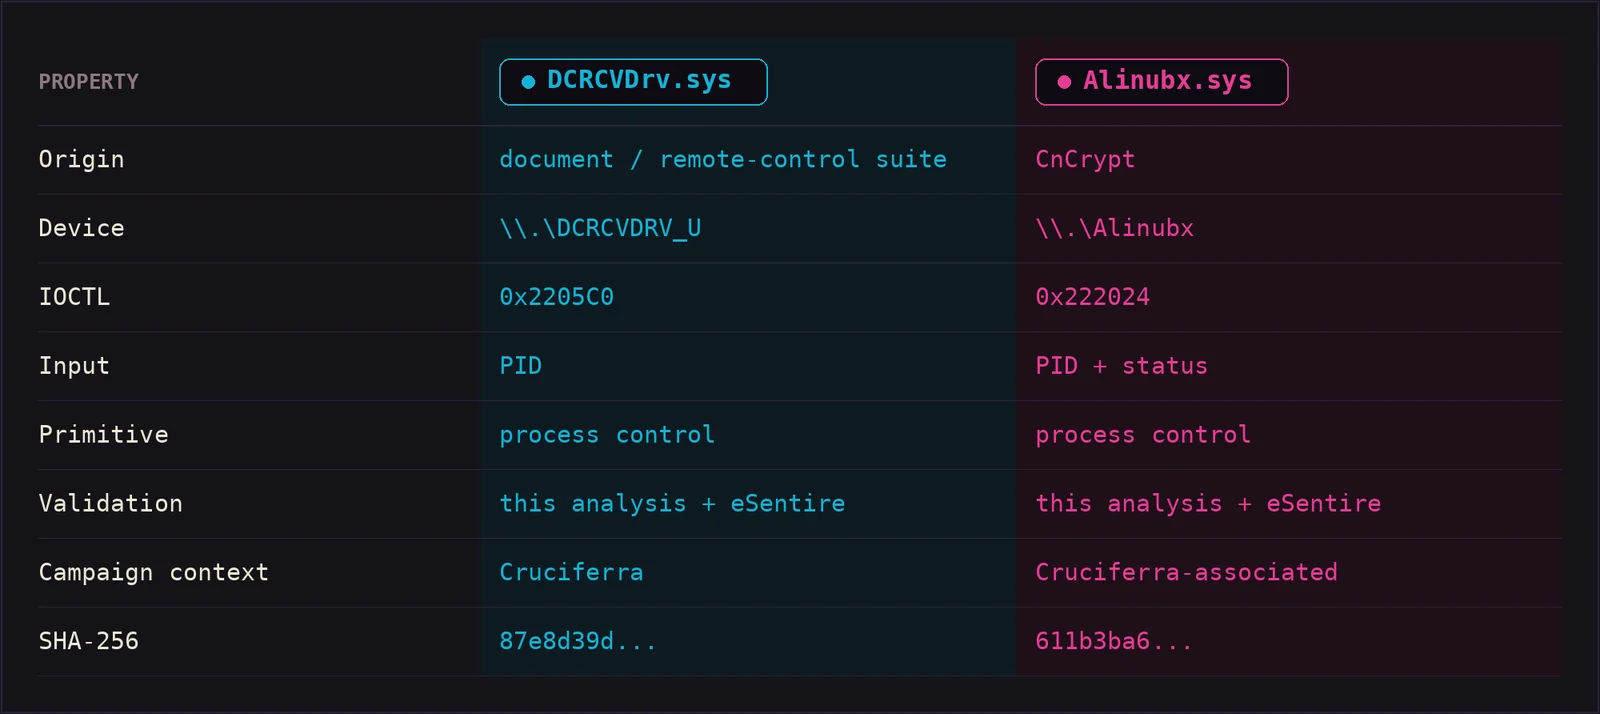 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.