
avpass
 sslab-gatech/avpass
Tool for leaking and bypassing Android malware detection system
android-securityeducationexploit-frameworks+2
sslab-gatech/avpassTool for leaking and bypassing Android malware detection system
 calebfenton/dex-oracle
A pattern based Dalvik deobfuscator which uses limited execution to improve semantic analysis
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 maddiestone/conpresentations
Slide decks from my conference presentations
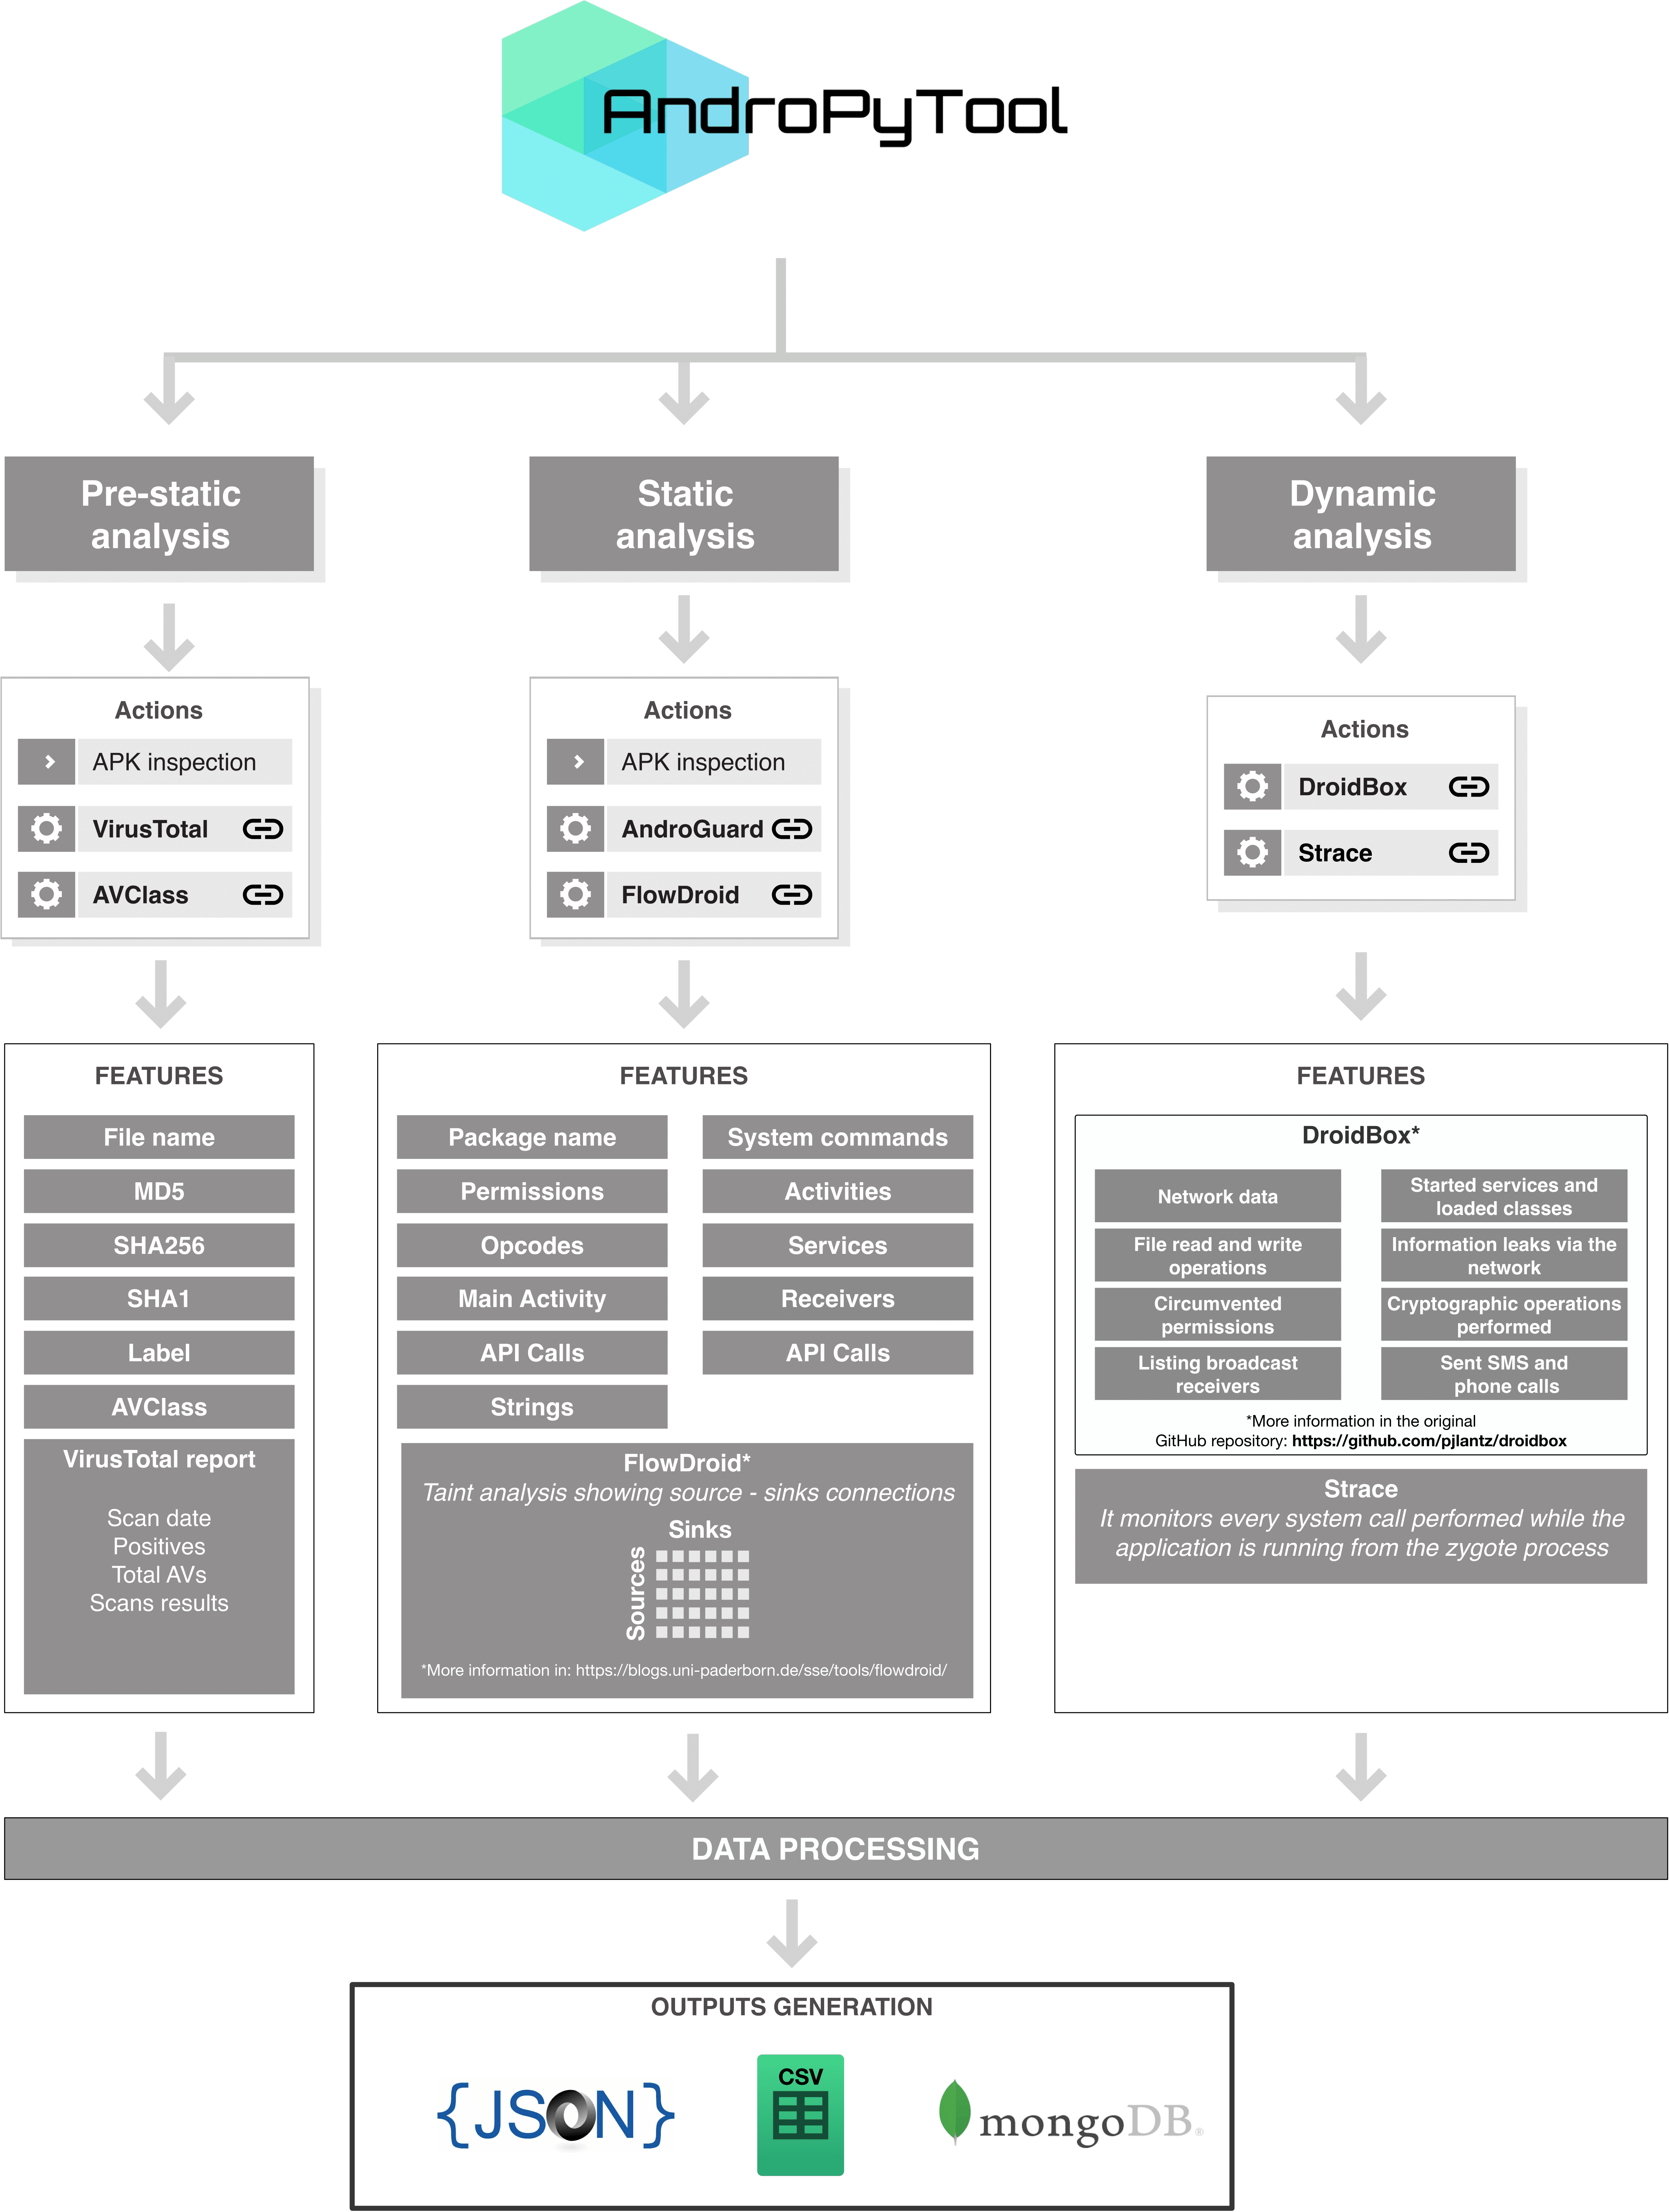 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…

 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
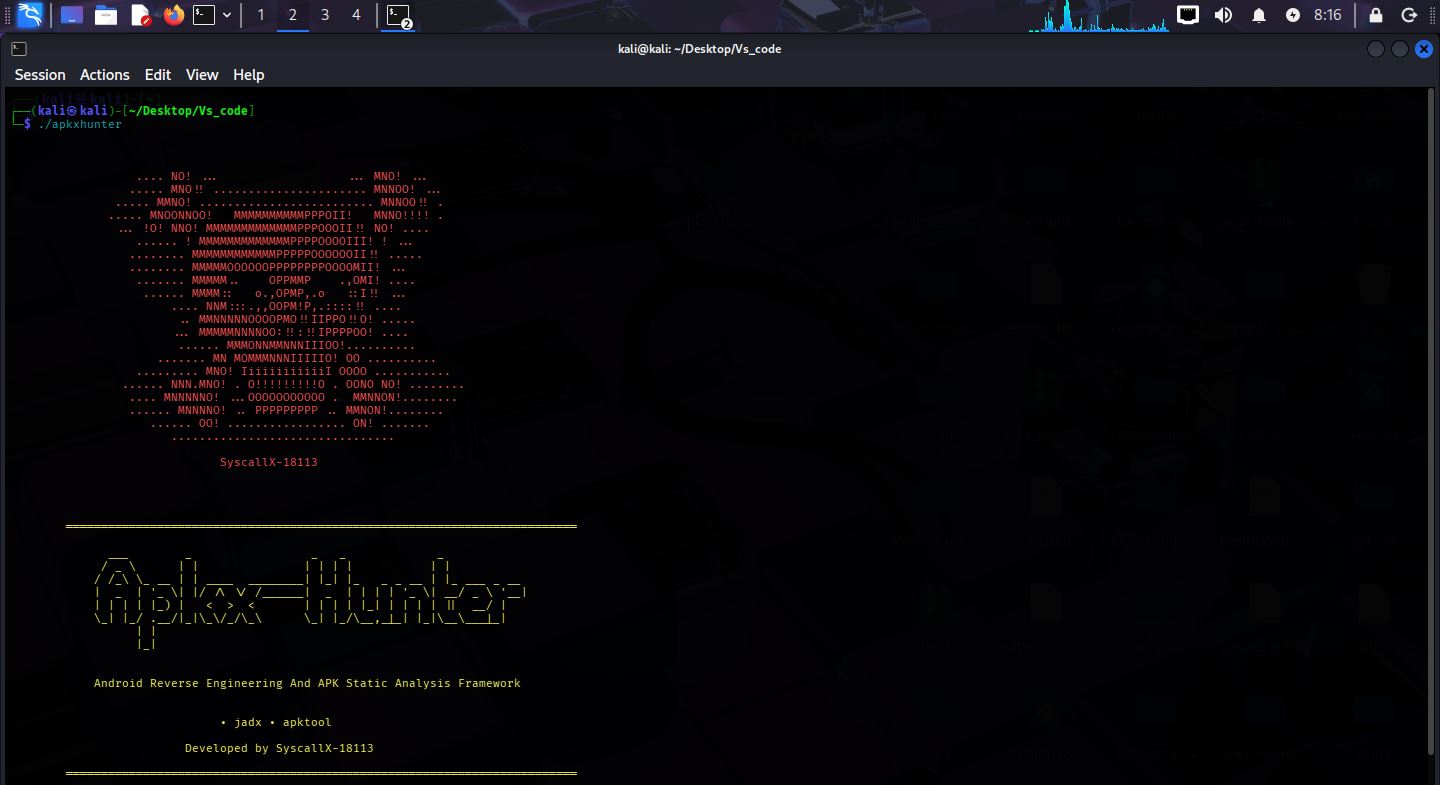 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 dkhuuthe/madlira
Malware detection using learning and information retrieval for Android
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…