

scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
2241 day ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
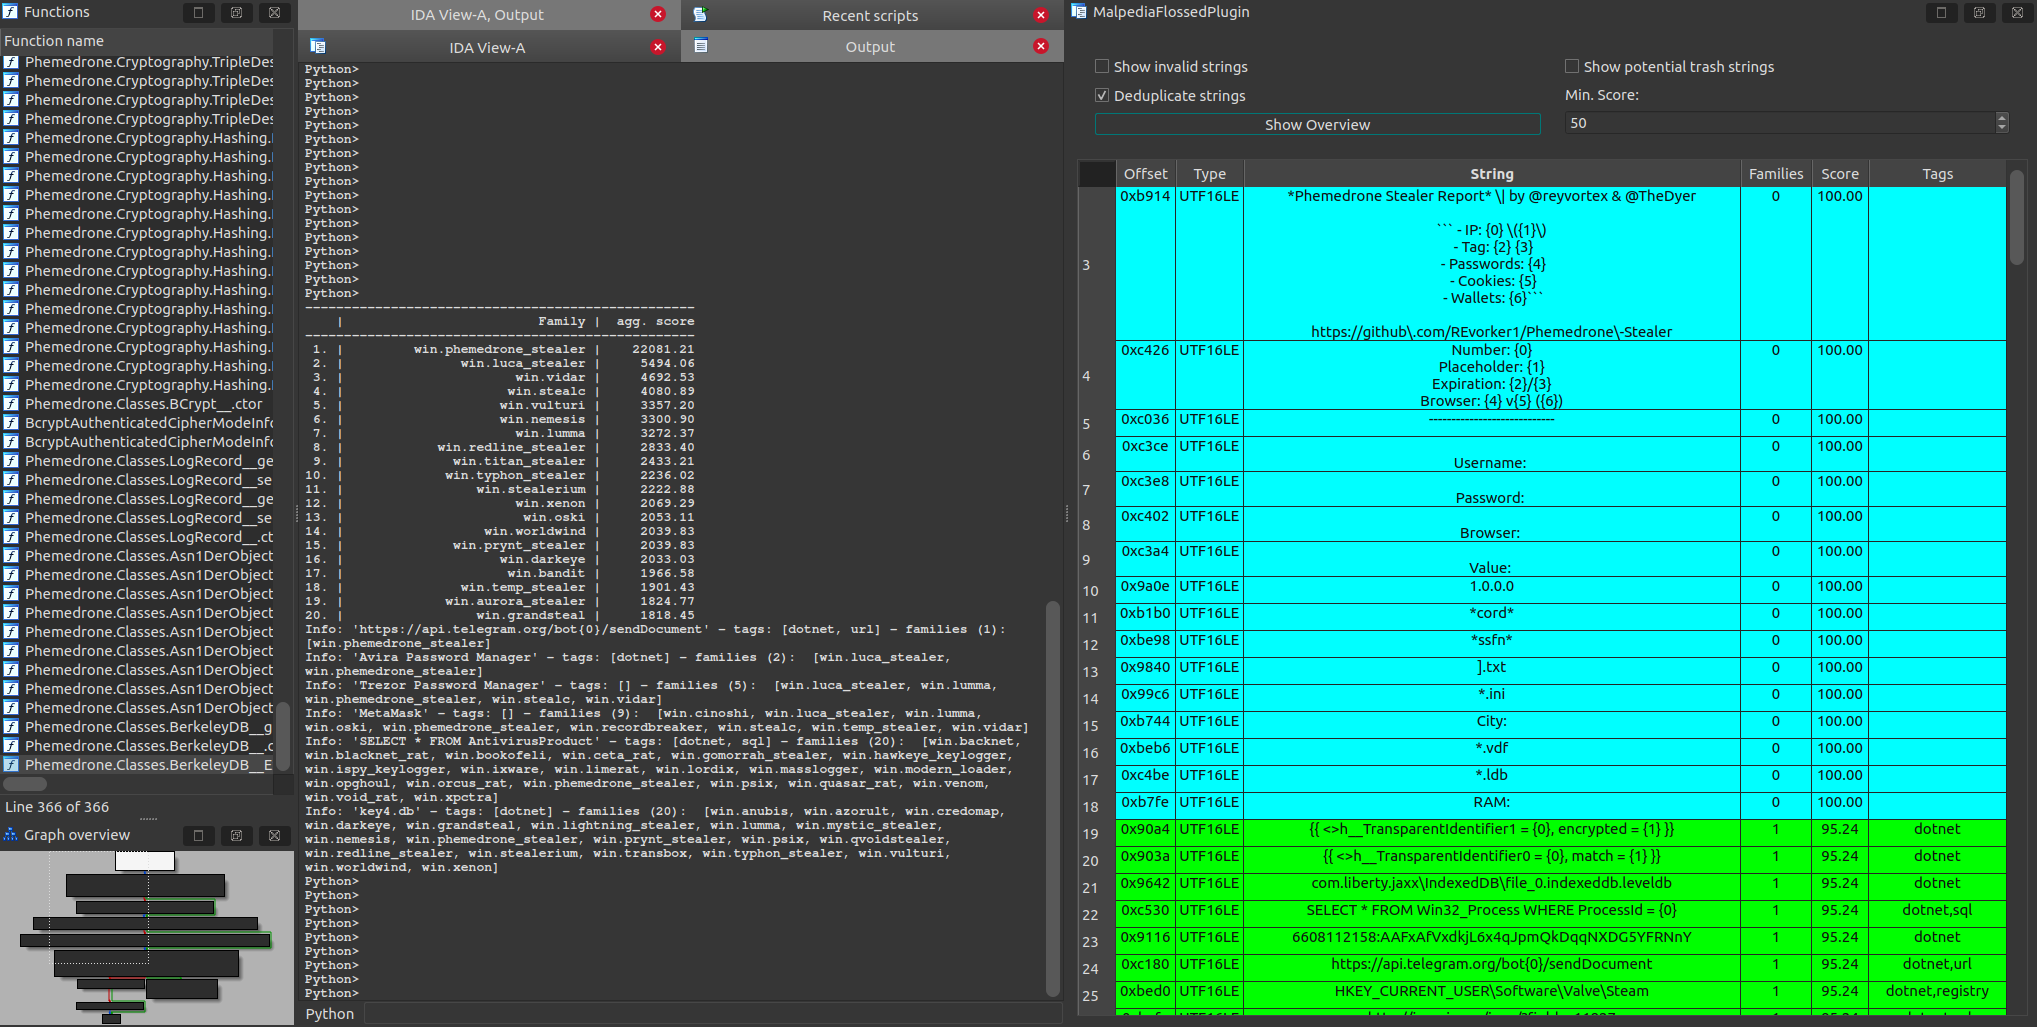 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
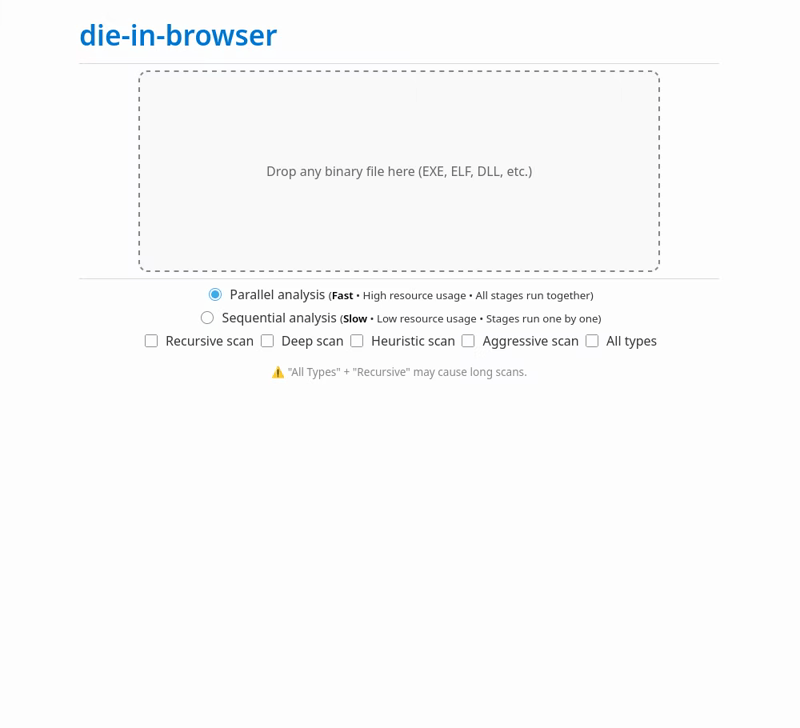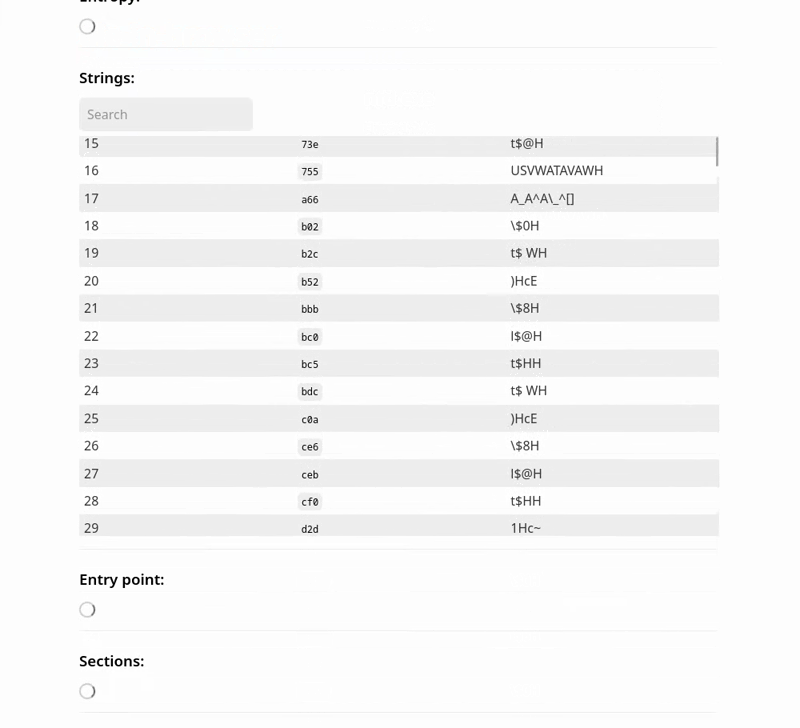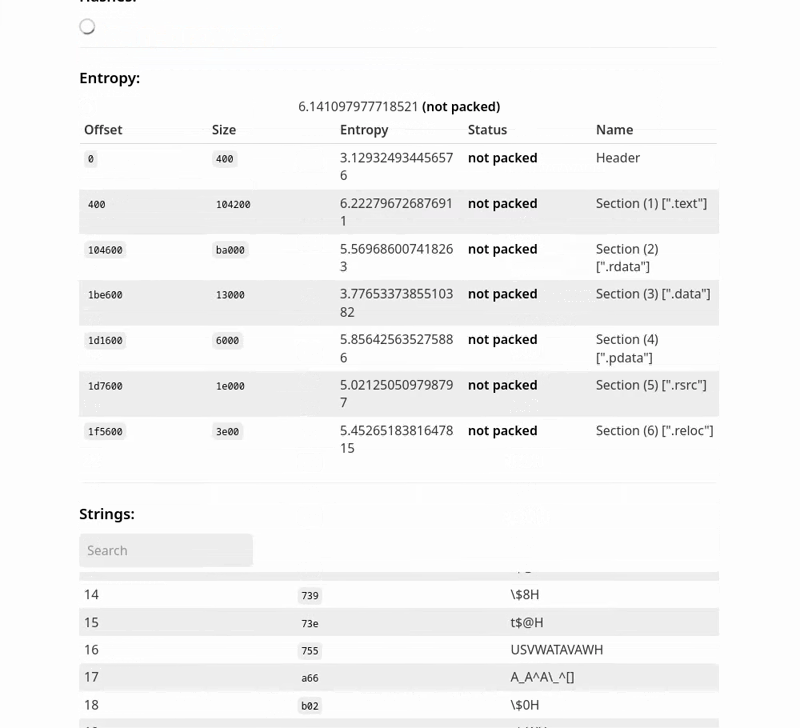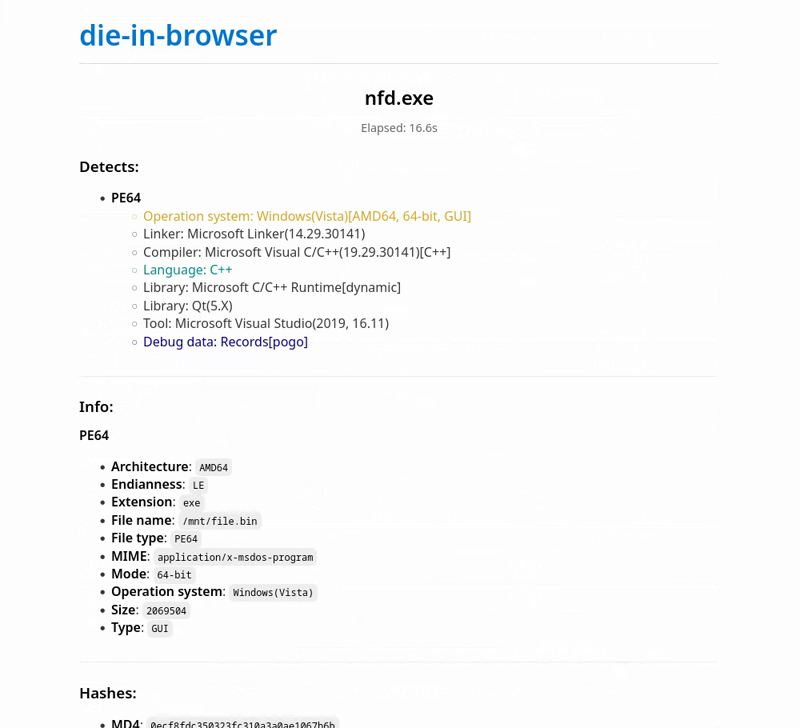 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
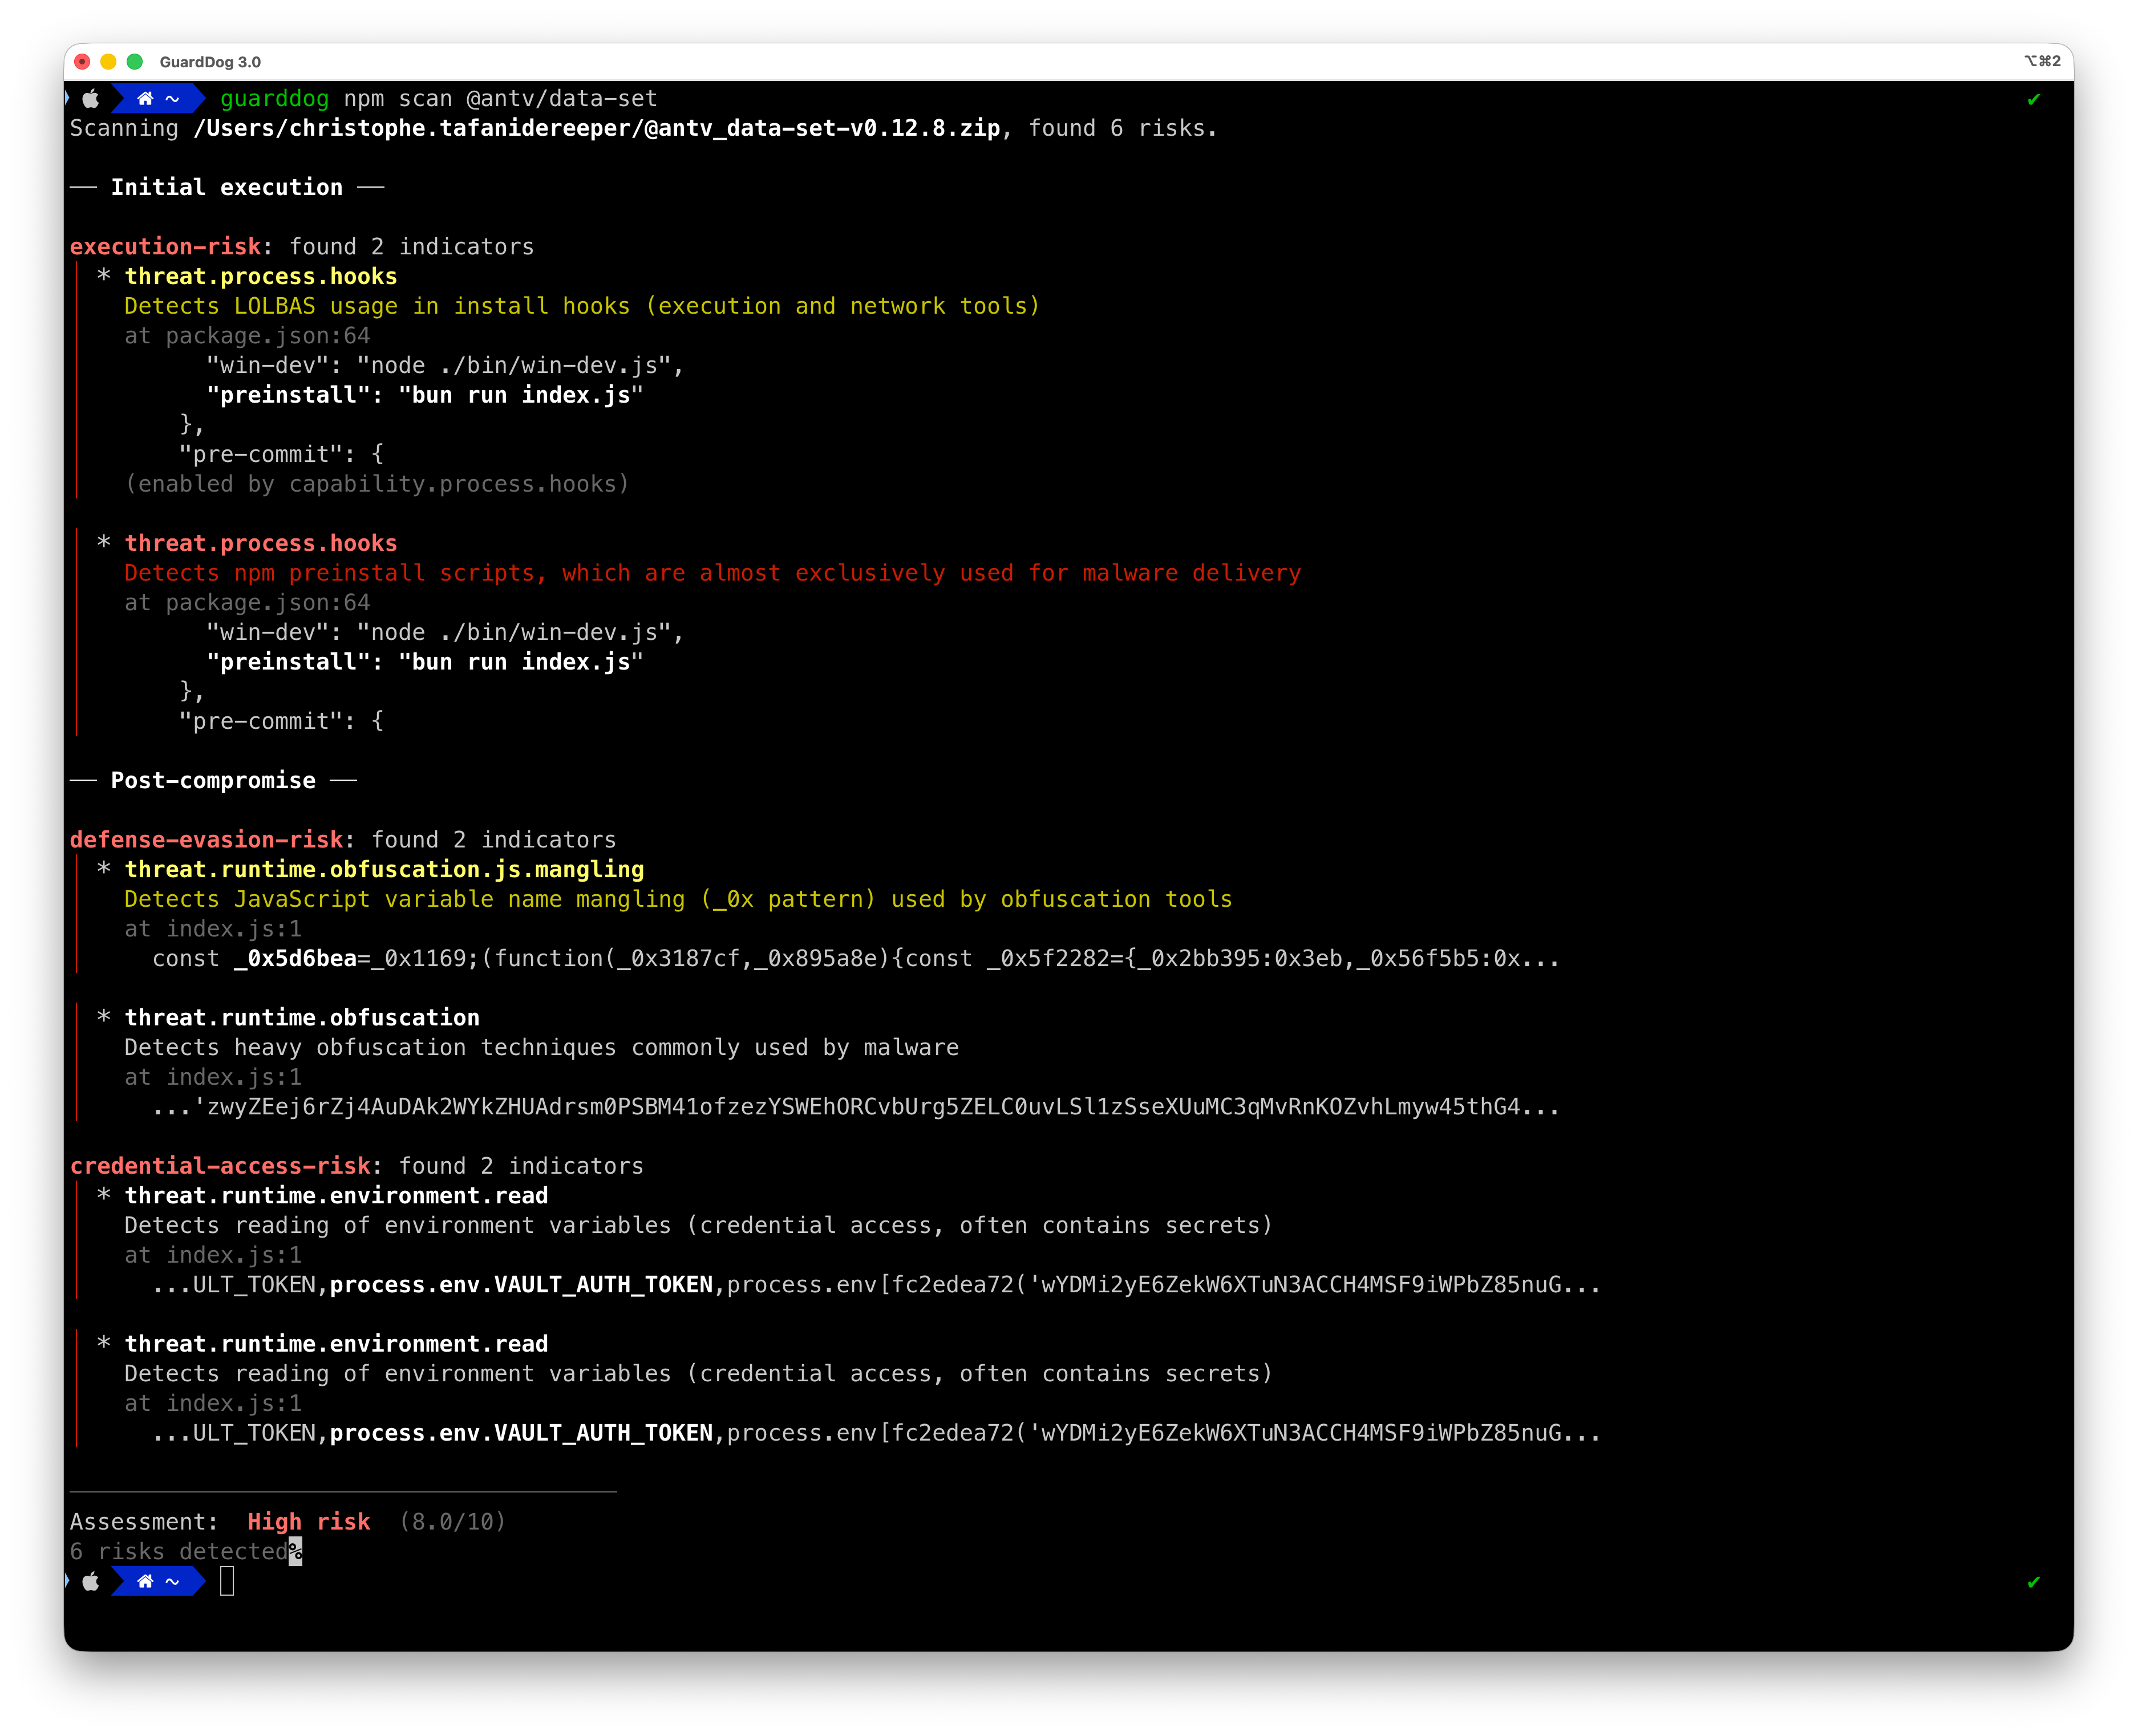 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 jvoisin/php-malware-finder
Detect potentially malicious PHP files
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
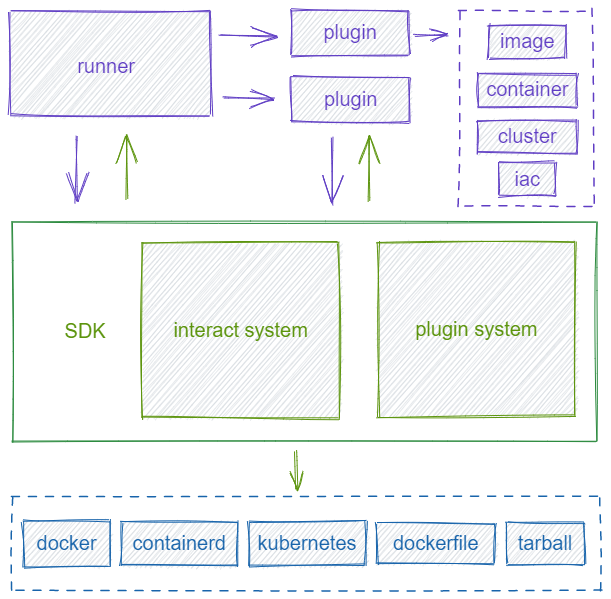 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 code5ecure/cve-2024-41453_cve-2024-41454
Proof-of-concept exploits for CVE-2024-41453 and CVE-2024-41454 demonstrating stored XSS and malicious file upload vulnerabilities in ProcessMaker 4…
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations