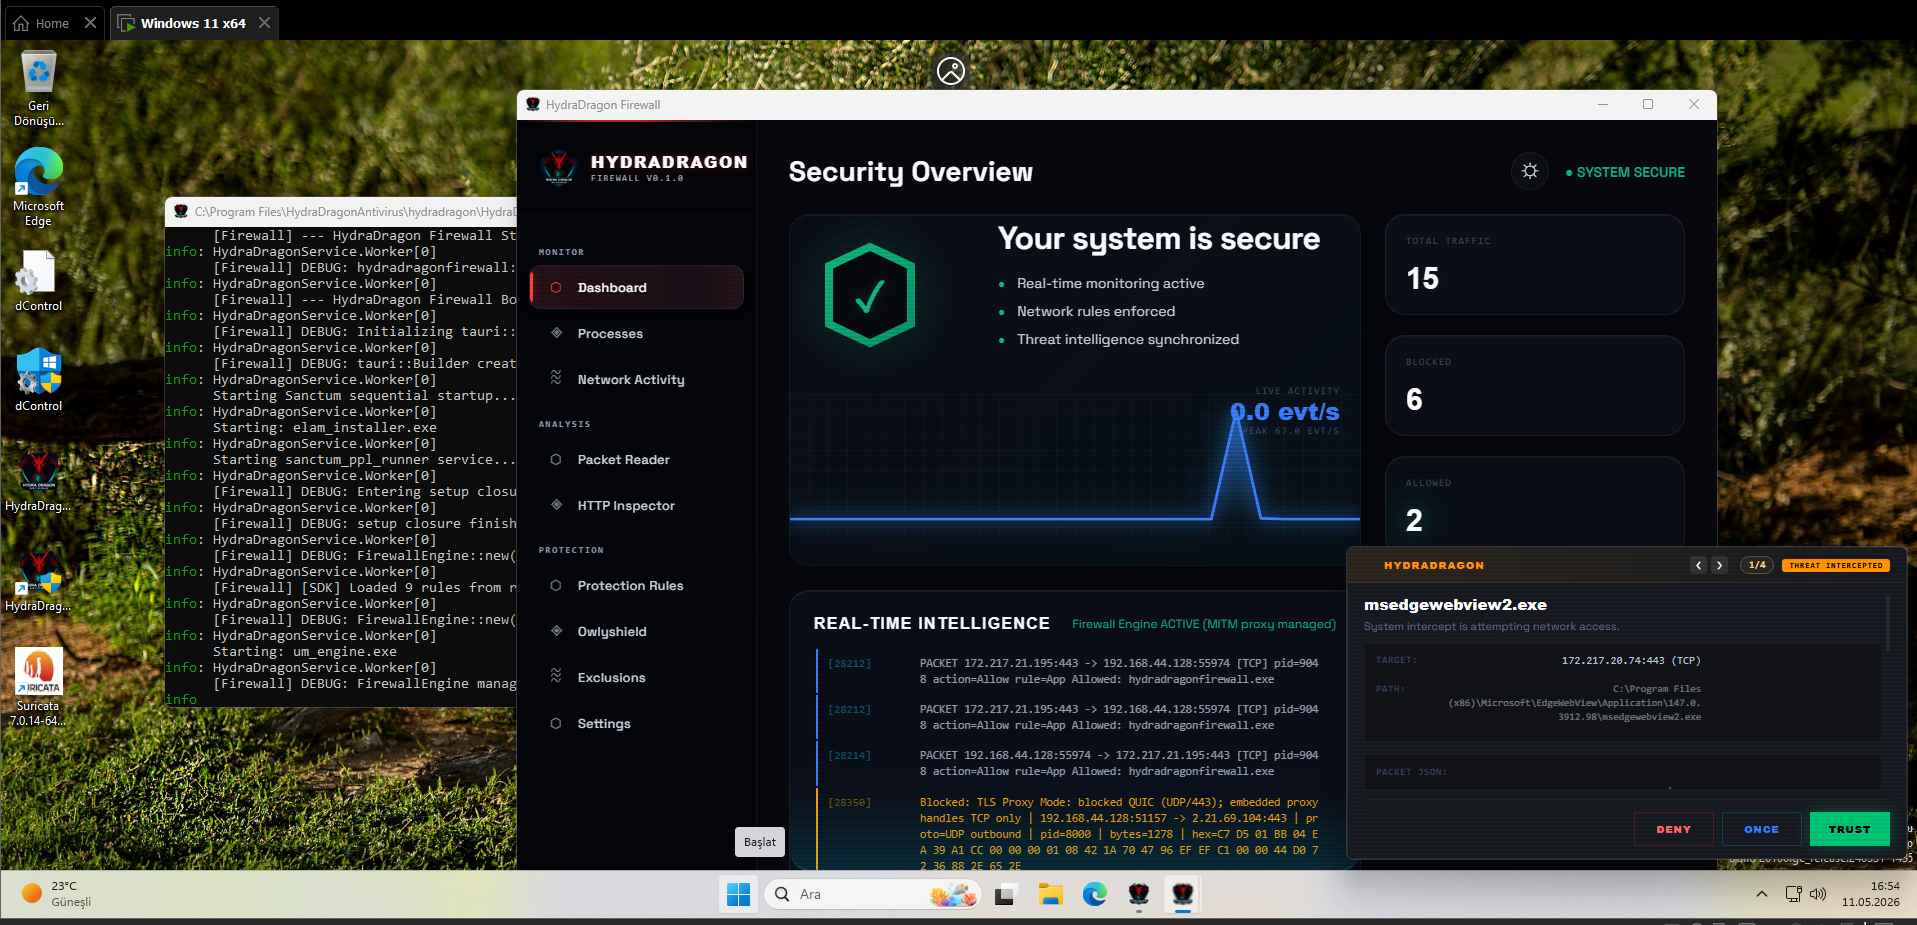
HydraDragonAntivirus

Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

Proper sandboxing for agentic coding and web browsing

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…

Portable Executable reversing tool with a friendly GUI

Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…

Tracking interesting Linux (and UNIX) malware. Send PRs

Sandboxie Plus & Classic

IoCs and YARA rules from Threatray's Threat Research

Clusters and elements to attach to MISP events or attributes (like threat actors)

Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

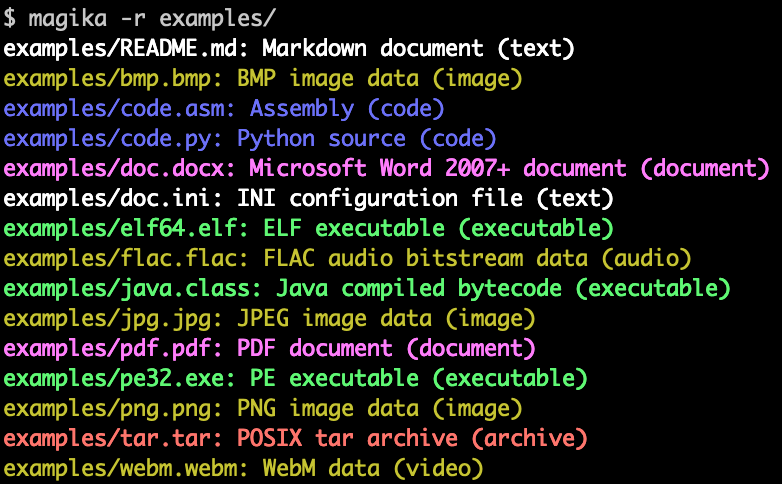
Fast and accurate AI powered file content types detection

A collection of android security related resources