


 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
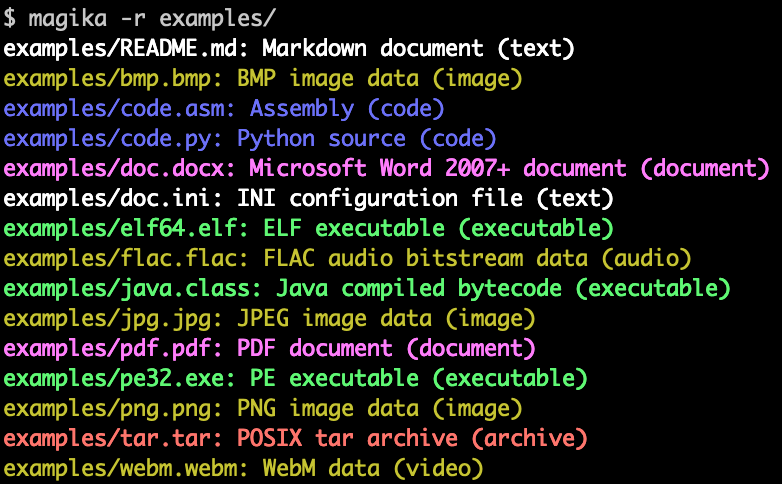 google/magika
Fast and accurate AI powered file content types detection
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 sandboxie-plus/sandboxie
Sandboxie Plus & Classic
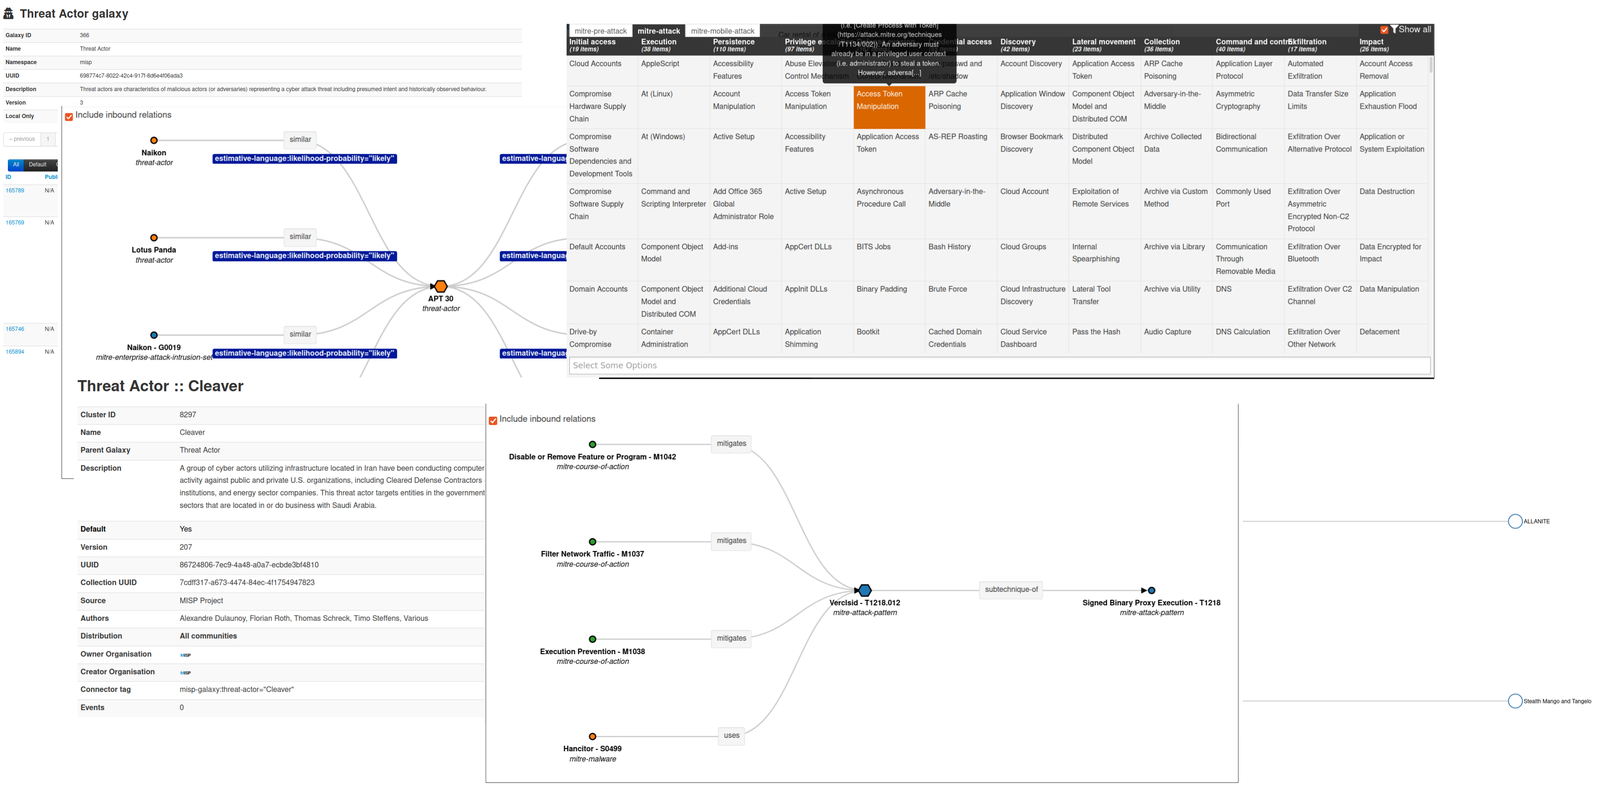 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 fhightower/ioc-finder
Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…
 x4nth055/pythoncode-tutorials
The Python Code Tutorials
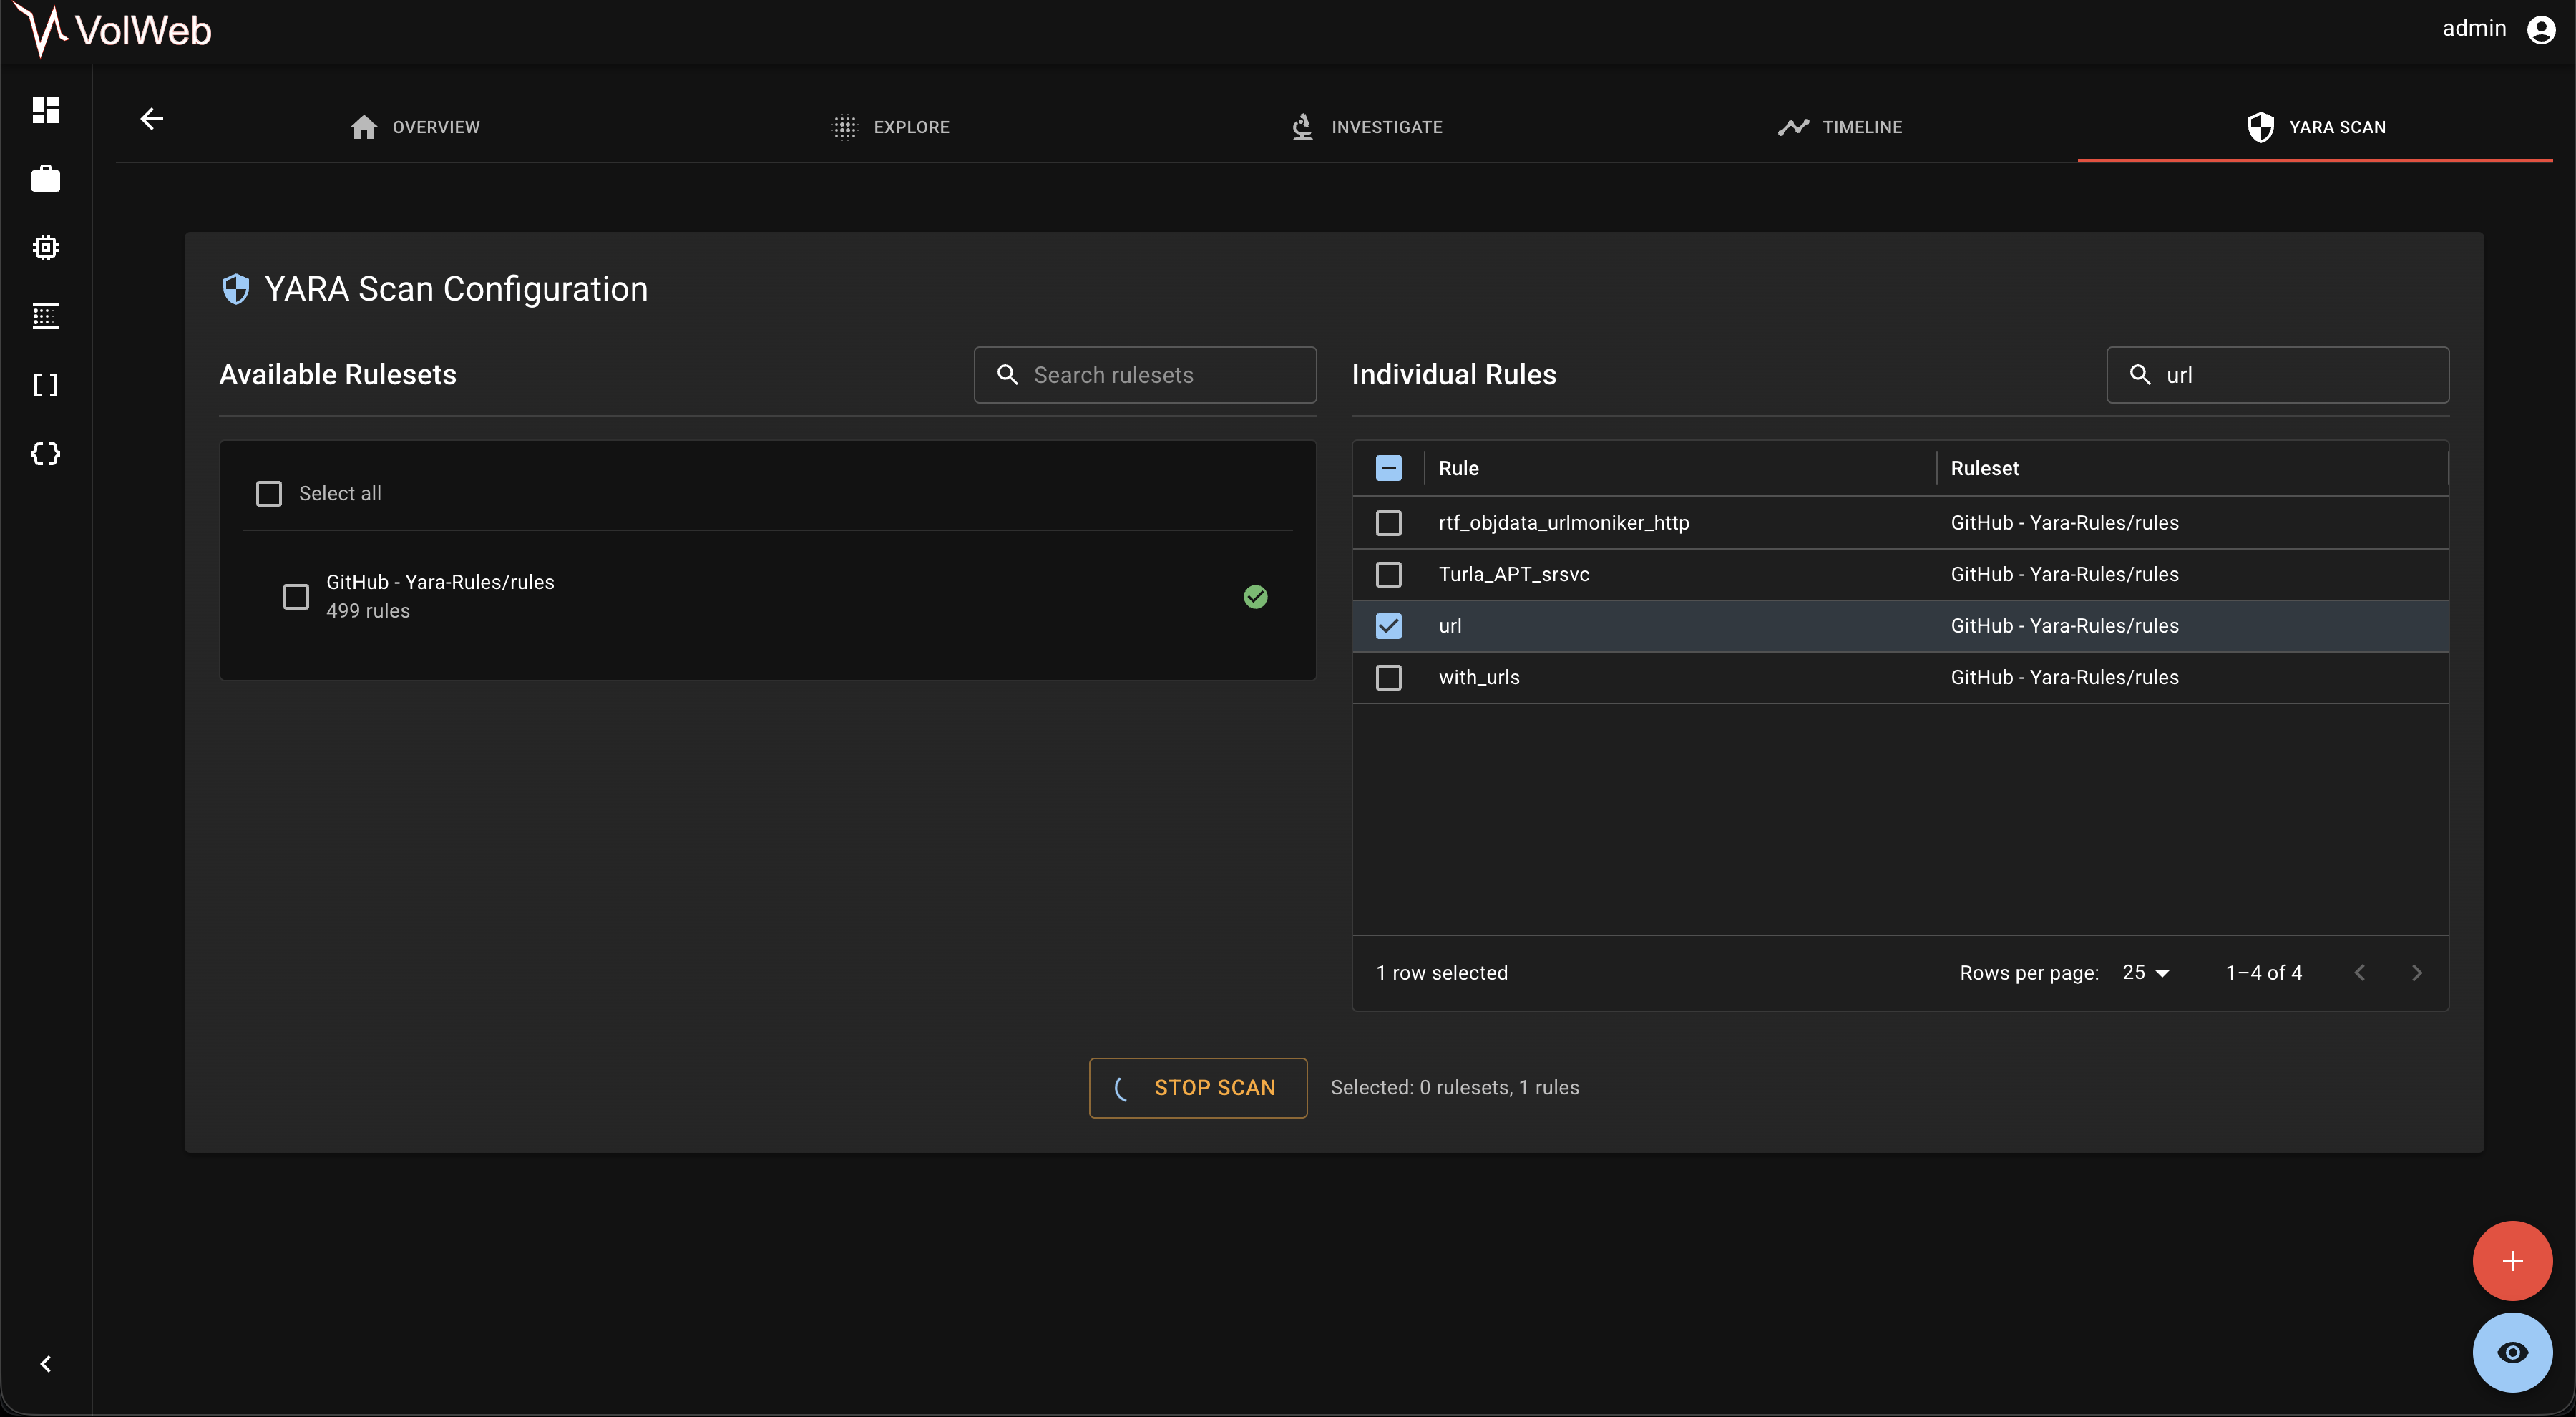 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 threatray/threat-research
IoCs and YARA rules from Threatray's Threat Research
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports