

pmg
 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
cloud-securitycontainer-securitydevsecops+6
safedep/pmgPMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 eset/malware-research
Code written as part of our various malware investigations
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
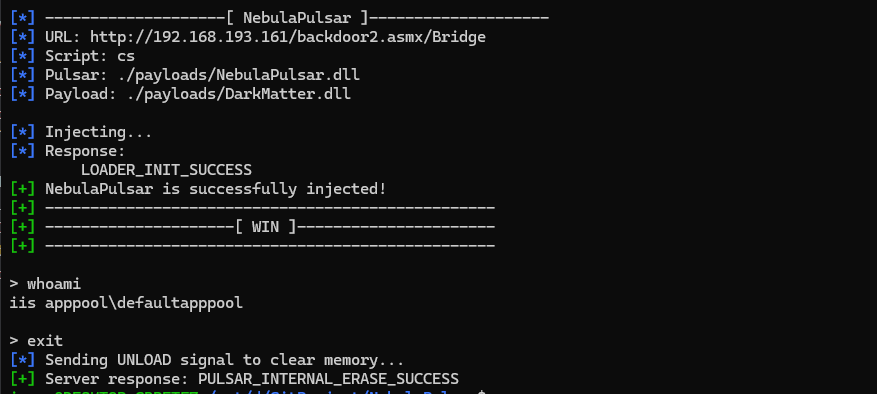 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
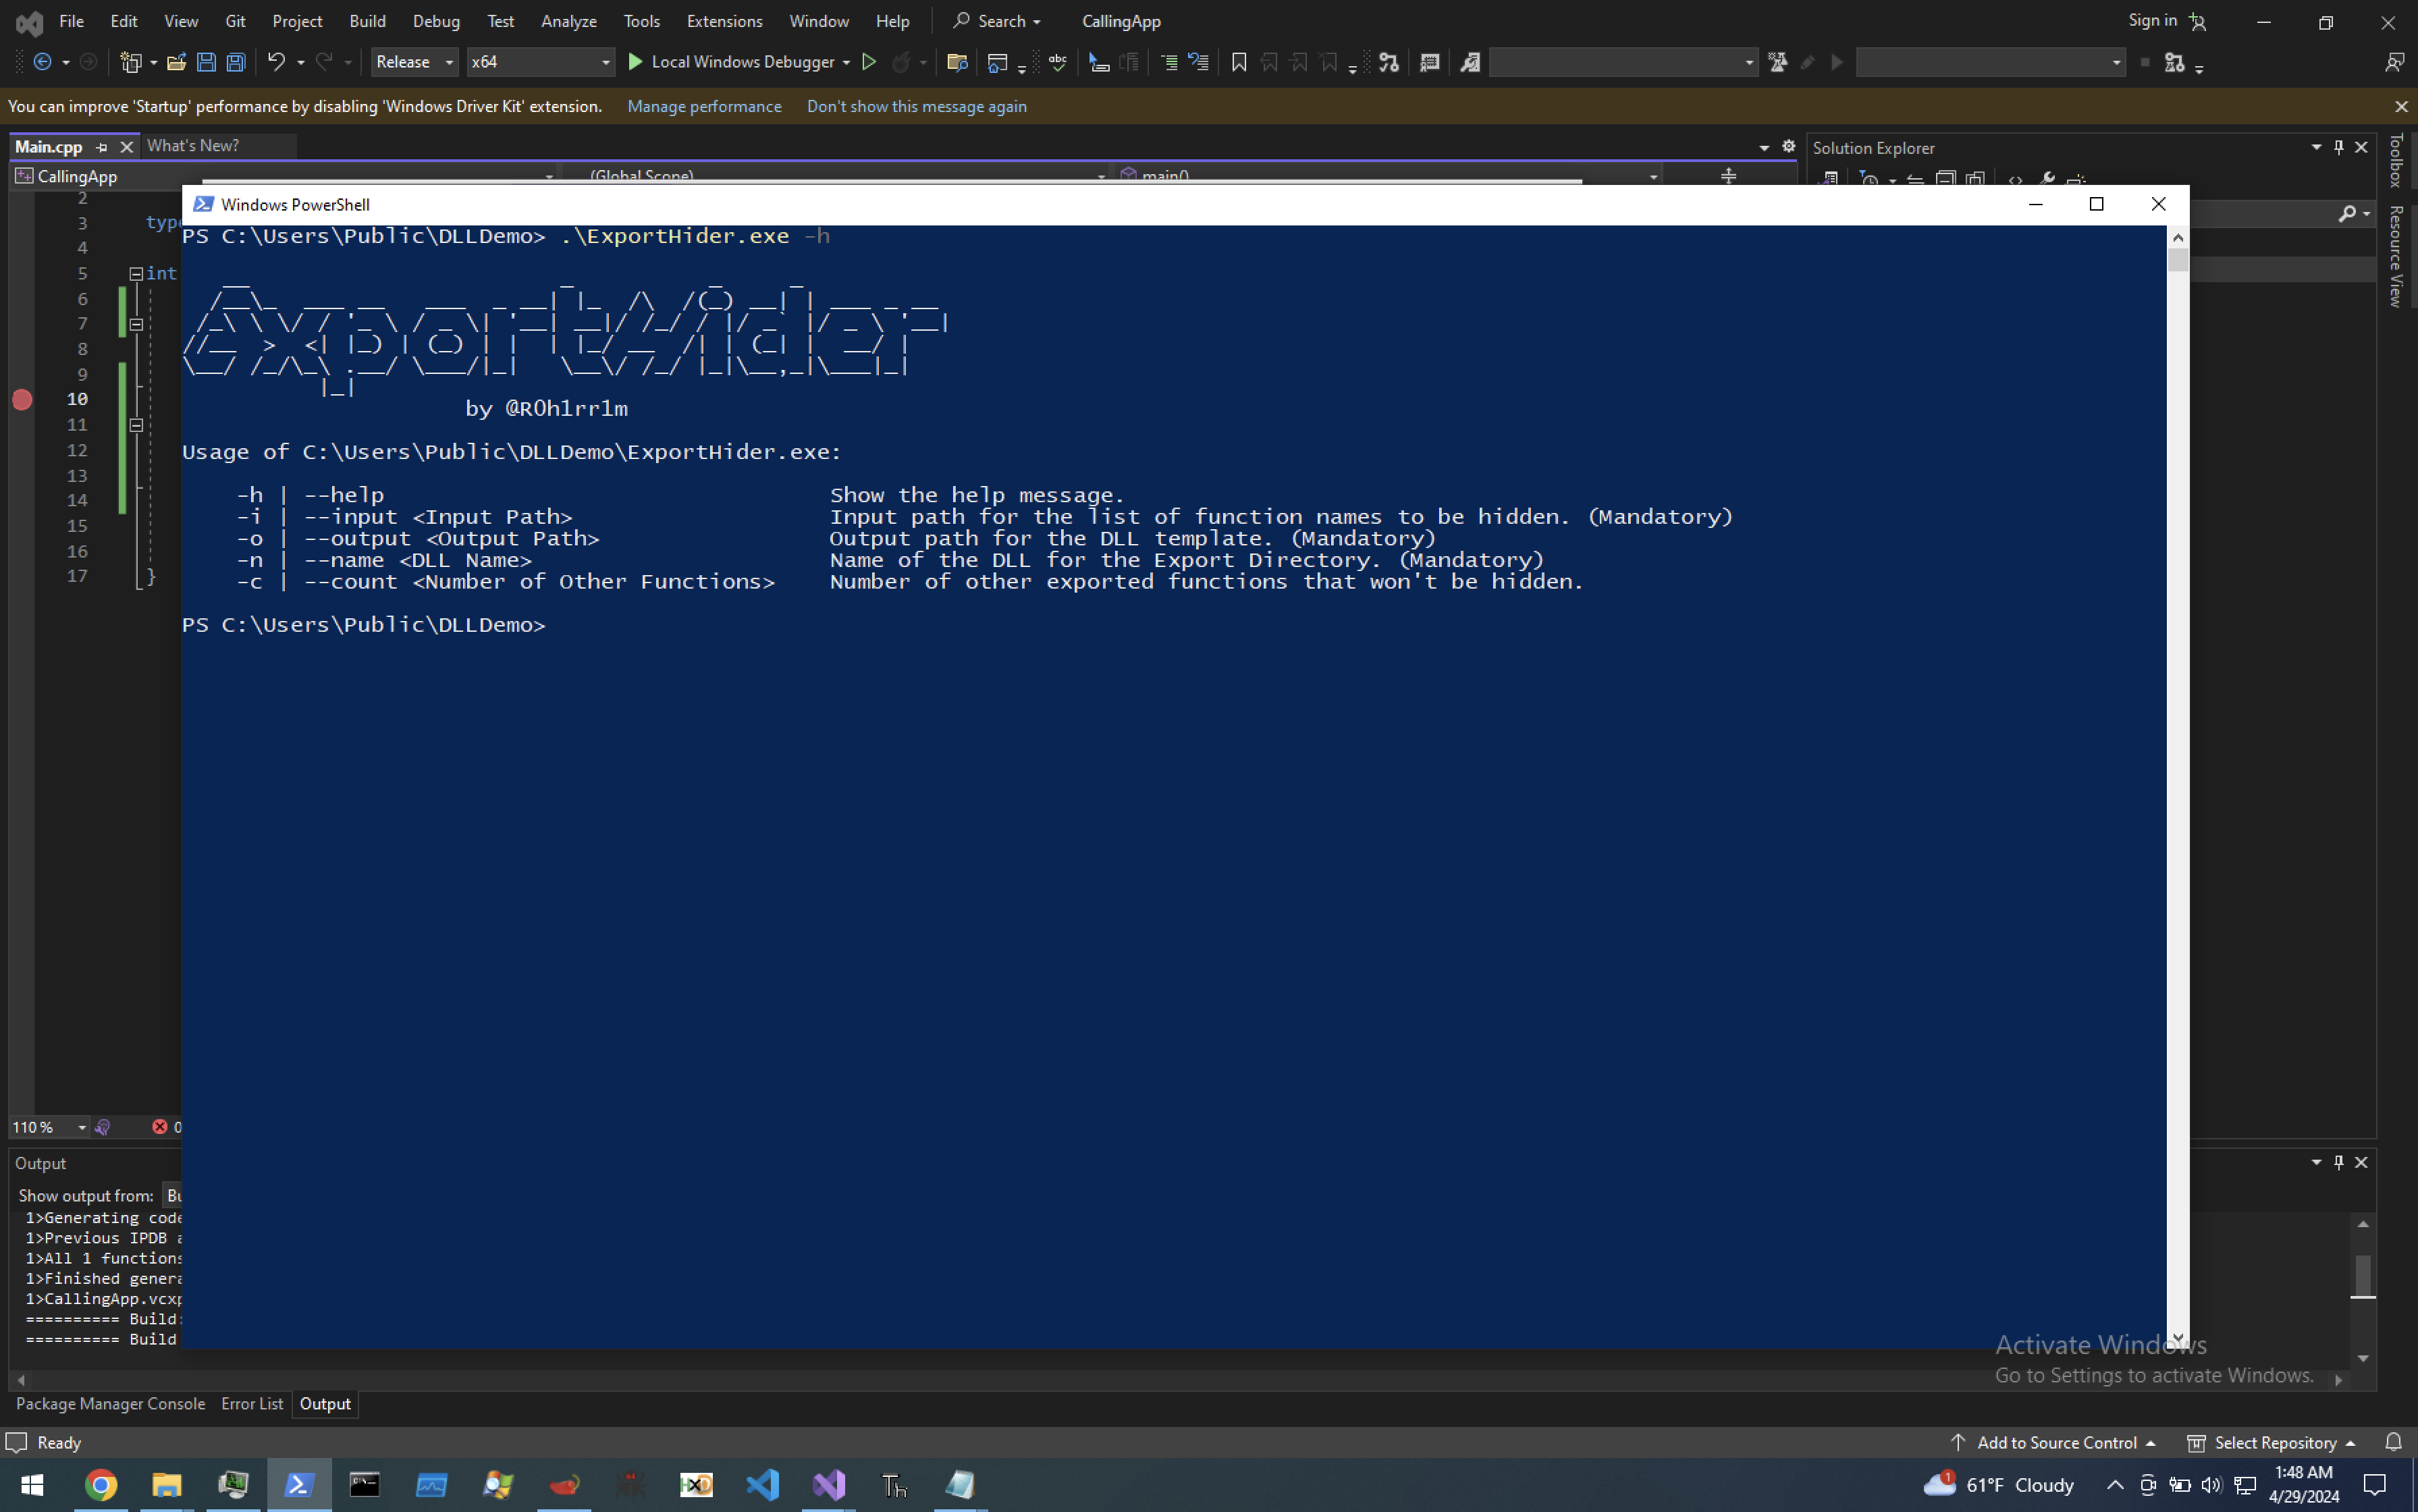 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 rshipp/awesome-malware-analysis
Defund the Police.
 byt3bl33d3r/dnschef-ng
DNSChef (NG) - DNS proxy for Penetration Testers and Malware Analysts
 hasherezade/pesieve-go
Golang bindings for PE-sieve
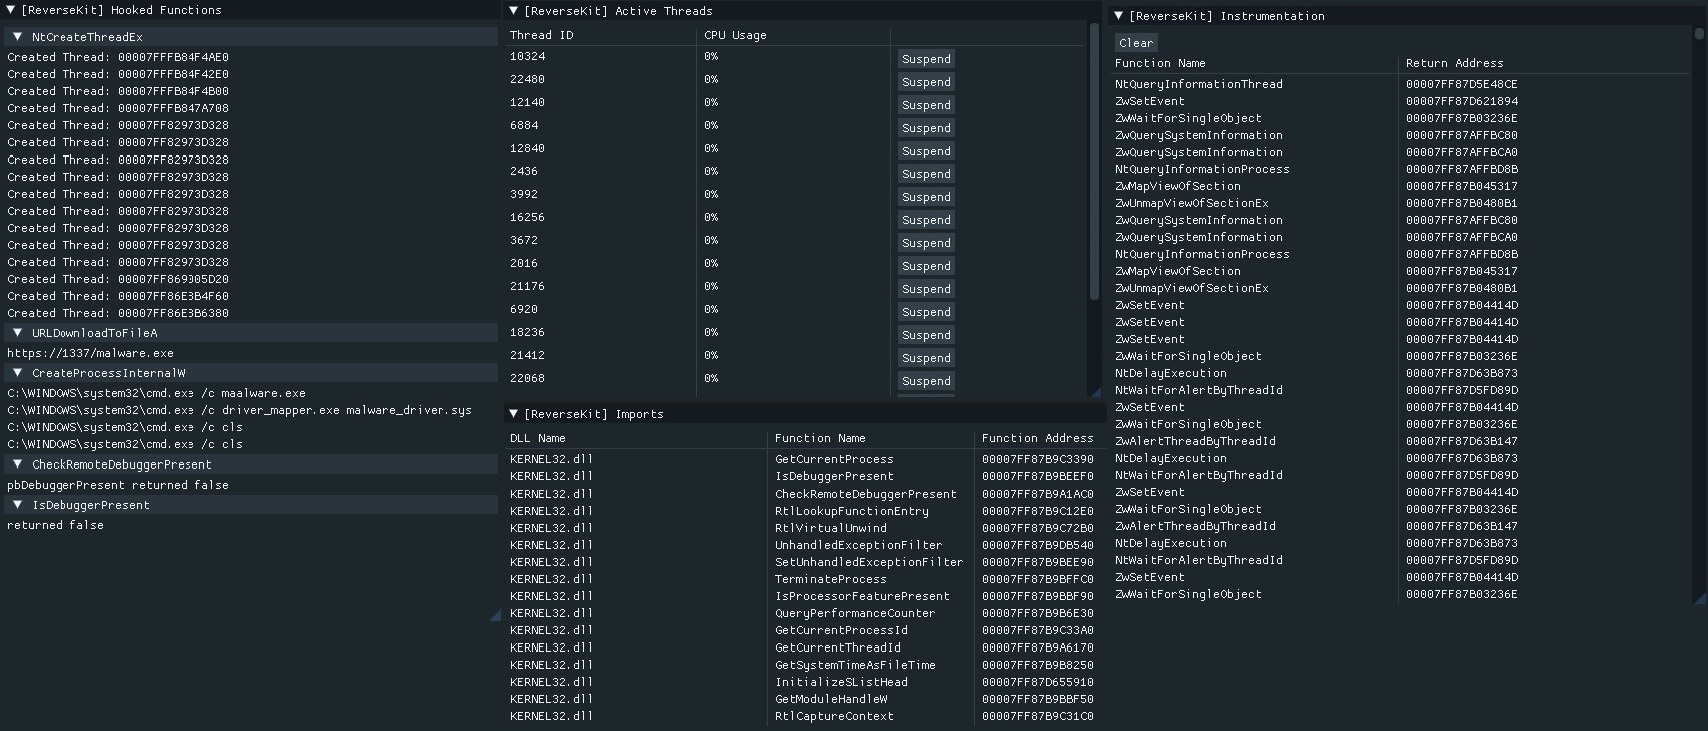 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
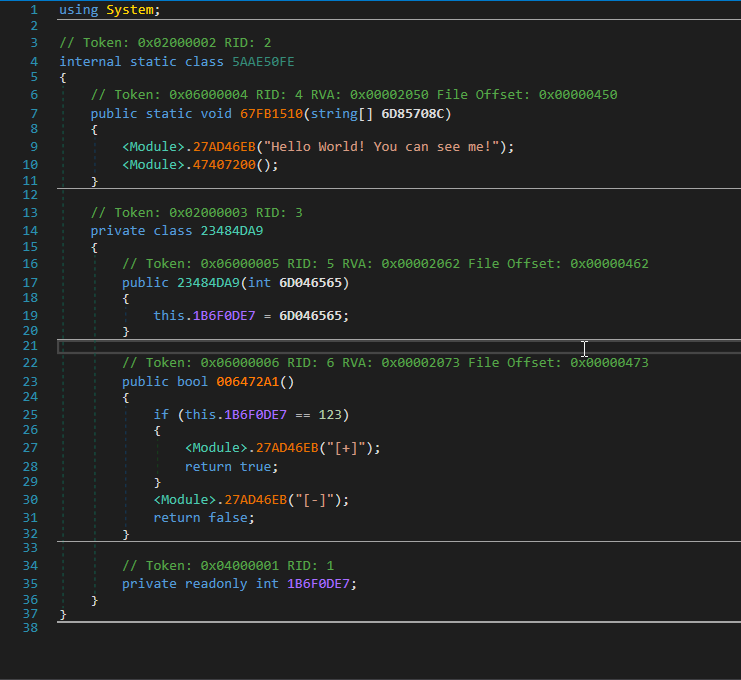 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.