Reversecore_MCP
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

A collection of android security related resources

0-day malware detection for binaries, source & scripts (that doesn't suck)

MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.

REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery


An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

An strace-like program for the Windows 'native' API

An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Mobile Edge-Dynamic Unified Security Analysis

A True Instrumentable Binary Emulation Framework

Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.

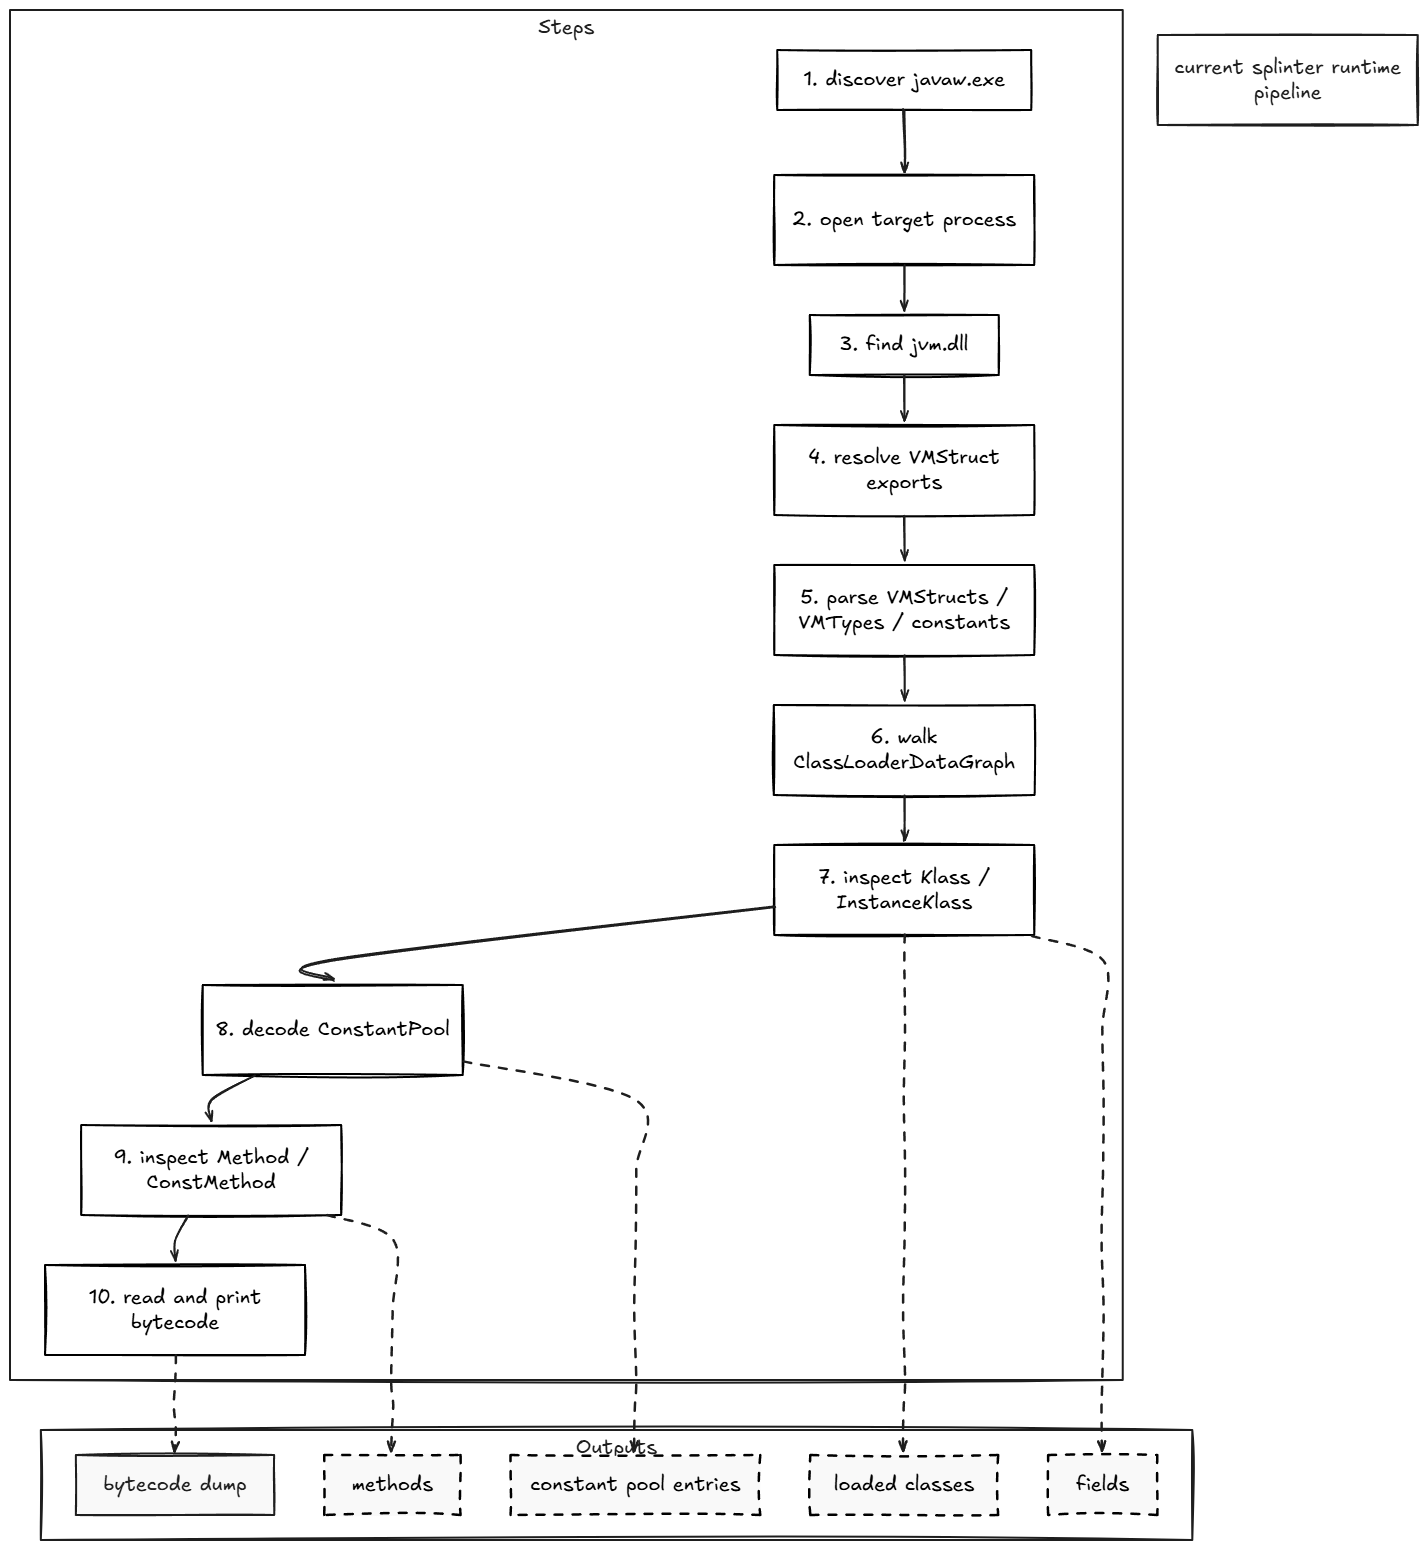
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode