
PCAPdroid
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
android-securitydns-analysiseducation+8
emanuele-f/pcapdroidNo-root network monitor, firewall and PCAP dumper for Android
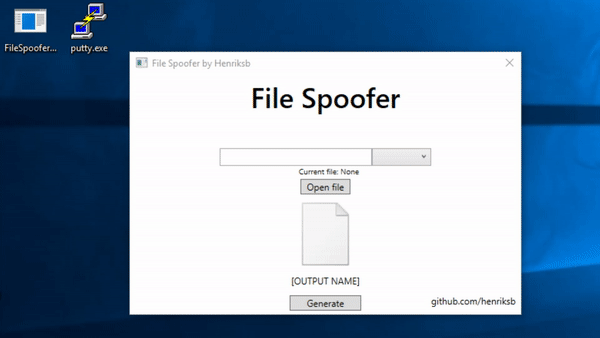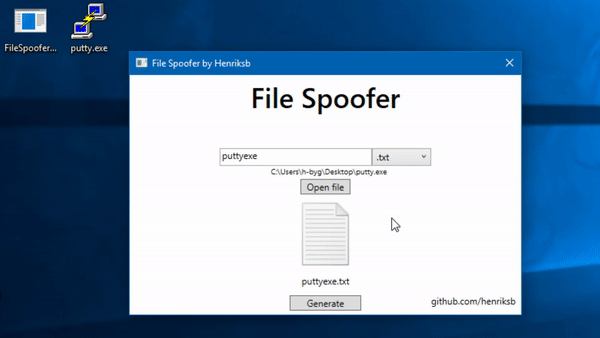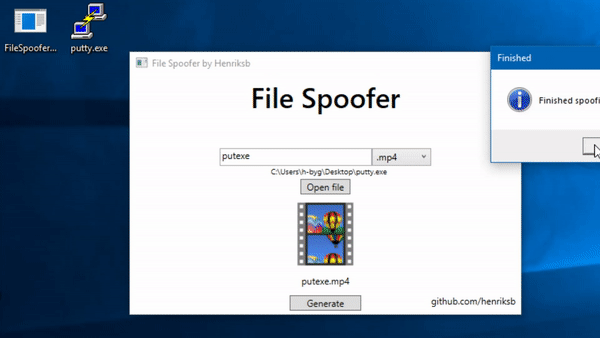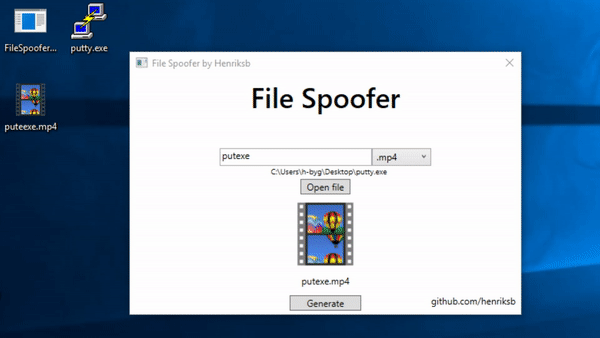 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 hassan-pouladi/cisco-fmc-honeypot
Originally a Honeypot for CVE-2026-20131
 bombadil-systems/zombie-zip
Malformed ZIP archive that evades antivirus detection by declaring Method=0 (stored) while containing DEFLATE-compressed payload.
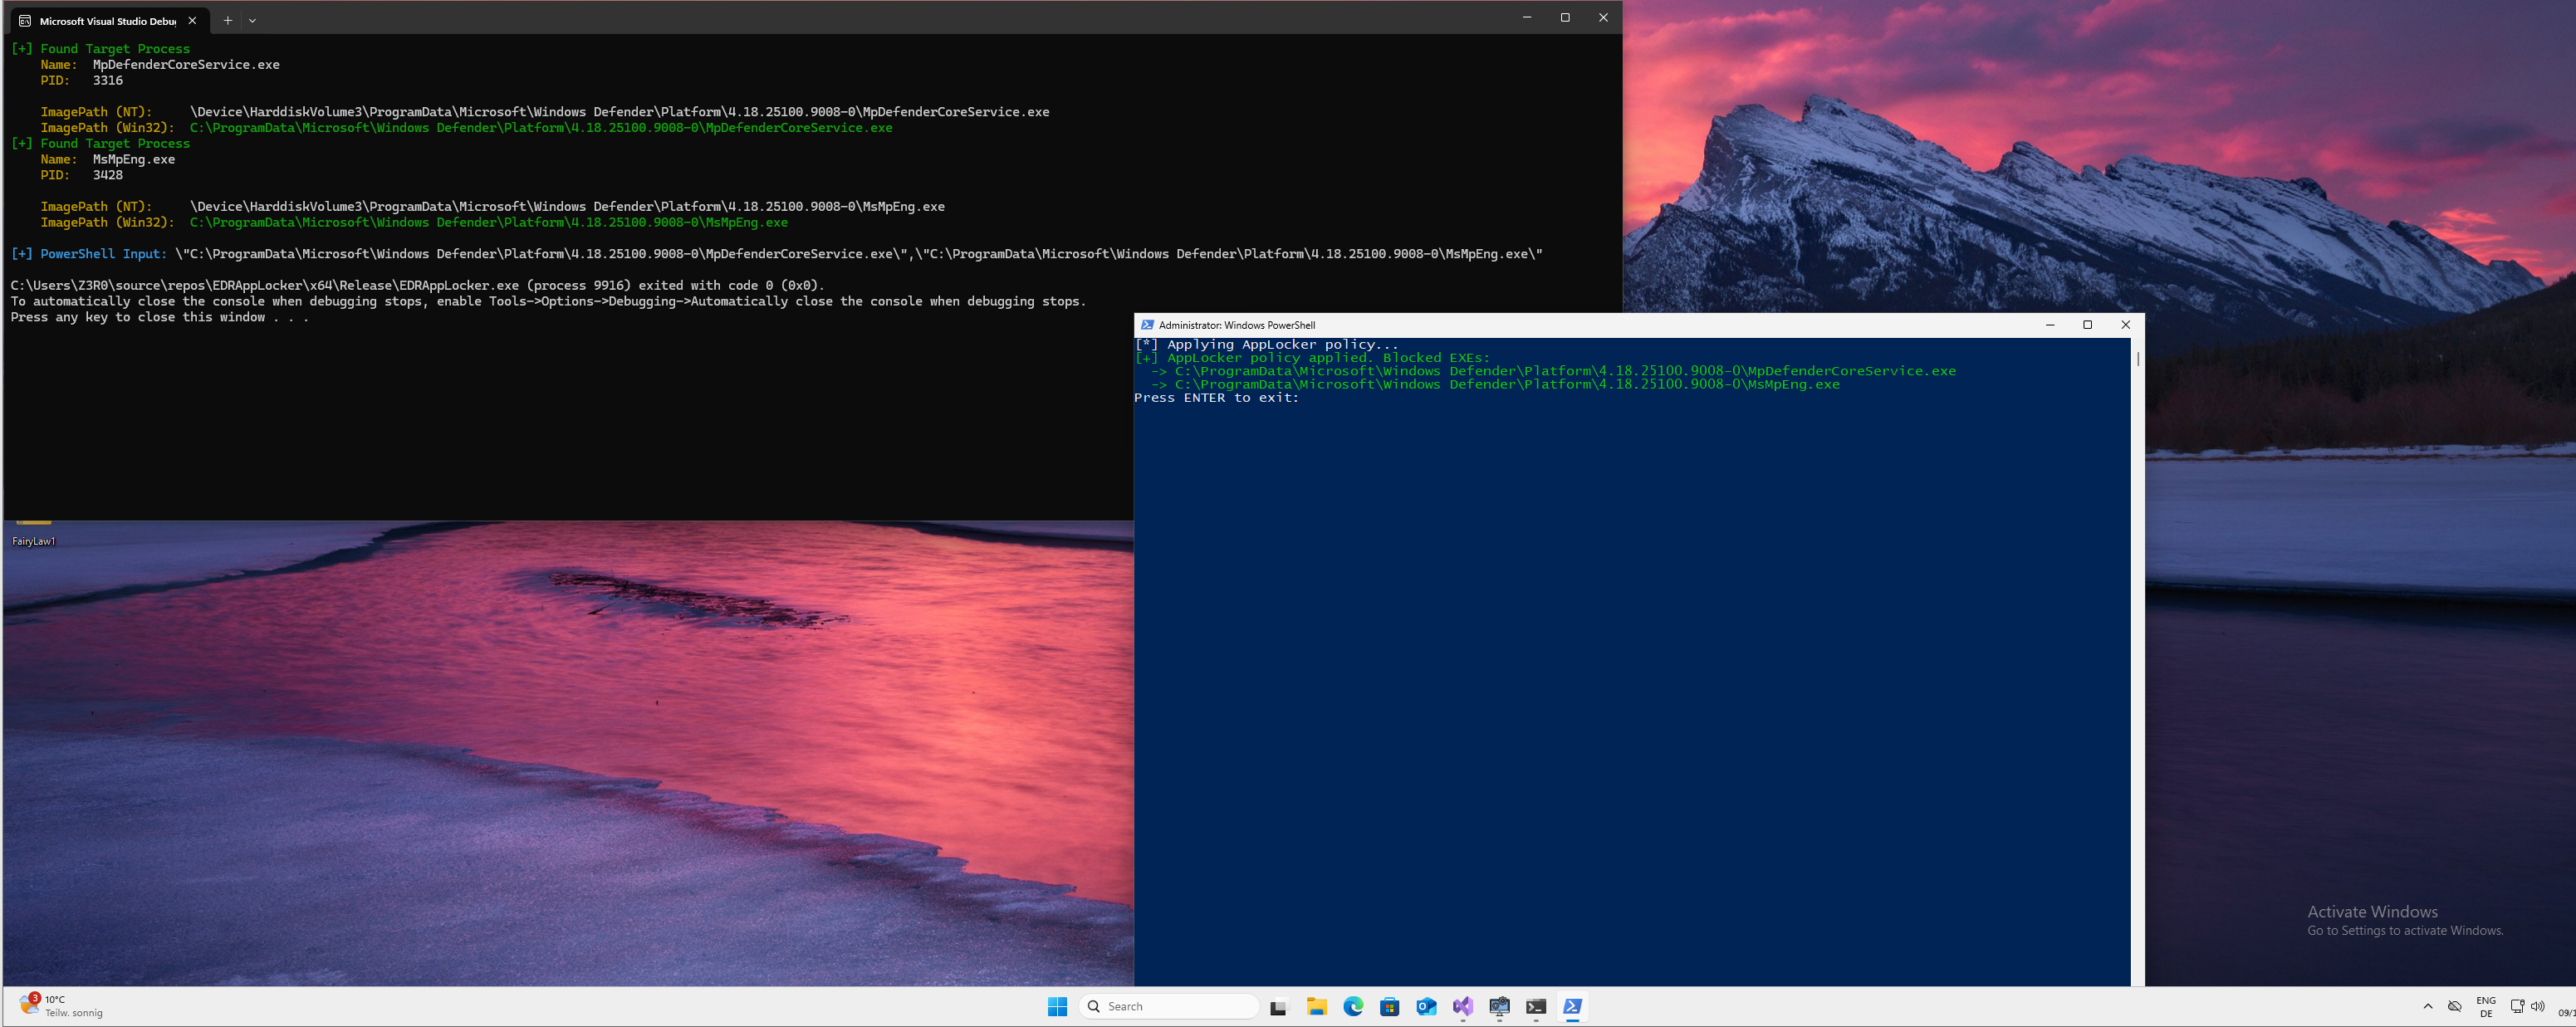 zero2504/edr-ghostlocker
AppLocker-Based EDR Neutralization
 d4rksystem/vboxcloak
A PowerShell script that attempts to help malware analysts hide their Windows VirtualBox Windows VM's from malware that may be trying to evade…
 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 therealdreg/anticuckoo
A tool to detect and crash Cuckoo Sandbox
 lsr00ter/cve-2024-21412_water-hydra
POC code according to trendmicro's research
 florylsk/execit
Execute shellcode files with rundll32
 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
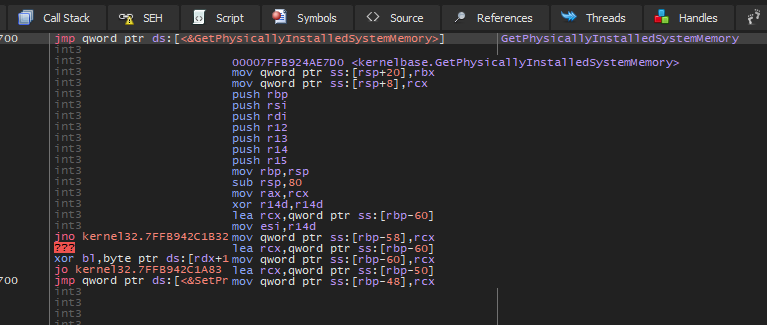 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 watchdogsecurity/ring3-kit
Hides Process From Task Manager Using NT API Hooking (NtQuerySystemInformation)
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 a3sal0n/falcongate
A smart gateway to stop cyber criminals - Sponsored by Falcon Guard
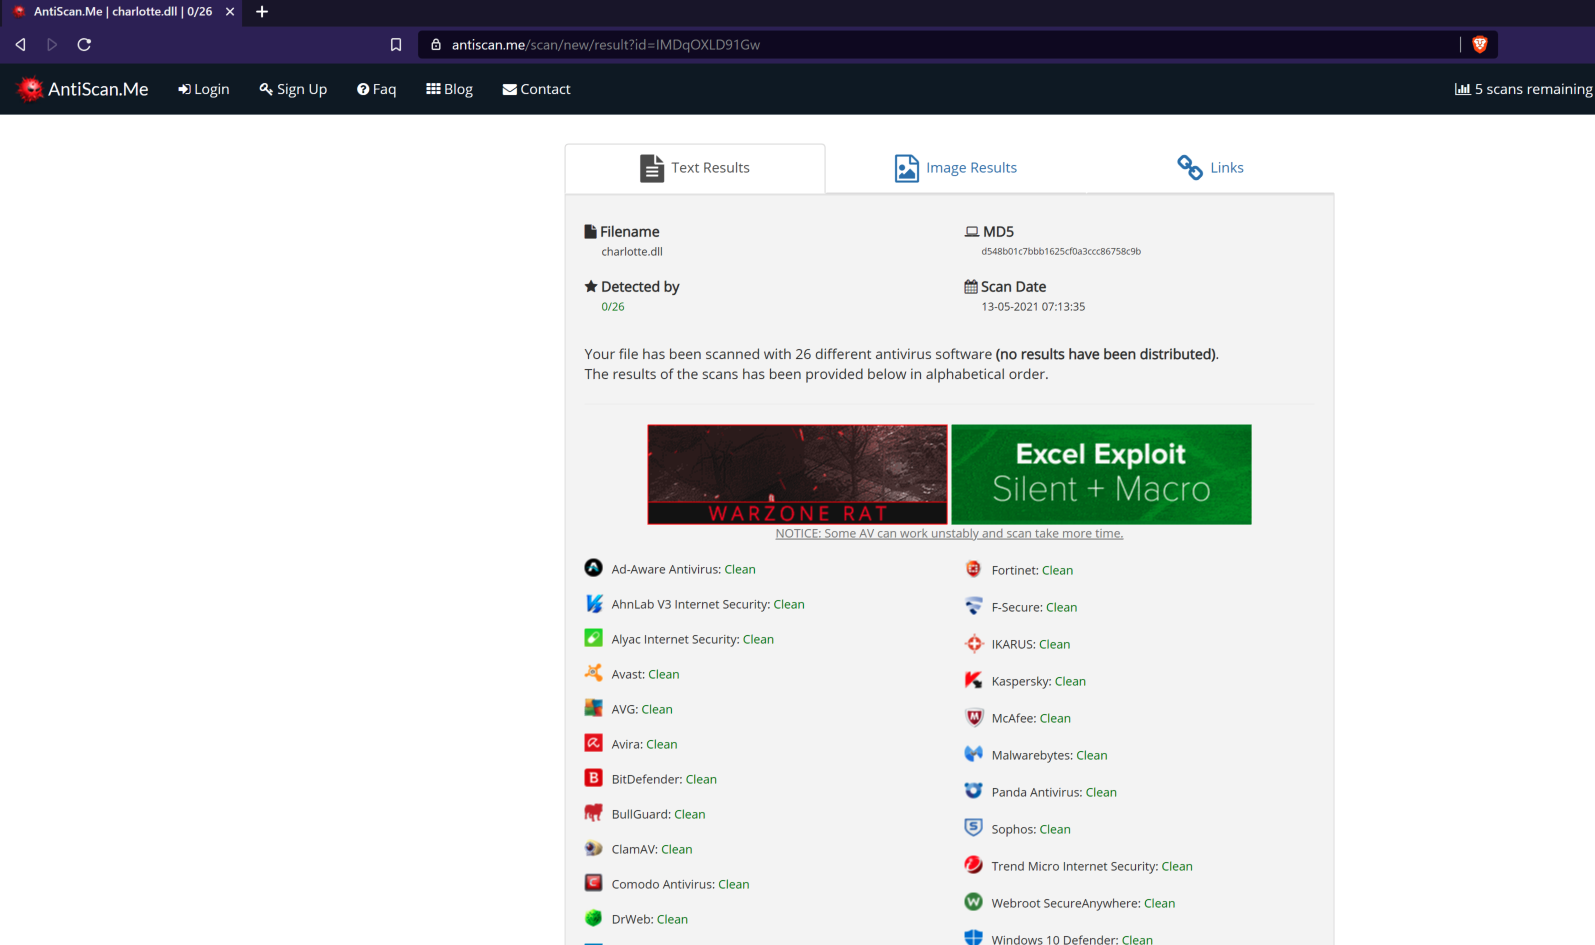 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
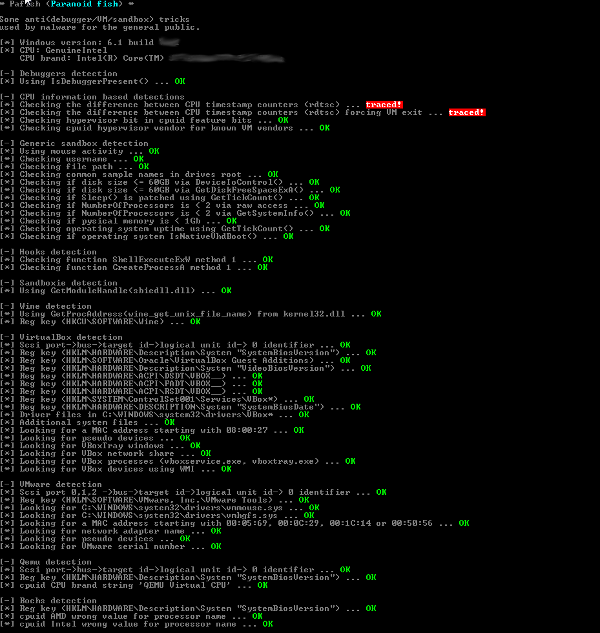 nsmfoo/antivmdetection
Script to create templates to use with VirtualBox to make vm detection harder
 benjholla/cve-2012-4681-armoring
An A/V evasion armoring experiment for CVE-2012-4681