

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
248 results
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k
4h 59m ago
magika preview

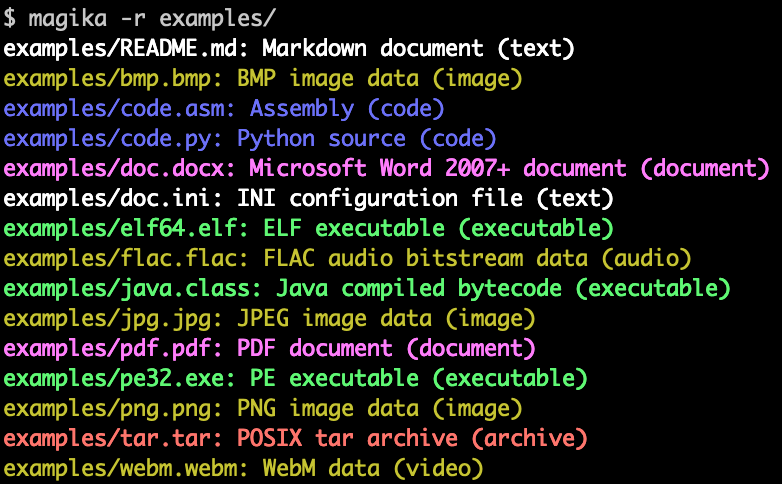
magika

GitHubgoogle/magika

Fast and accurate AI powered file content types detection

code-analysisforensicsgeneral-purpose-utilities+3
17.9k9h 36m ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.2k10h 55m ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
15.6k12h 43m ago
pe-bear preview

pe-bear

GitHubhasherezade/pe-bear

Portable Executable reversing tool with a friendly GUI

binary-analysisforensicsmalware-analysis+3
3.8k20h 15m ago
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.3k1 day ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
351 day ago
guarddog preview

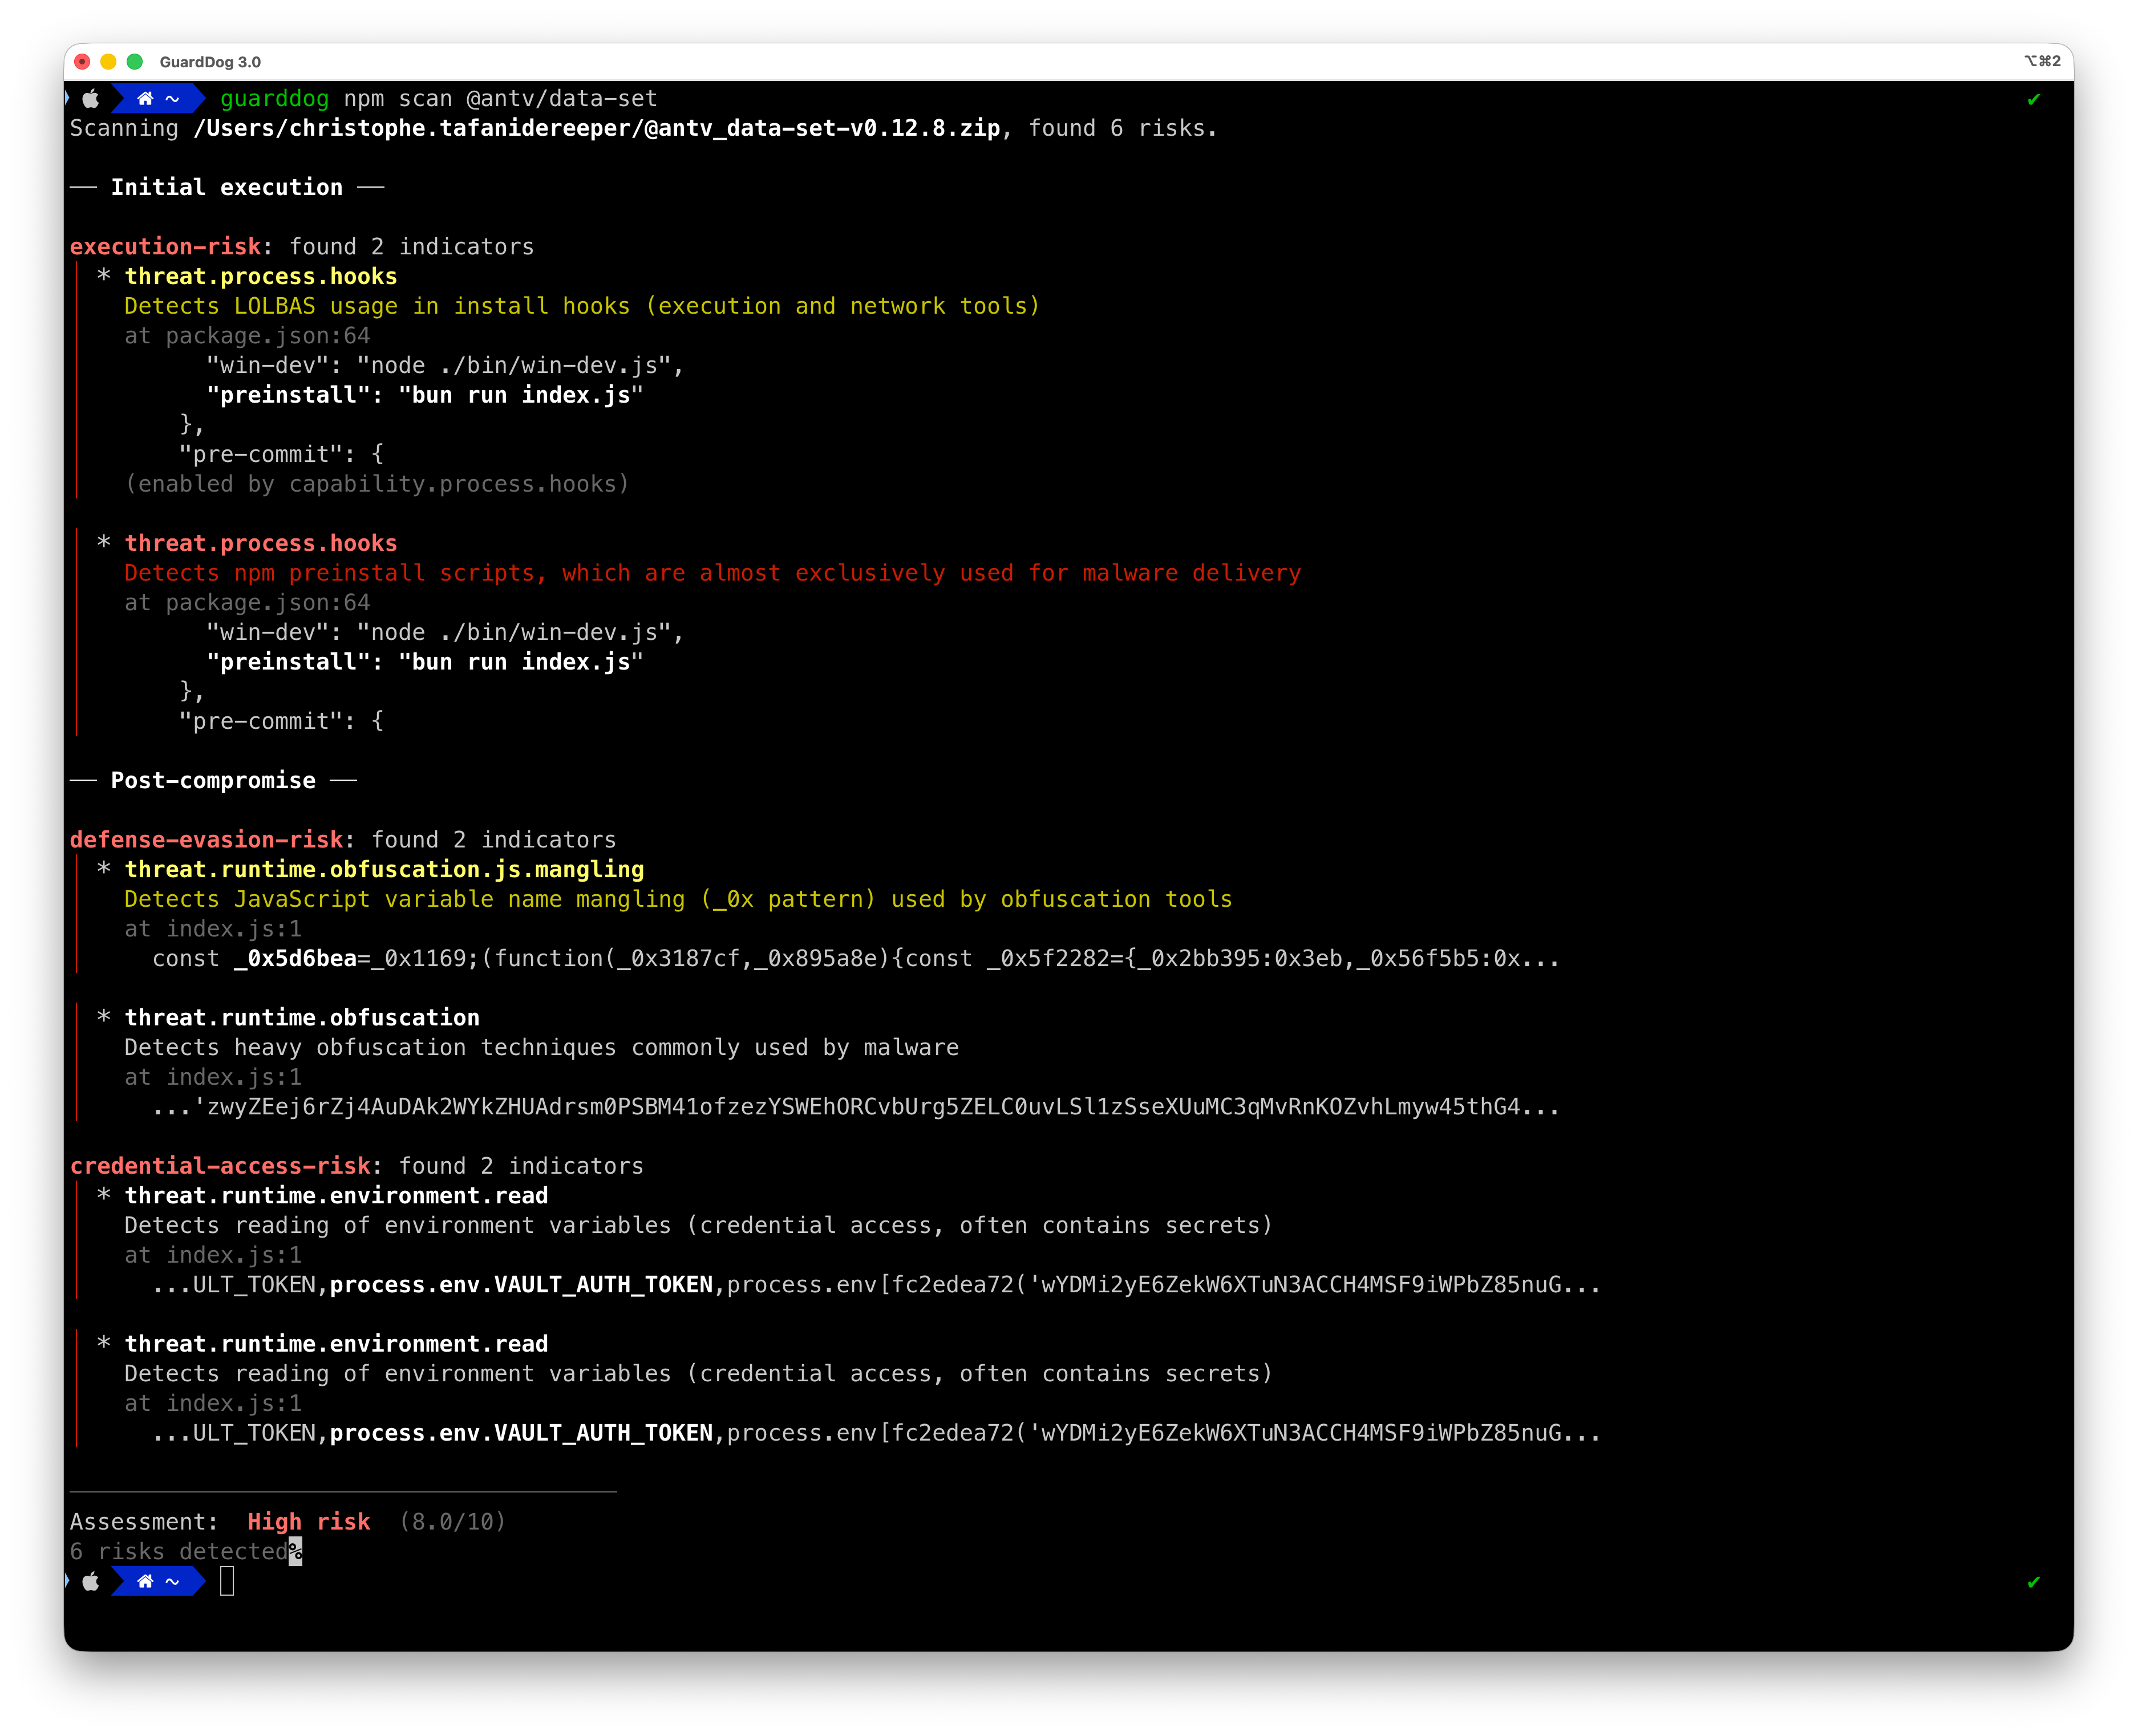
guarddog

GitHubdatadog/guarddog

🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
code-analysisdevsecopsdynamic-analysis-sandboxing+6
1.2k1 day ago
mac-monitor preview

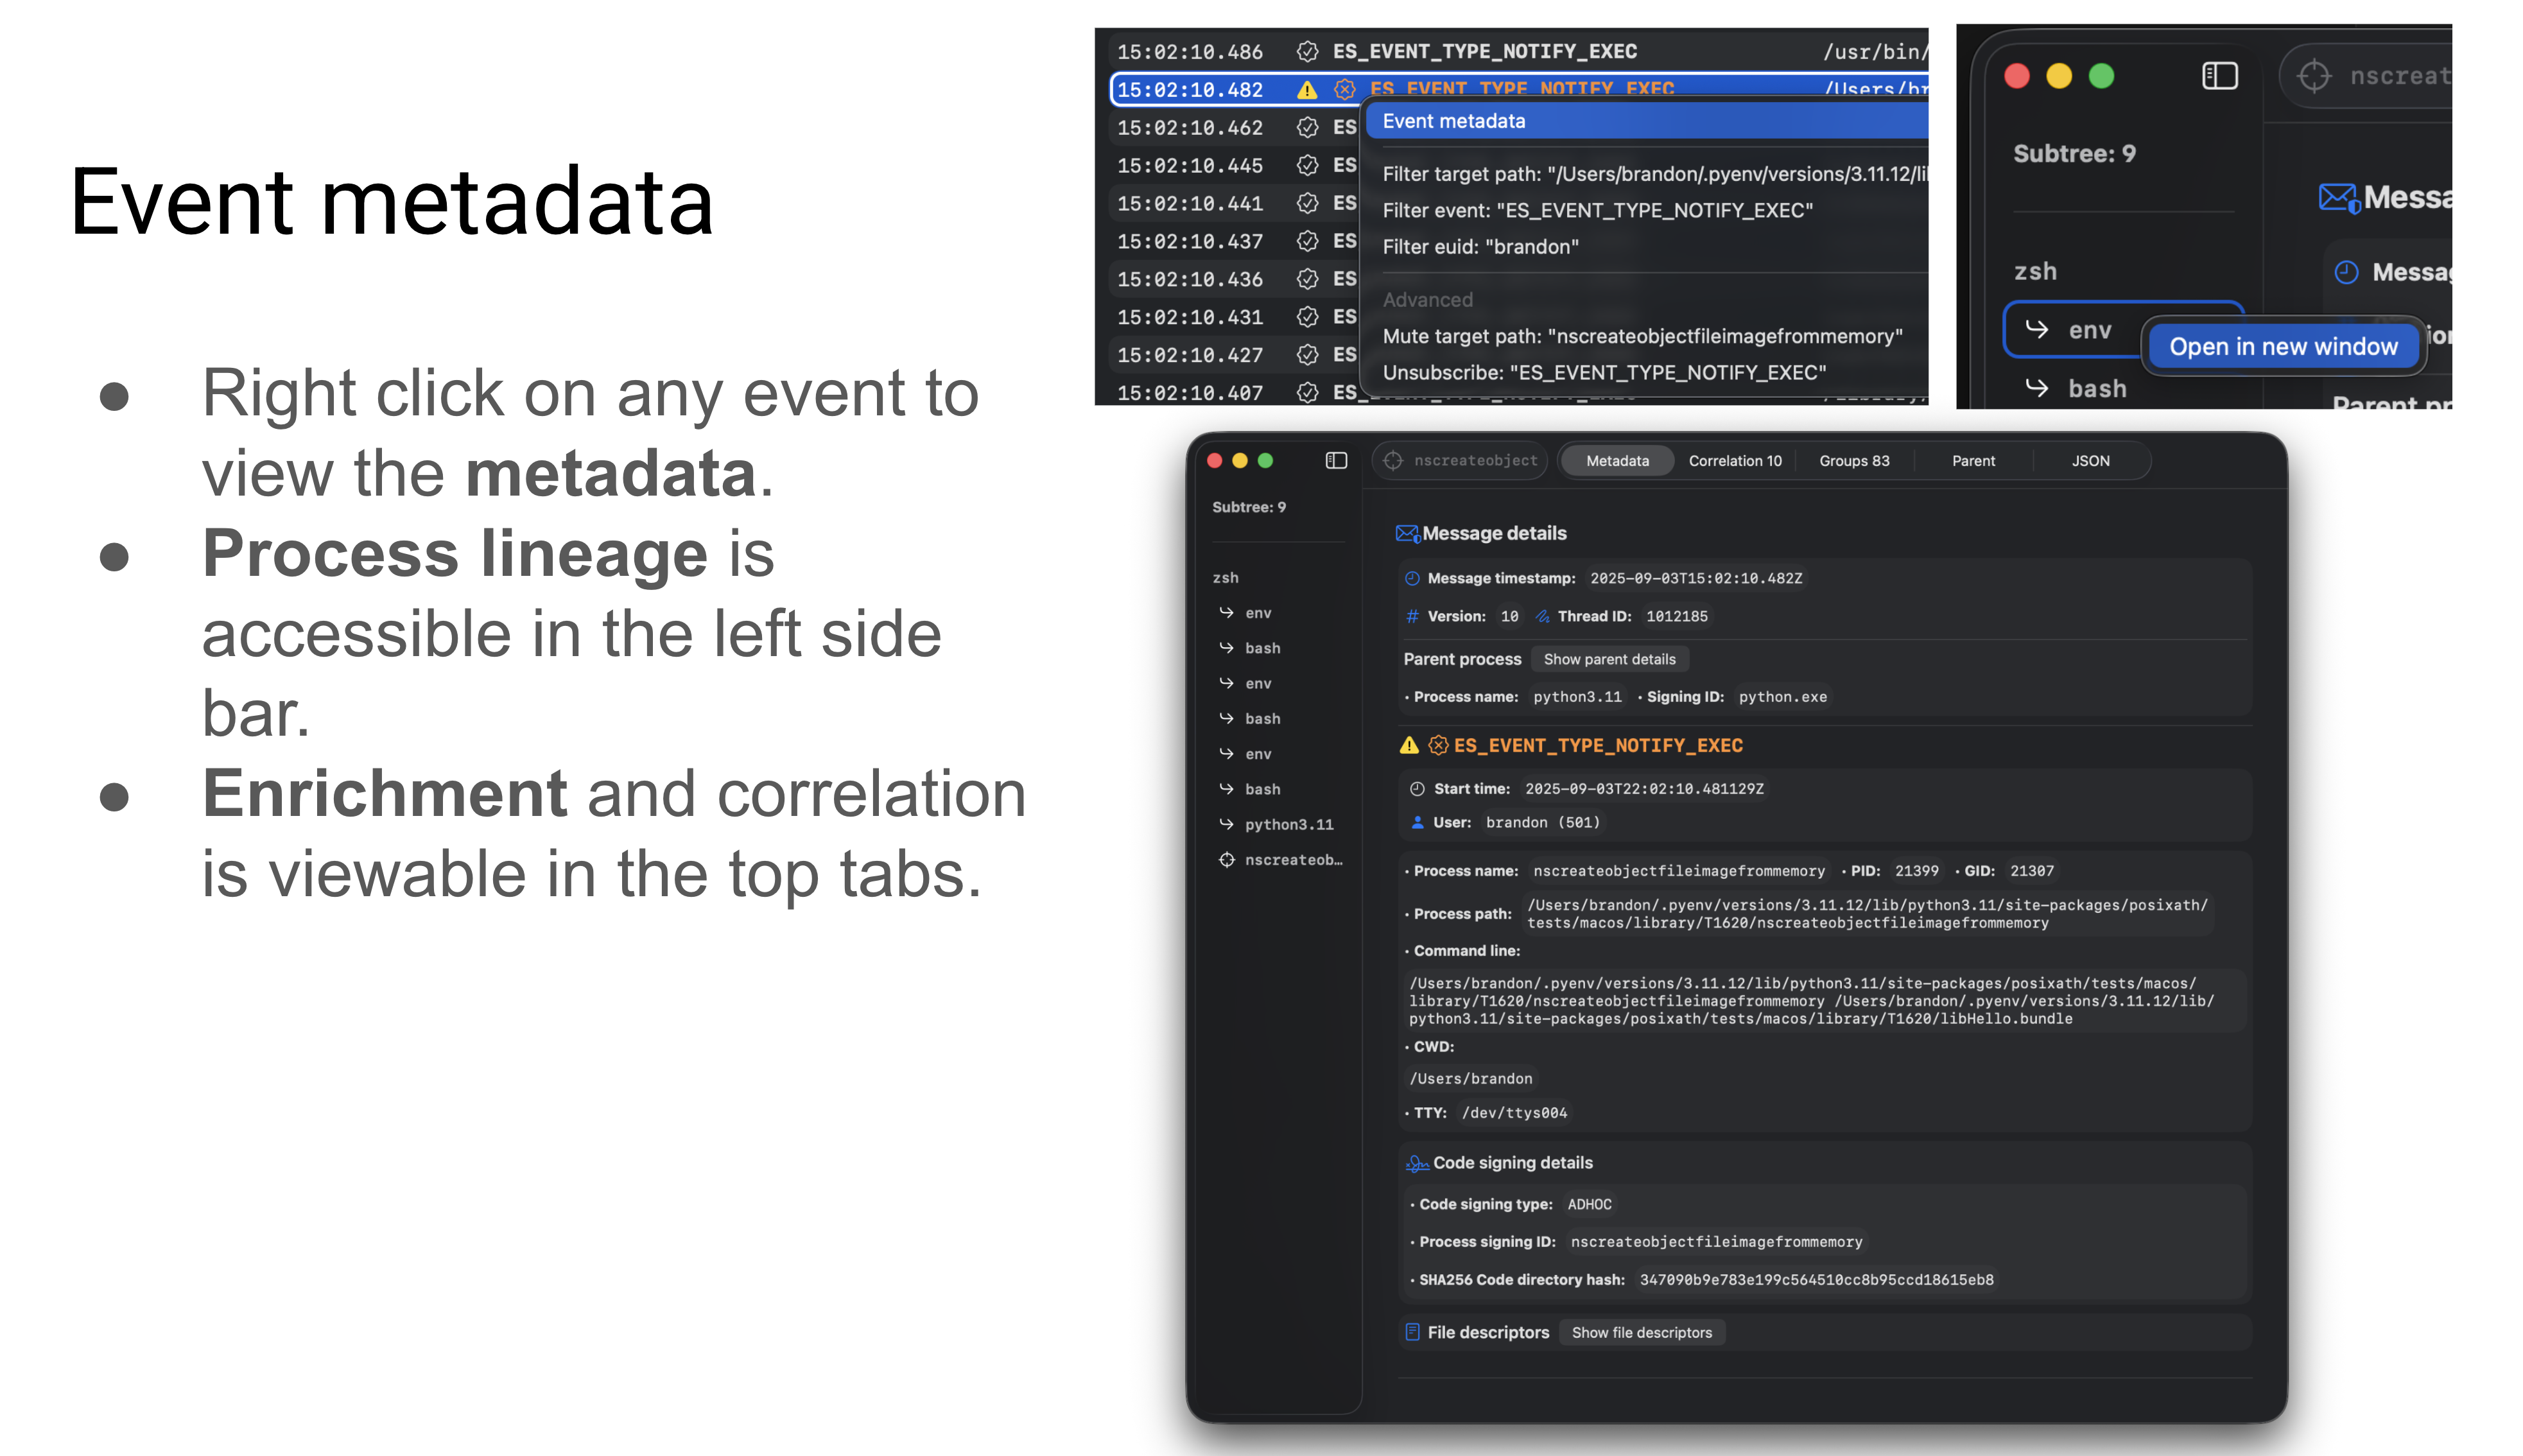
mac-monitor

GitHubbrandon7cc/mac-monitor

Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
dynamic-analysis-sandboxingeducationforensics+2
1.4k1 day ago
misp-galaxy preview

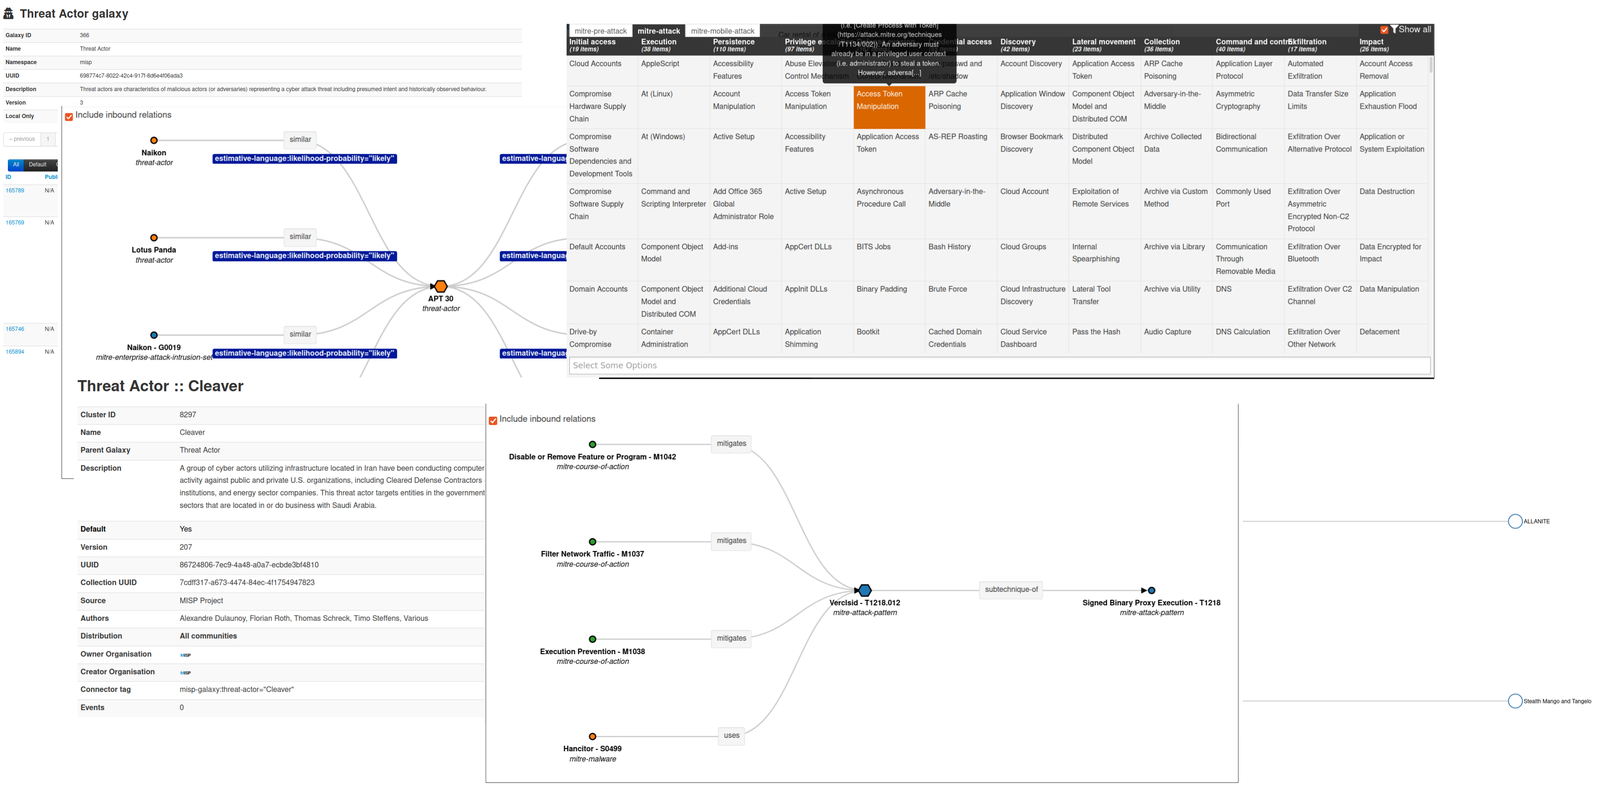
misp-galaxy

GitHubmisp/misp-galaxy

Clusters and elements to attach to MISP events or attributes (like threat actors)

adversarial-attackcurated-resourcesioc-management+5
6501 day ago
Information-Security-Tasks preview

Information-Security-Tasks

GitHubbb1nfosec/information-security-tasks

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…
curated-resourcesdigital-forensicseducation+9
1882 days ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool
debuggersdynamic-analysis-sandboxingincident-response+2
3.1k6 days ago
unthemidator preview

unthemidator

GitHubx86rc/unthemidator

An automated Themida / Code Virtualizer / WinLicense (v3.0-v4) unpacker and dump fixer tool

binary-analysisbinary-exploitationdebuggers+4
3866 days ago
ReArk preview

ReArk

GitHublkimuk/reark

An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
ai-assisted-reversingandroid-securitybinary-analysis+6
8946 days ago
elegant-bouncer preview

elegant-bouncer

GitHubmsuiche/elegant-bouncer

ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

binary-analysisdigital-forensicsios-security+4
1776 days ago
yara preview

yara

GitHubvirustotal/yara

The pattern matching swiss knife

forensicsmalware-analysisstatic-analysis+2
9.8k7 days ago
rea-rust preview

rea-rust

GitHubnanashili/rea-rust

Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker

ai-assisted-reversingbinary-analysisdebuggers+7
718 days ago
voidsyscall preview

voidsyscall

GitHubvoidsecsoftwares/voidsyscall

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

command-and-controlencryption-decryption-toolsids-ips-evasion+9
689 days ago
Previous12…14Next

