

javascript-deobfuscator
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
code-analysisdynamic-code-analysismalware-analysis+4
2
lolcaken/javascript-deobfuscatorDeobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
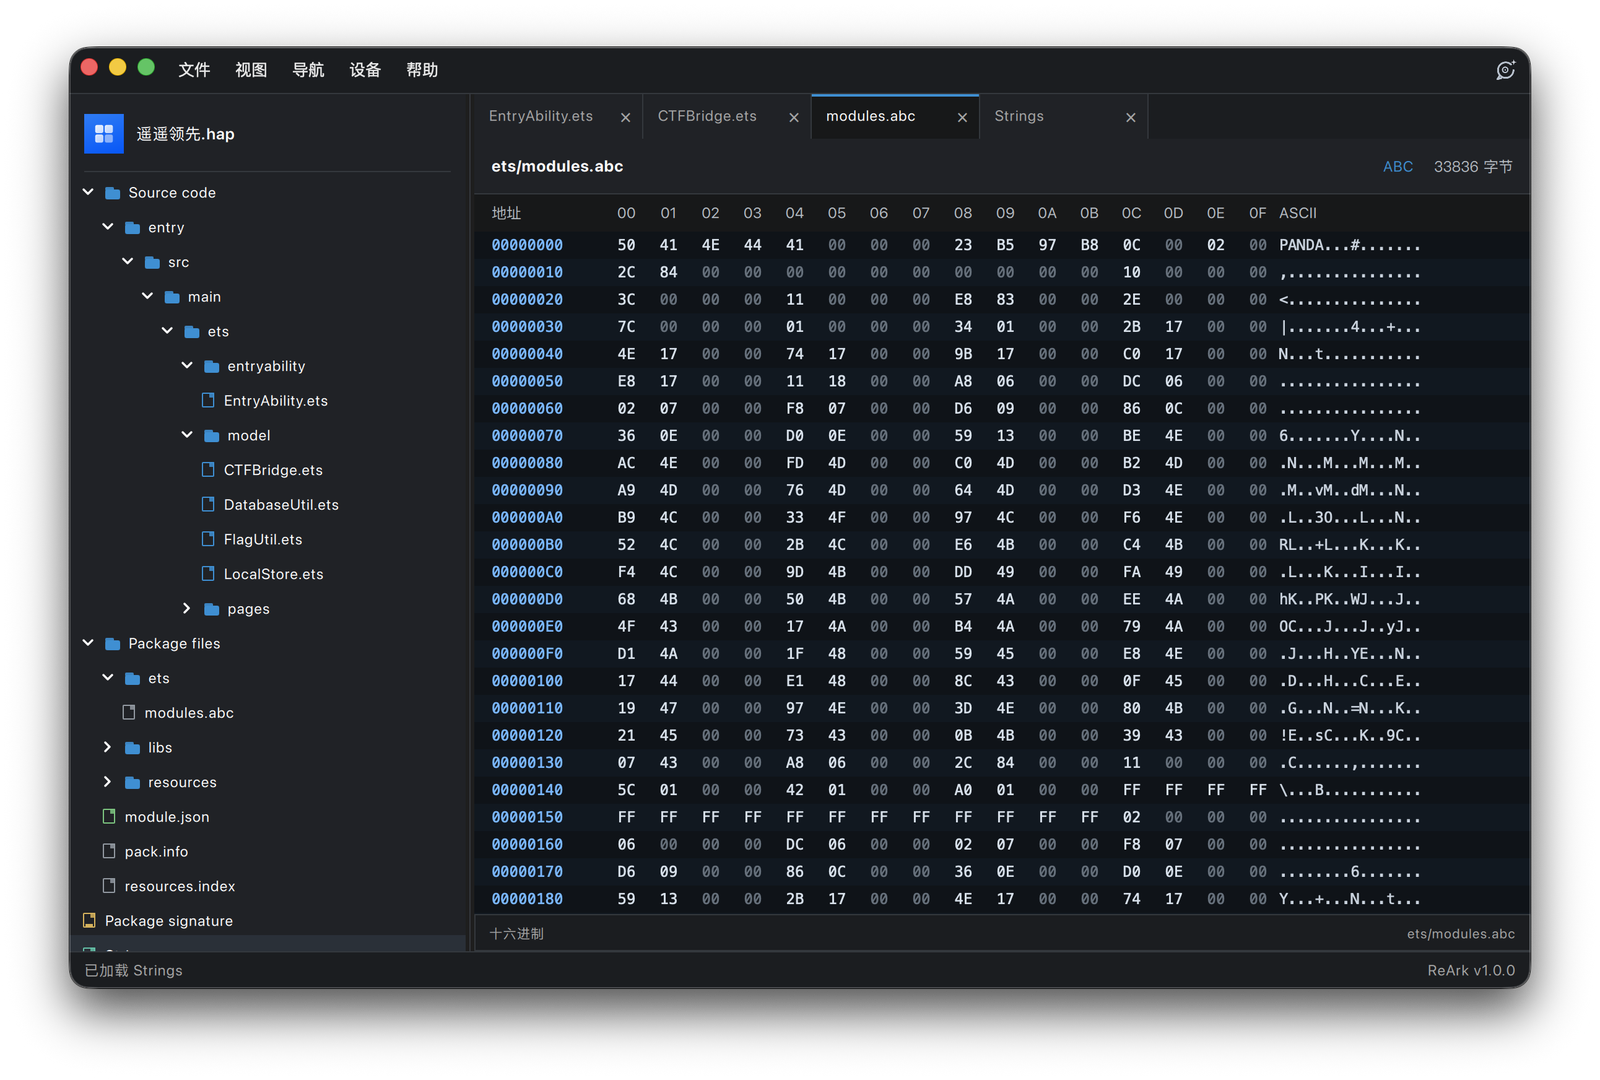 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 eddinos2/cve-2026-28956-jxl-messages-surface
iOS Messages JPEG XL delivery-surface probe and patch-diff notes for CVE-2026-28956.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 hackpatato/cve-2026-33057---mesop-unauthenticated-rce-poc-and-yara-rules
Proof-of-concept exploit for CVE-2026-33057, an unauthenticated RCE in Mesop, with accompanying YARA rules for detection.
 hackpatato/poc-and-yara-rules-of-cve-2025-59528-flowise-has-remote-code-execution-vulnerability
Proof-of-concept exploit and YARA detection rules for CVE-2025-59528, a remote code execution vulnerability in Flowise, intended for authorized…
 perl-code/cve-2026-5000
Proof-of-concept demonstrating a Windows Defender bypass technique for CVE-2026-5000, intended for controlled testing and defensive research.
 xuedugu/cve-2024-7965-poc
CVE-2024-7965是Google Chrome浏览器中V8 JavaScript引擎的一个高危漏洞。该漏洞源于V8引擎在处理特定JavaScript代码时实现不当,导致堆内存损坏。攻击者可通过诱导用户访问包含特制JavaScript的恶意网页,利用此漏洞在Chrome渲染器中执行任意代码。