
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts
digital-forensicsforensicsincident-response+2
339
2 years ago
freedomfighting preview

freedomfighting

GitHubjusticerage/freedomfighting

A collection of scripts which may come in handy during your freedom fighting activities.

crawlerencryption-decryption-toolsforensics+8
4183 years ago
scripts preview

scripts

GitHubclausing/scripts

Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
842 days ago
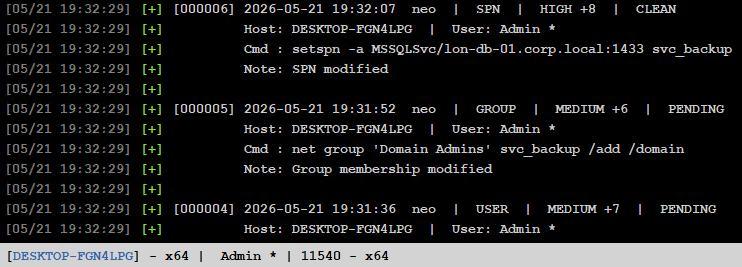
Ledger preview

Ledger

GitHubshellkraft/ledger

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
command-and-controlincident-responselog-analysis+5
294 months ago
Leaktopus preview
Archived

Leaktopus

GitHubplaytikaoss/leaktopus

Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
code-analysisdevsecopsincident-response+6
296 months ago
Threat-Remediation-Scripts preview

Threat-Remediation-Scripts

GitHubxephora/threat-remediation-scripts

This repository contains a list of new remediation scripts.
defensive-toolsdigital-forensicsincident-response+5
2051 day ago
ZeroLogon-Exploitation-Check preview

ZeroLogon-Exploitation-Check

GitHubyossisassi/zerologon-exploitation-check

quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…
exploitationincident-responseinformation-gathering+3
75 years ago
ThreatSentry-AI preview

ThreatSentry-AI

GitHubeclipsemanic/threatsentry-ai

ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
defensive-toolsincident-responseinformation-gathering+6
18 months ago
rip_raw preview
Archived

rip_raw

GitHubcado-security/rip_raw

Rip Raw is a small tool to analyse the memory of compromised Linux systems.
data-recoverydigital-forensicsforensics+3
1334 years ago
DeTTECT preview

DeTTECT

GitHubrabobank-cdc/dettect

Detect Tactics, Techniques & Combat Threats

defensive-toolsincident-responseintrusion-detection+4
2.3k26 days ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

anomaly-detectiondigital-forensicsincident-response+5
7381 month ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

anomaly-detectioncommand-and-controldns-analysis+4
6583 months ago
Purple-Team-Automation preview

Purple-Team-Automation

GitHubjoshuagodwin7929/purple-team-automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
adversarial-attackcommand-and-controlincident-response+6
5315 days ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
1592 years ago
mongobleed-detector preview

mongobleed-detector

GitHubneo23x0/mongobleed-detector

Detection Script for MongoBleed Exploitation

database-securitydigital-forensicsforensics+5
829 months ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

anomaly-detectiondefensive-toolsincident-response+6
211 days ago
SonicWall-SMA1000-Zero-Day-IoC-Check preview

SonicWall-SMA1000-Zero-Day-IoC-Check

GitHubmrrawbit/sonicwall-sma1000-zero-day-ioc-check

Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.
exploitationforensicsincident-response+5
2 months ago
Zircolite preview

Zircolite

GitHubwagga40/zircolite

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs

forensicsincident-responselog-analysis+1
8581 day ago
Previous12Next