

ThreatLens
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
defensive-toolsincident-responseinformation-gathering+7
25
abdaullahag/threatlensPython CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 9 more ran, and flags risky actions and leaked…
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
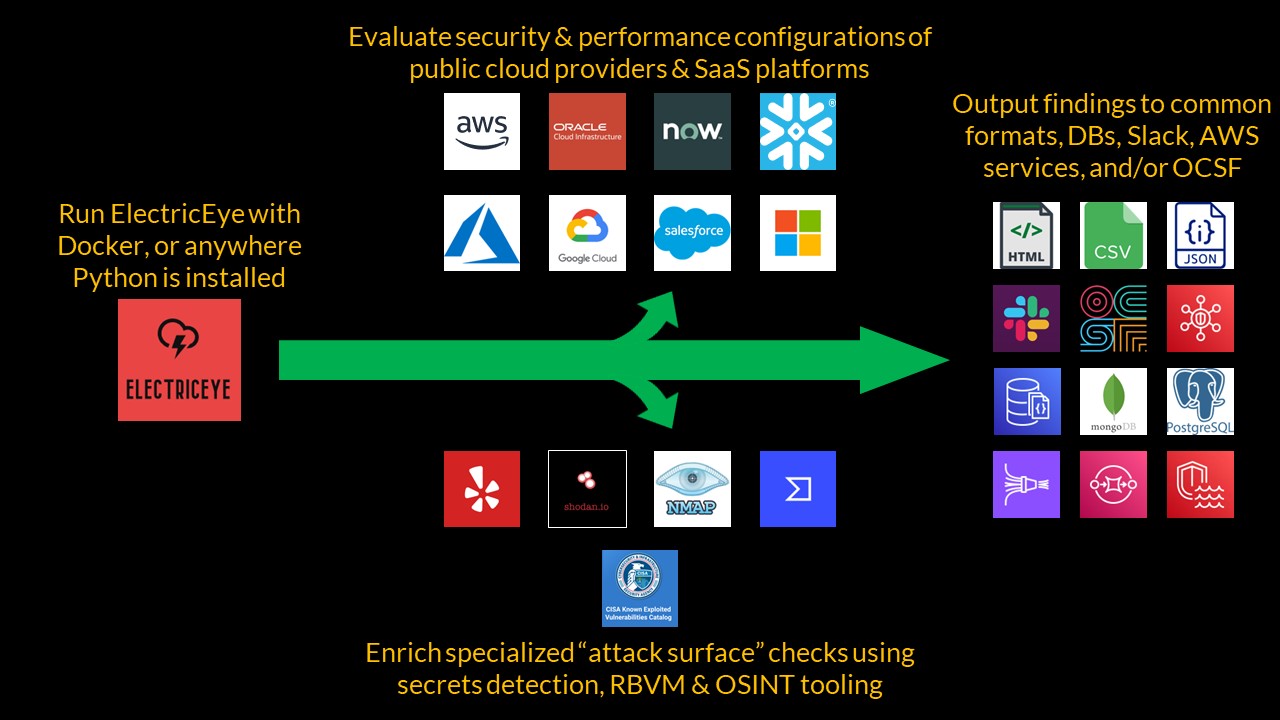 jonrau1/electriceye
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 itskill-jp/wordpress-upgrade-check
Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 jdormannn/secureops-lab
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…
 hasecuritysolutions/vulnwhisperer
Create actionable data from your Vulnerability Scans
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting
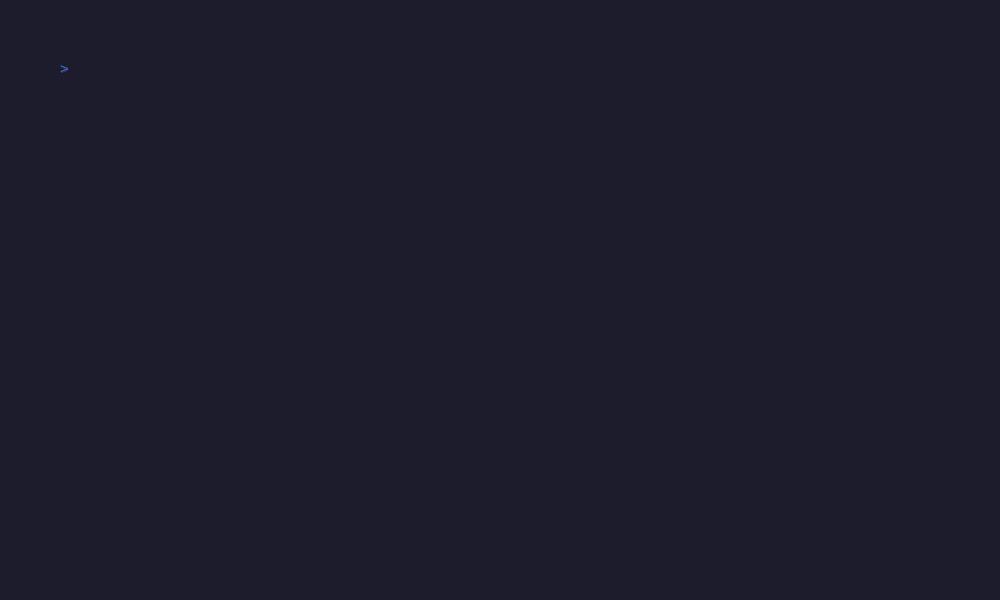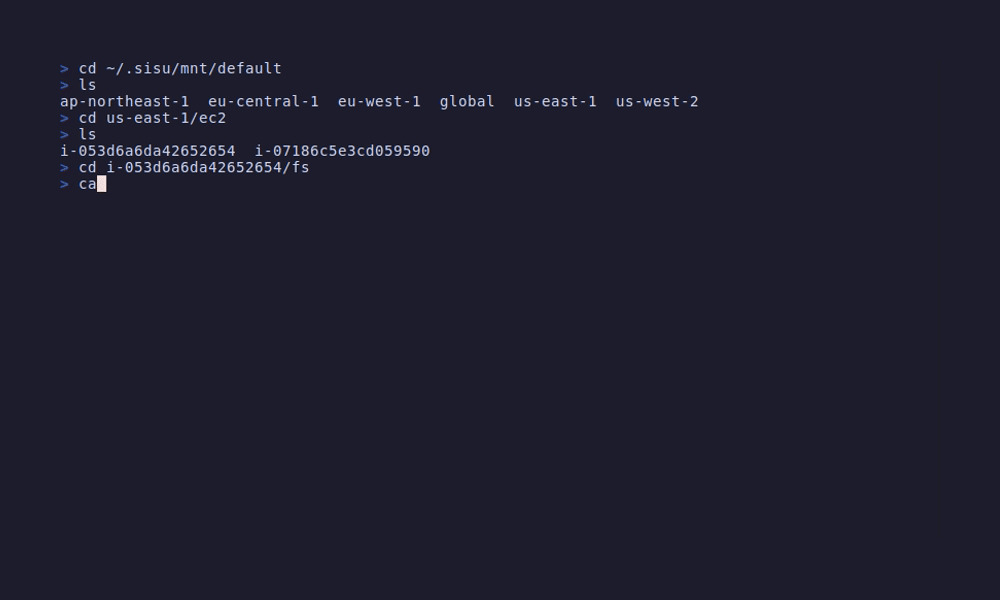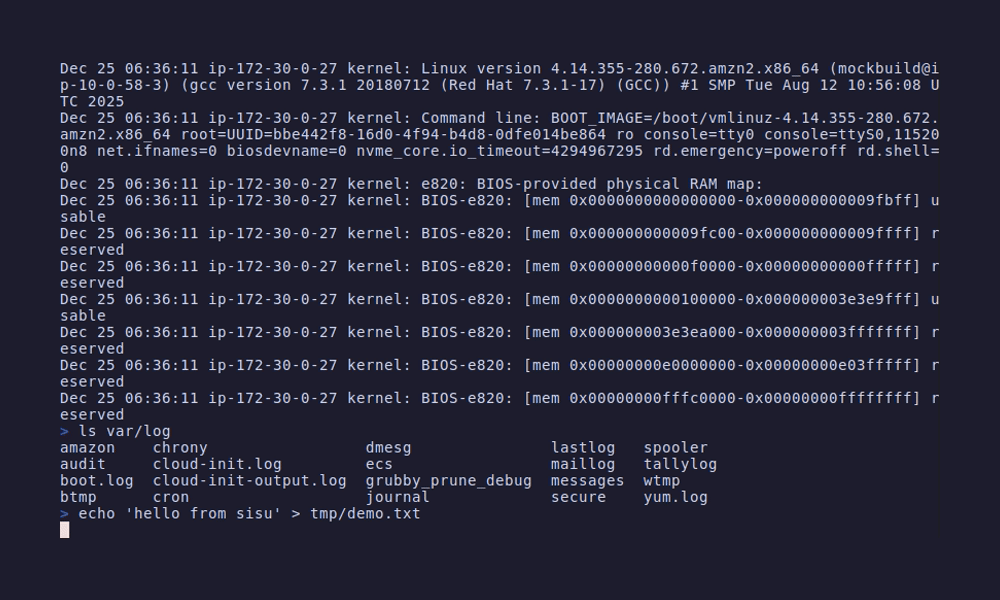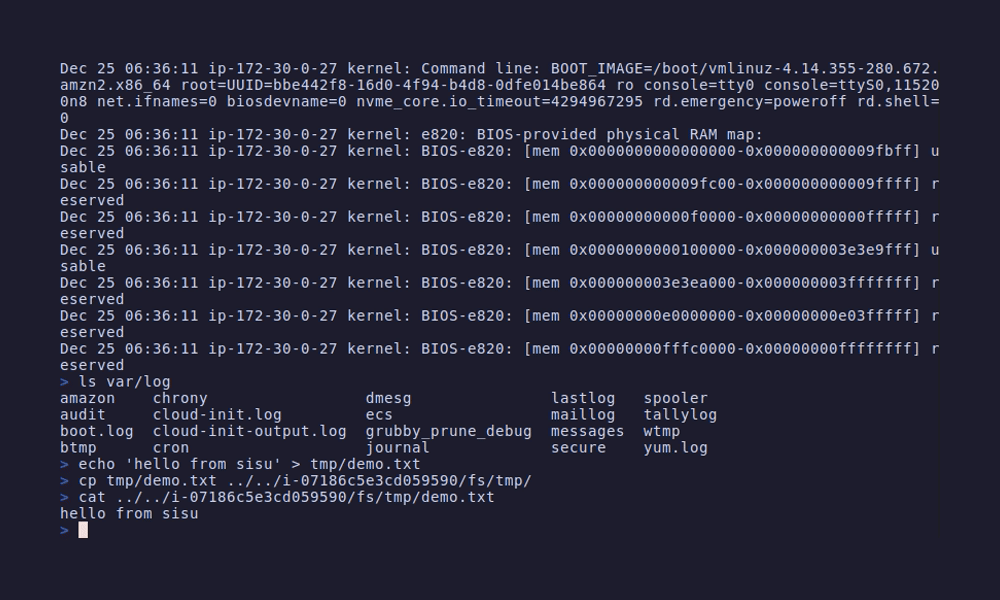 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 trinadh465/external_tcpdump_cve-2018-14880
Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…