Archived

 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 raj3shp/malscore
Maliciousness scoring for Linux commands
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
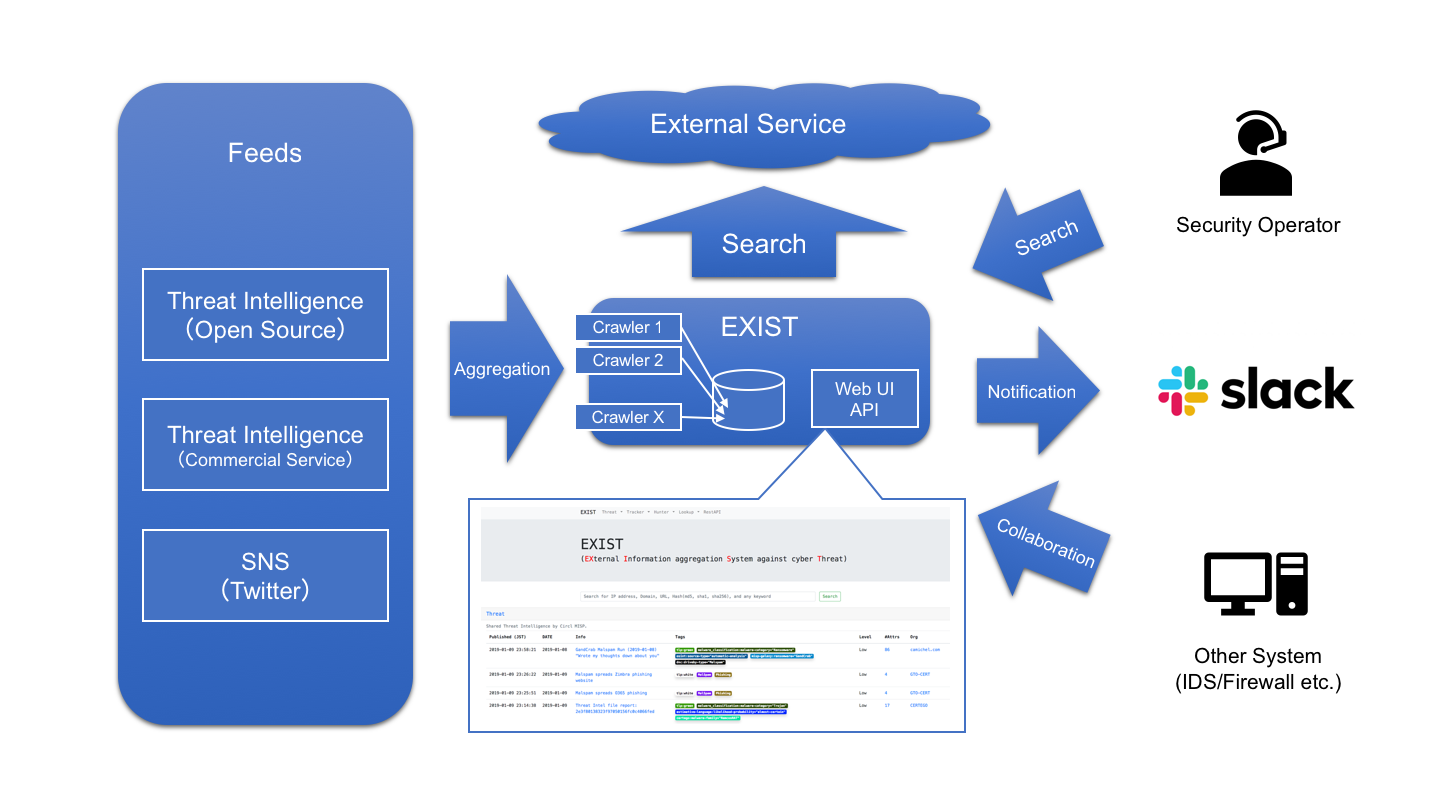 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 treussart/probemanager
Centralize Management of Intrusion Detection System like Suricata Bro Ossec ...
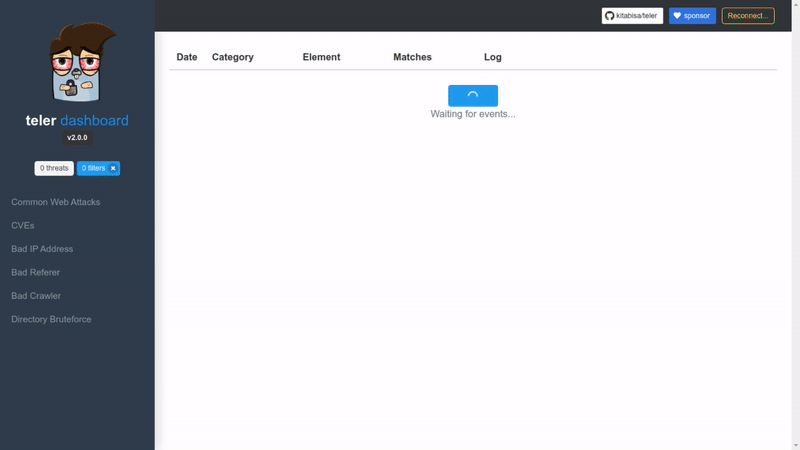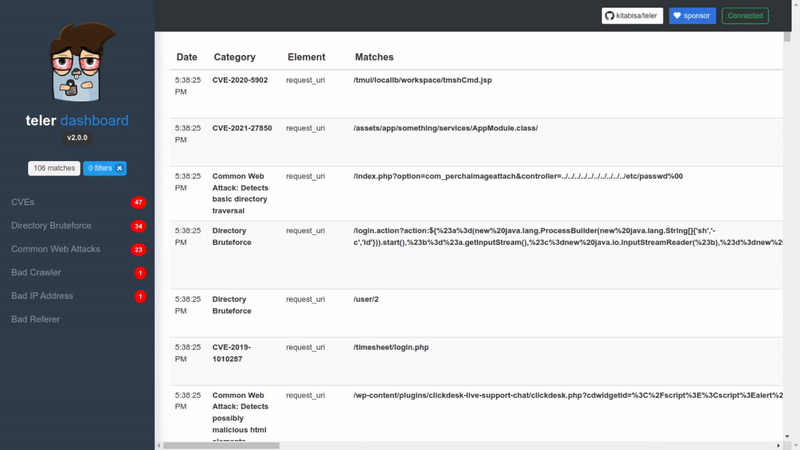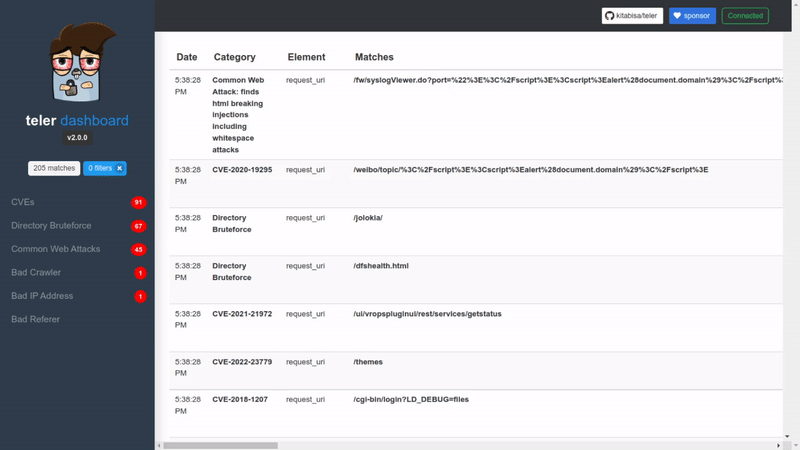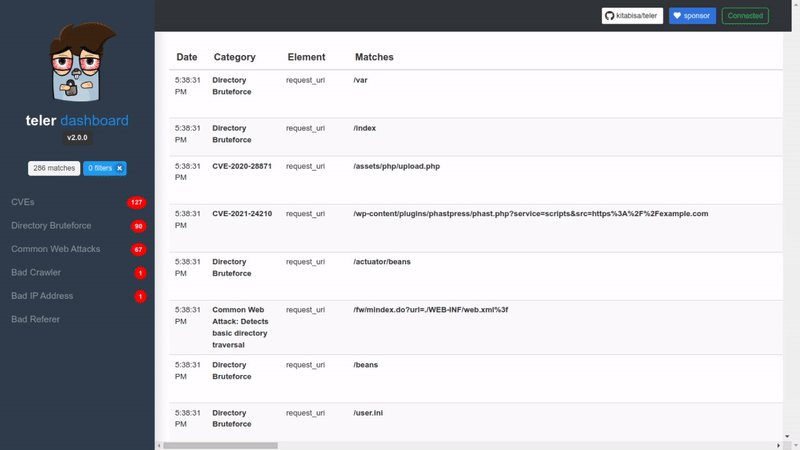 teler-sh/teler
Real-time HTTP Intrusion Detection
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints

 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 tnich/honssh
HonSSH is designed to log all SSH communications between a client and server.
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…