 teler-sh/teler
Real-time HTTP Intrusion Detection

[!IMPORTANT]
Dear users,We wanted to share some important updates regarding the development of teler IDS.
🛑 The development of teler IDS is currently on hold. However, we're thrilled to inform you that we've decided to take a bold step by embarking on a complete refactor, starting from scratch to enhance the overall development process. 🚀
In parallel, we're actively laying down the roadmap for teler IDS v3. 📝
What we can reveal at this point is that version 3 will leverage eBPF & teler-waf as its support, promising advanced features and capabilities. 🌟If you have feedback or suggestions regarding the features you'd like to see in teler IDS v3, kindly participate in our anonymous survey 👉 https://s.surveyplanet.com/8he6p7rq
Stay tuned for more updates as we continue to innovate and enhance our intrusion detection system! Tipis-tipis asal menyala abangkuuhh! 🔥🔝🙌🏼
Best!
dw1
As announced in teler-announce#Fm8Yjh_4of0.
[!NOTE] In the meantime, you can install and download the latest v2 version to continue using it.



Real-time HTTP Intrusion Detection
Contribute
·
What's new
·
Report Bug
·
Request Feature
teler is an real-time intrusion detection and threat alert based on web log that runs in a terminal with resources that we collect and provide by the community. ❤️
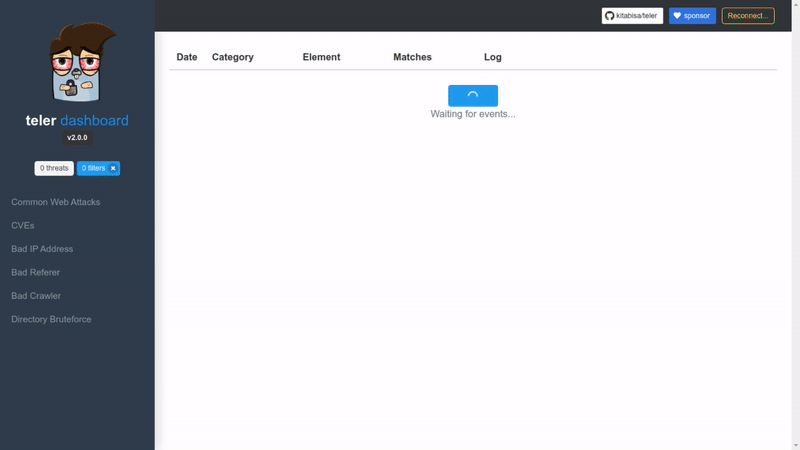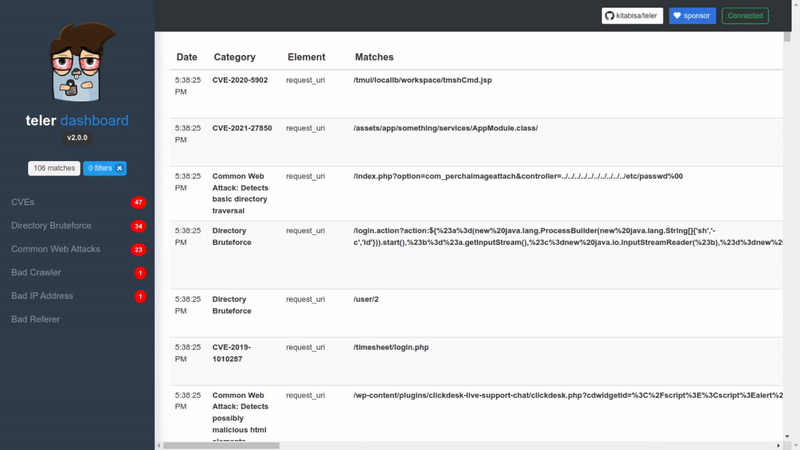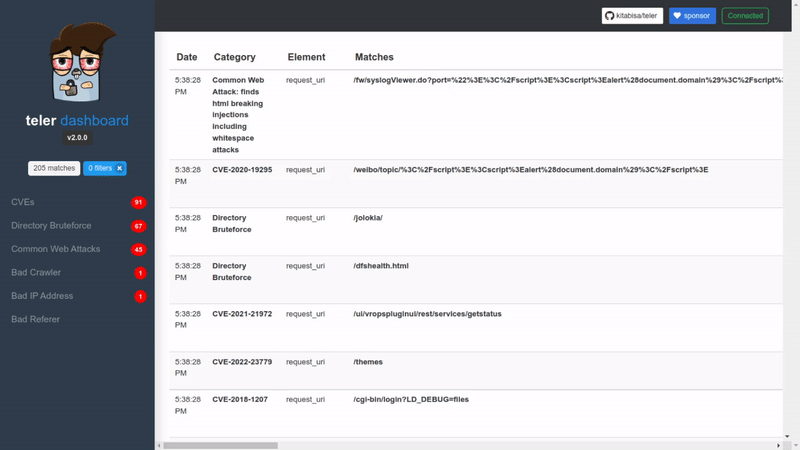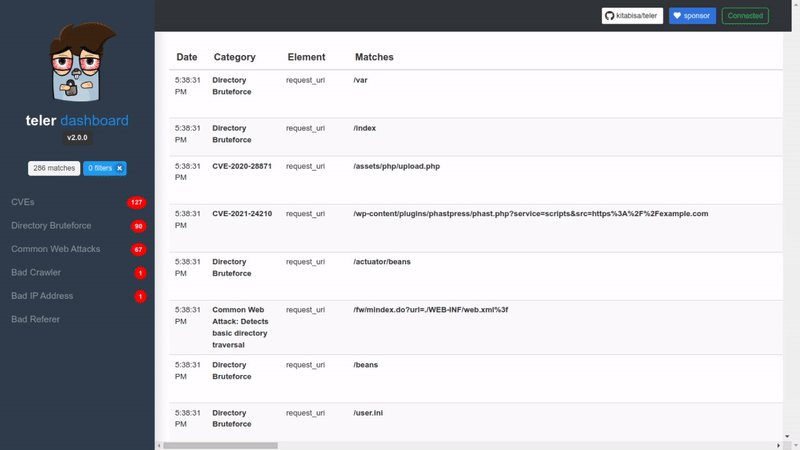
| CLI | Dashboard |
|---|---|
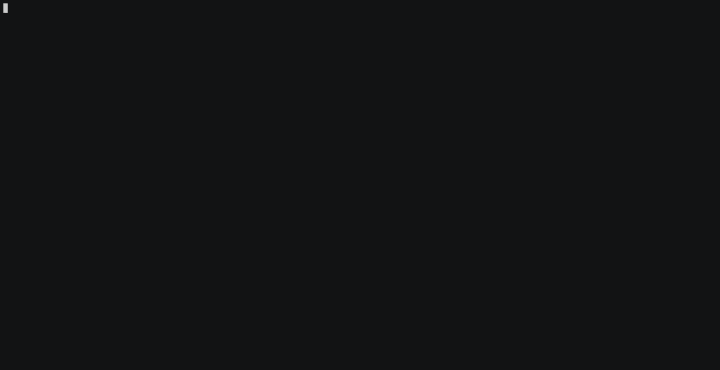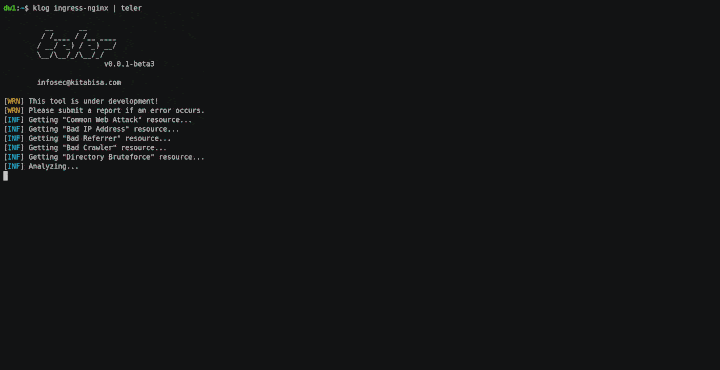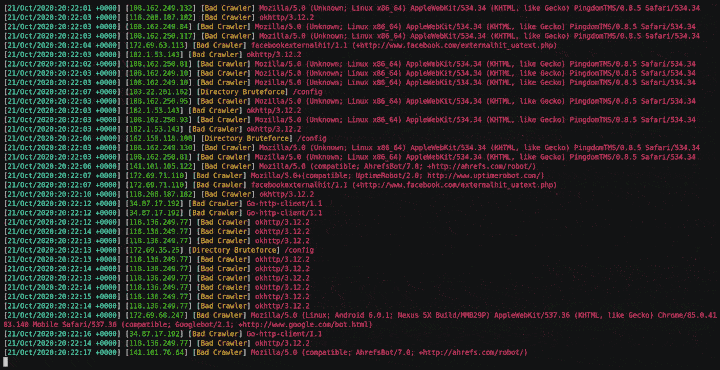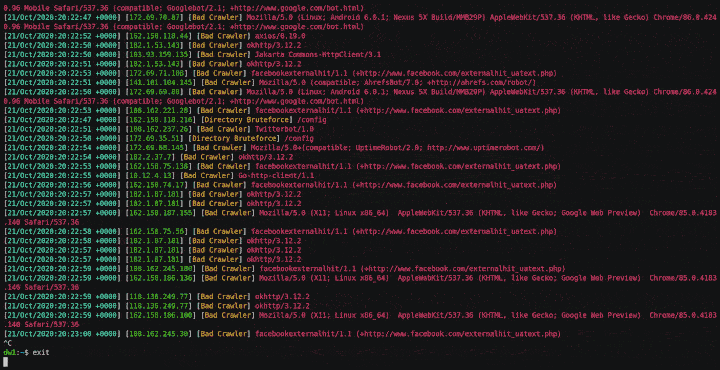 | 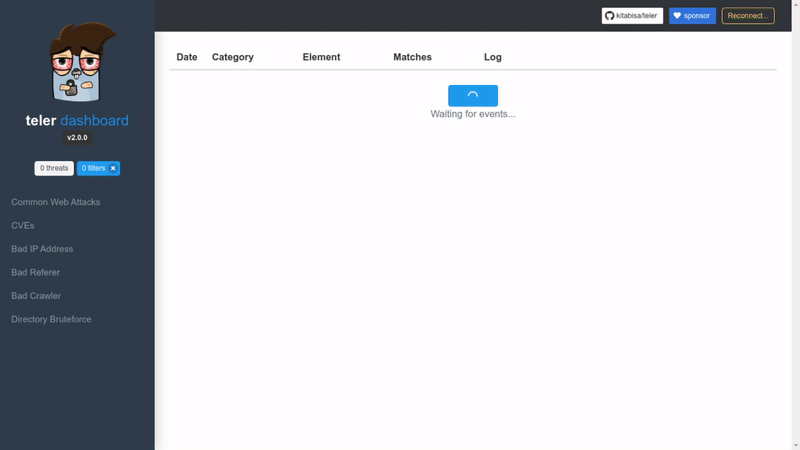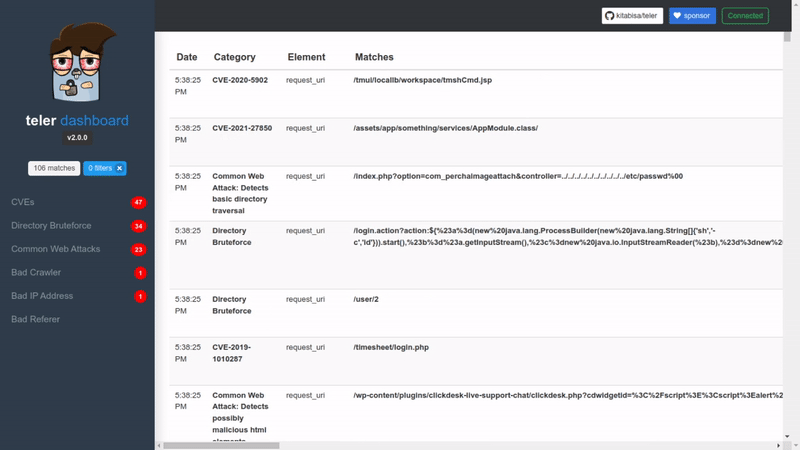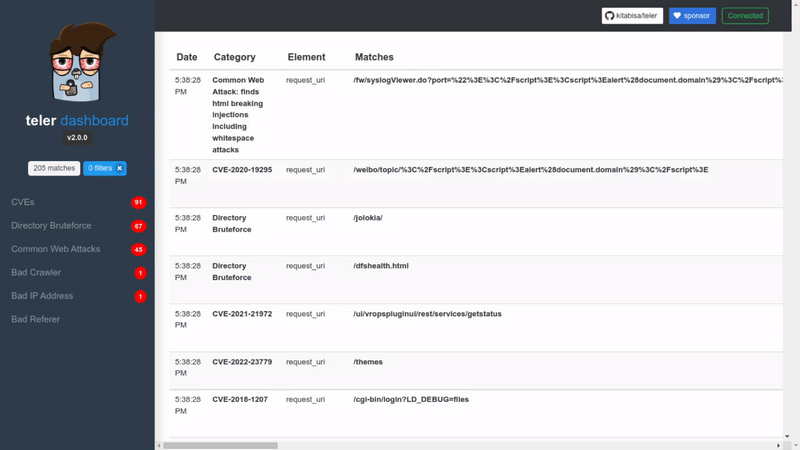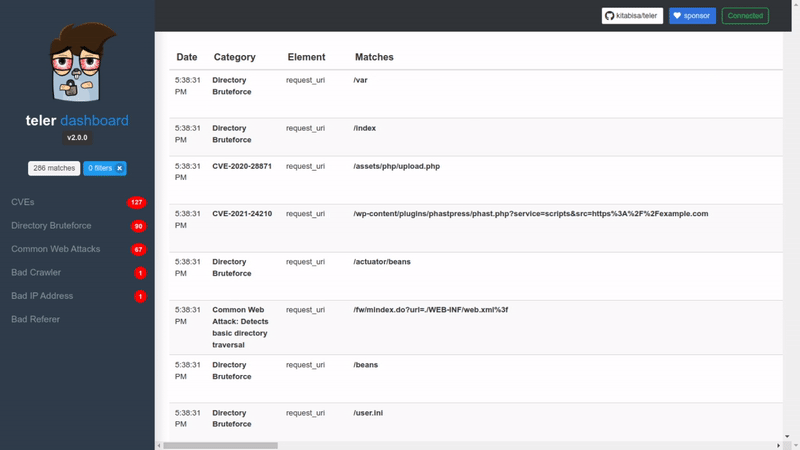 |
[!NOTE] If you upgrade from prior to v2 frontwards there will be some break changes that affect configuration files. Appropriate adaptations can refer to teler.example.yaml file.
See also:
Real-time: Analyze logs and identify suspicious activity in real-time.
Alerting: teler provides alerting when a threat is detected, push notifications include Slack, Mattermost, Telegram and Discord.
Monitoring: We've our own metrics if you want to monitor threats easily, and we use Prometheus for that.
Logging: is also provided in file form or sends detected threats to the Zinc logs search engine.
Latest resources: Collections is continuously up-to-date.
Minimal configuration: You can just run it against your log file, write the log format and let teler analyze the log and show you alerts!
Flexible log formats: teler allows any custom log format string! It all depends on how you write the log format in configuration file.
Custom threat rules: Want to reach a wider range of threats instead of engine-based (default) rules? You can customize threat rules!
Incremental log processing: Need data persistence rather than buffer stream? teler has the ability to process logs incrementally through the on-disk persistence options.
teler was designed to be a fast, terminal-based threat analyzer. Its core idea is to quickly analyze and hunt threats in real time!
Here is a preview of teler with conditions of use as:
| Buffer-streams | Incremental |
|---|---|
 |  |
All related documentation about installation, usage & configuration is on teler.app.
This project exists thanks to all the people who contribute. To learn how to setup a development environment and for contribution guidelines, see CONTRIBUTING.md.
