Graylog2__graylog2-server_CVE-2023-41044_5-1-2

Open source log management platform for centralized log aggregation, real-time analysis, and security event monitoring with customizable dashboards…

Open source log management platform for centralized log aggregation, real-time analysis, and security event monitoring with customizable dashboards…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

DEPRECATED - MozDef: Mozilla Enterprise Defense Platform

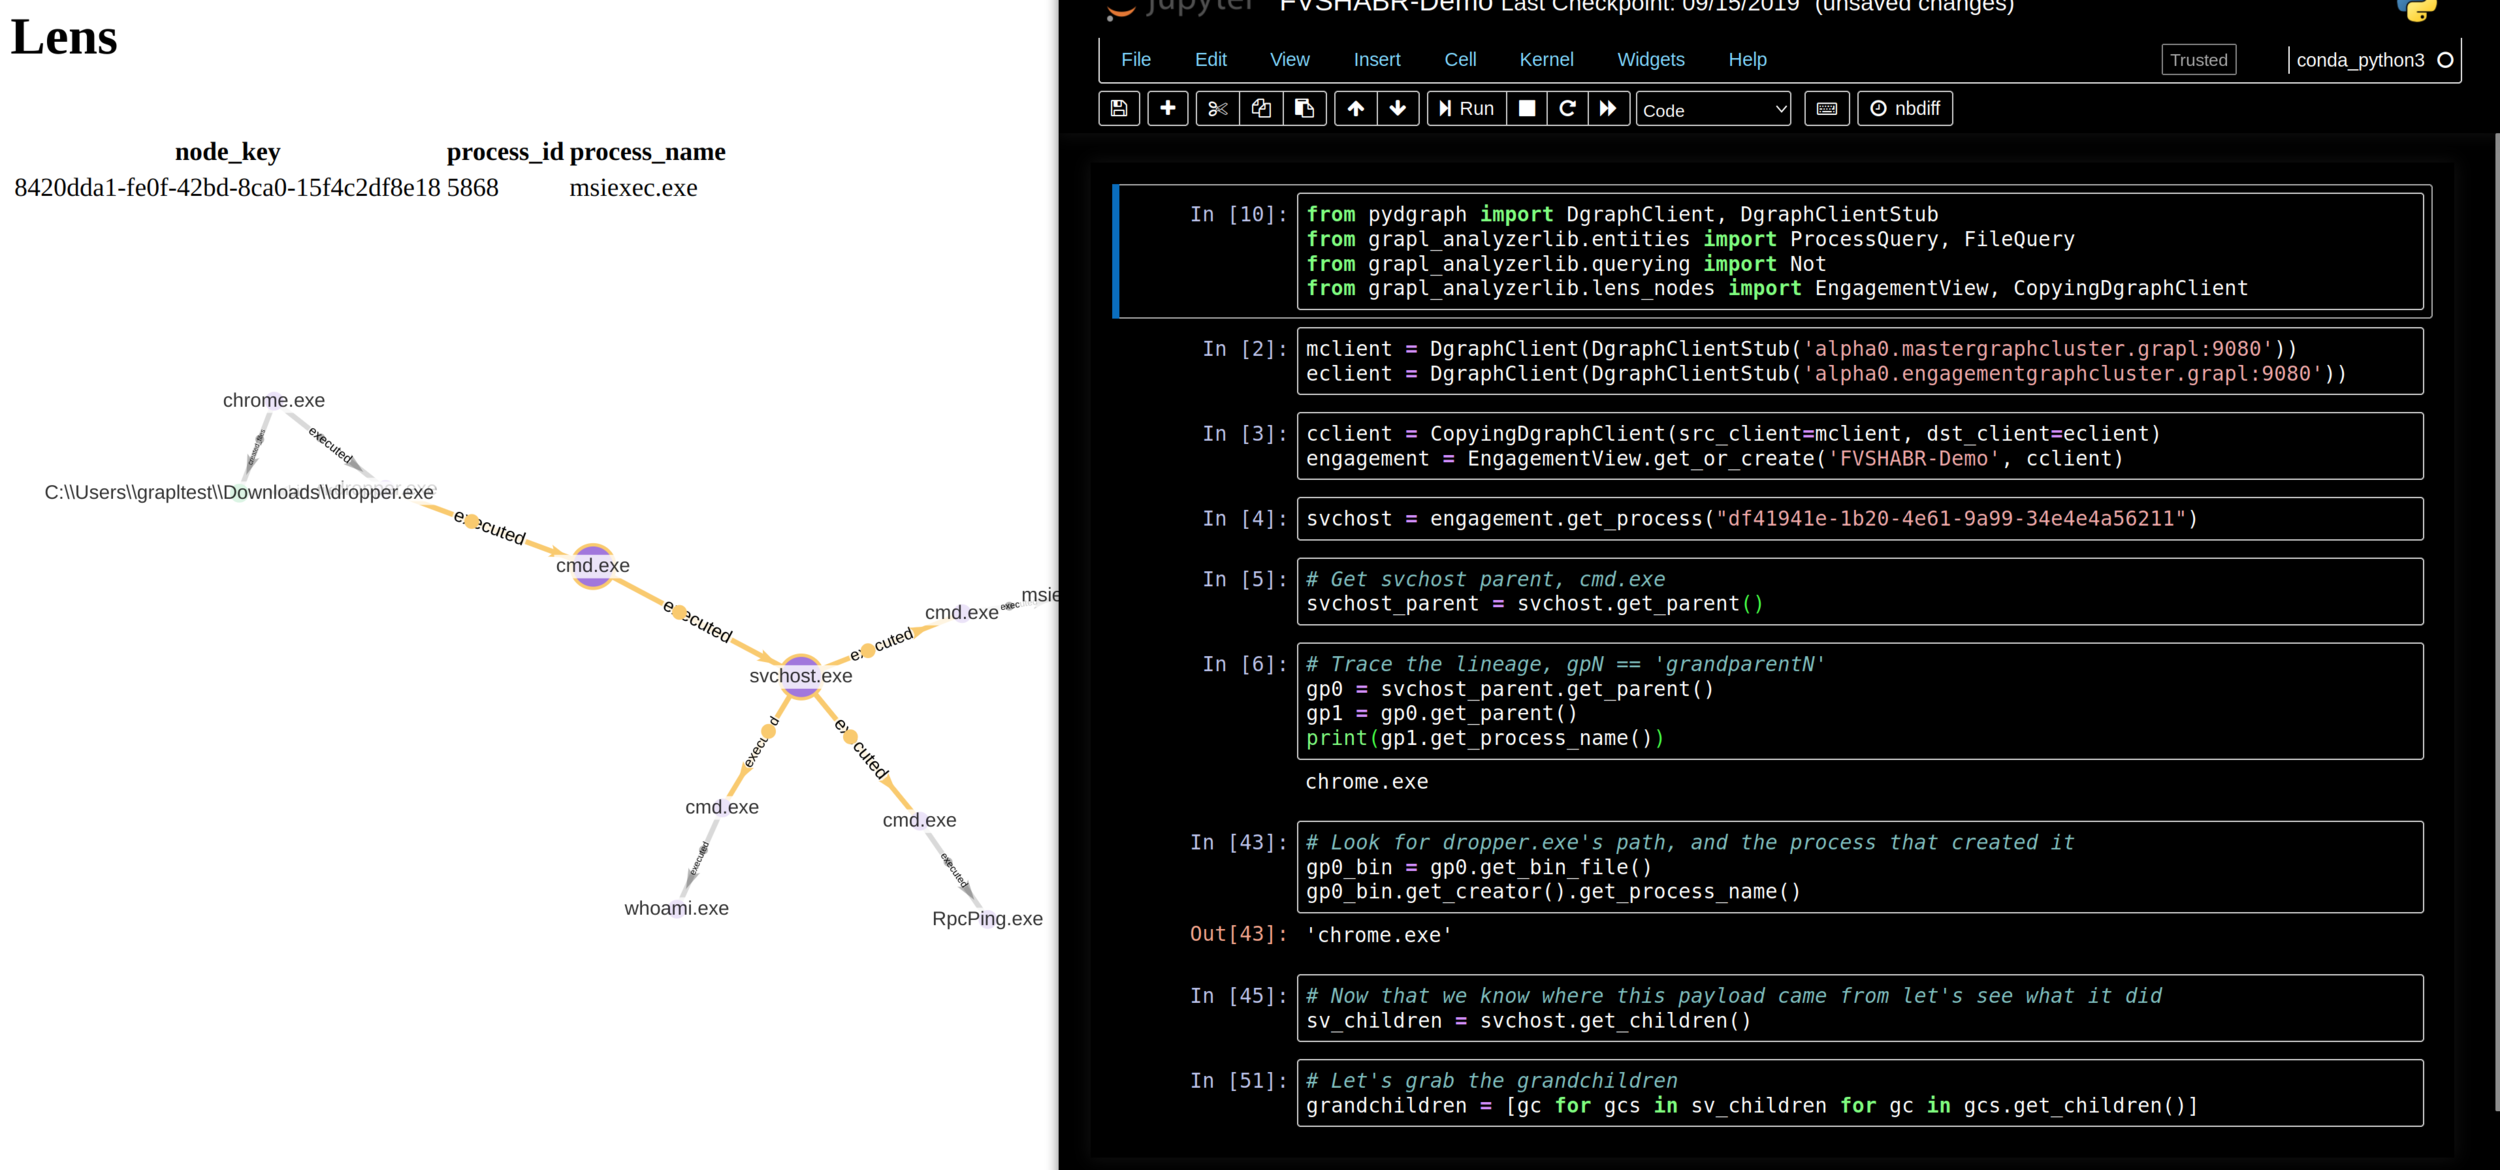
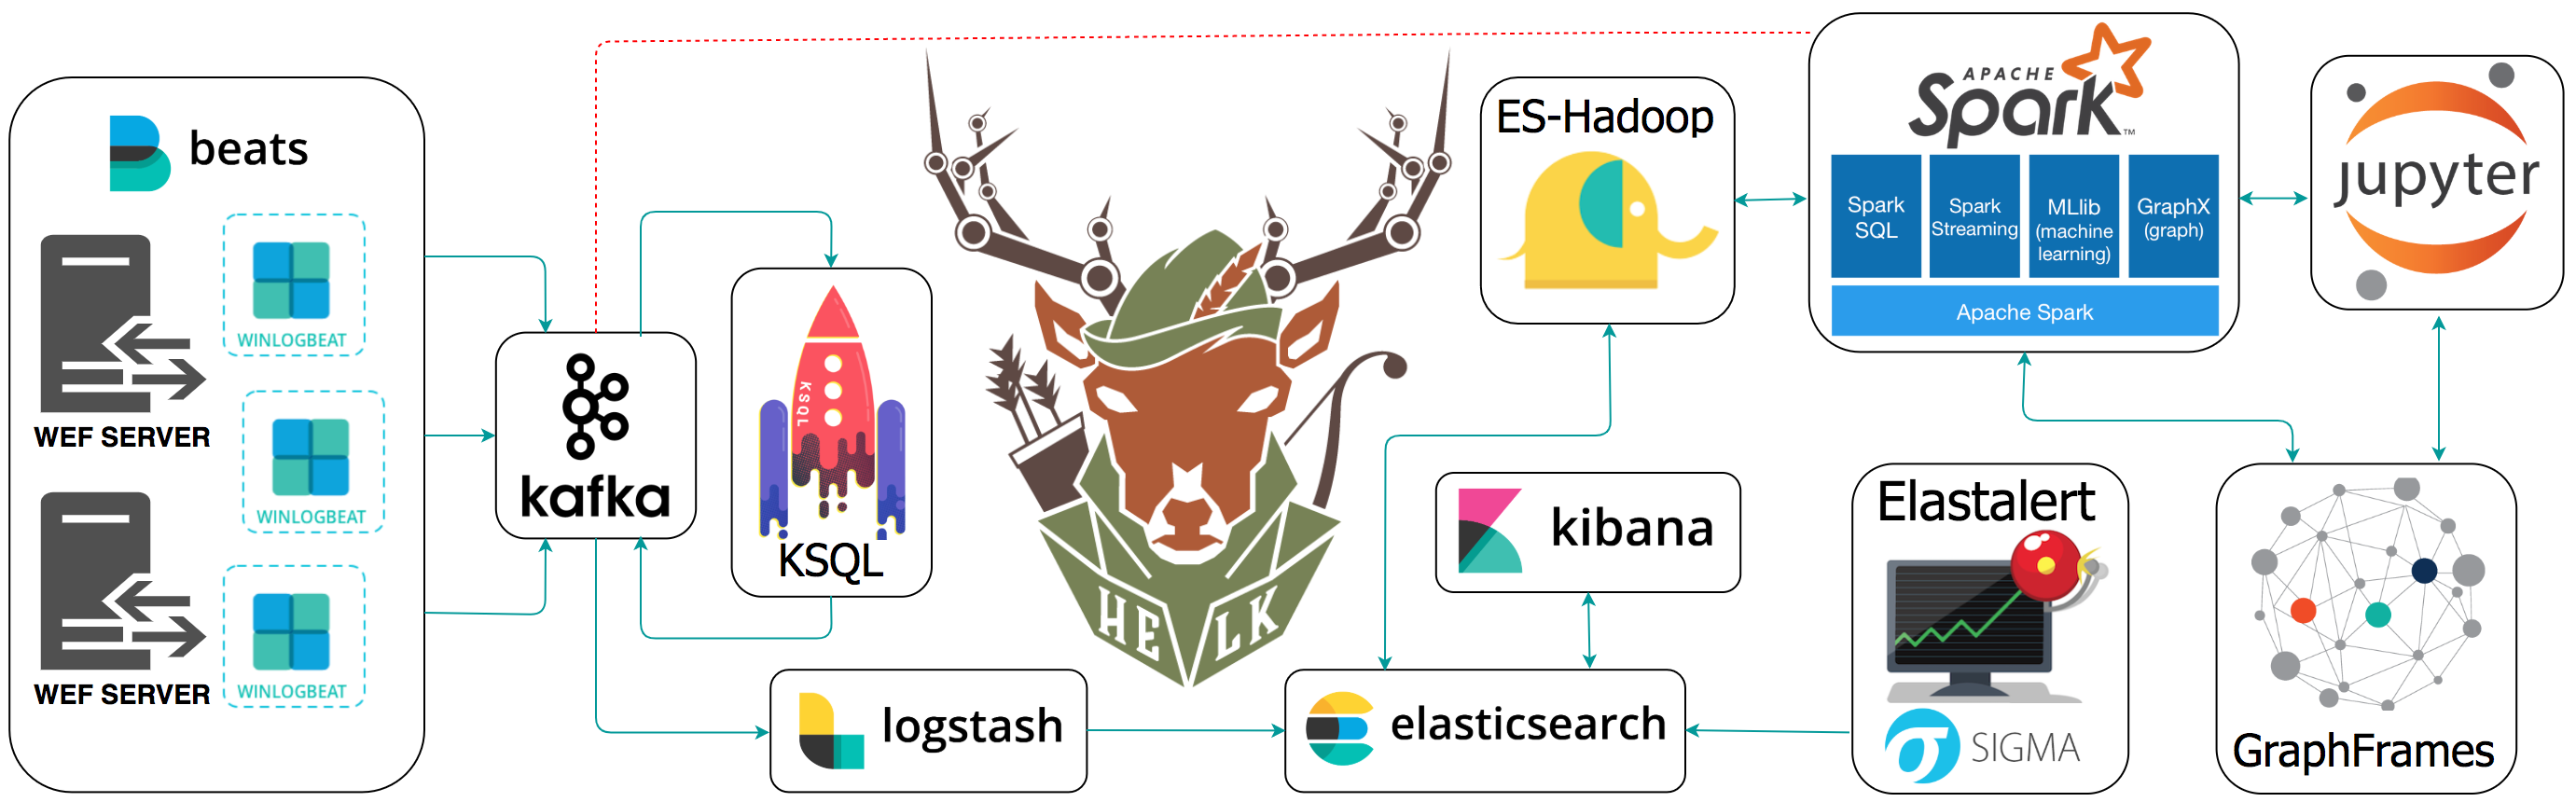
Graph platform for Detection and Response

AI 驱动的 SOC 仿真平台

Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…

OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…

A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs

A Fast (and safe) parser for the Windows XML Event Log (EVTX) format

Security event correlation engine for ELK stack

🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM


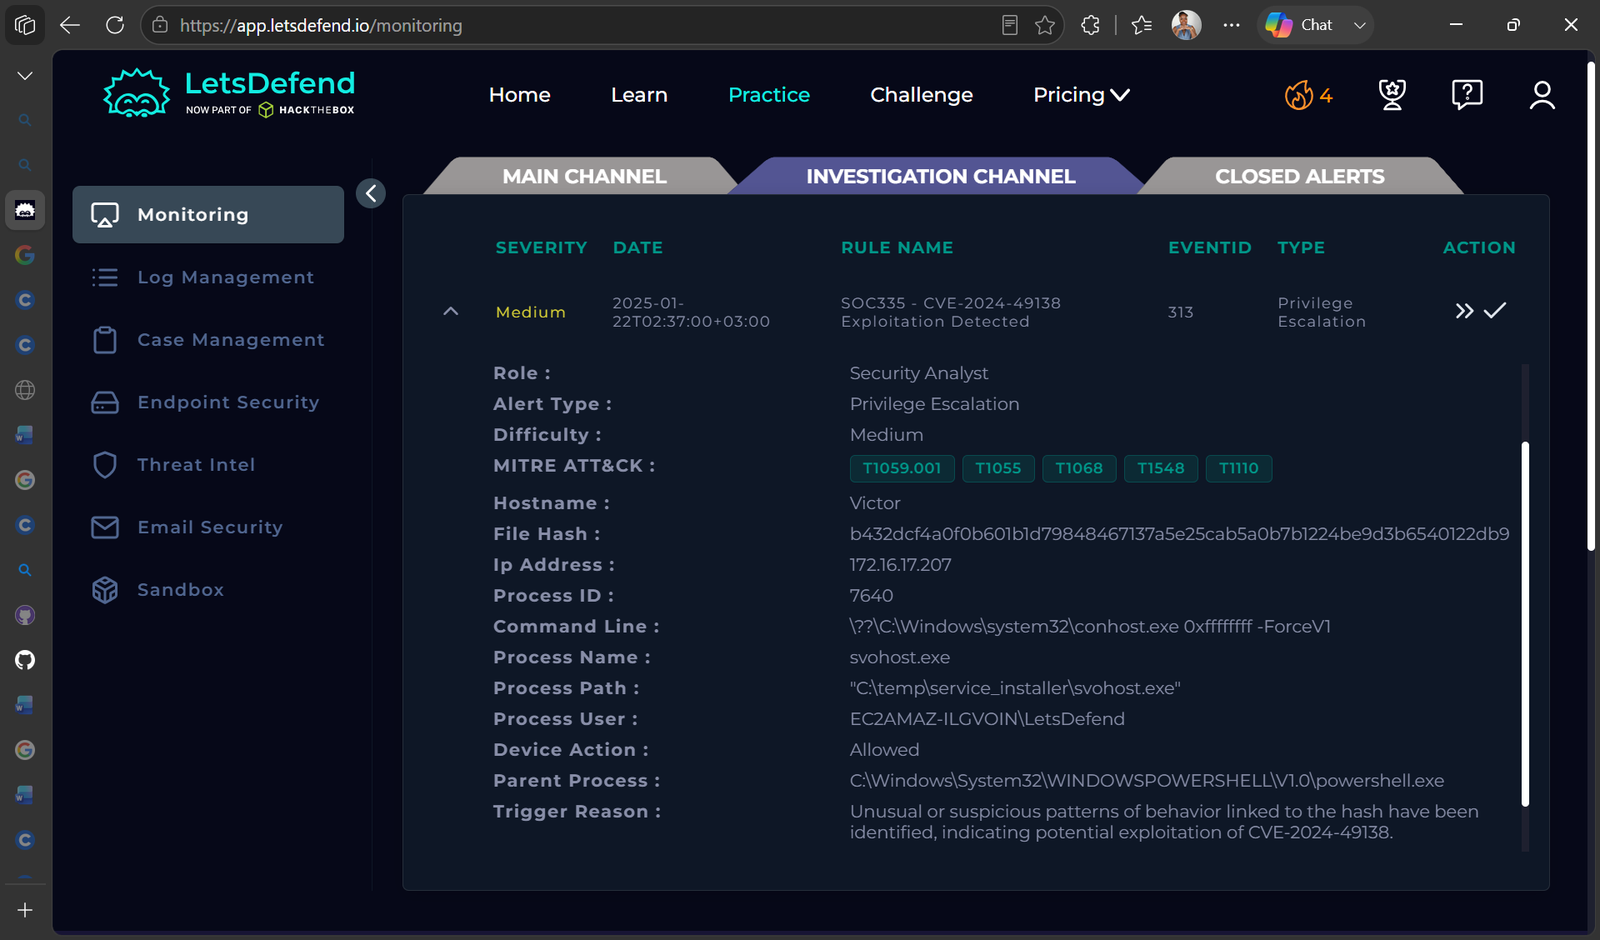
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.

Distributed & real time digital forensics at the speed of the cloud

A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).

MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs

This project is a SIEM with SIRP and Threat Intel, all in one.