
netward-standalone
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
anomaly-detectionanti-botdefensive-tools+6
dragon-lady/netward-standaloneUser-space bot and DDoS deflection for small HTTP services
 gary23w/hodometer
A single-file native Windows tray application (C, Win32, no runtime) that shows exactly which program is sending and receiving bytes and to which…
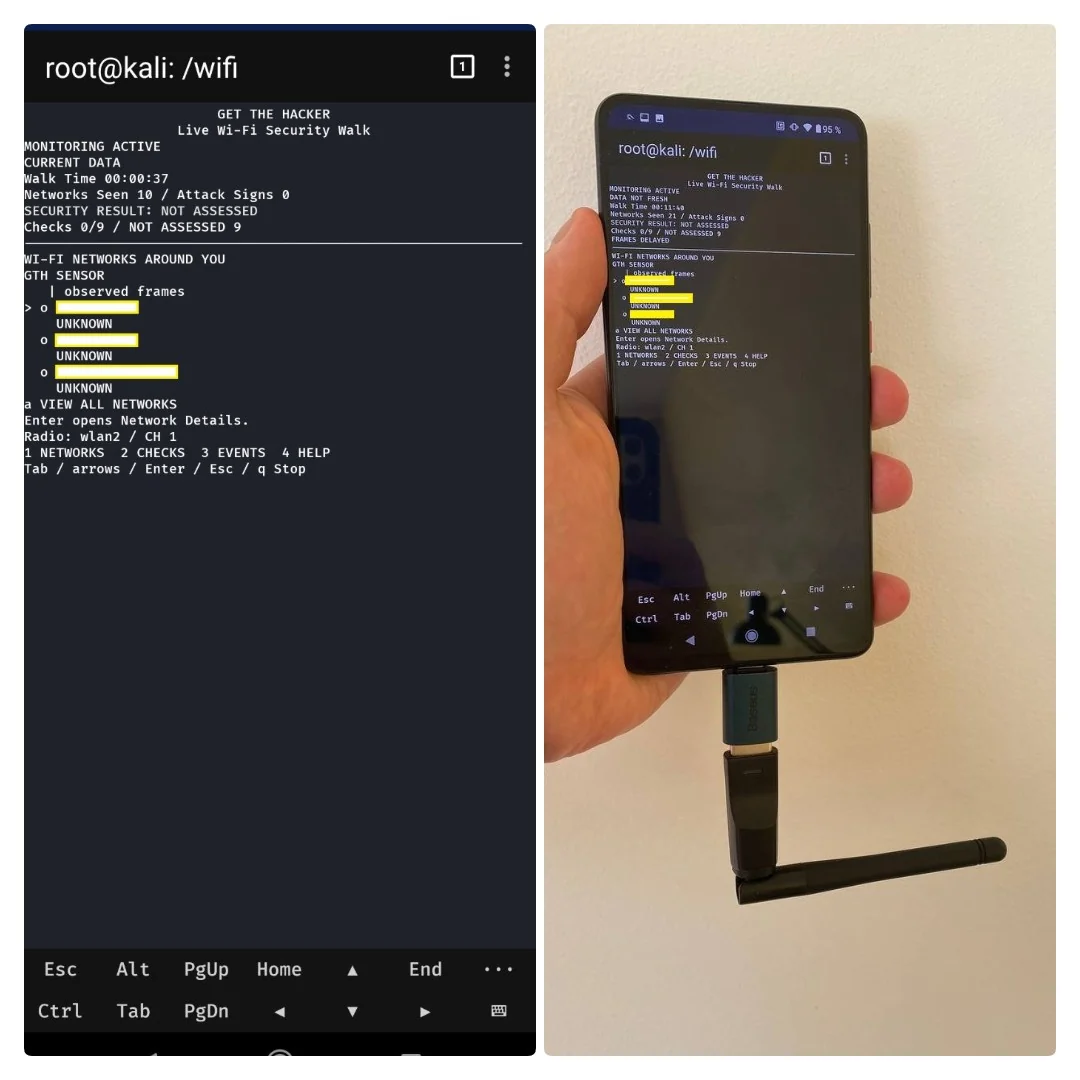 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
 lhiebert01/network-attack-simulator
Streamlit educational dashboard that simulates port scanning, DoS, brute force and data exfiltration attacks, with visualizations, attack logs and…
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 jondean213-pixel/quietos-sentinel
Sentinel — DeanWay Labs' inbound governor. Guards what an AI agent hears: world content is data, never orders. The mirror of QuietOS.
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 oscerd/cve-2026-85260
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85260, demonstrating camel-mllp PHI logging in affected versions and suppression after the…
 raj3shp/malscore
Maliciousness scoring for Linux commands
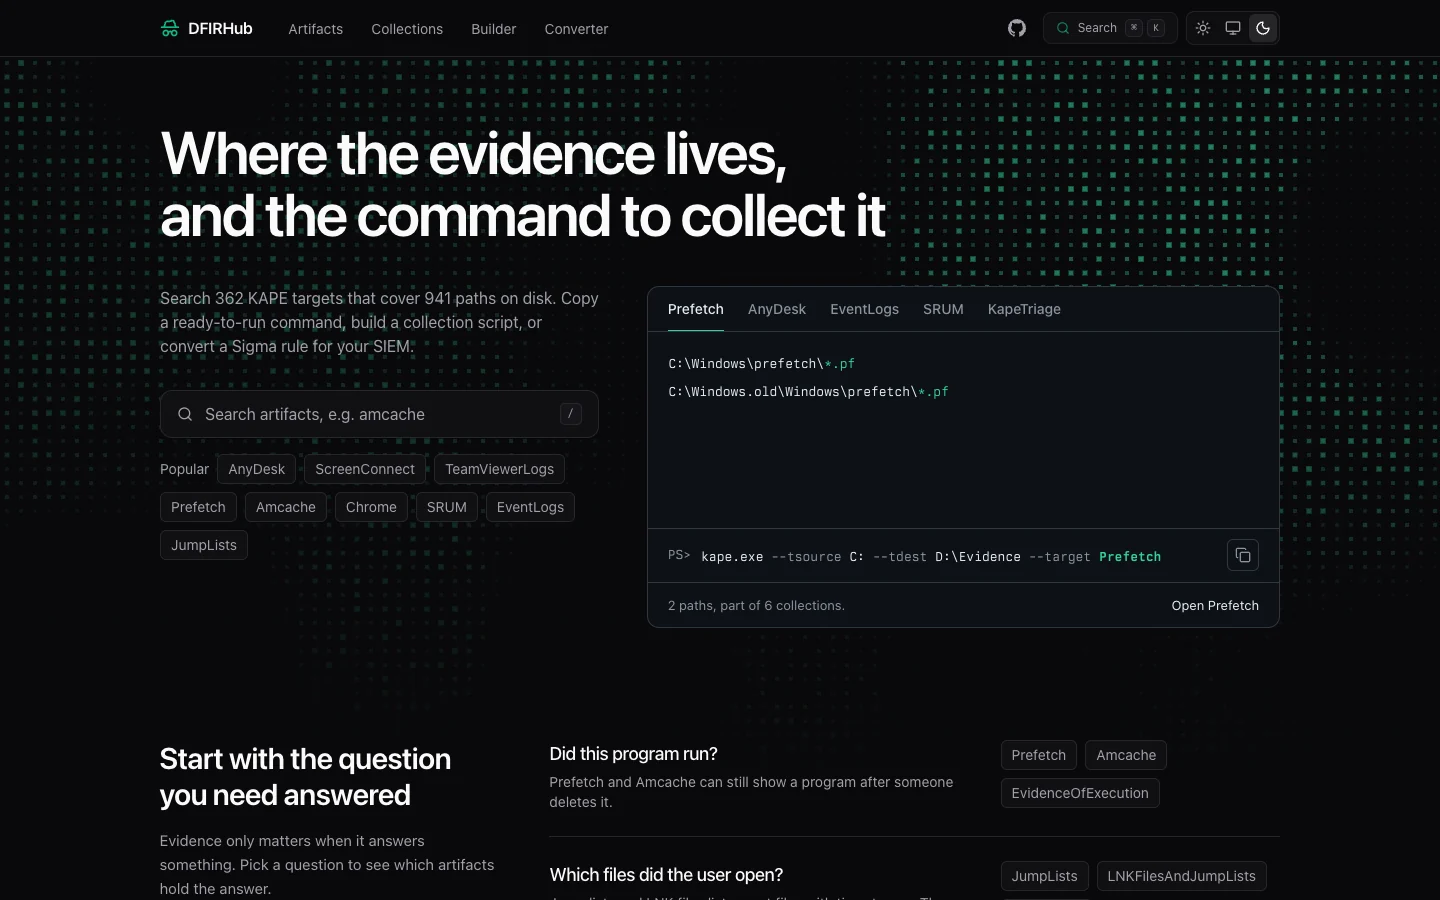 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…