Information-Security-Tasks

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…

Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…

A community-curated knowledge hub and catalog for computer science, cybersecurity & software engineering books

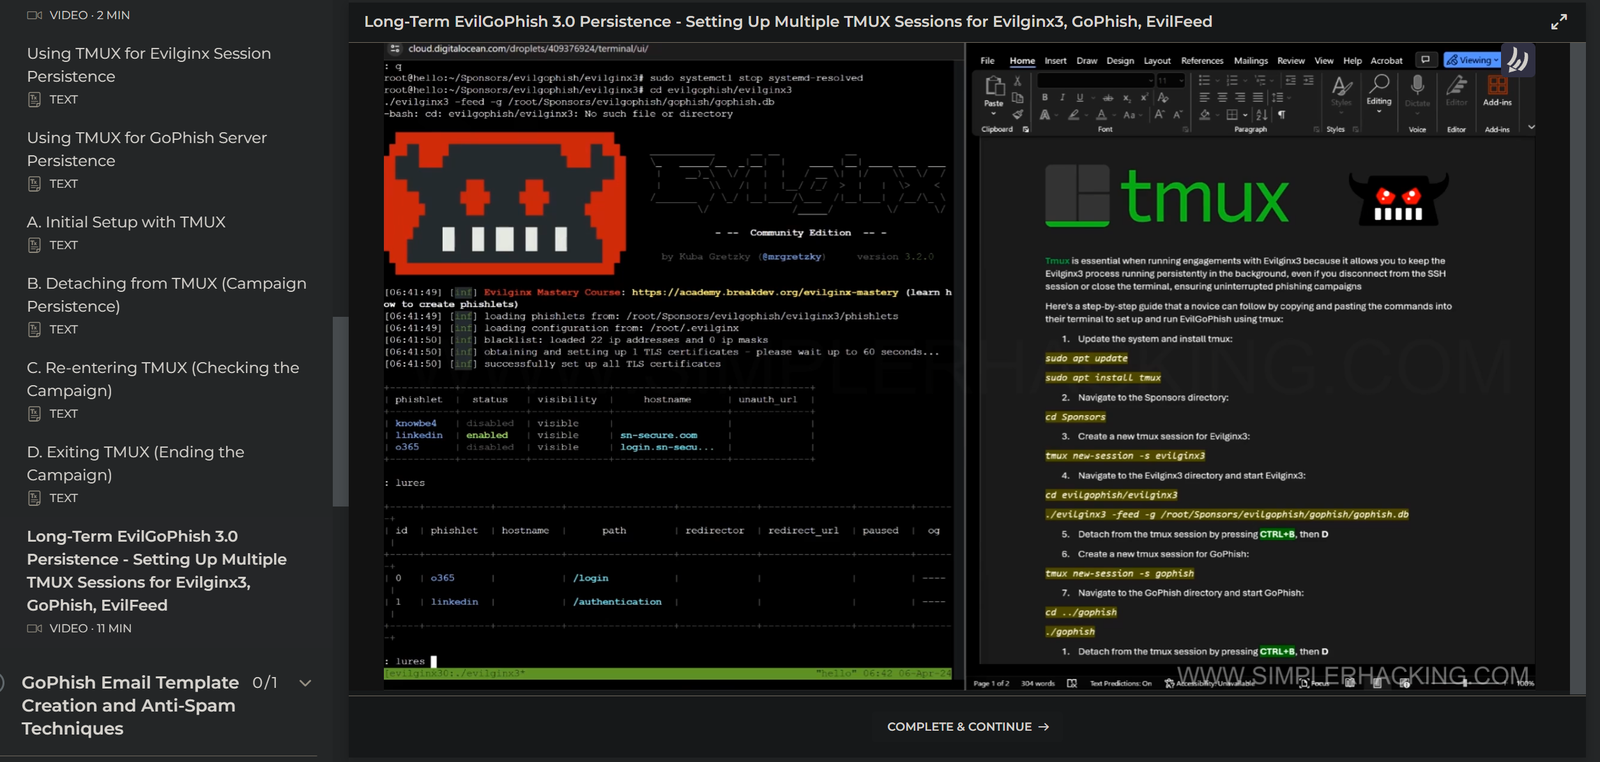
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

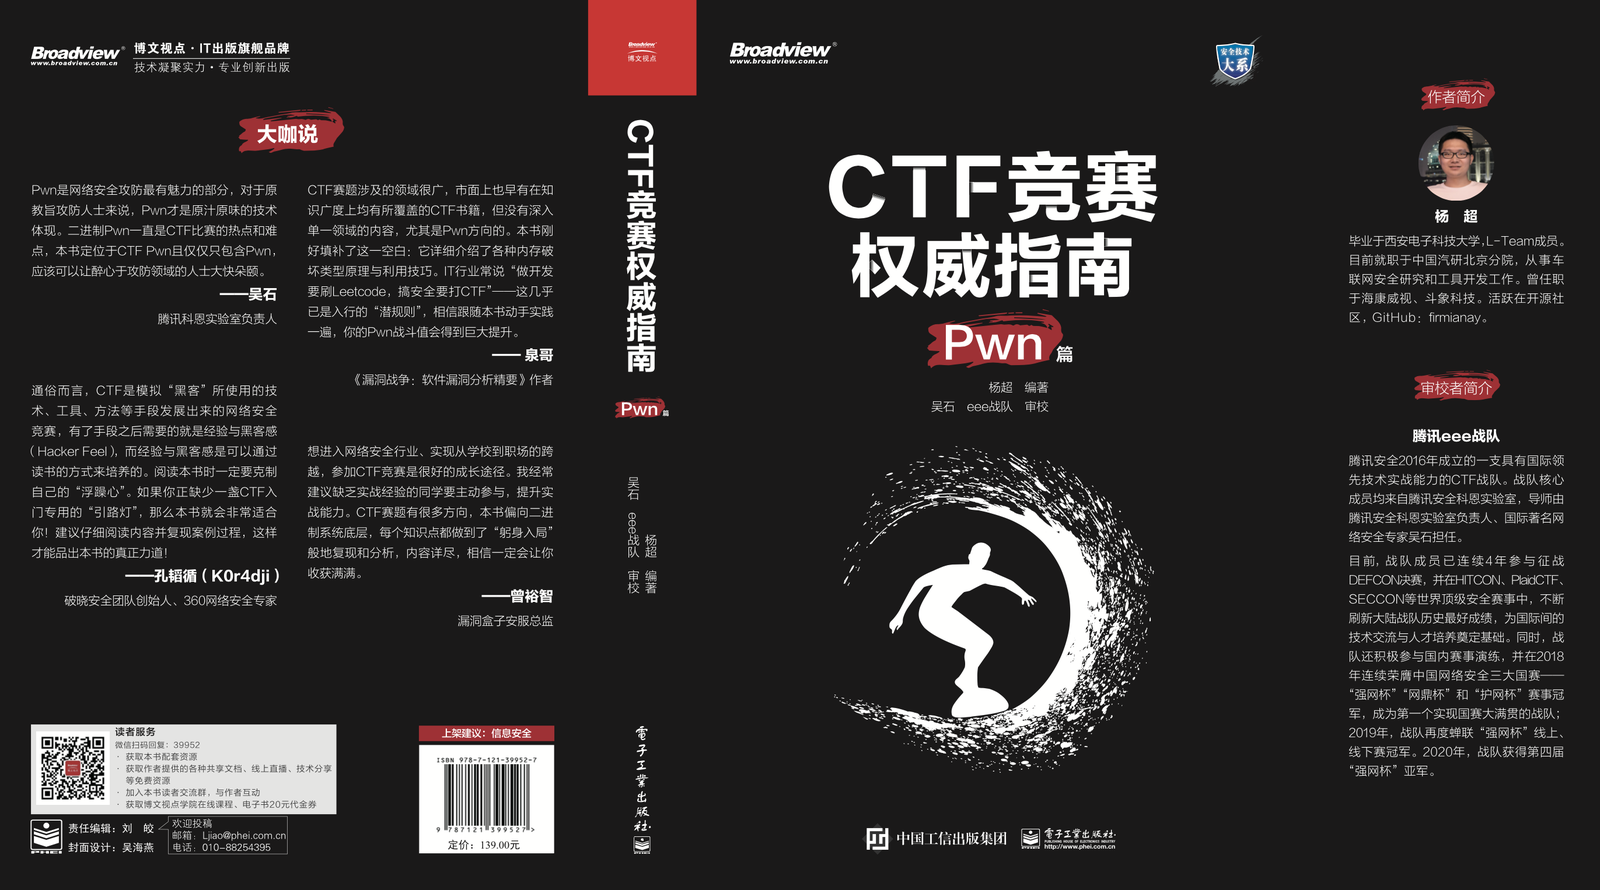
Open-source CTF guidebook covering Pwn, reverse engineering, and web security, with structured chapters, worked examples, and tooling setup for…

Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…

OWASP Top 10 for Large Language Model Applications

Monorepo of OWASP Bug Logging Tool projects: crowd-sourced vulnerability reporting, bug bounty workflows, CVE namespace, autopatching, and security…

Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…

Curated knowledge base of blockchain security research, audit reports, guides, and translations covering smart contracts, cryptography, and AI…

Community-maintained Markdown knowledge base covering cybersecurity foundations, offensive and defensive practice, governance, threat intelligence,…

Collection of Linux kernel exploitation CTF challenges covering buffer overflow, use-after-free, and race condition vulnerabilities for hands-on…

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.

OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.

Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging

:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.