SSH-Private-Key-Looting-Wordlists

Curated wordlists for brute-forcing SSH private key filenames, aiding penetration testers in locating keys via LFI or enumeration during lateral…

Curated wordlists for brute-forcing SSH private key filenames, aiding penetration testers in locating keys via LFI or enumeration during lateral…

Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool

Red Team Cheatsheet in constant expansion.

Tools and Techniques for Red Team / Penetration Testing

RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.

Collection of PowerShell functions a Red Teamer may use in an engagement

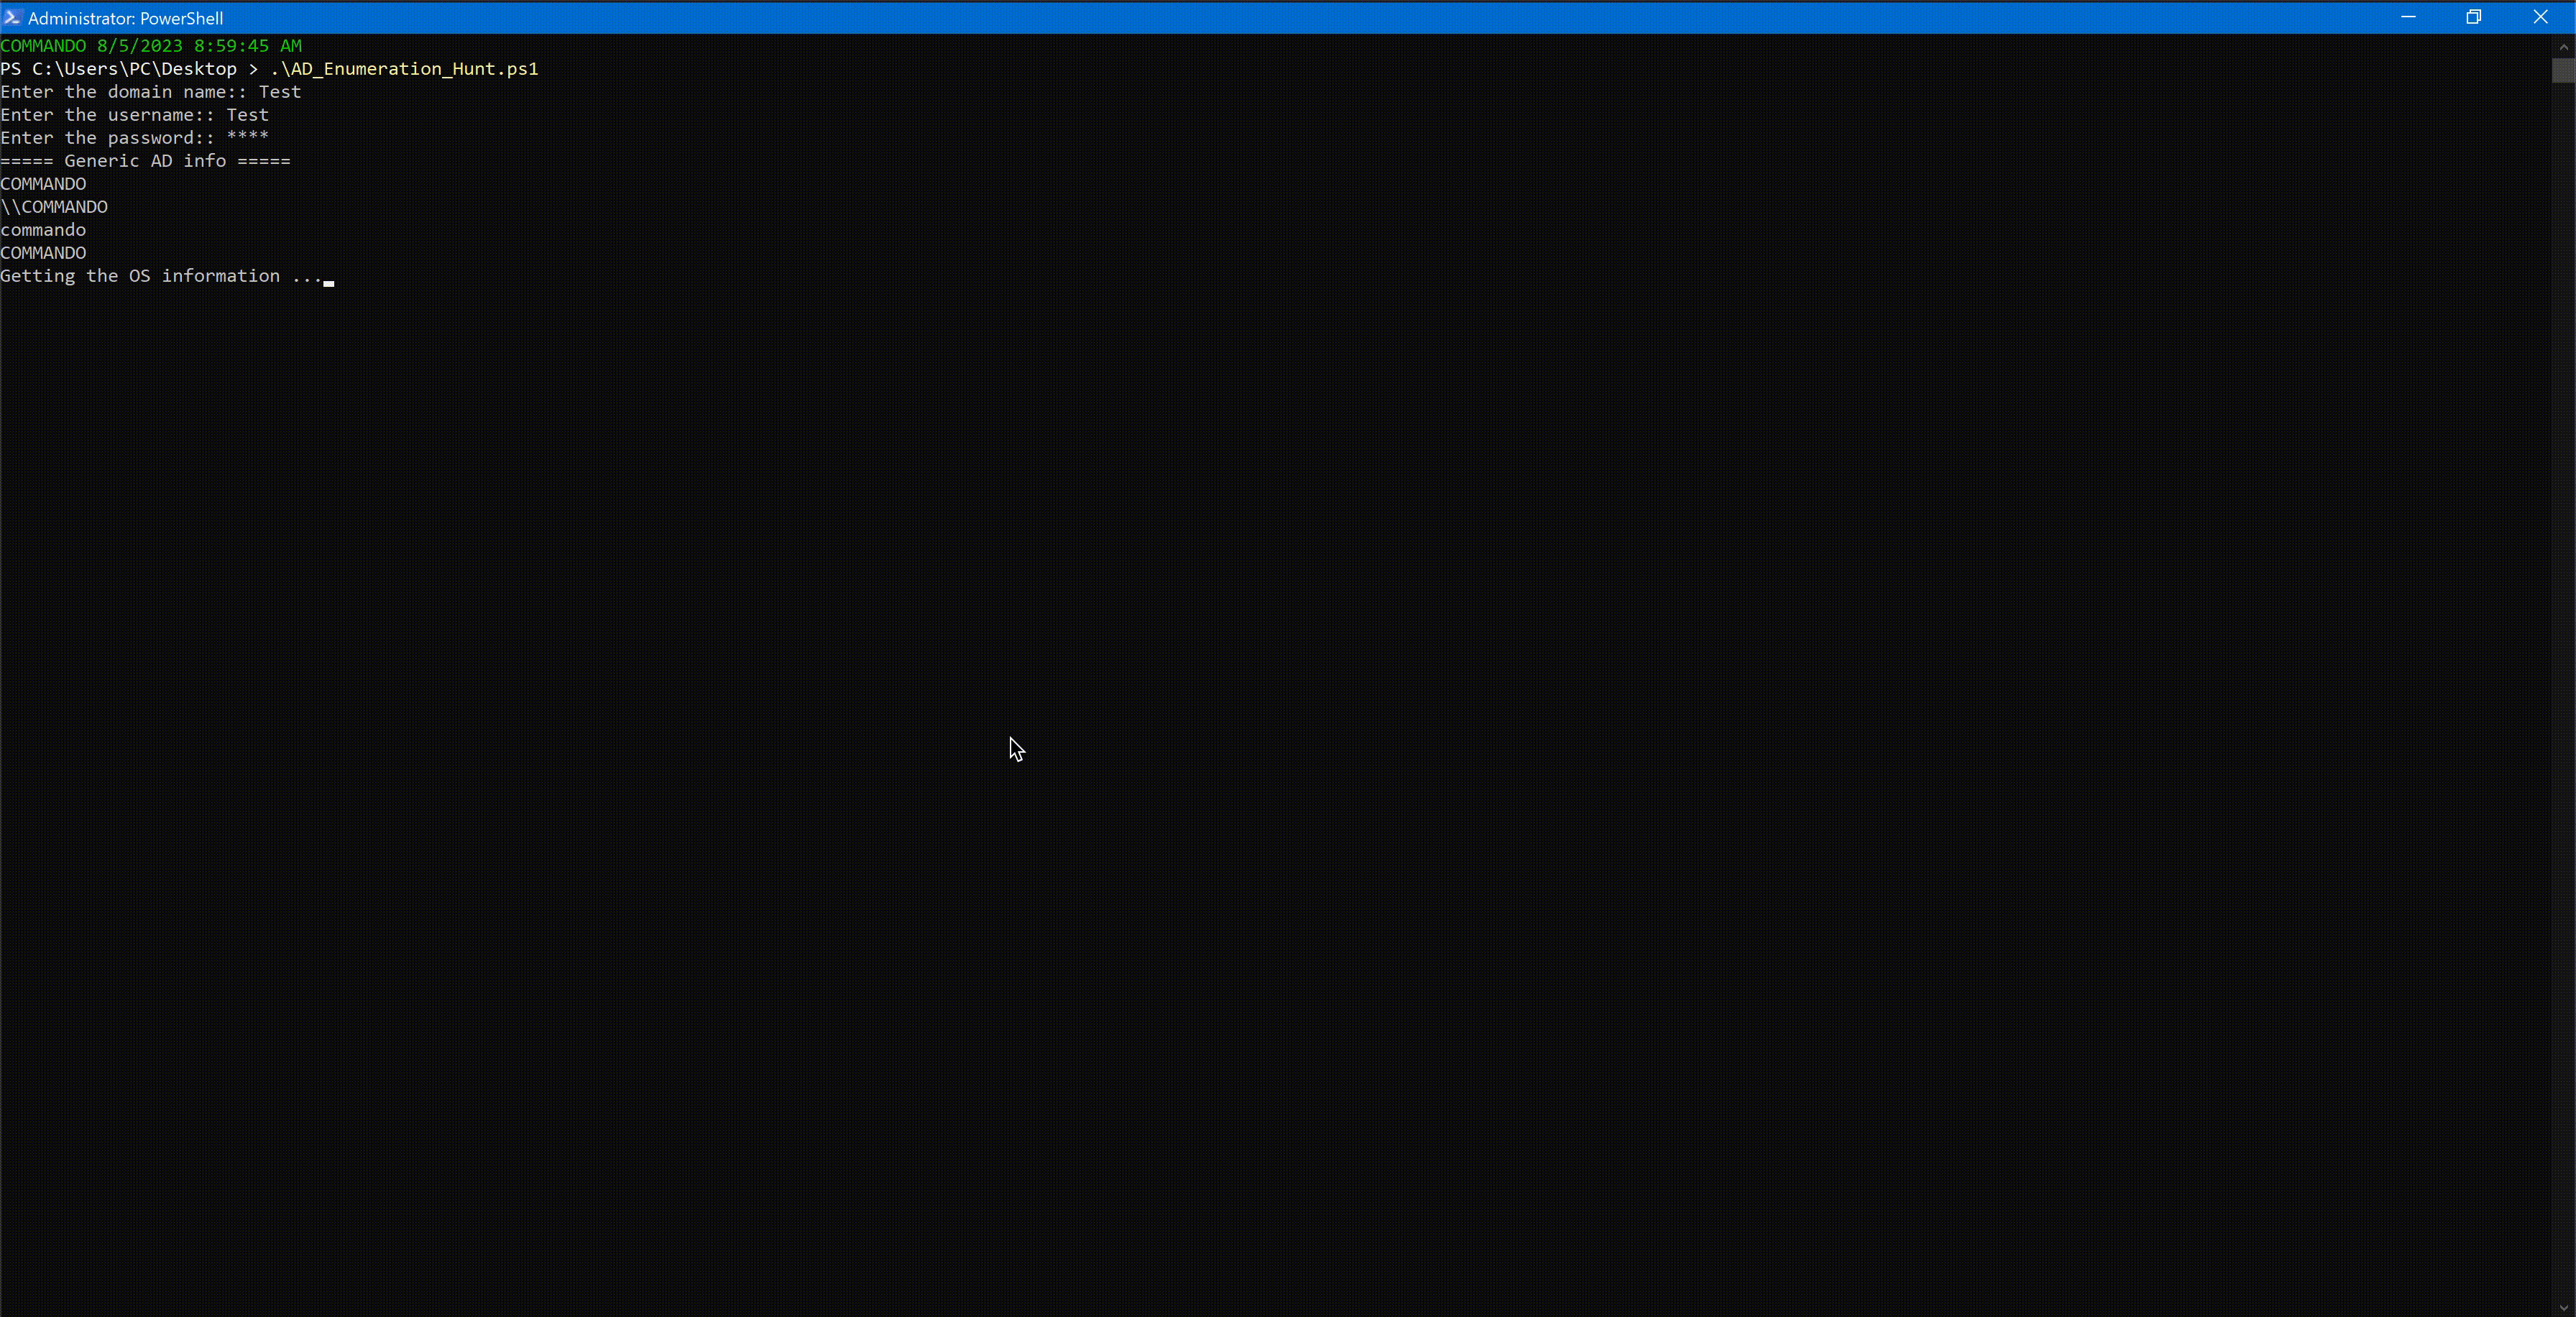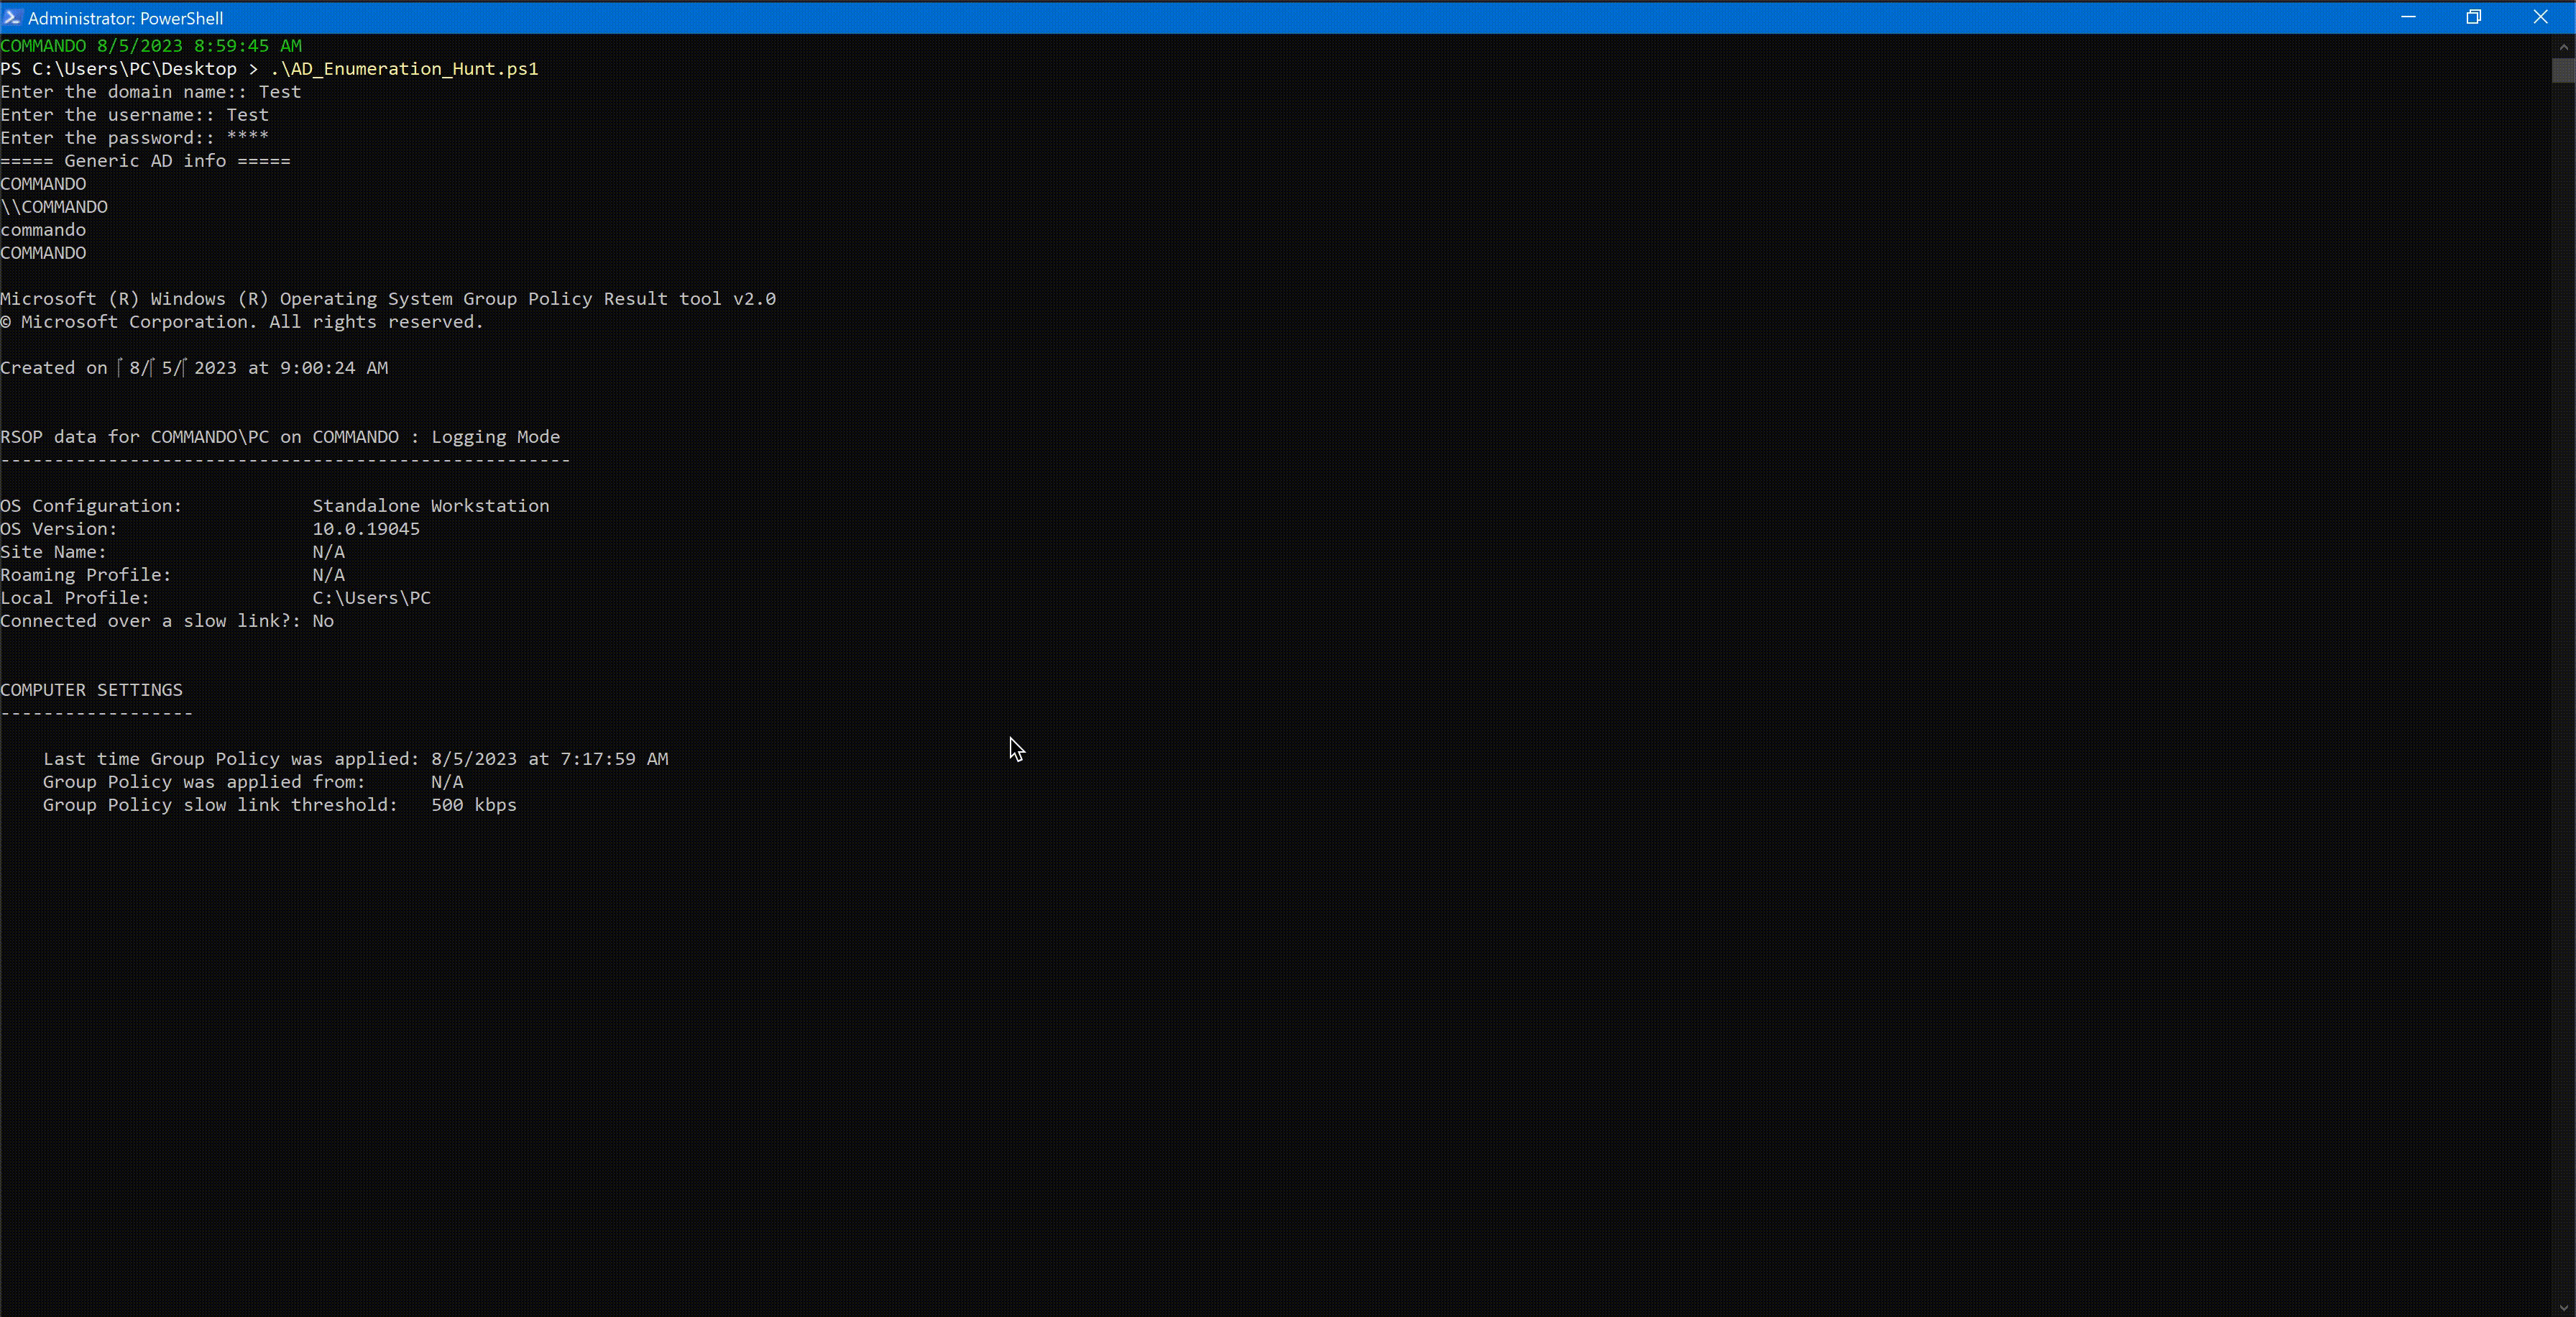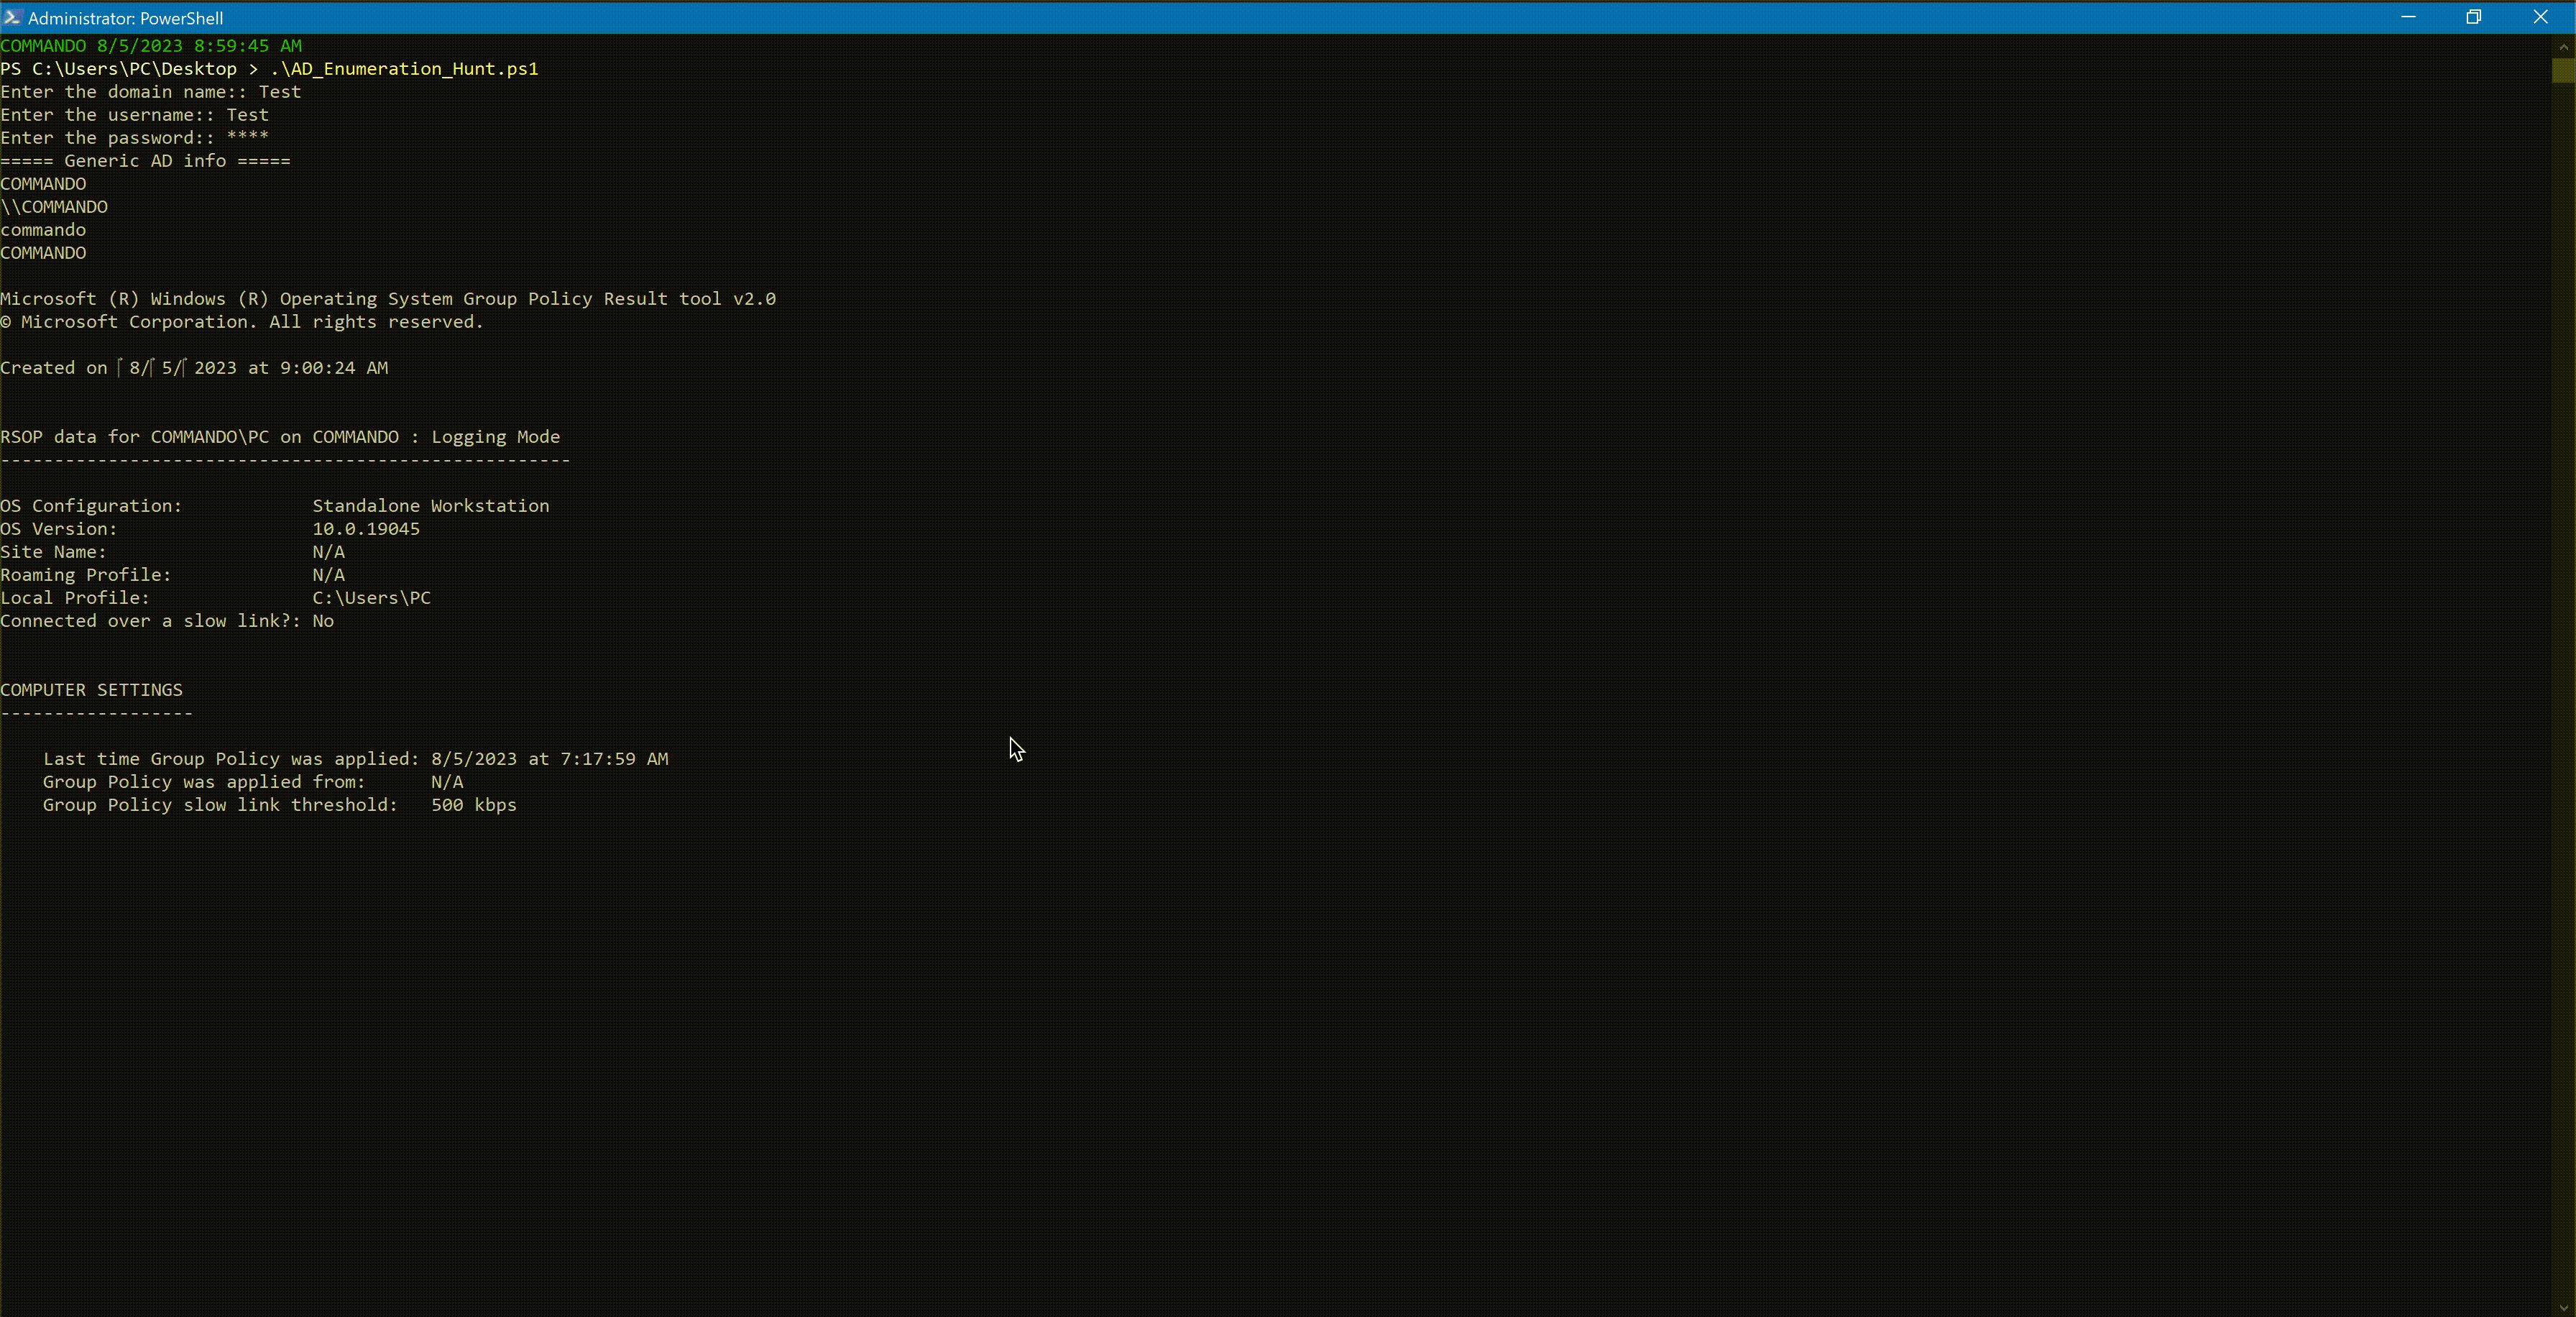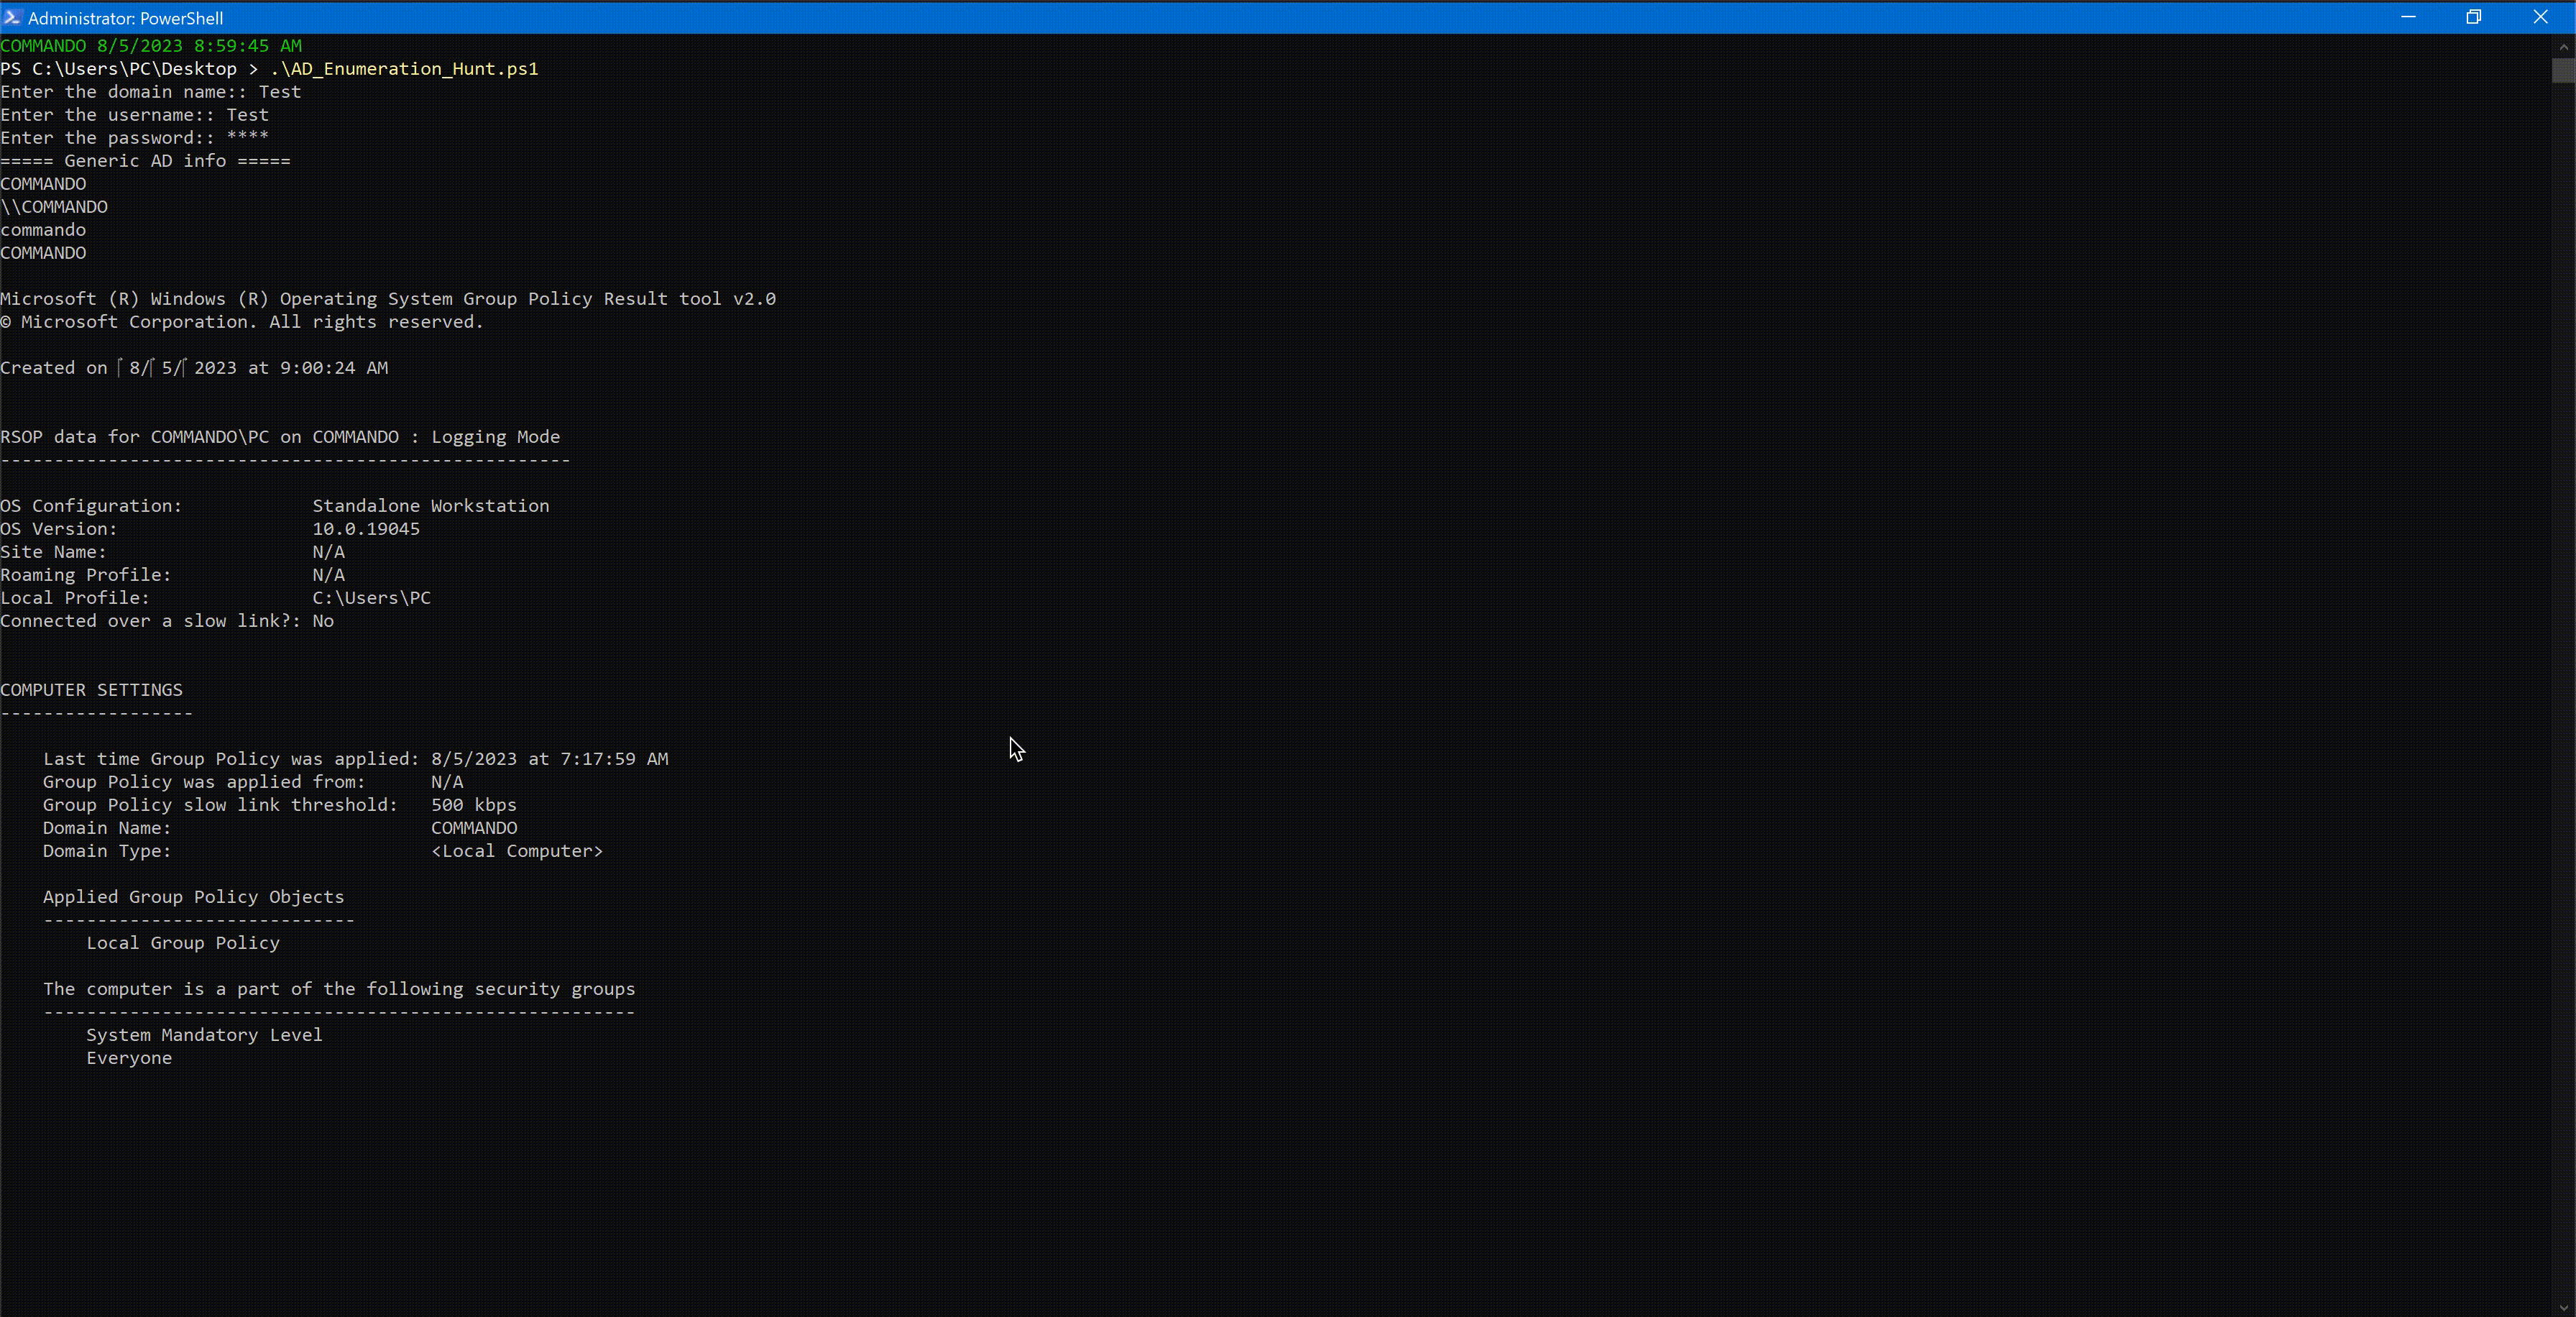
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.

A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.

.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…

PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

PowerShell enumeration script for discovering service-backed COM objects via CLSID/AppID correlation and activation testing.

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…

Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…

Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…