
SessionGopher
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
information-gatheringlateral-movementpenetration-testing+3
1.3k
arvanaghi/sessiongopherSessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
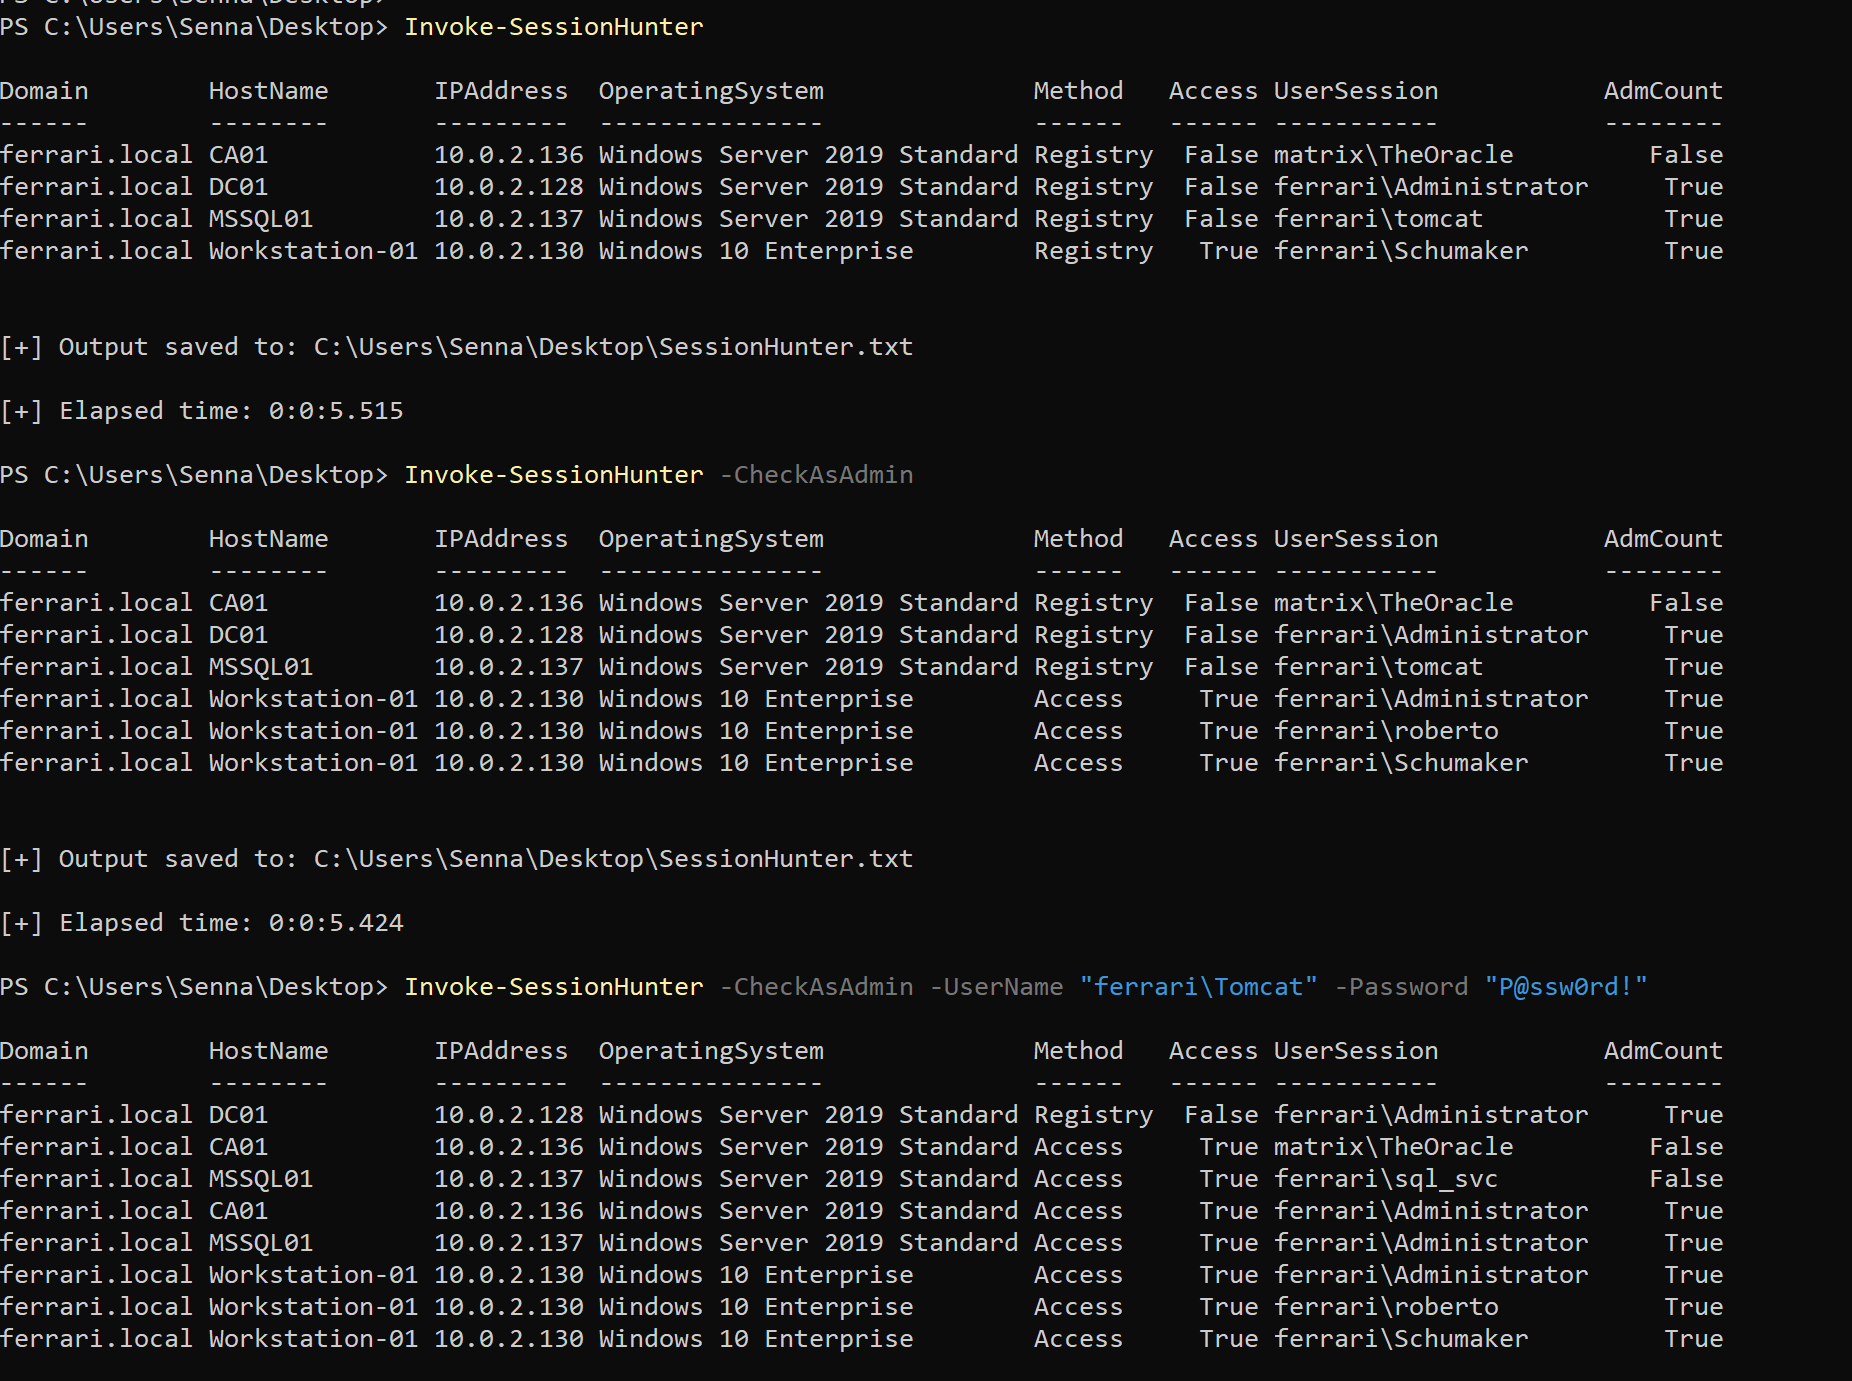 leo4j/invoke-sessionhunter
Retrieve and display information about active user sessions on remote computers. No admin privileges required.
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
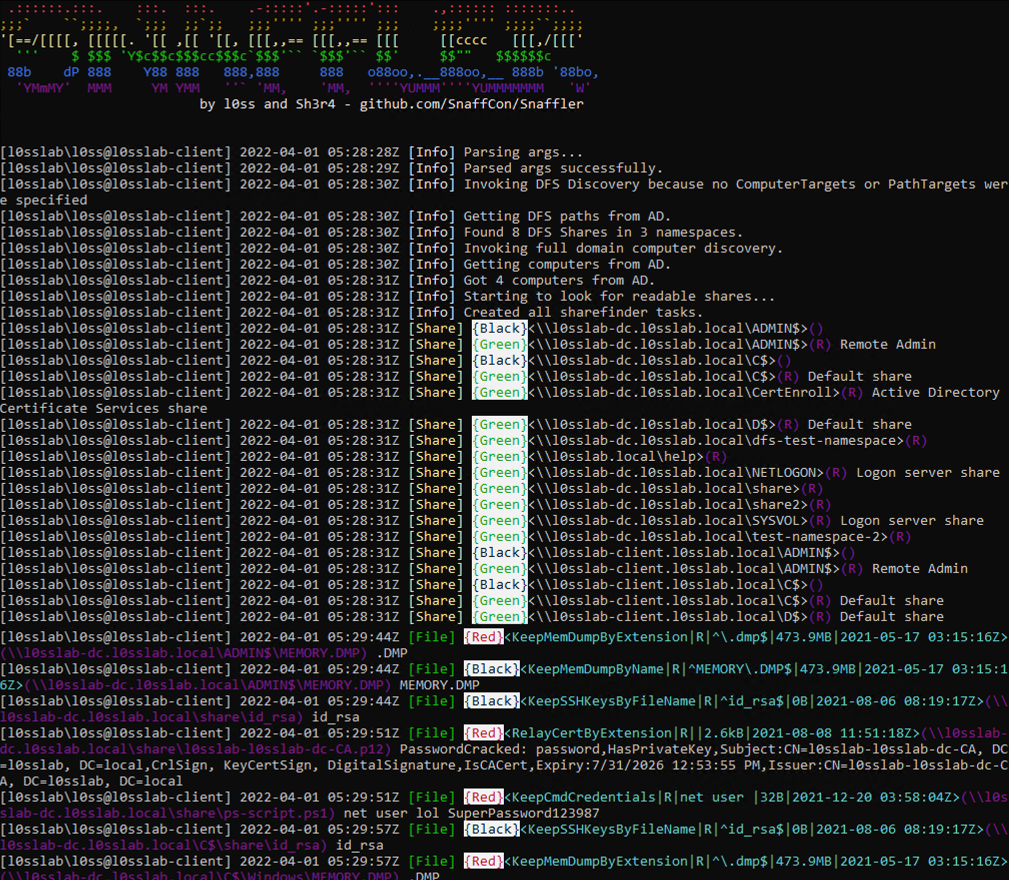 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
 trustedsec/titanis
Windows protocol library, including SMB and RPC implementations, among others.
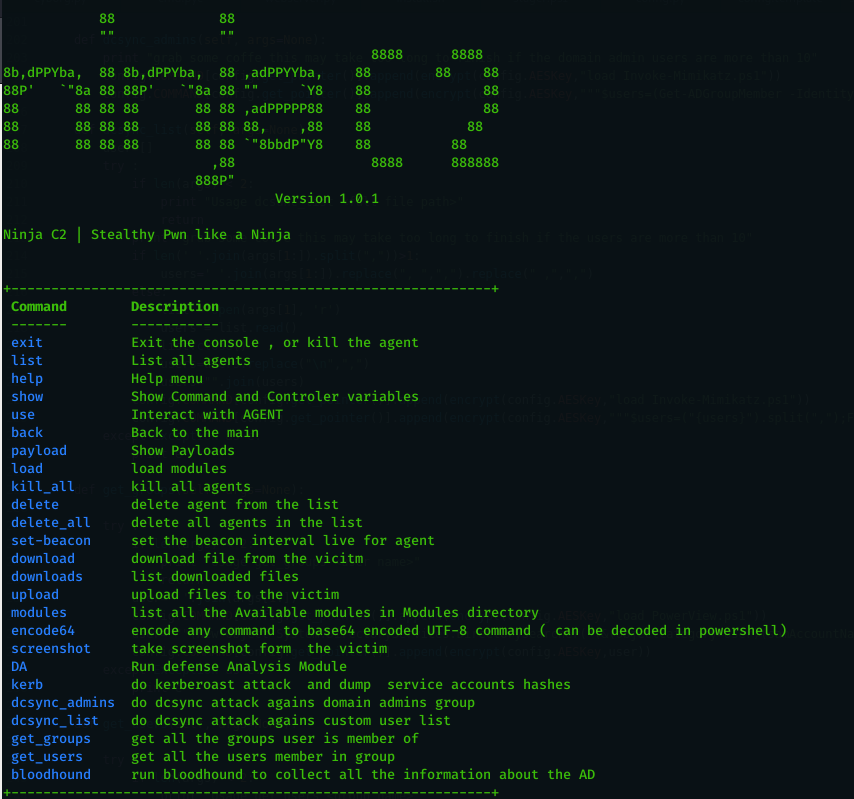 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 redcode-labs/bashark
Bash post exploitation toolkit
 al1ex/pentest-tools
Intranet penetration tools
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 raikia/credninja
A multithreaded tool designed to identify if credentials are valid, invalid, or local admin valid credentials within a network at-scale via SMB, plus…