
NetNTLMtoSilverTicket
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
authenticationexploitationlateral-movement+5
982
notmedic/netntlmtosilverticketSpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 dirkjanm/pkinittools
Tools for Kerberos PKINIT and relaying to AD CS
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
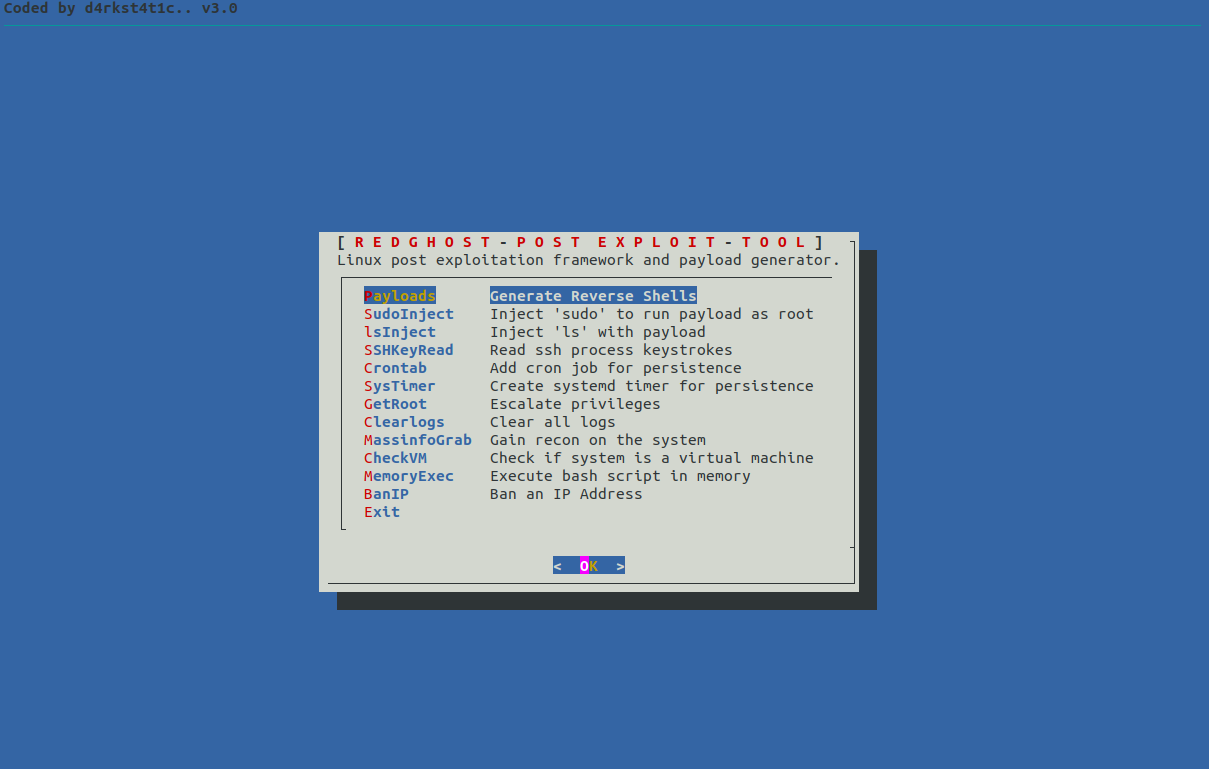 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 nccgroup/keimpx
Check for valid credentials across a network over SMB
 sensepost/impersonate
A windows token impersonation tool
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
 pinoywh1z/ssh-private-key-looting-wordlists
Curated wordlists for brute-forcing SSH private key filenames, aiding penetration testers in locating keys via LFI or enumeration during lateral…
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
 mitre/caldera-agent
Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
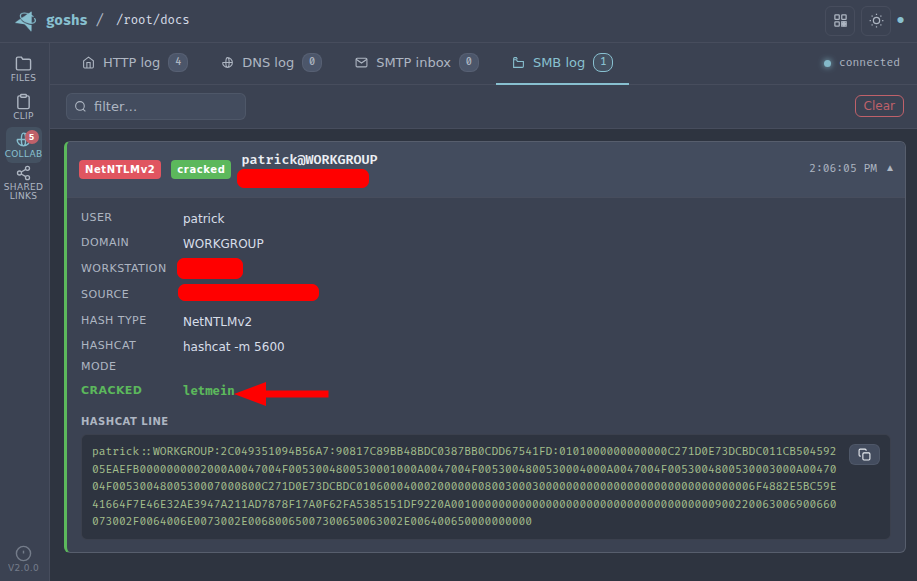 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 ghostpack/rubeus
Trying to tame the three-headed dog.
 0xthirteen/sharprdp
Remote Desktop Protocol .NET Console Application for Authenticated Command Execution
 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils