

gp_netSecDSS
 ahmad.zaid/netsecdss
Decision Support System for Risk Assessing Network and System Security in Small and Medium Enterprises (SMEs), A graduation project.
educationlabs-practicenetwork-security
ahmad.zaid/netsecdssDecision Support System for Risk Assessing Network and System Security in Small and Medium Enterprises (SMEs), A graduation project.

 kasunpriyashan/y2s1-project-linux-exploitaion-using-cve-2016-5195-vulnerability
Educational Linux privilege escalation exploit targeting CVE-2016-5195 (Dirty COW) to demonstrate kernel vulnerability exploitation and root access…
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 nu11secur1ty/linux_hardening_and_security
Collection of Linux hardening scripts and security configurations for system auditing, access control, and defensive posture improvement. Includes…
 arisharazakhan-cpu/dod-blue-team-network-lab
High fidelity defensive security lab simulating a DoD aligned enterprise network with Active Directory, VLAN segmentation, STIG based hardening,…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…
 elihiho/security-operations-labs
Threat Modeling, IT-/OT-Segmentierung, Snort Detection und reproduzierbare Validierung eines Drupal-Detection-Profils.
 kingsrule50/nessus-vulnerability-scanning-lab
Enterprise vulnerability management on Azure — Terraform-deployed Nessus scanner, credentialed scanning, CVE-2013-3900 remediation with verified…
 amirmuhammadmarvi/network-security-lab
Controlled virtual attack & defense lab — CVE-2011-2523 exploitation, Nmap recon, Nikto scanning, UFW hardening on Metasploitable 2
 ikarolaborda/cve2026-42926
Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research
 hirokiii/cve-2023-44487
Educational environment for LTAT.04.022 Homework 4.
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
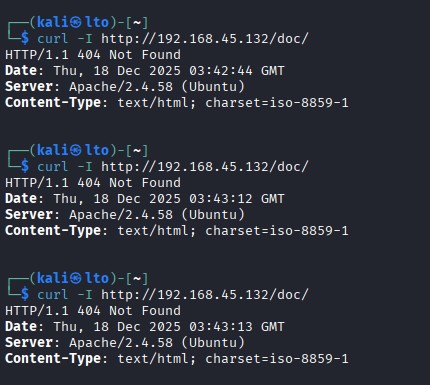 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable