mediawiki-CVE-2026-100382

Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…

Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…

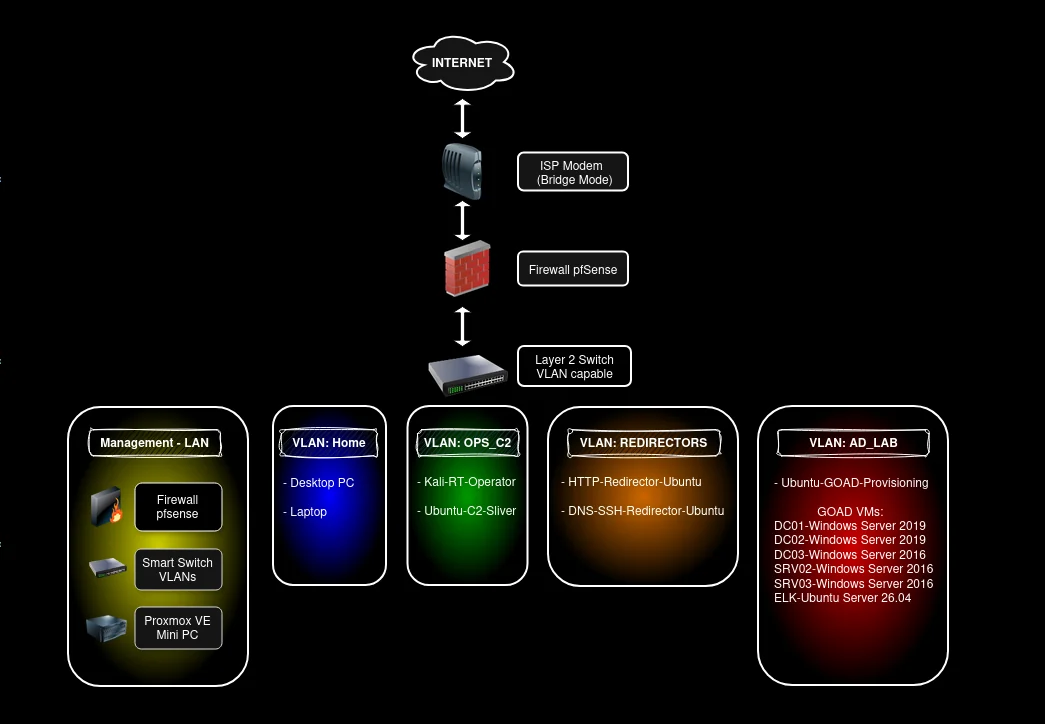
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…

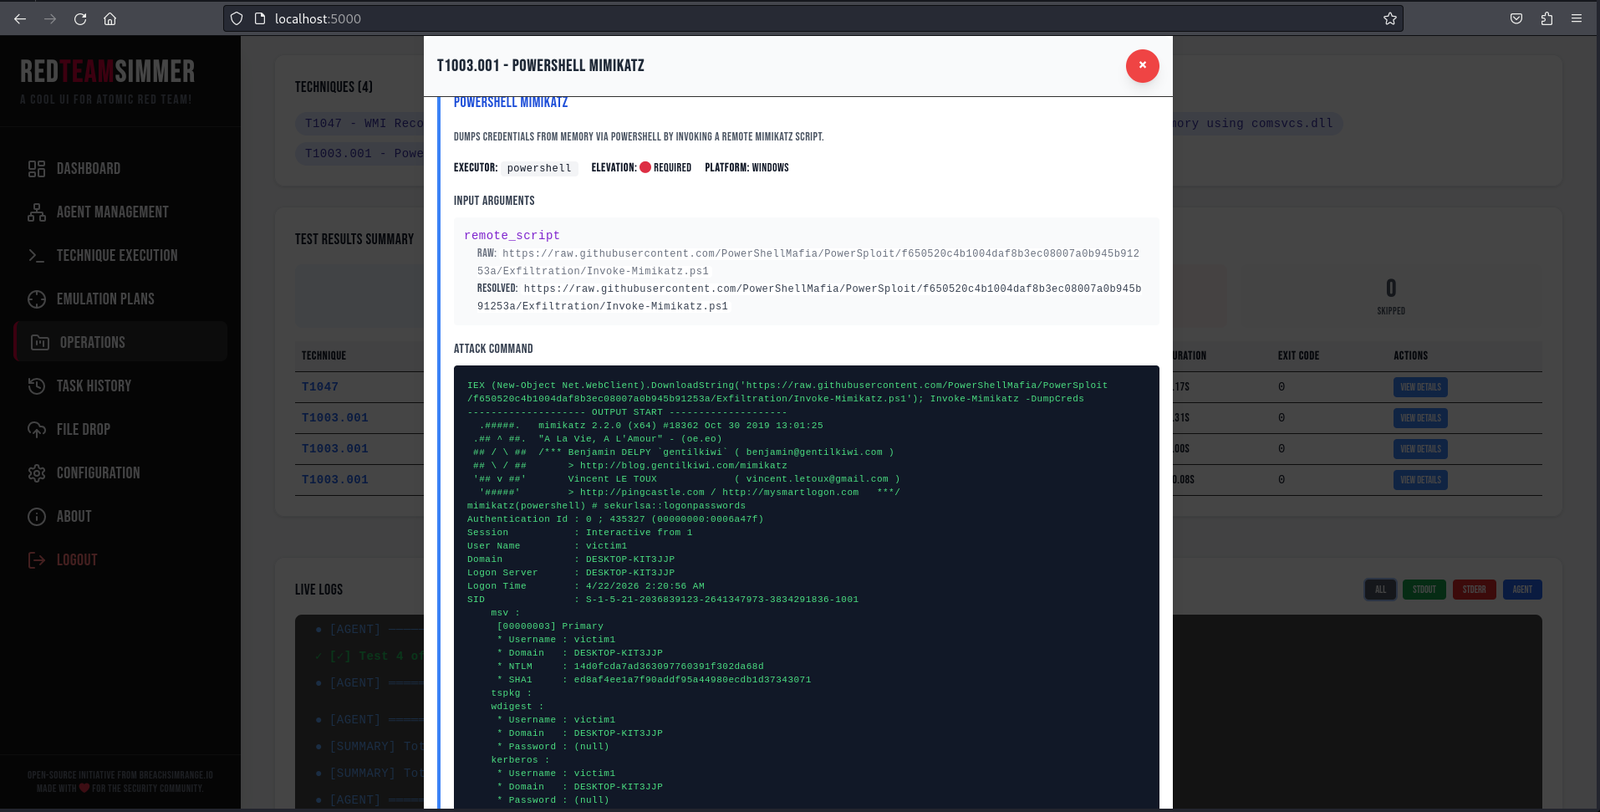
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

Automated Adversary Emulation Platform

Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…

Step-by-step walkthrough exploiting CVE-2023-30258 (MagnusBilling RCE) and escalating privileges via fail2ban misconfiguration on a TryHackMe lab.…

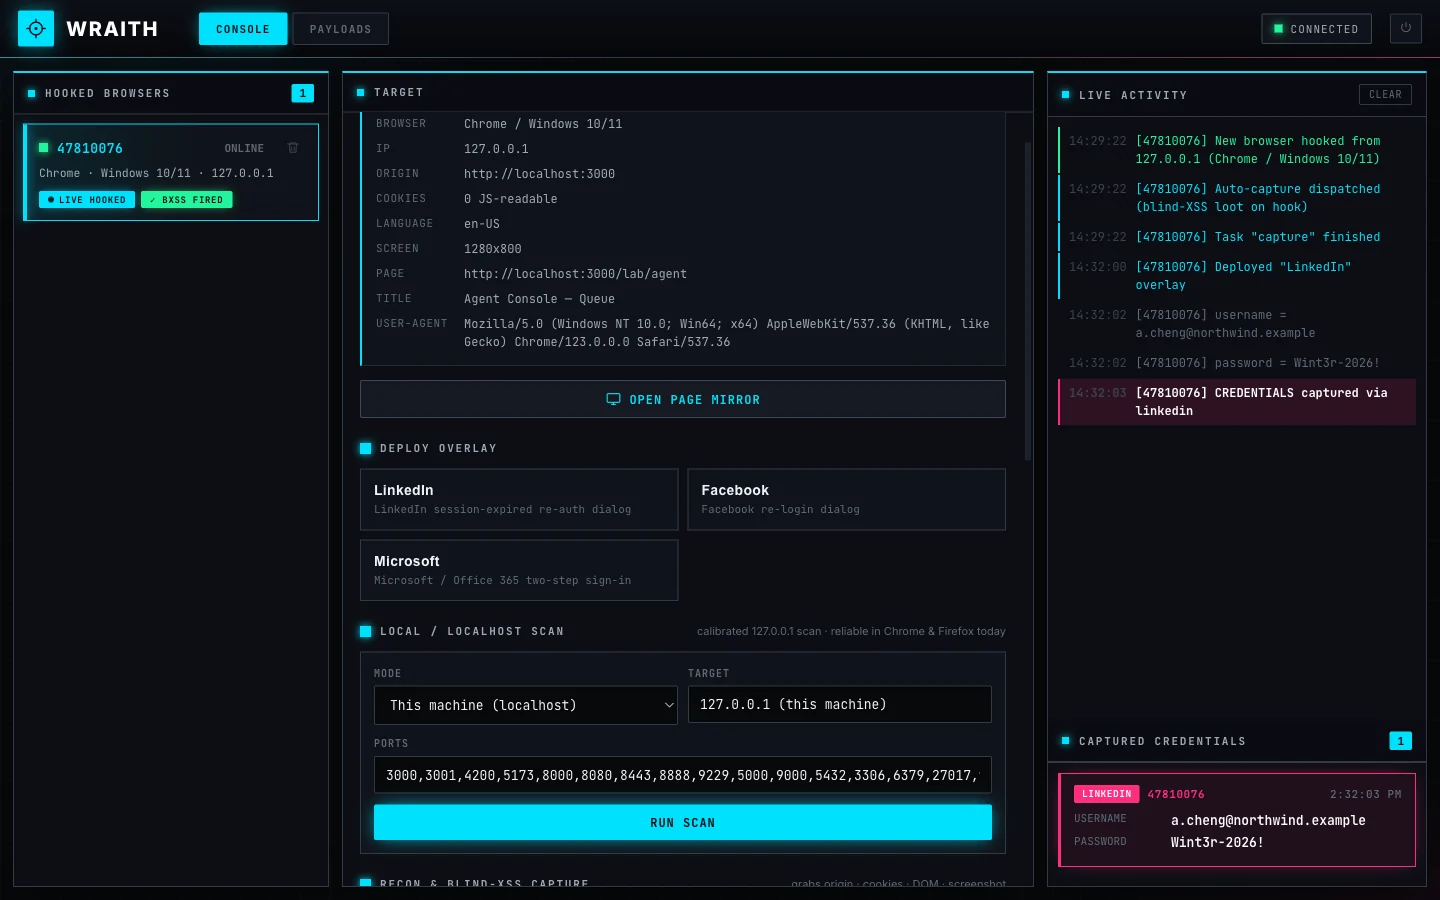
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…

Reproduction of cve-2024-3400-panos_rce_reproduction

CVE-2026-63030 + CVE-2026-60137 - “wp2shell”: unauthenticated RCE in WordPress core

Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…

Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…

PoC for CVE-2025-55319

PoC for CVE-2023-22496: Netdata Agent <1.37 OS Command Injection via registry_hostname

CVE-2026-58138 — Conductor (3.21.21..<3.30.2) unauthenticated RCE via INLINE GraalVM evaluator (HostAccess.ALL). Lab + PoC, verified e2e (root).