

work1-secure-api
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
api-securityauthentication-authorizationdevsecops+7
ght657/work1-secure-apiHDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 abraxas/ats-realip-plugin-acl
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
 zishanadthandar/pentest
Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
 abraxas/pfsense-api-fleet-jwt
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - IDOR - one controller JWT is a fleet token
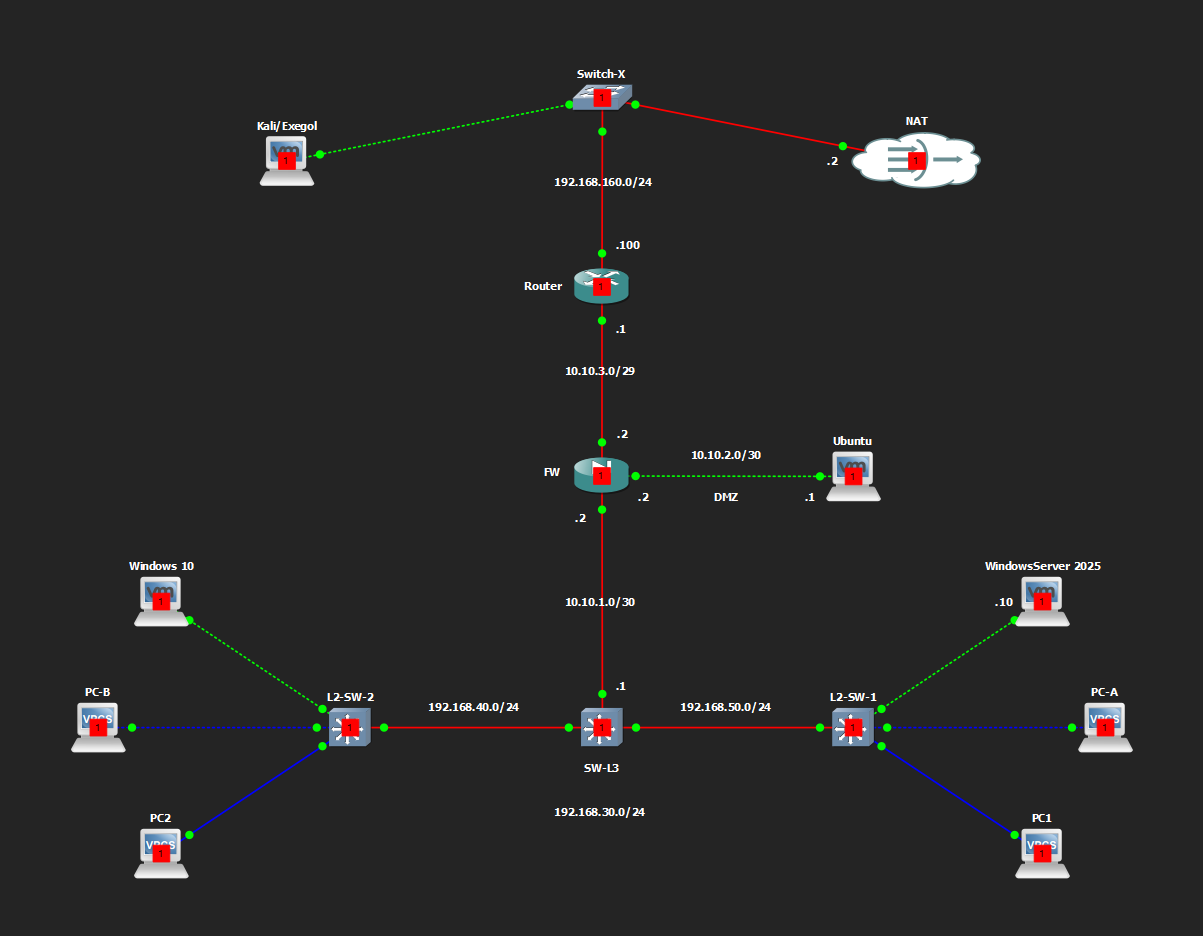 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 dievus/powershellforpentesters
Course repository for PowerShell for Pentesters Course
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 zephrfish/ludus-defender-lab
MDE/MDI Defender setup for Ludus
 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
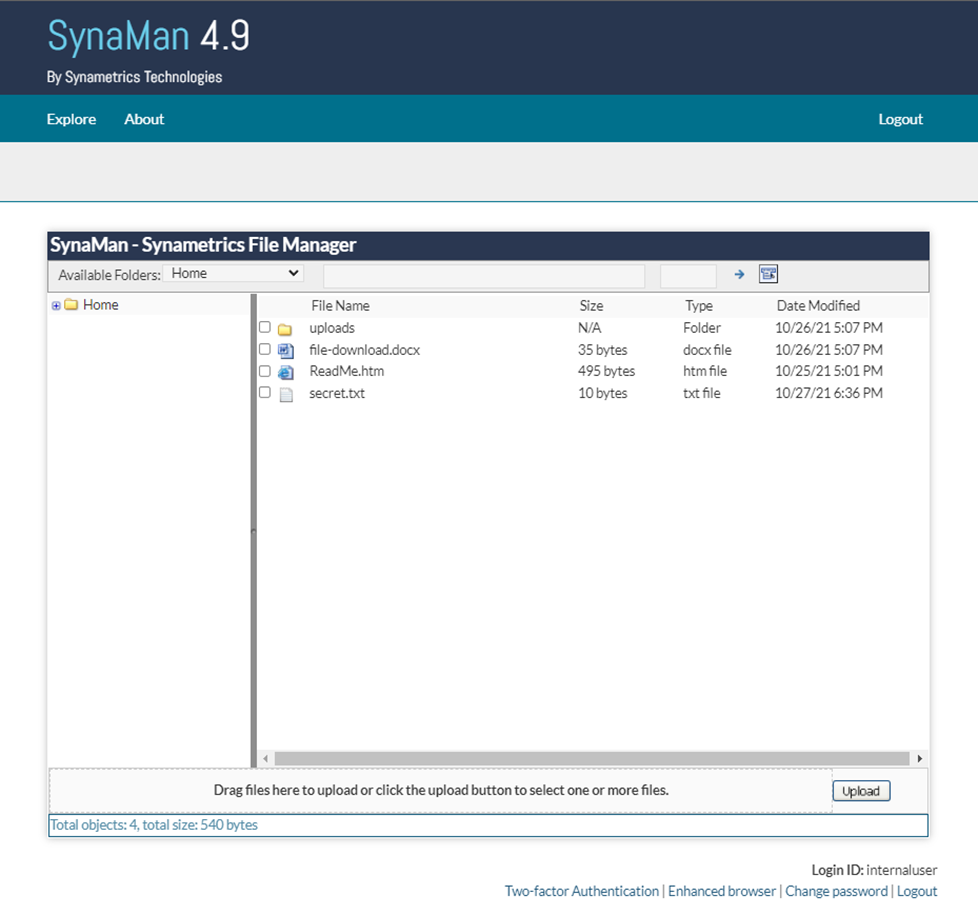 videnlabs/cve-2022-22828
Write-up of CVE-2022-22828
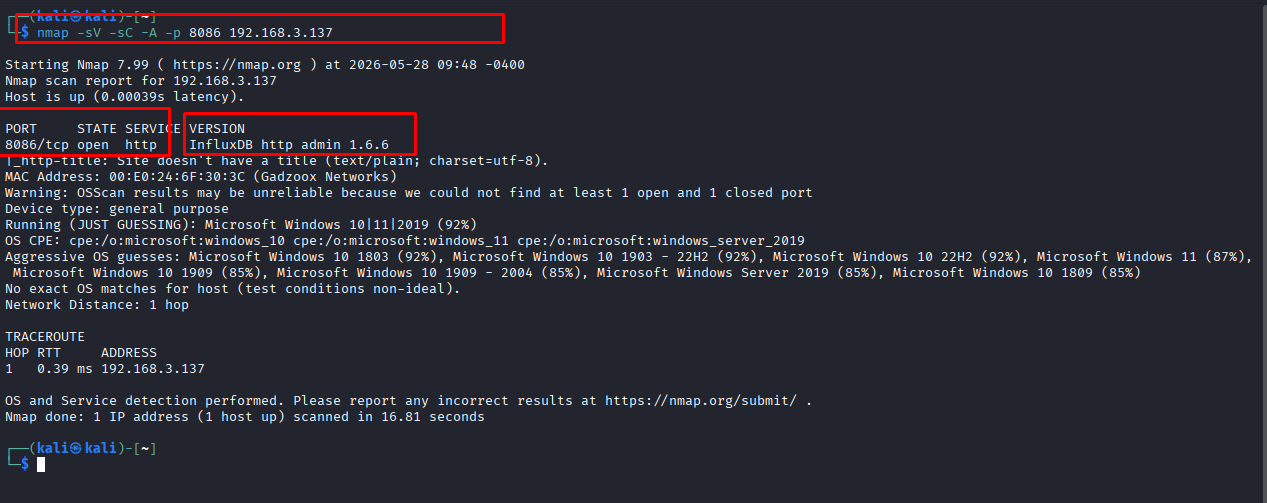 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…