
esp32-sniffer
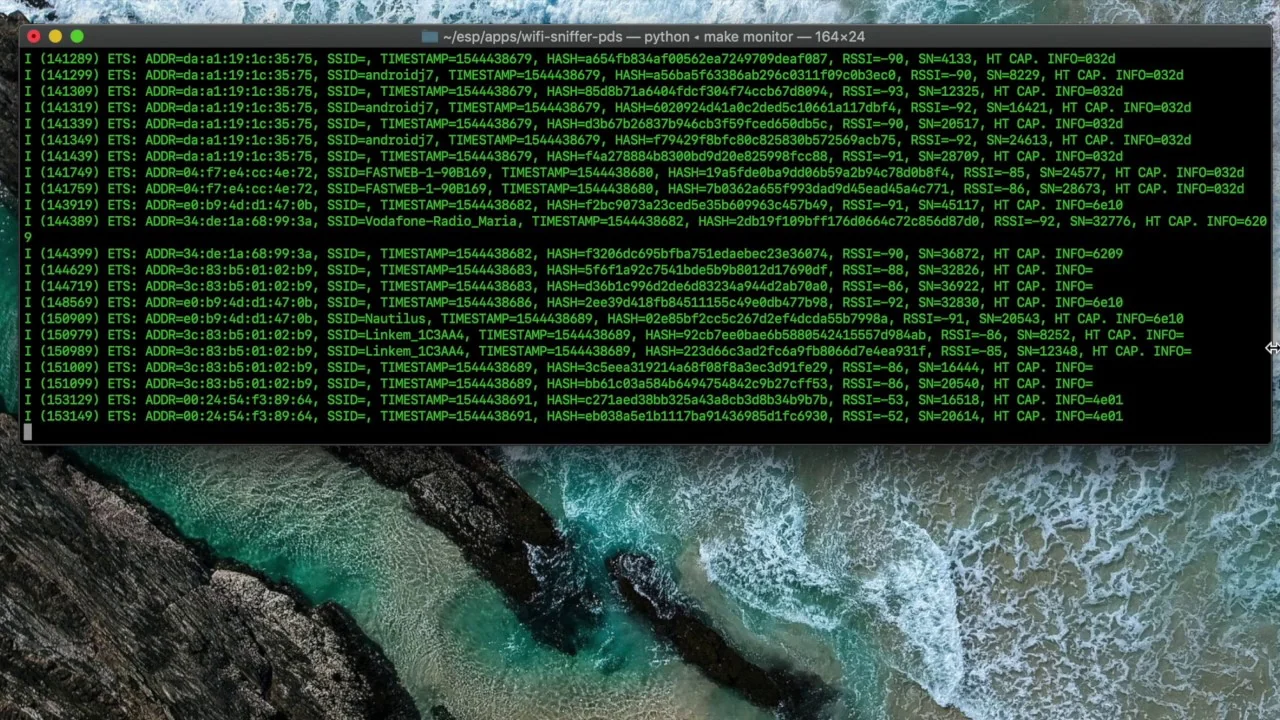
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information

ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information

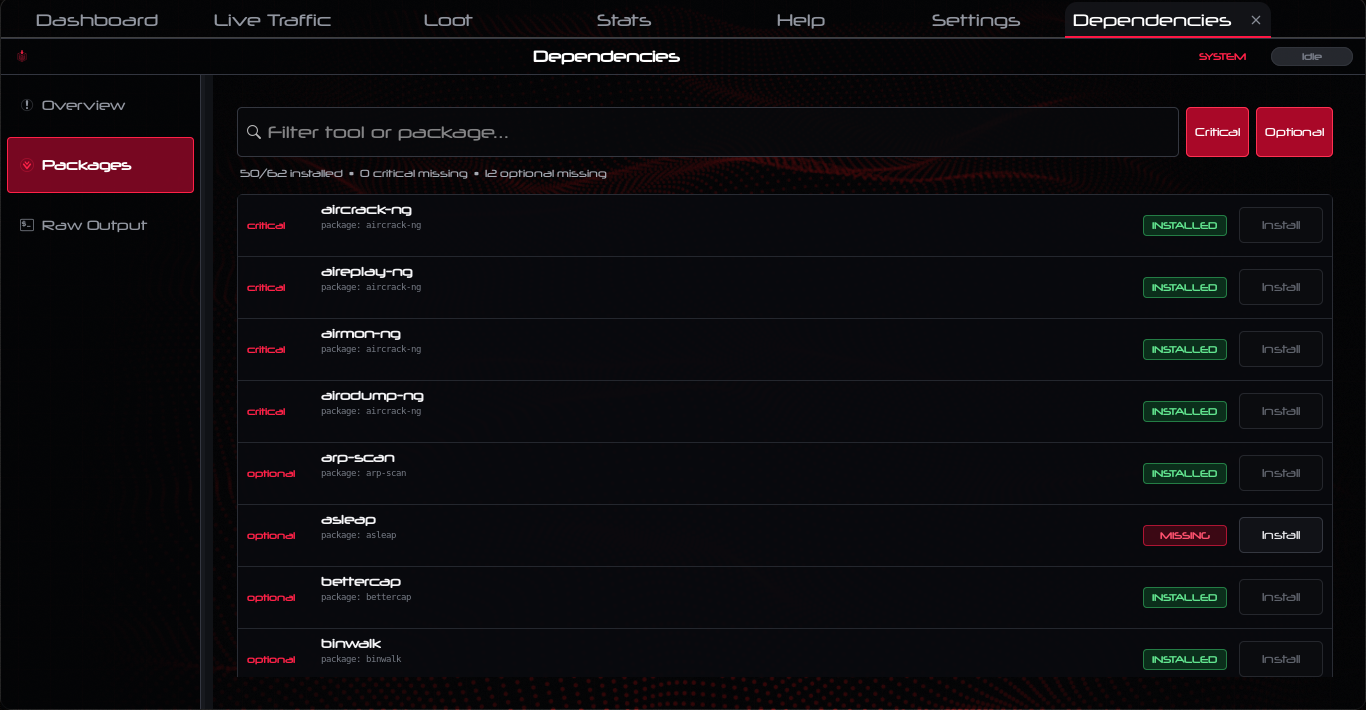
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…

Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.

GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…

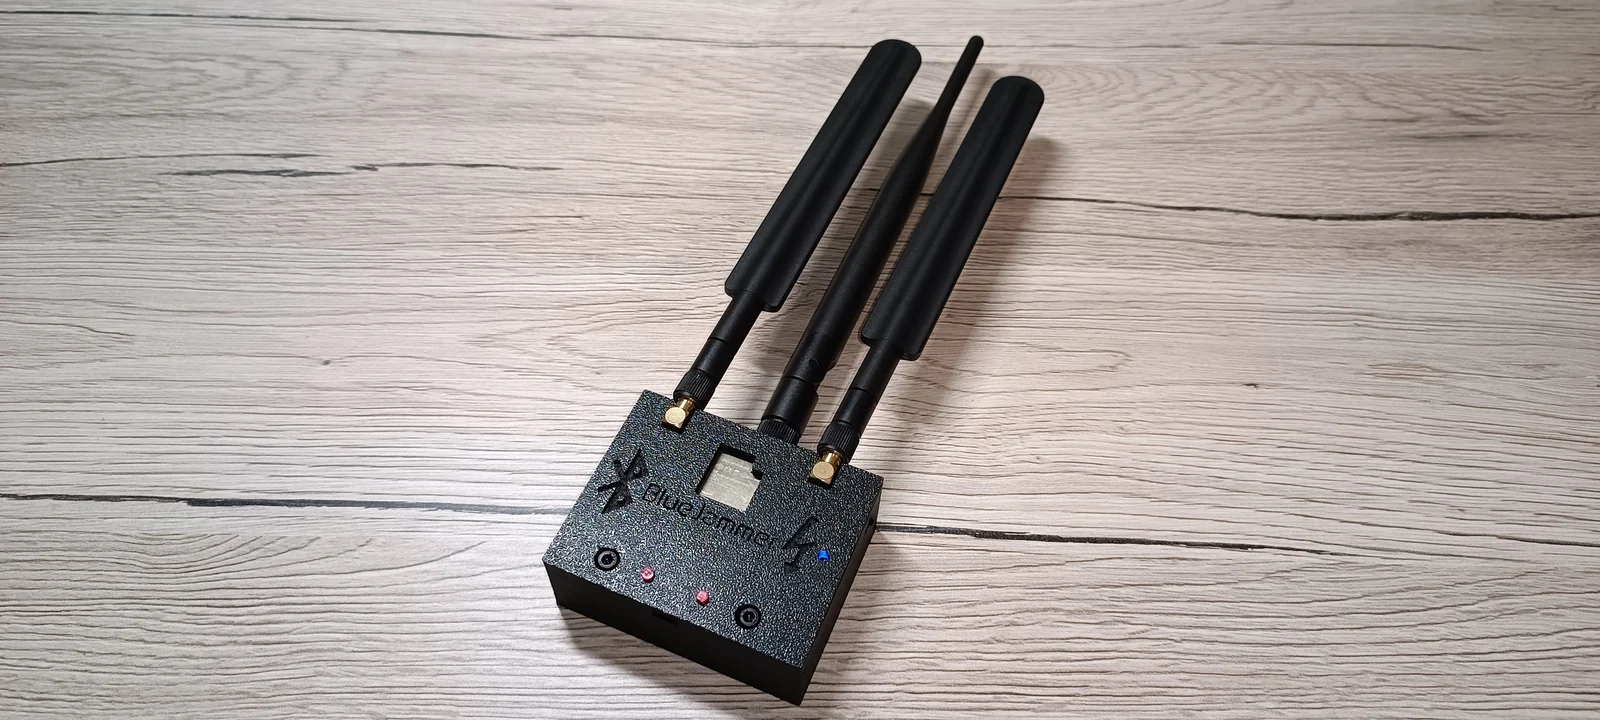
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.

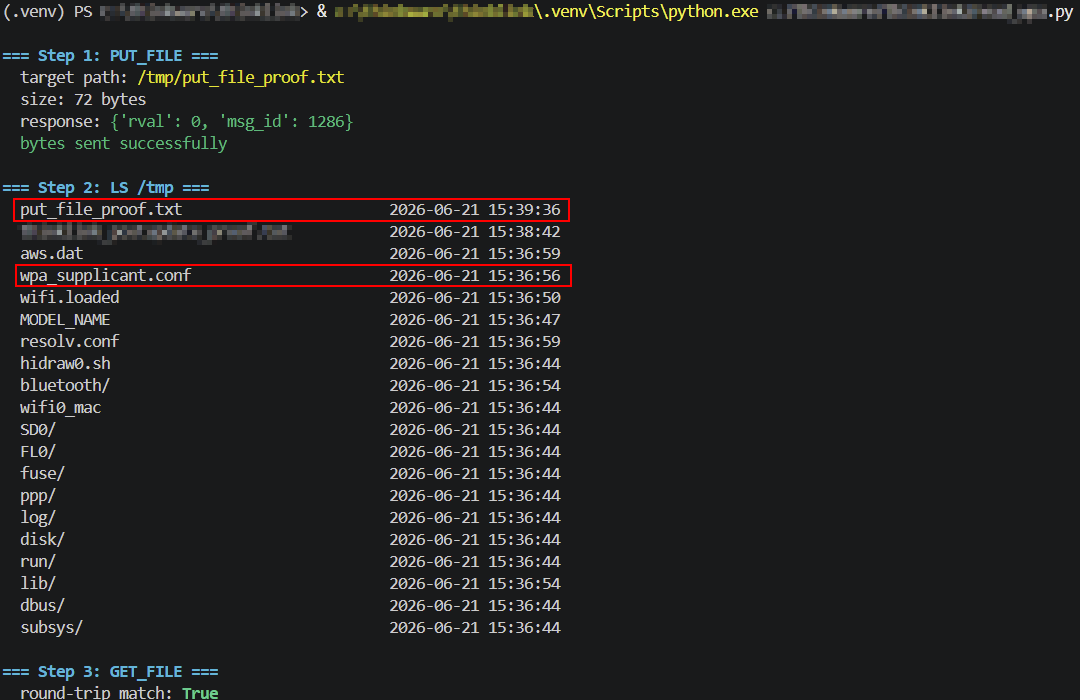
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…

Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…

Proof-of-concept exploiting DJI drone Bluetooth DUML command injection, sending unauthenticated commands to read credentials, alter Wi-Fi config, and…

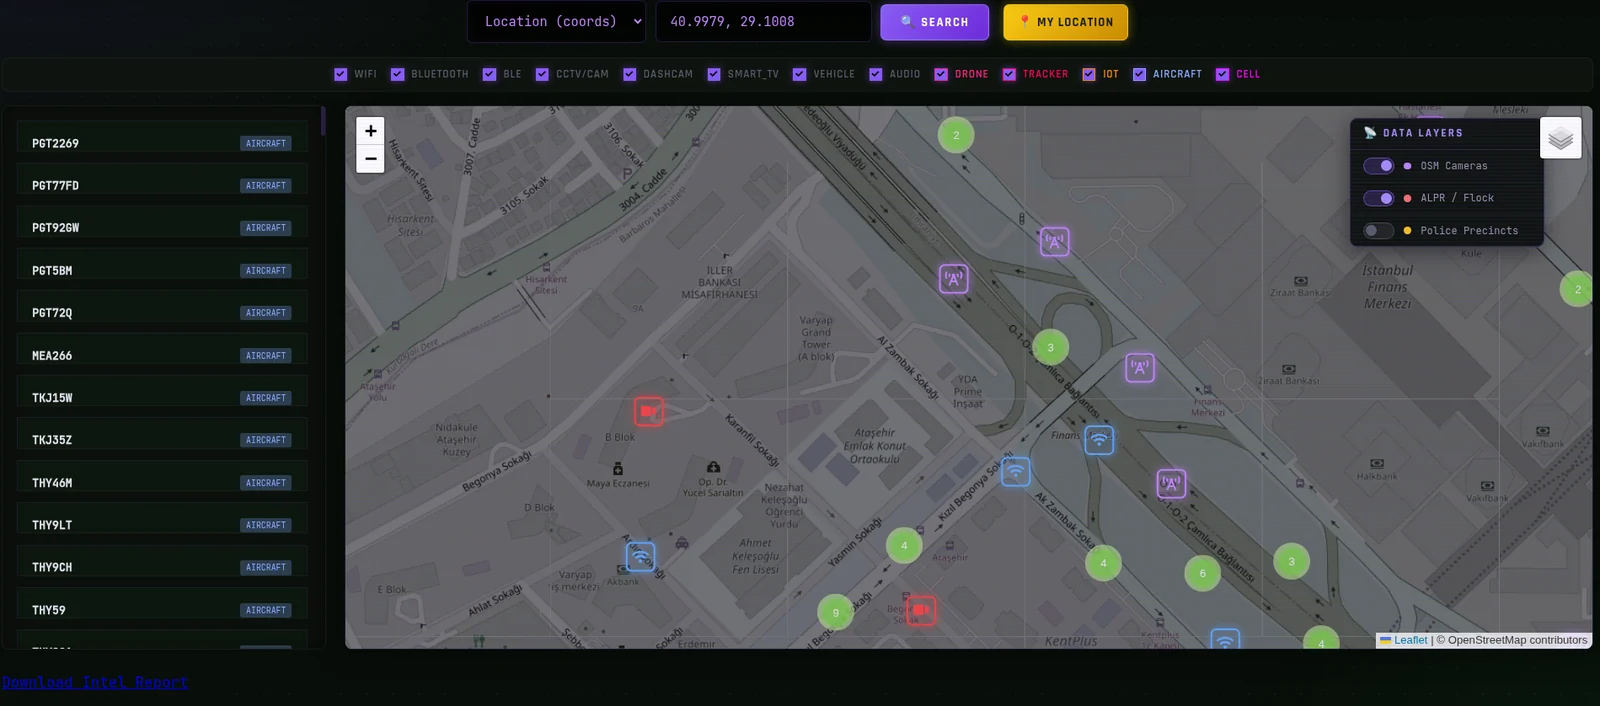
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…

Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…

Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…

Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers

Python3 script to scan for Linksys smart wifi devices that are vulnerable to CVE-2014-8244

eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

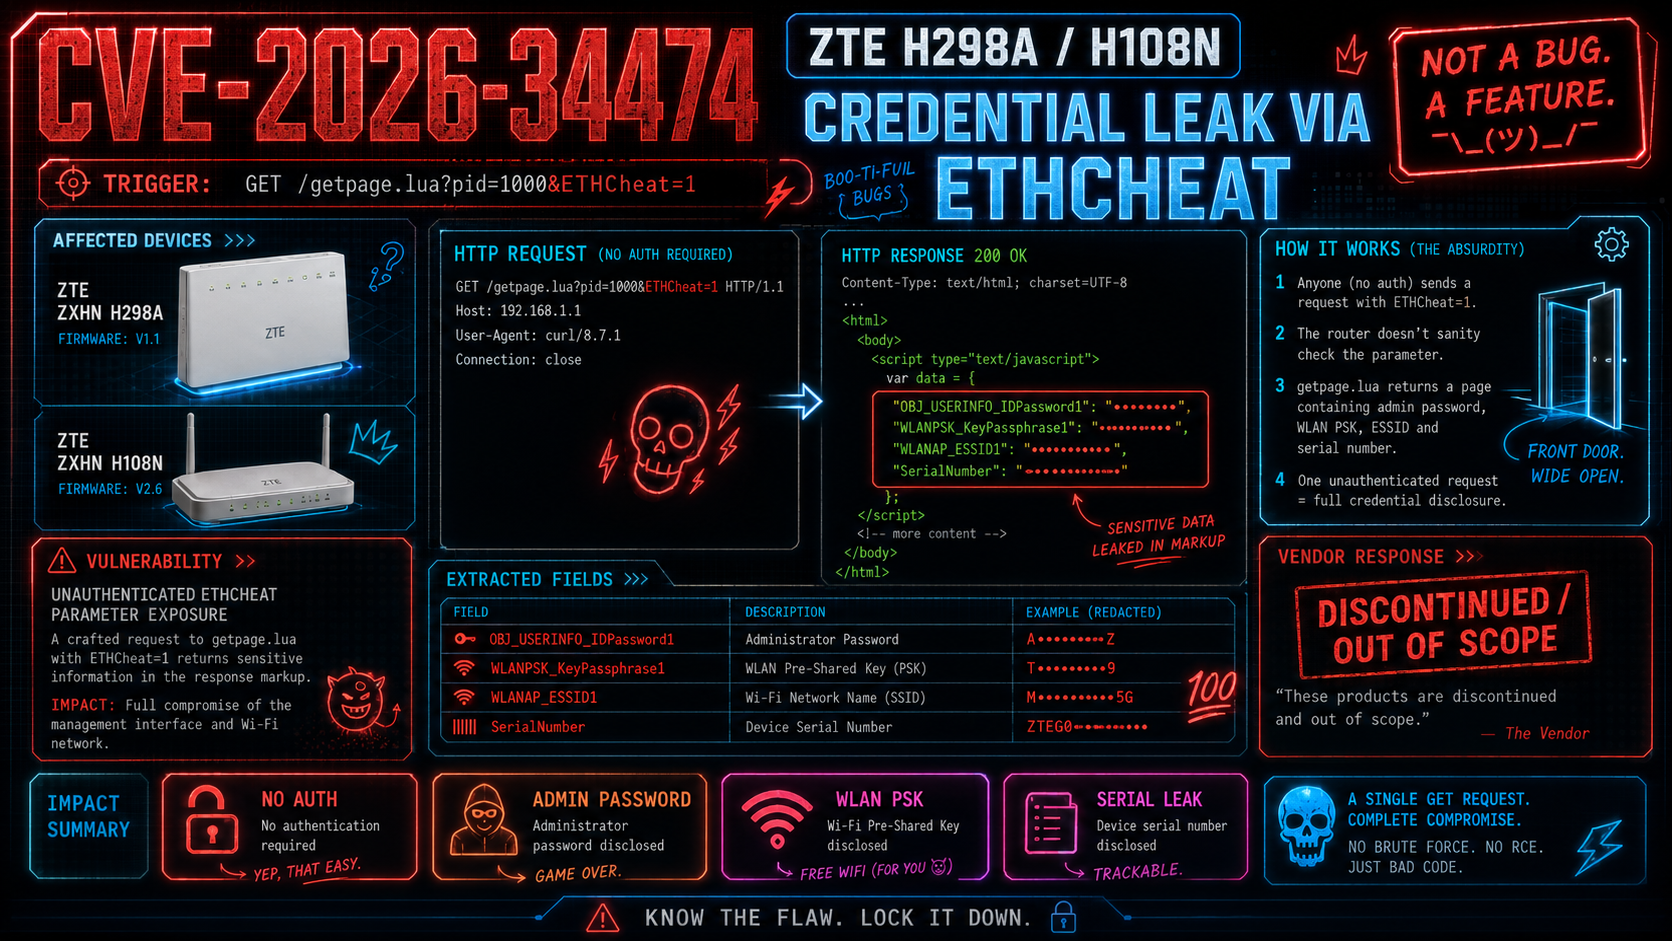
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.

Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…