process-watcher
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
defensive-toolsdynamic-analysis-sandboxingincident-response+4
13
neo23x0/process-watcherA process monitoring tool that tries to detect exploitation
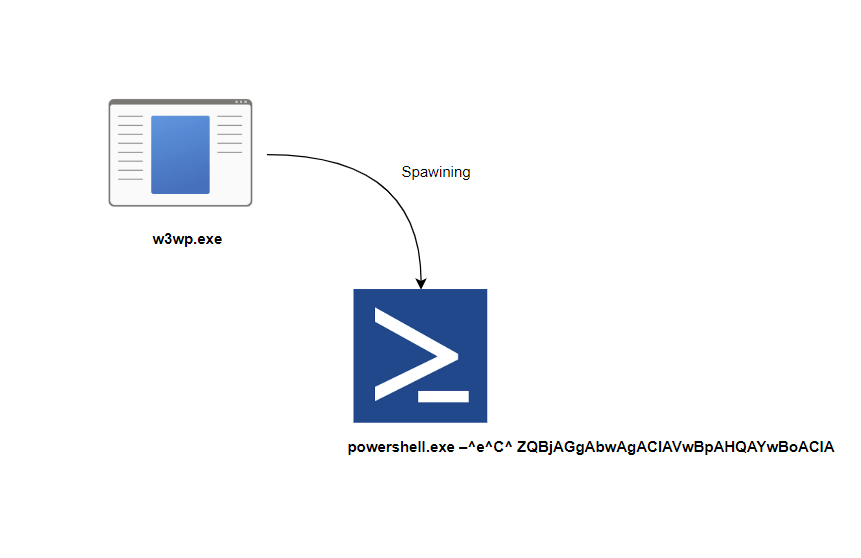 alwashali/detection-validation
Detection rule validation
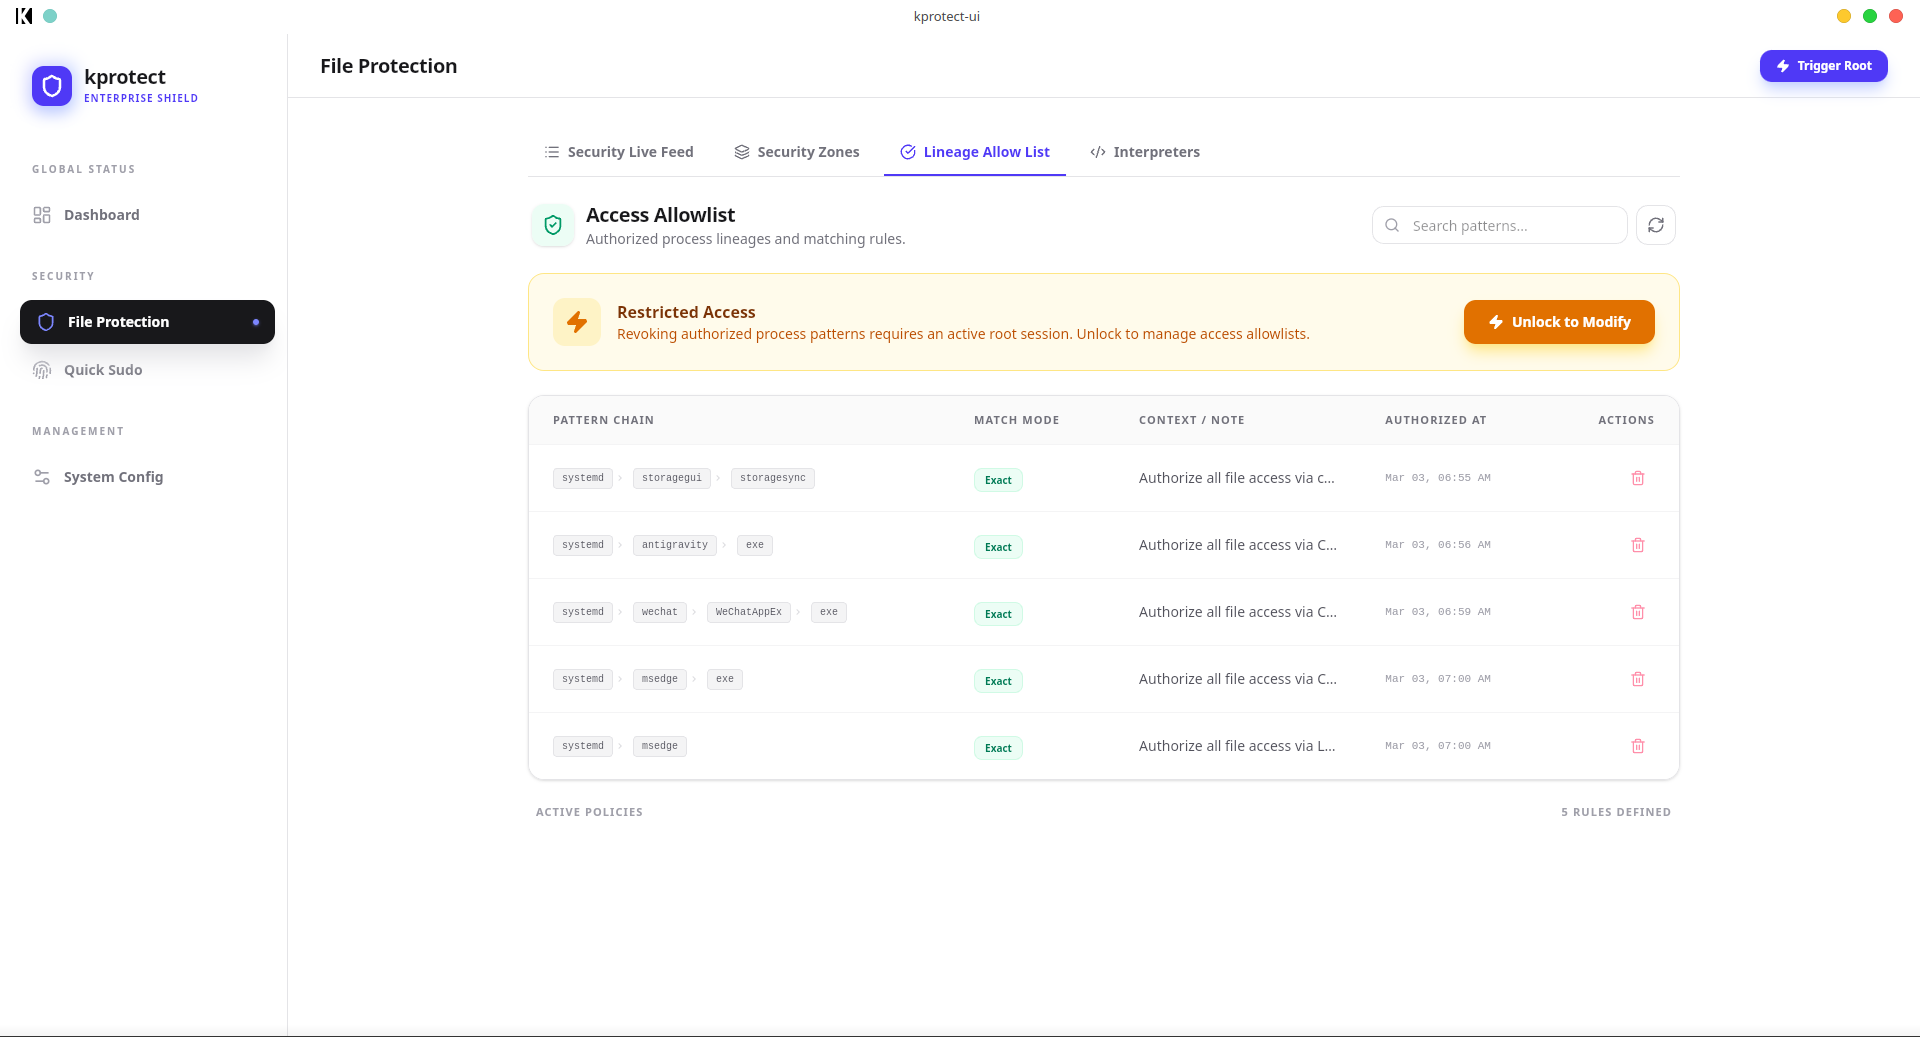 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 ernestak/sigma-rule-for-cve-2022-30190
Sigma rule for detecting exploitation of CVE-2022-30190 (Follina) via Windows process creation events, enabling SOC teams to identify malicious…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
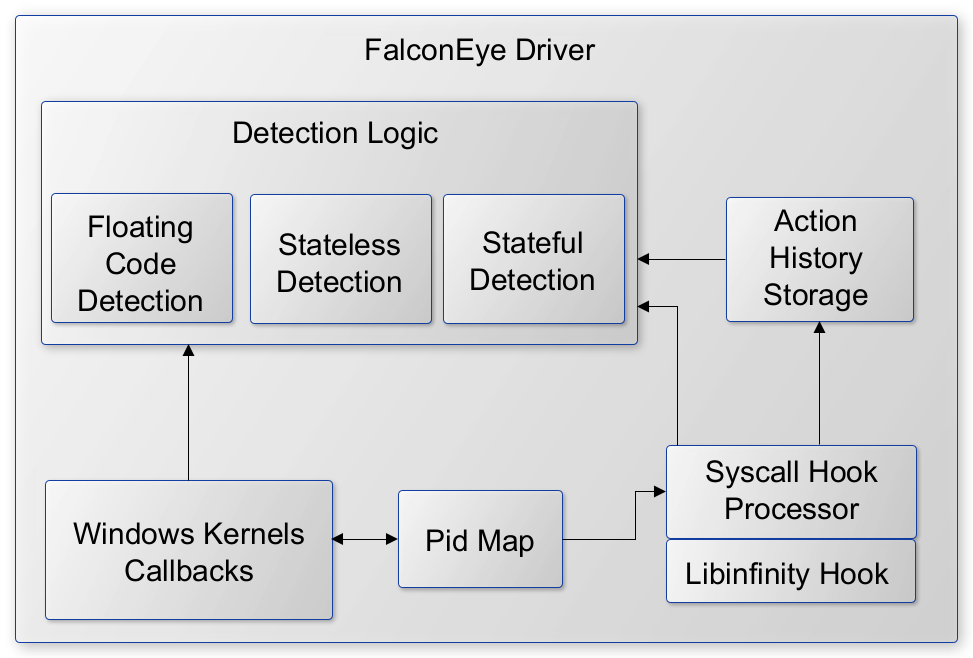 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 yjesus/patriot-linux
Host IDS for desktop users
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.