
siper
 fksvs/siper
XDP Based Lightweight and Fast Firewall
cloud-securityconfiguration-auditingdefensive-tools+3
fksvs/siperXDP Based Lightweight and Fast Firewall
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 arisharazakhan-cpu/dod-blue-team-network-lab
High fidelity defensive security lab simulating a DoD aligned enterprise network with Active Directory, VLAN segmentation, STIG based hardening,…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
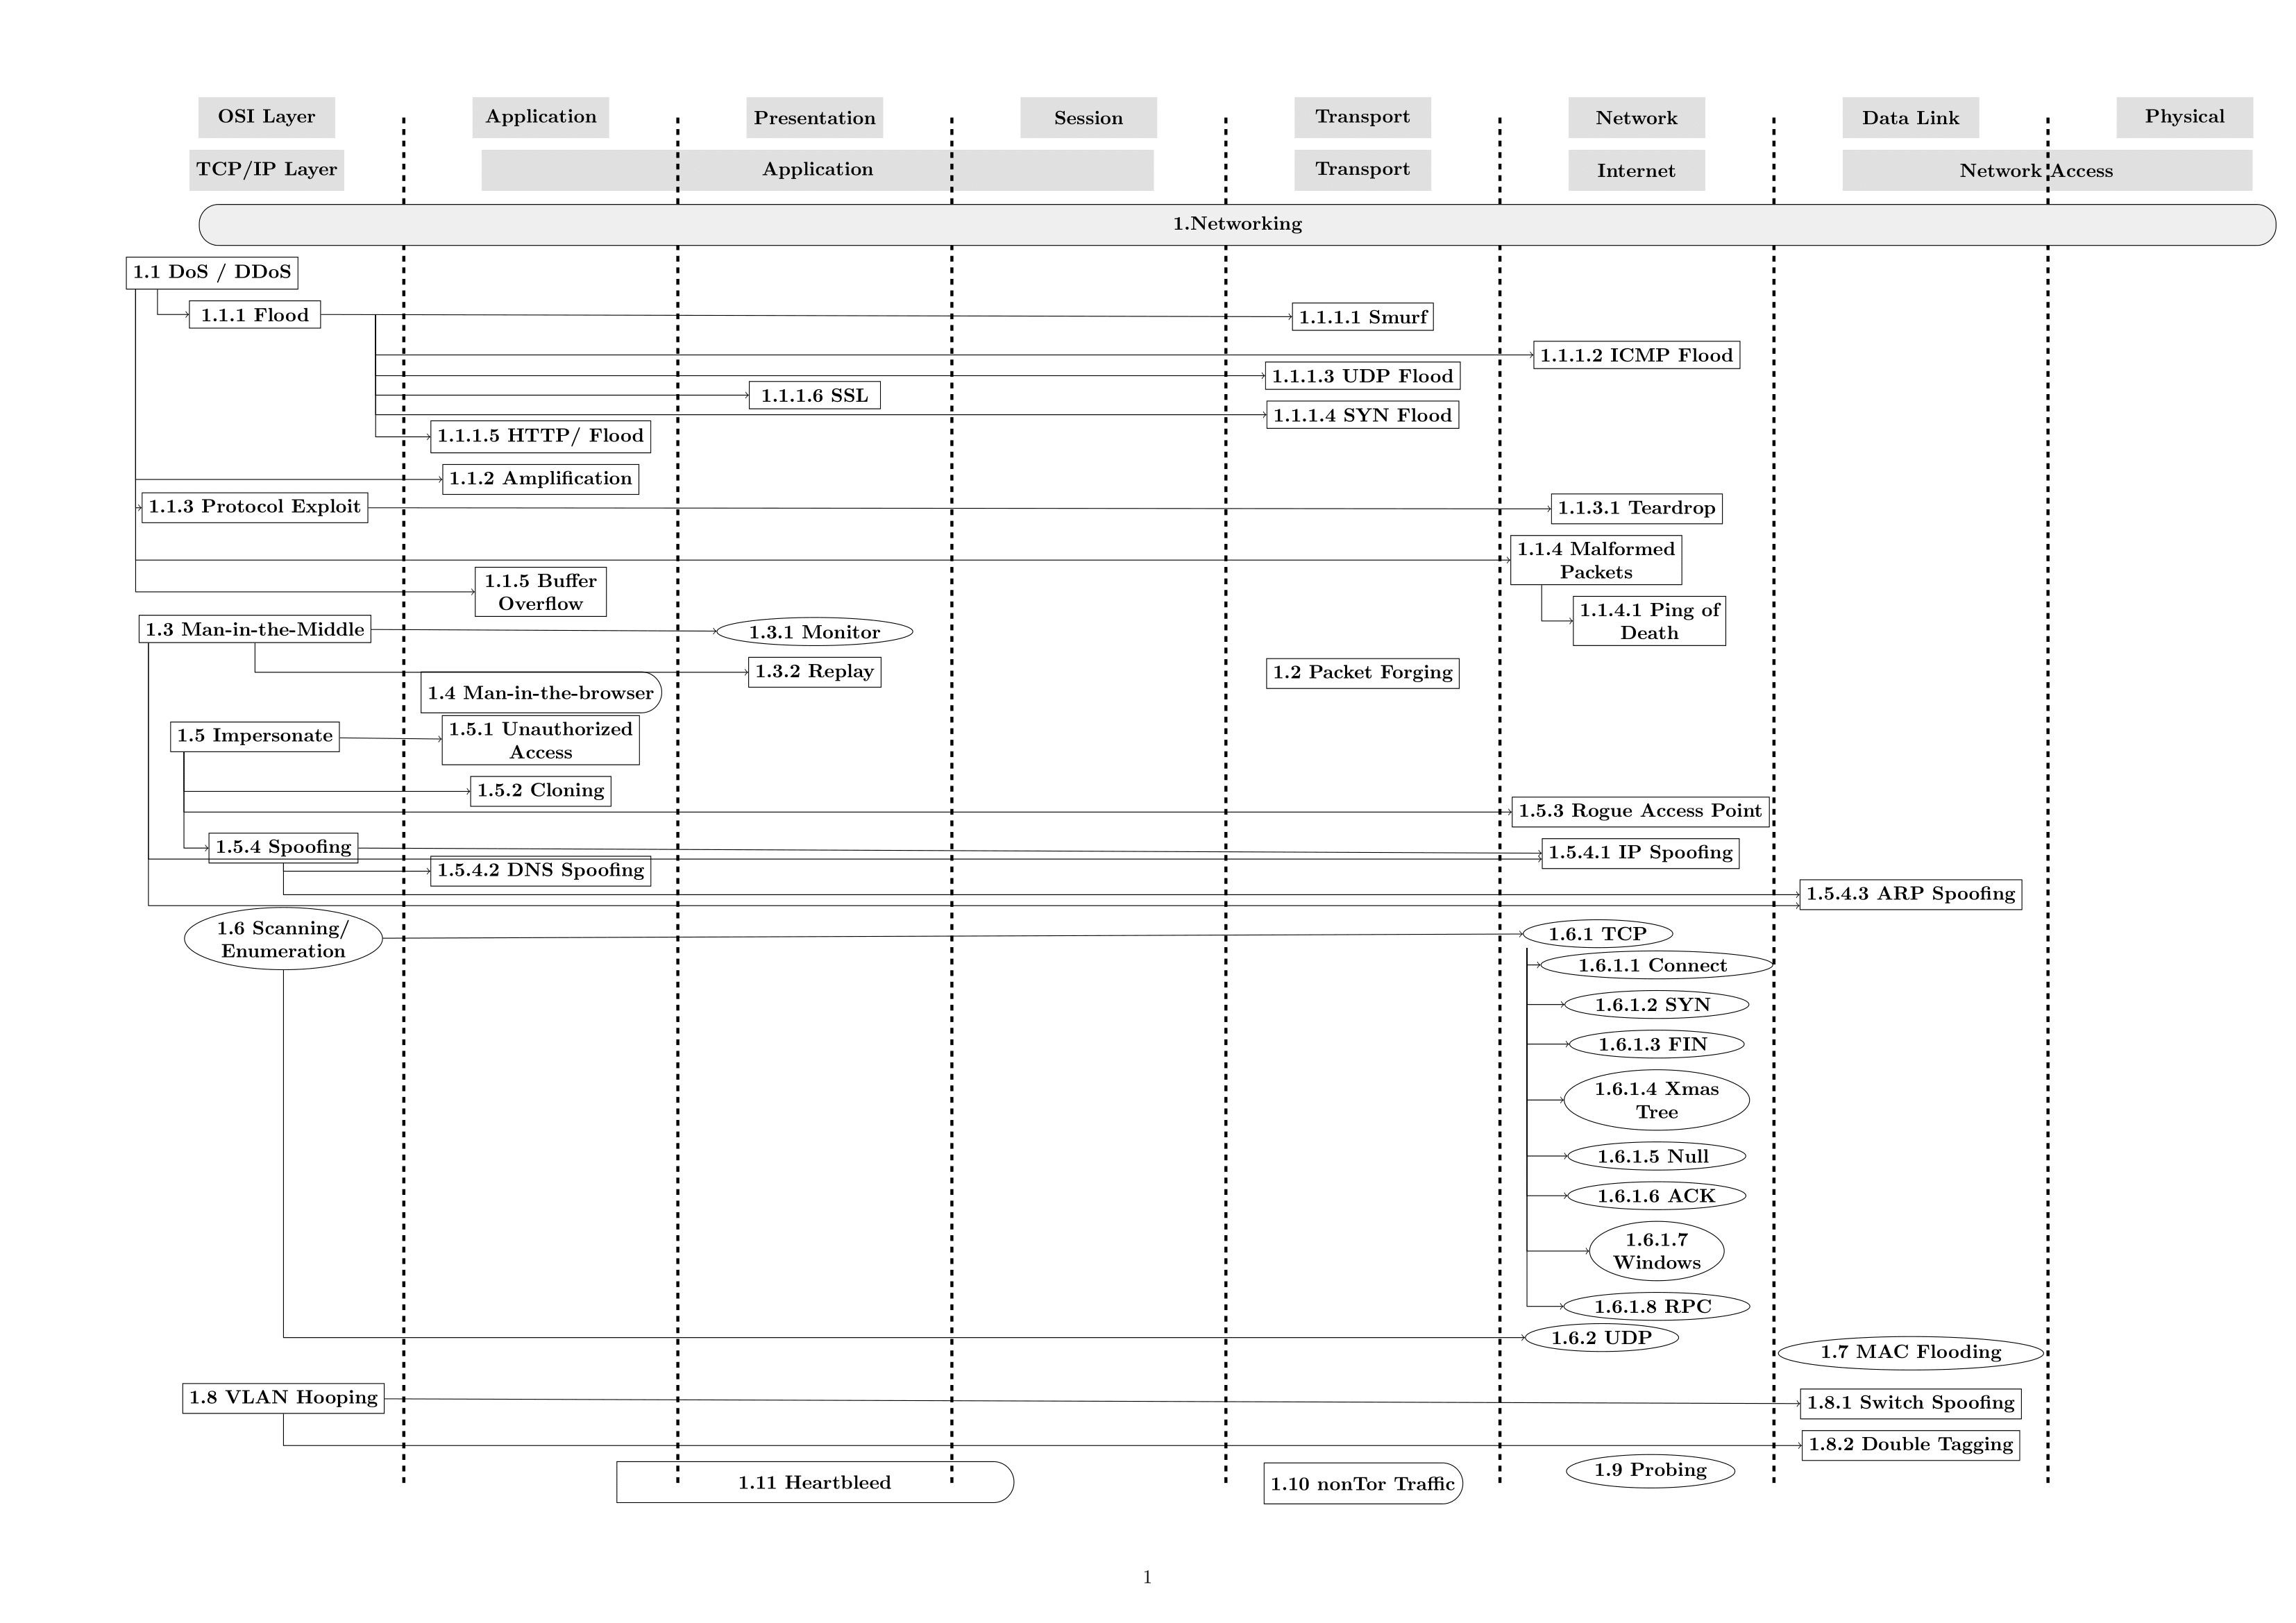 abertaymachinelearninggroup/network-threats-taxonomy
Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…
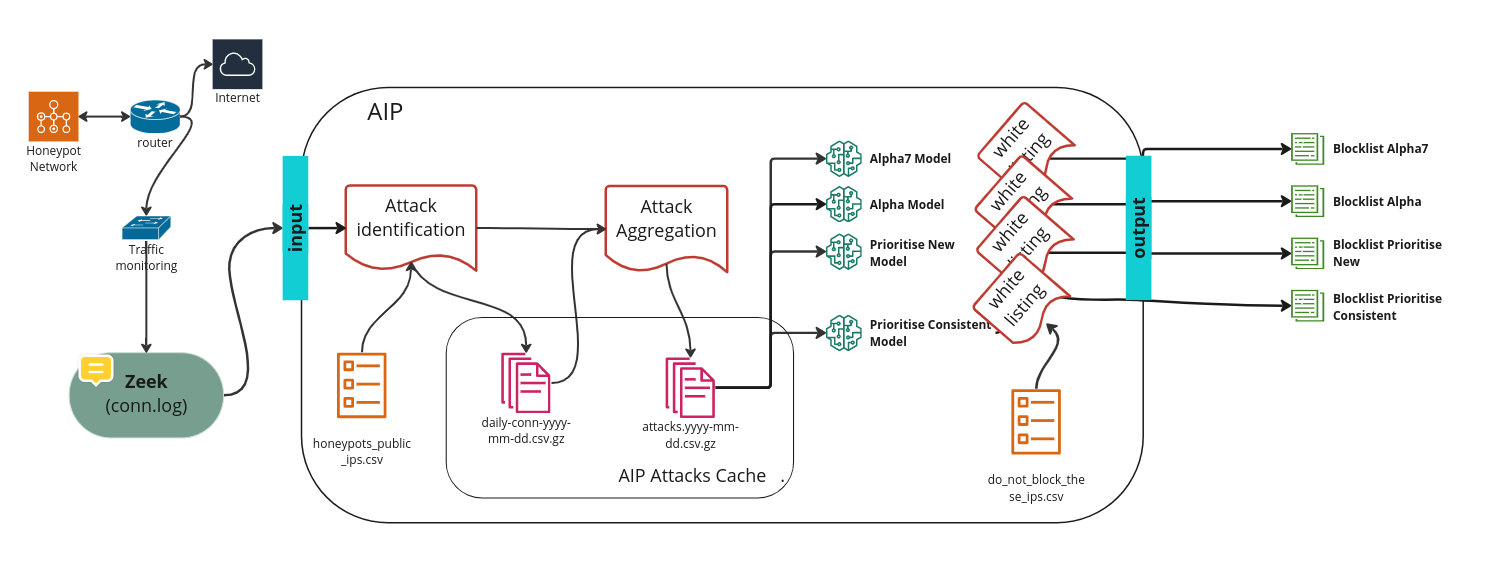 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 nccgroup/ip-reputation-snort-rule-generator
A tool to generate Snort rules based on public IP reputation data
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
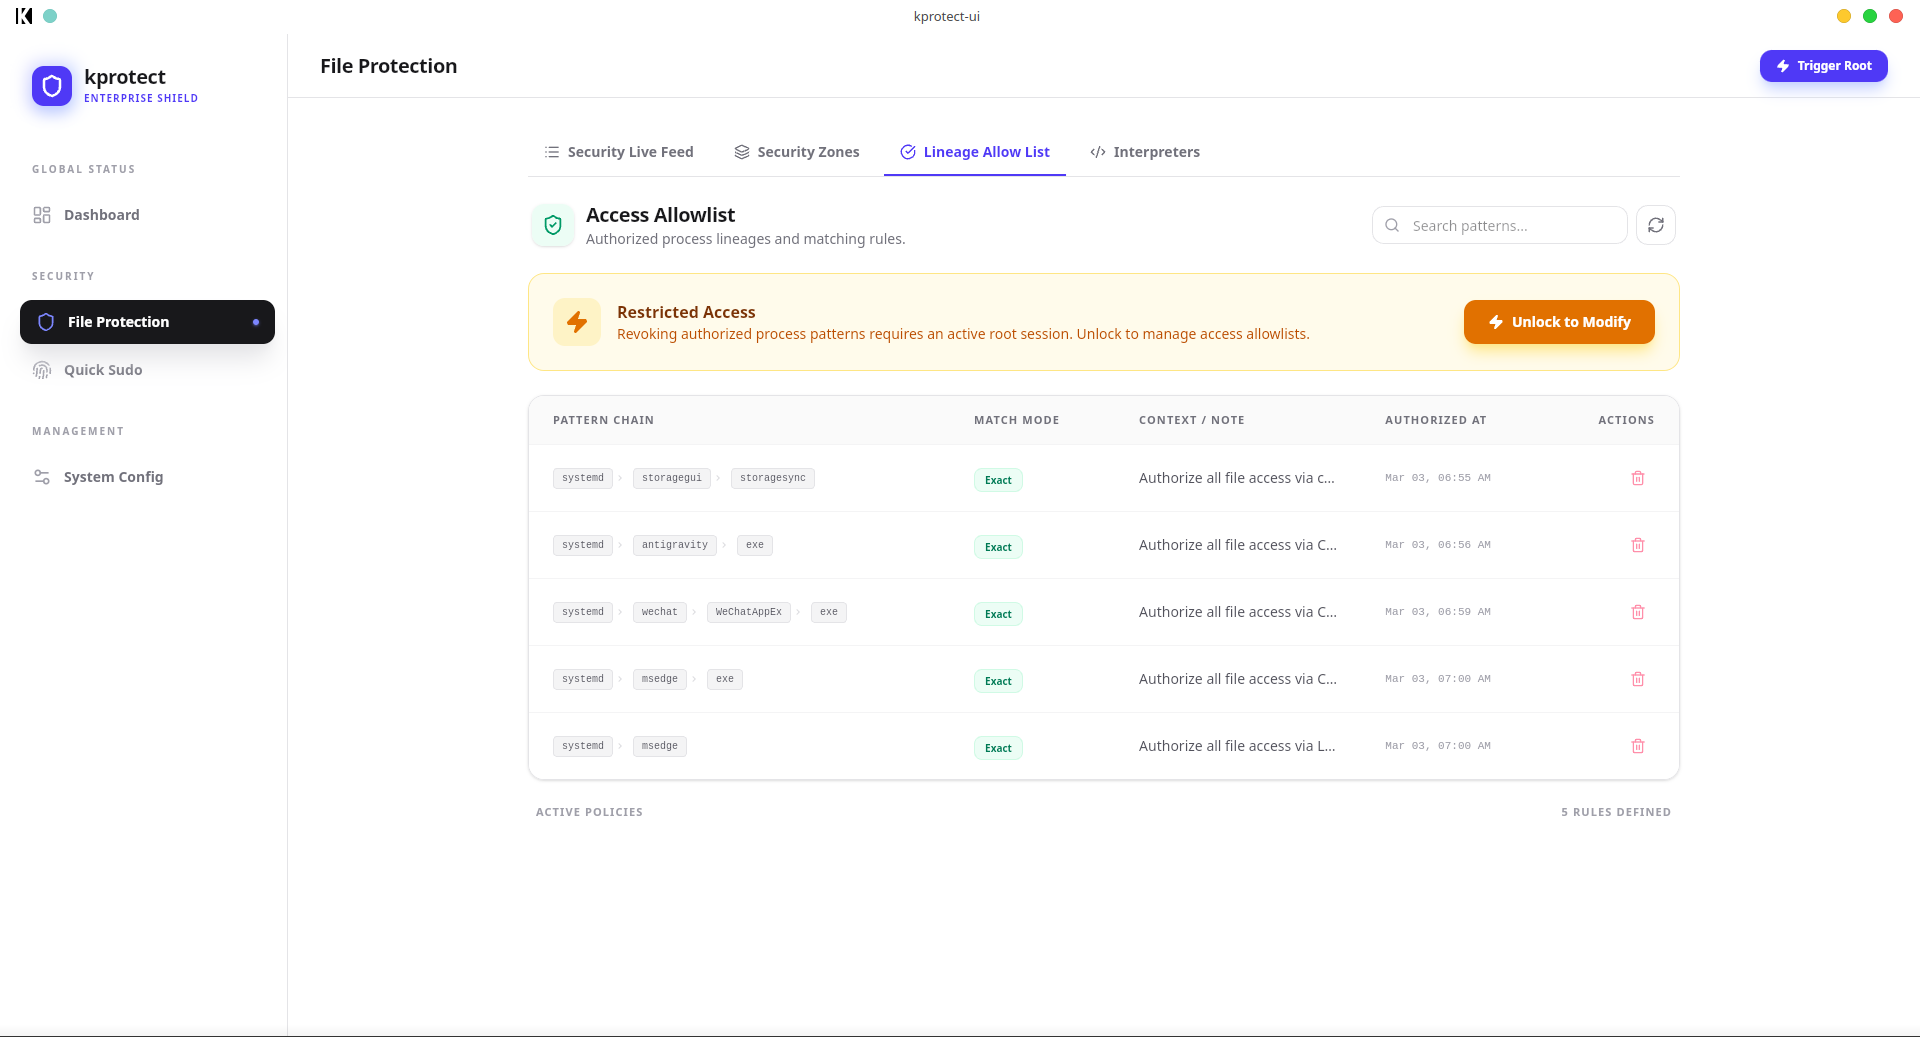 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 corelight/zeek-spicy-openvpn
A Zeek OpenVPN protocol analyzer, based on Spicy.
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.