
fire-wall-server
 nosie12/fire-wall-server
Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
defensive-toolseducationintrusion-detection+3
nosie12/fire-wall-serverPython-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 corelight/detect-ransomware-filenames
Zeek script that monitors SMB traffic and alerts on known ransomware filenames using the Anti-Ransomware File System Resource Manager list.
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 alloysecuregroup/phantomfs
Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
 sinologicnet/sipcheck
Monitors Asterisk authentication logs and automatically bans IPs with repeated failed login attempts using iptables, with configurable thresholds and…
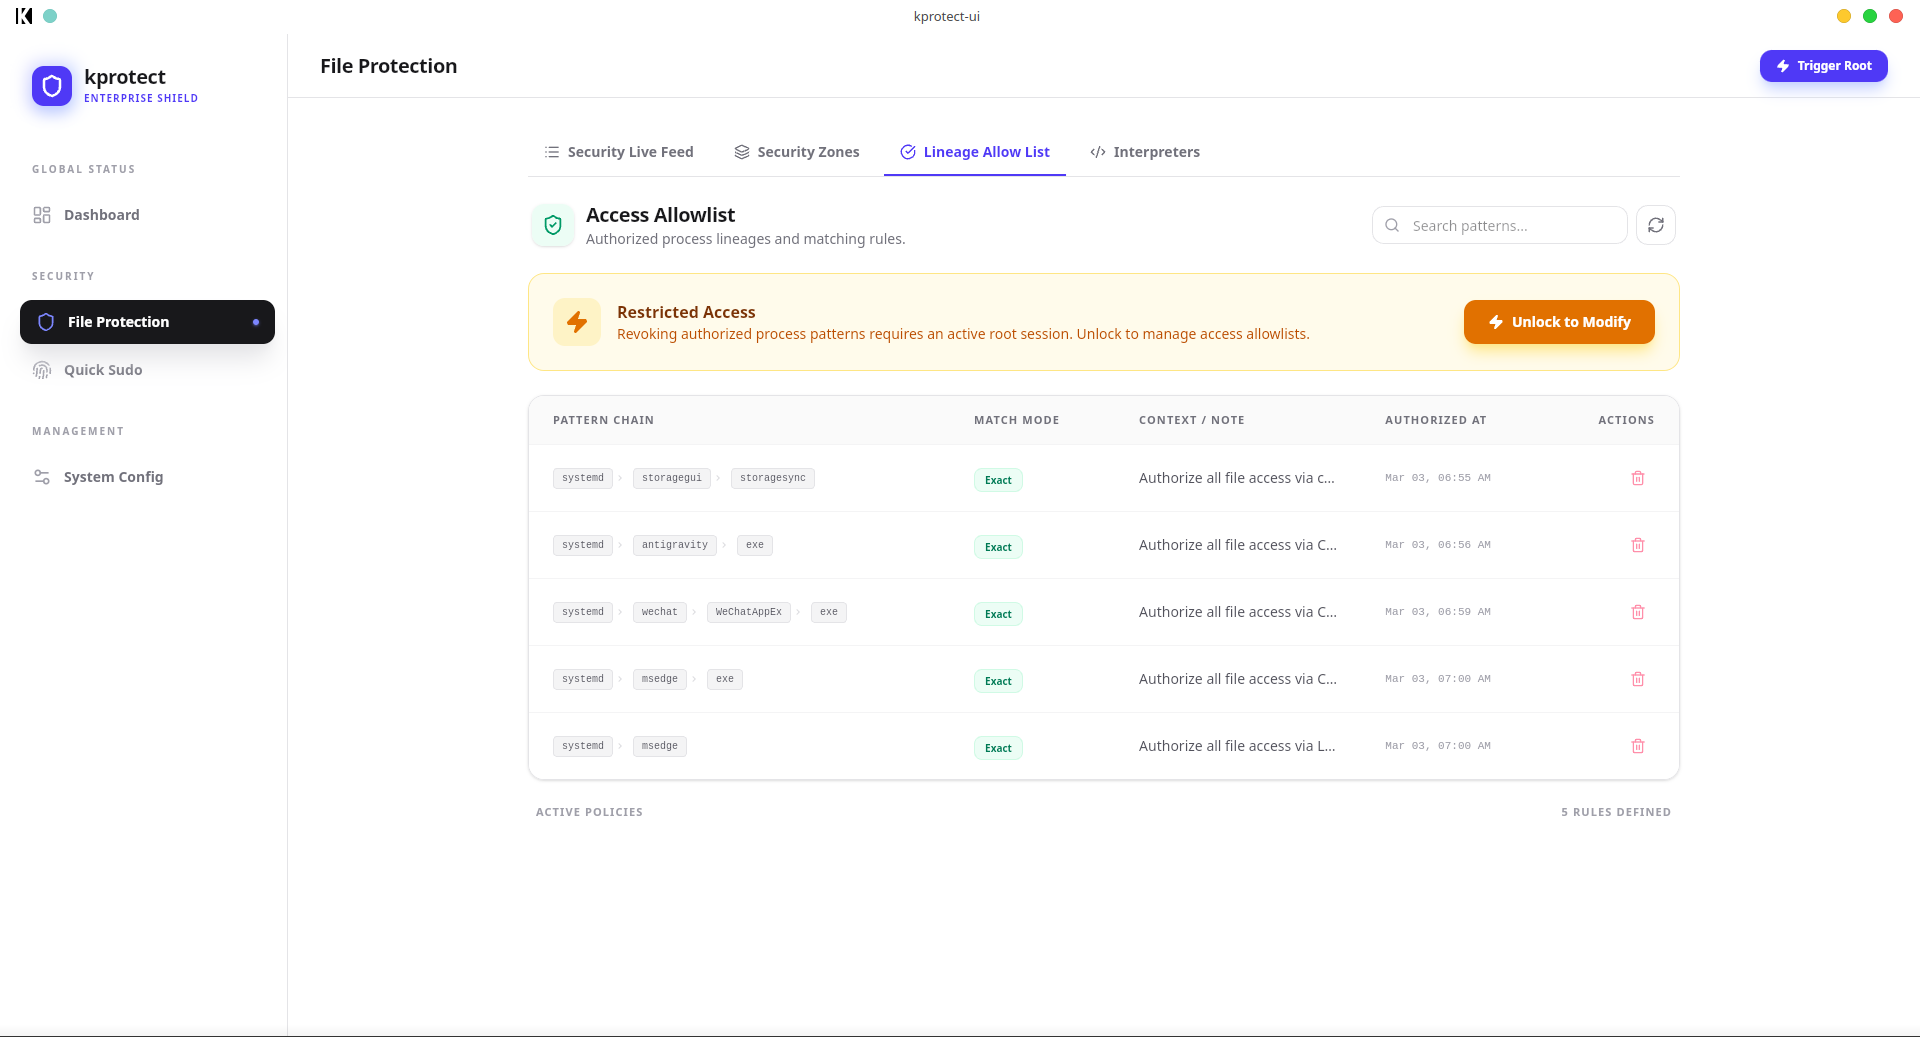 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
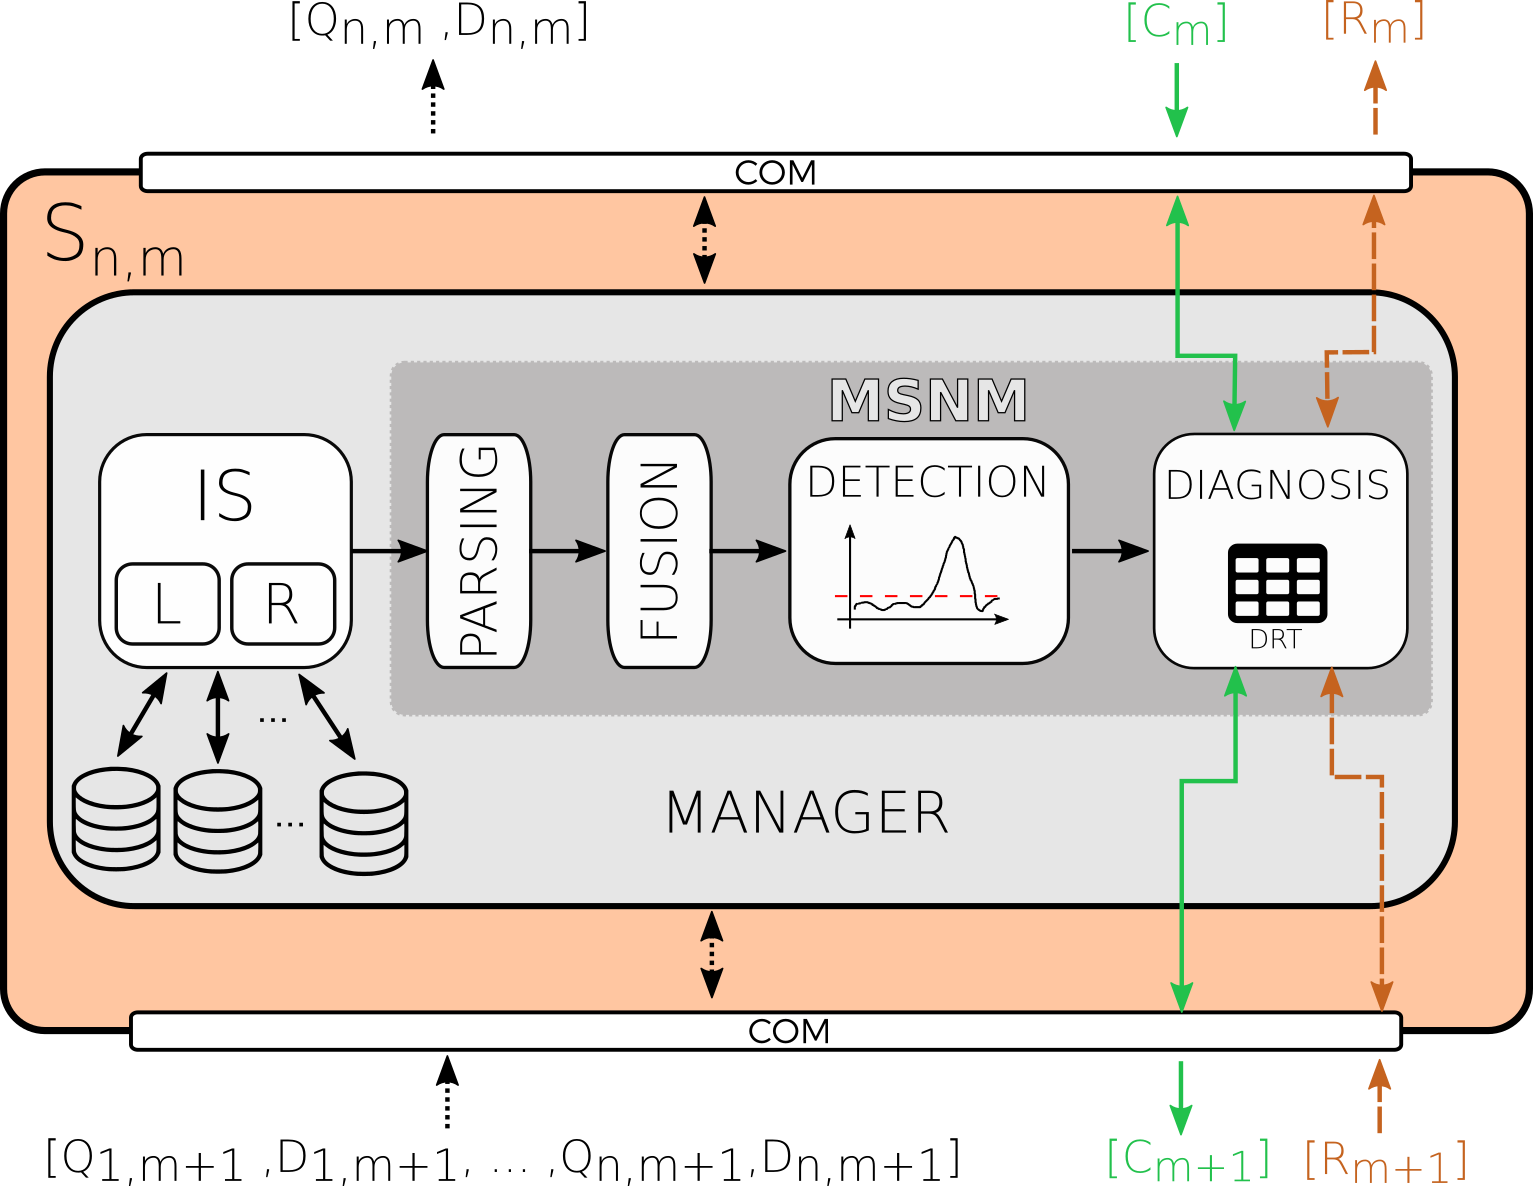 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques