

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.5k3 days ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
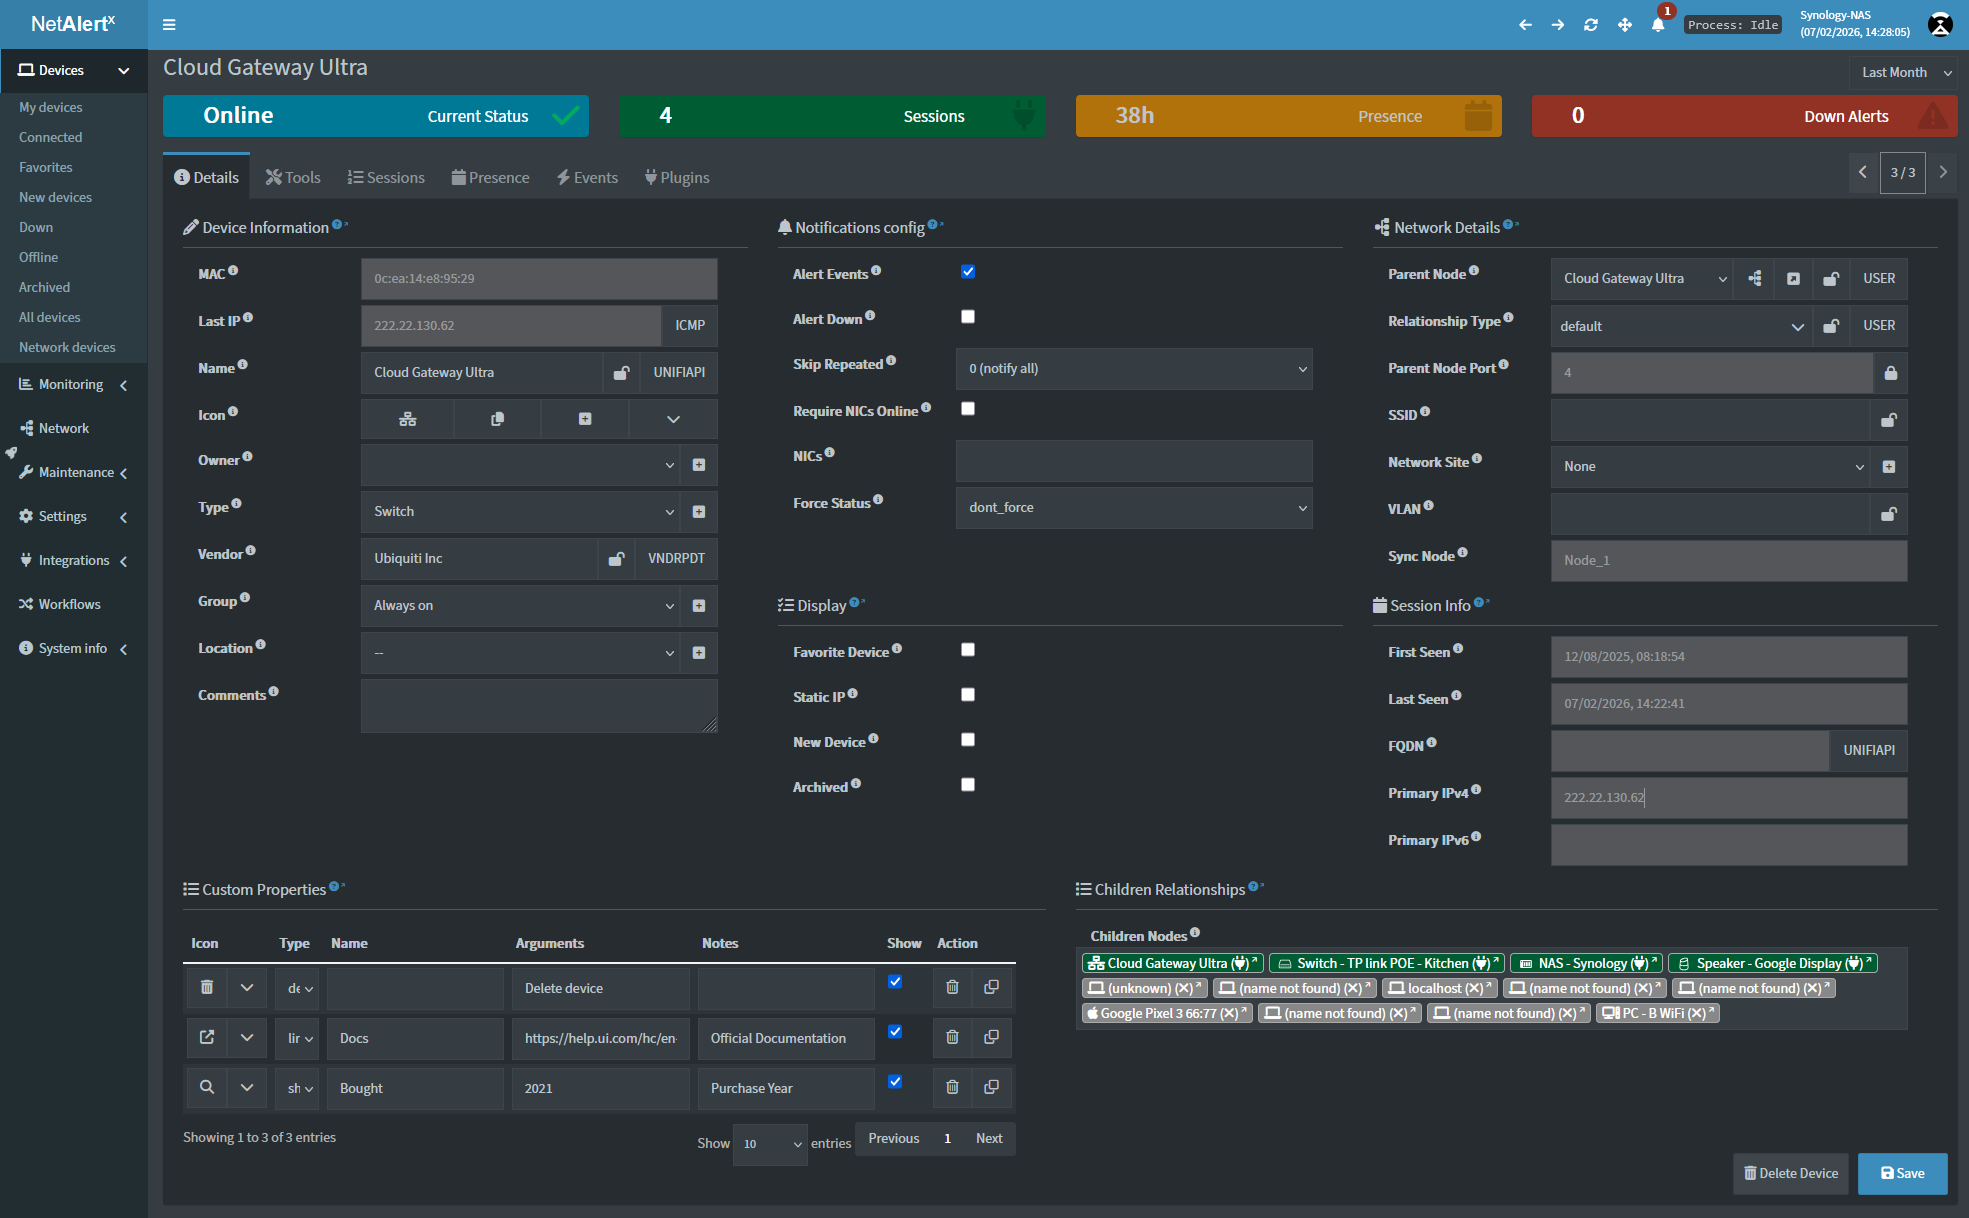 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
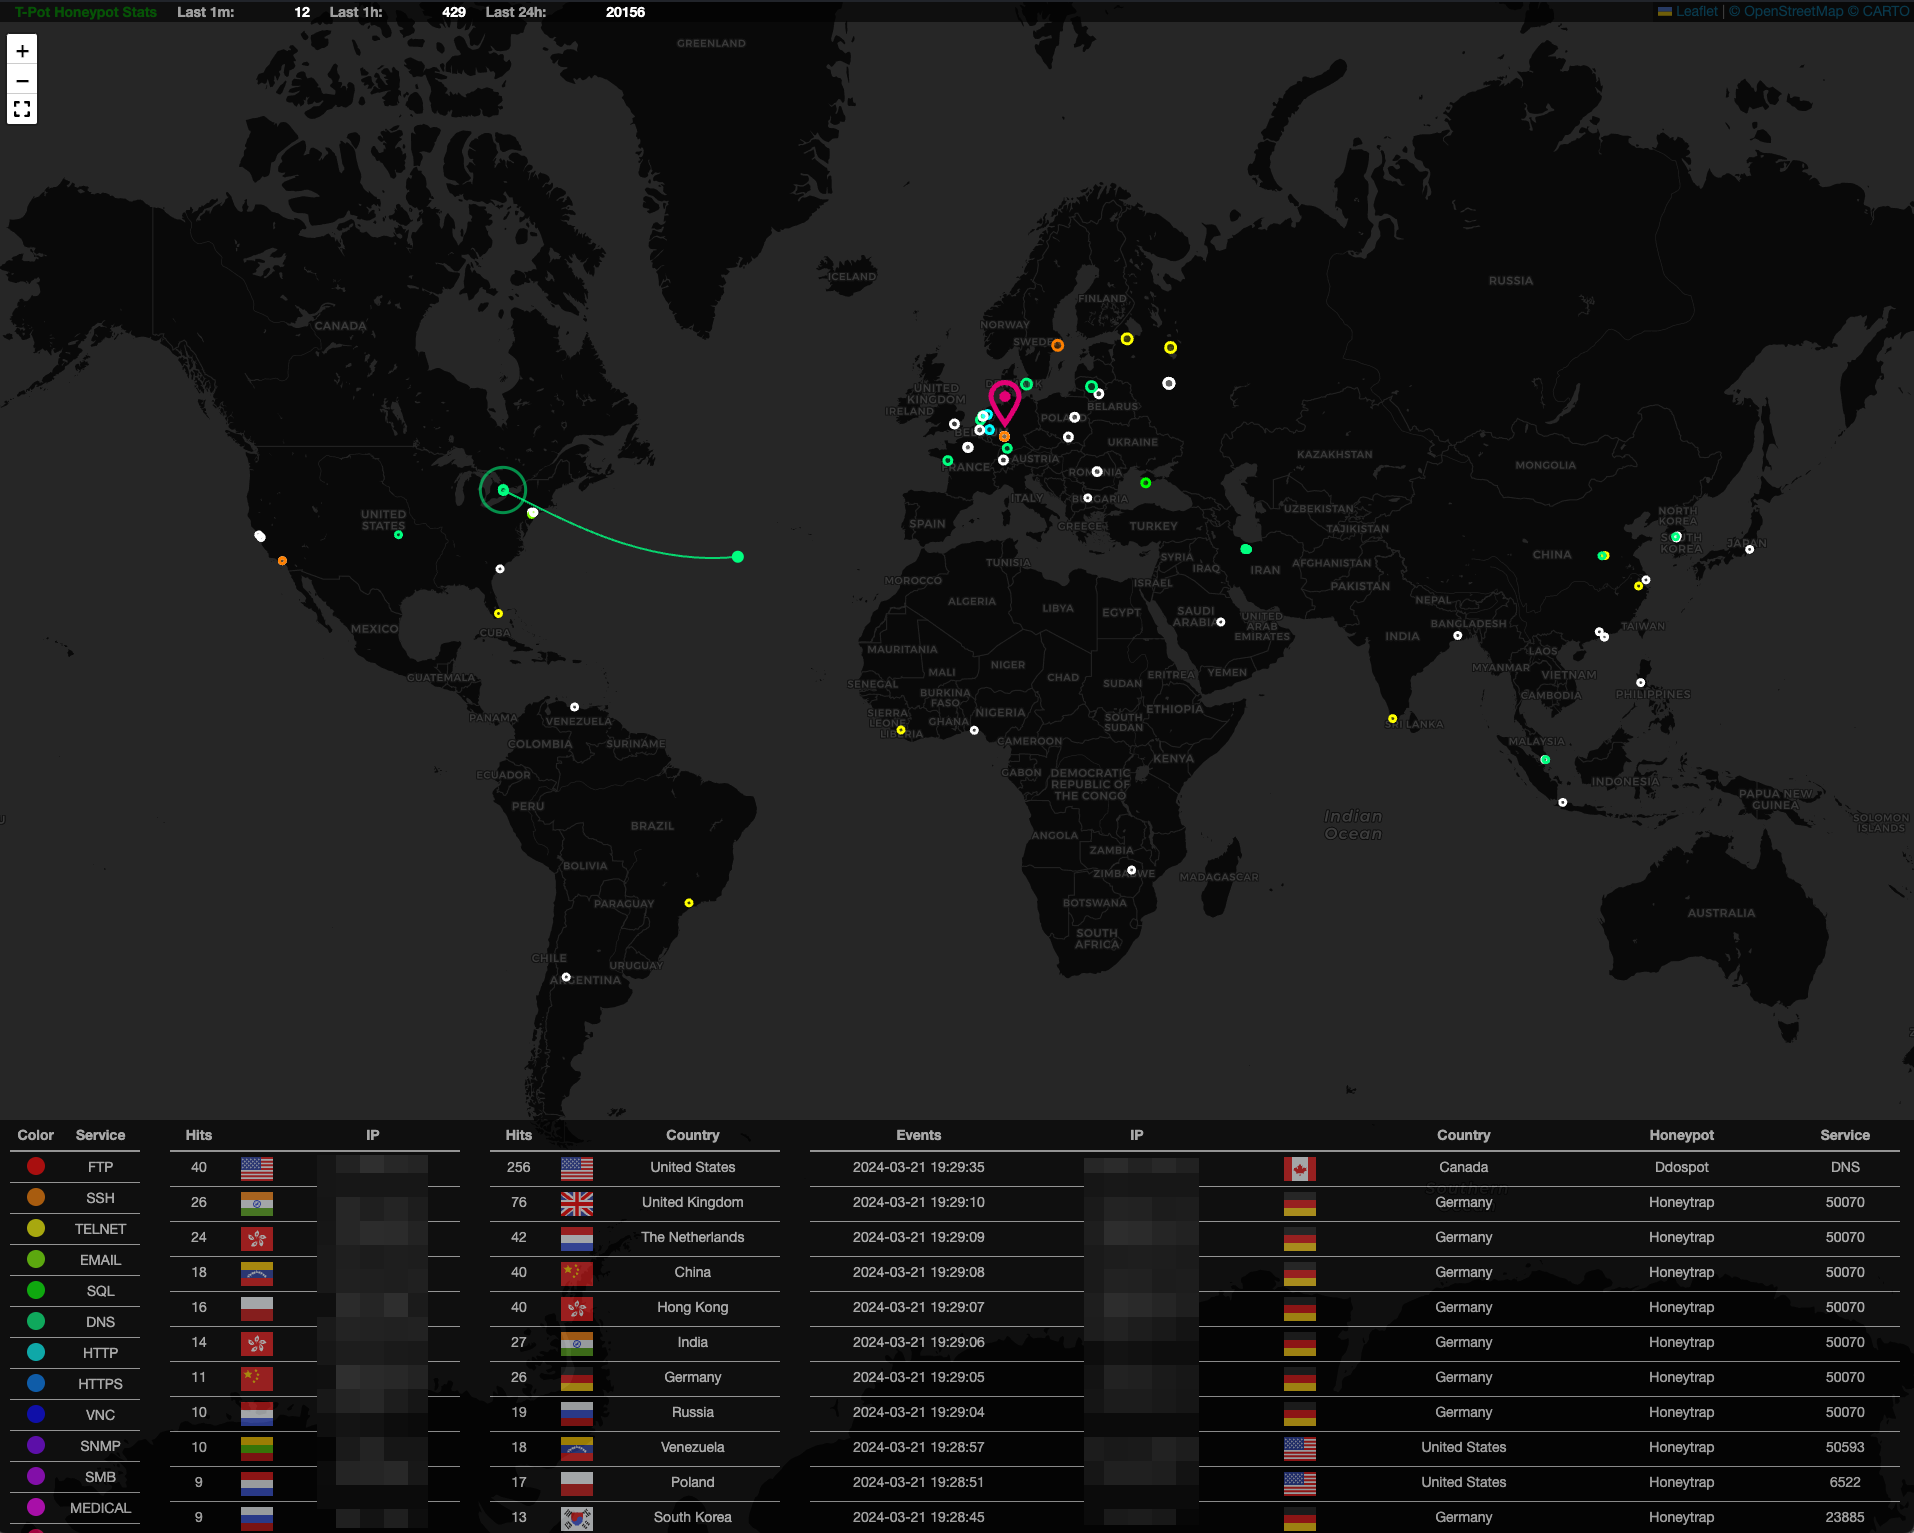 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝

 ndaal_open_source/ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
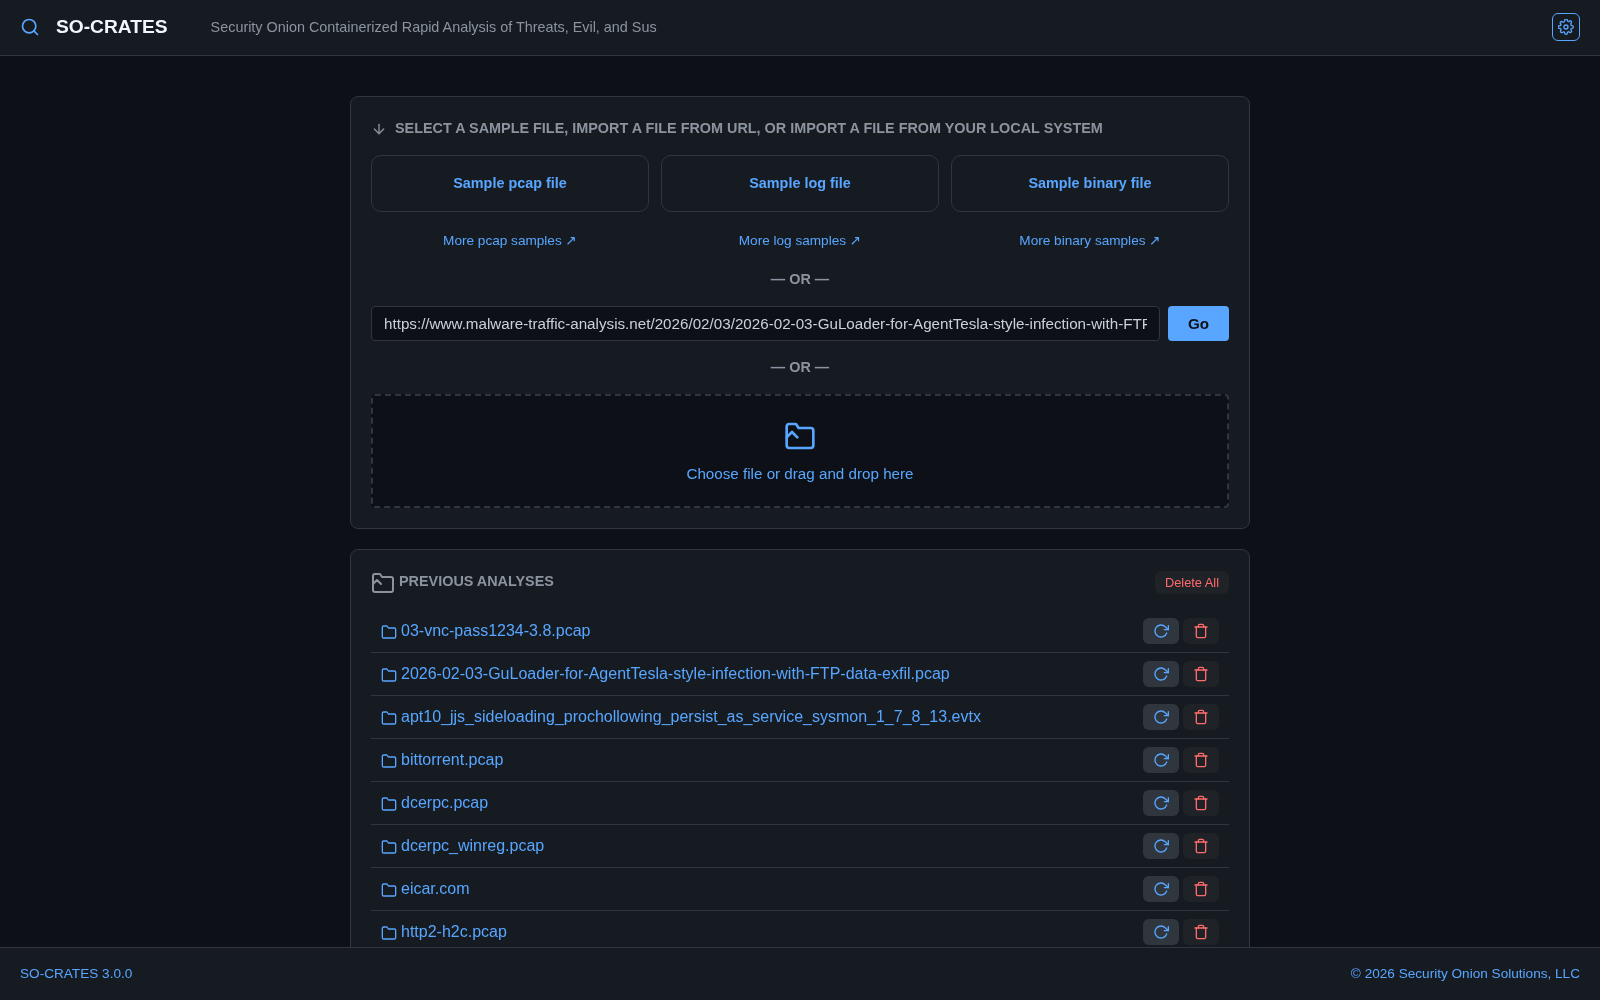 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.