
pockint
 edoardogerosa/pockint
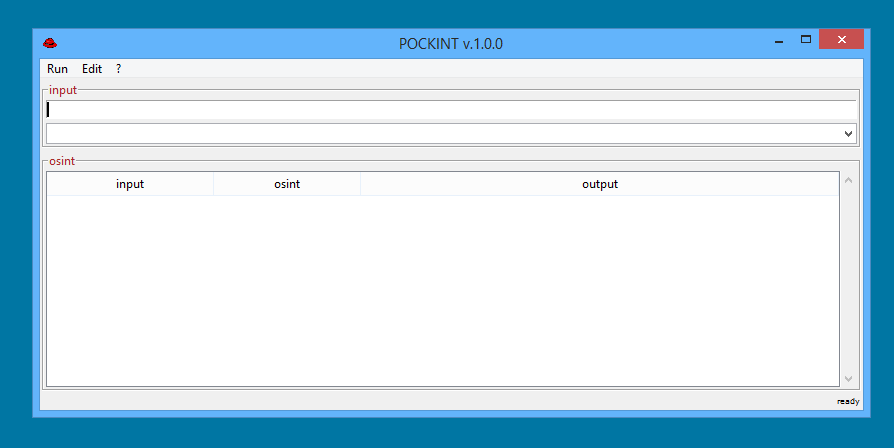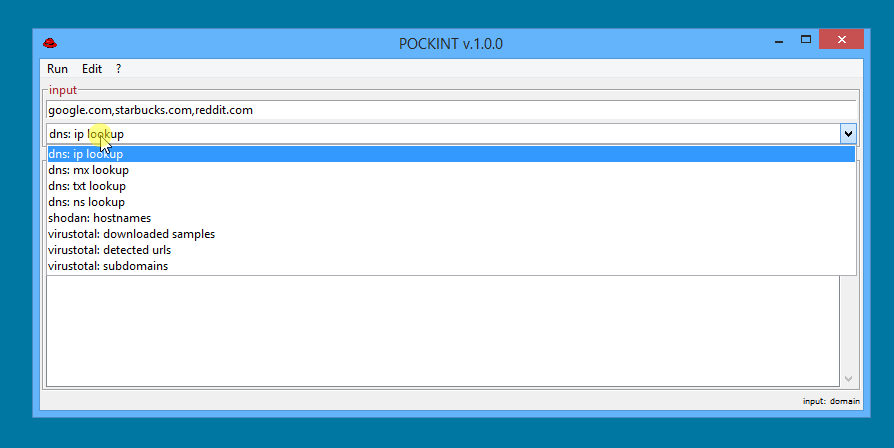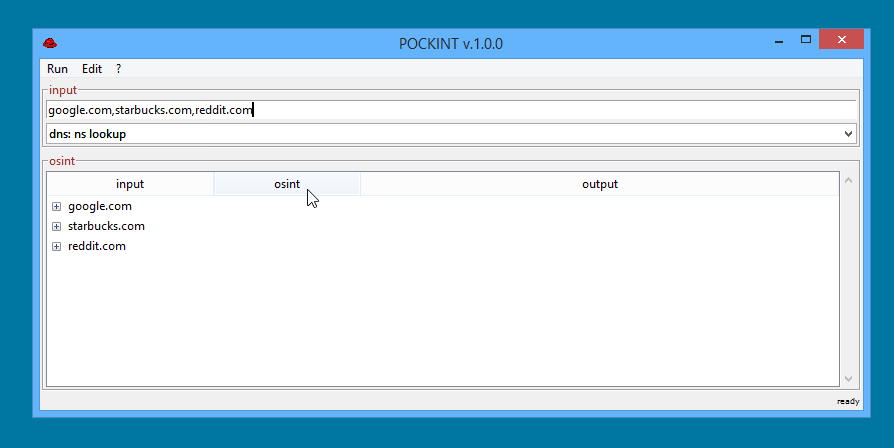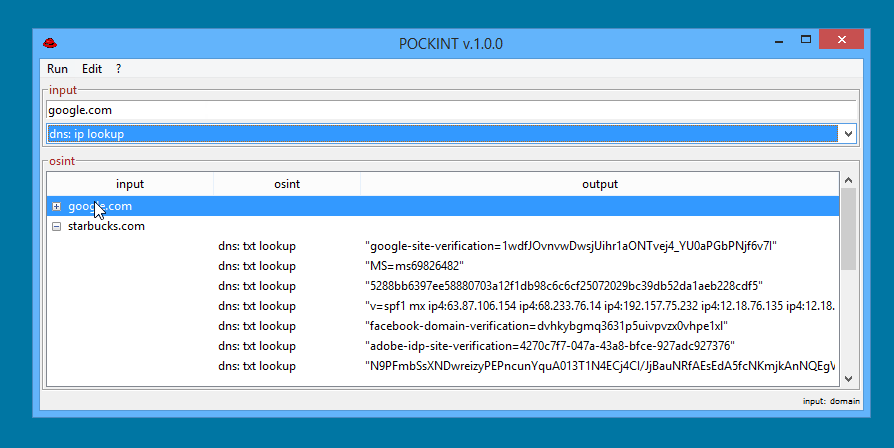
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
digital-forensicsdns-analysisincident-response+5
2843 years ago
edoardogerosa/pockintA portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 mandatoryprogrammer/xsshunter
The XSS Hunter service - a portable version of XSSHunter.com
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
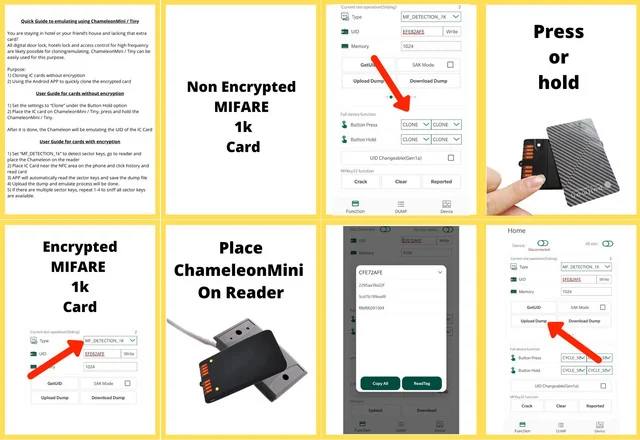 rfidresearchgroup/chameleonmini
Portable NFC/RFID security tool for emulating and cloning contactless smartcards, reading tags, sniffing RF traffic, and recovering Mifare access…
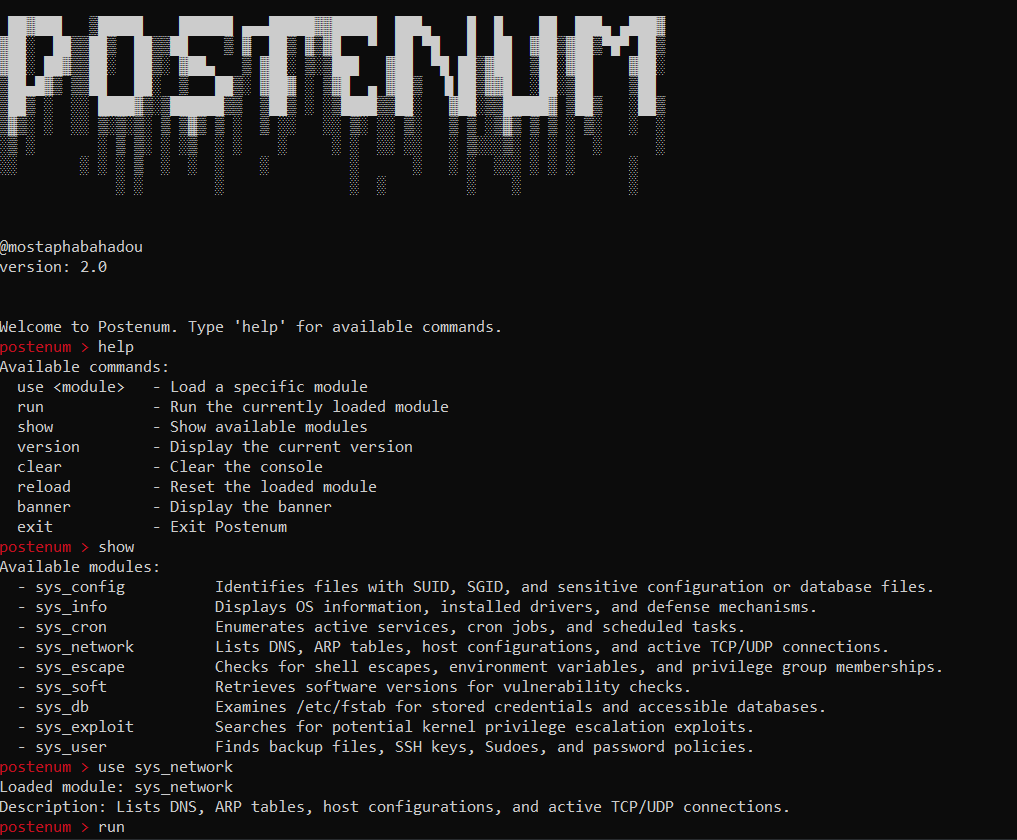 mostaphabahadou/postenum
A lightweight, portable, and modular tool for Linux enumeration and privilege escalation.

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 lsecqt/sessionview
A portable C# utility for enumerating local and remote windows sessions
 brucedevices/firmware
Predatory ESP32 Firmware
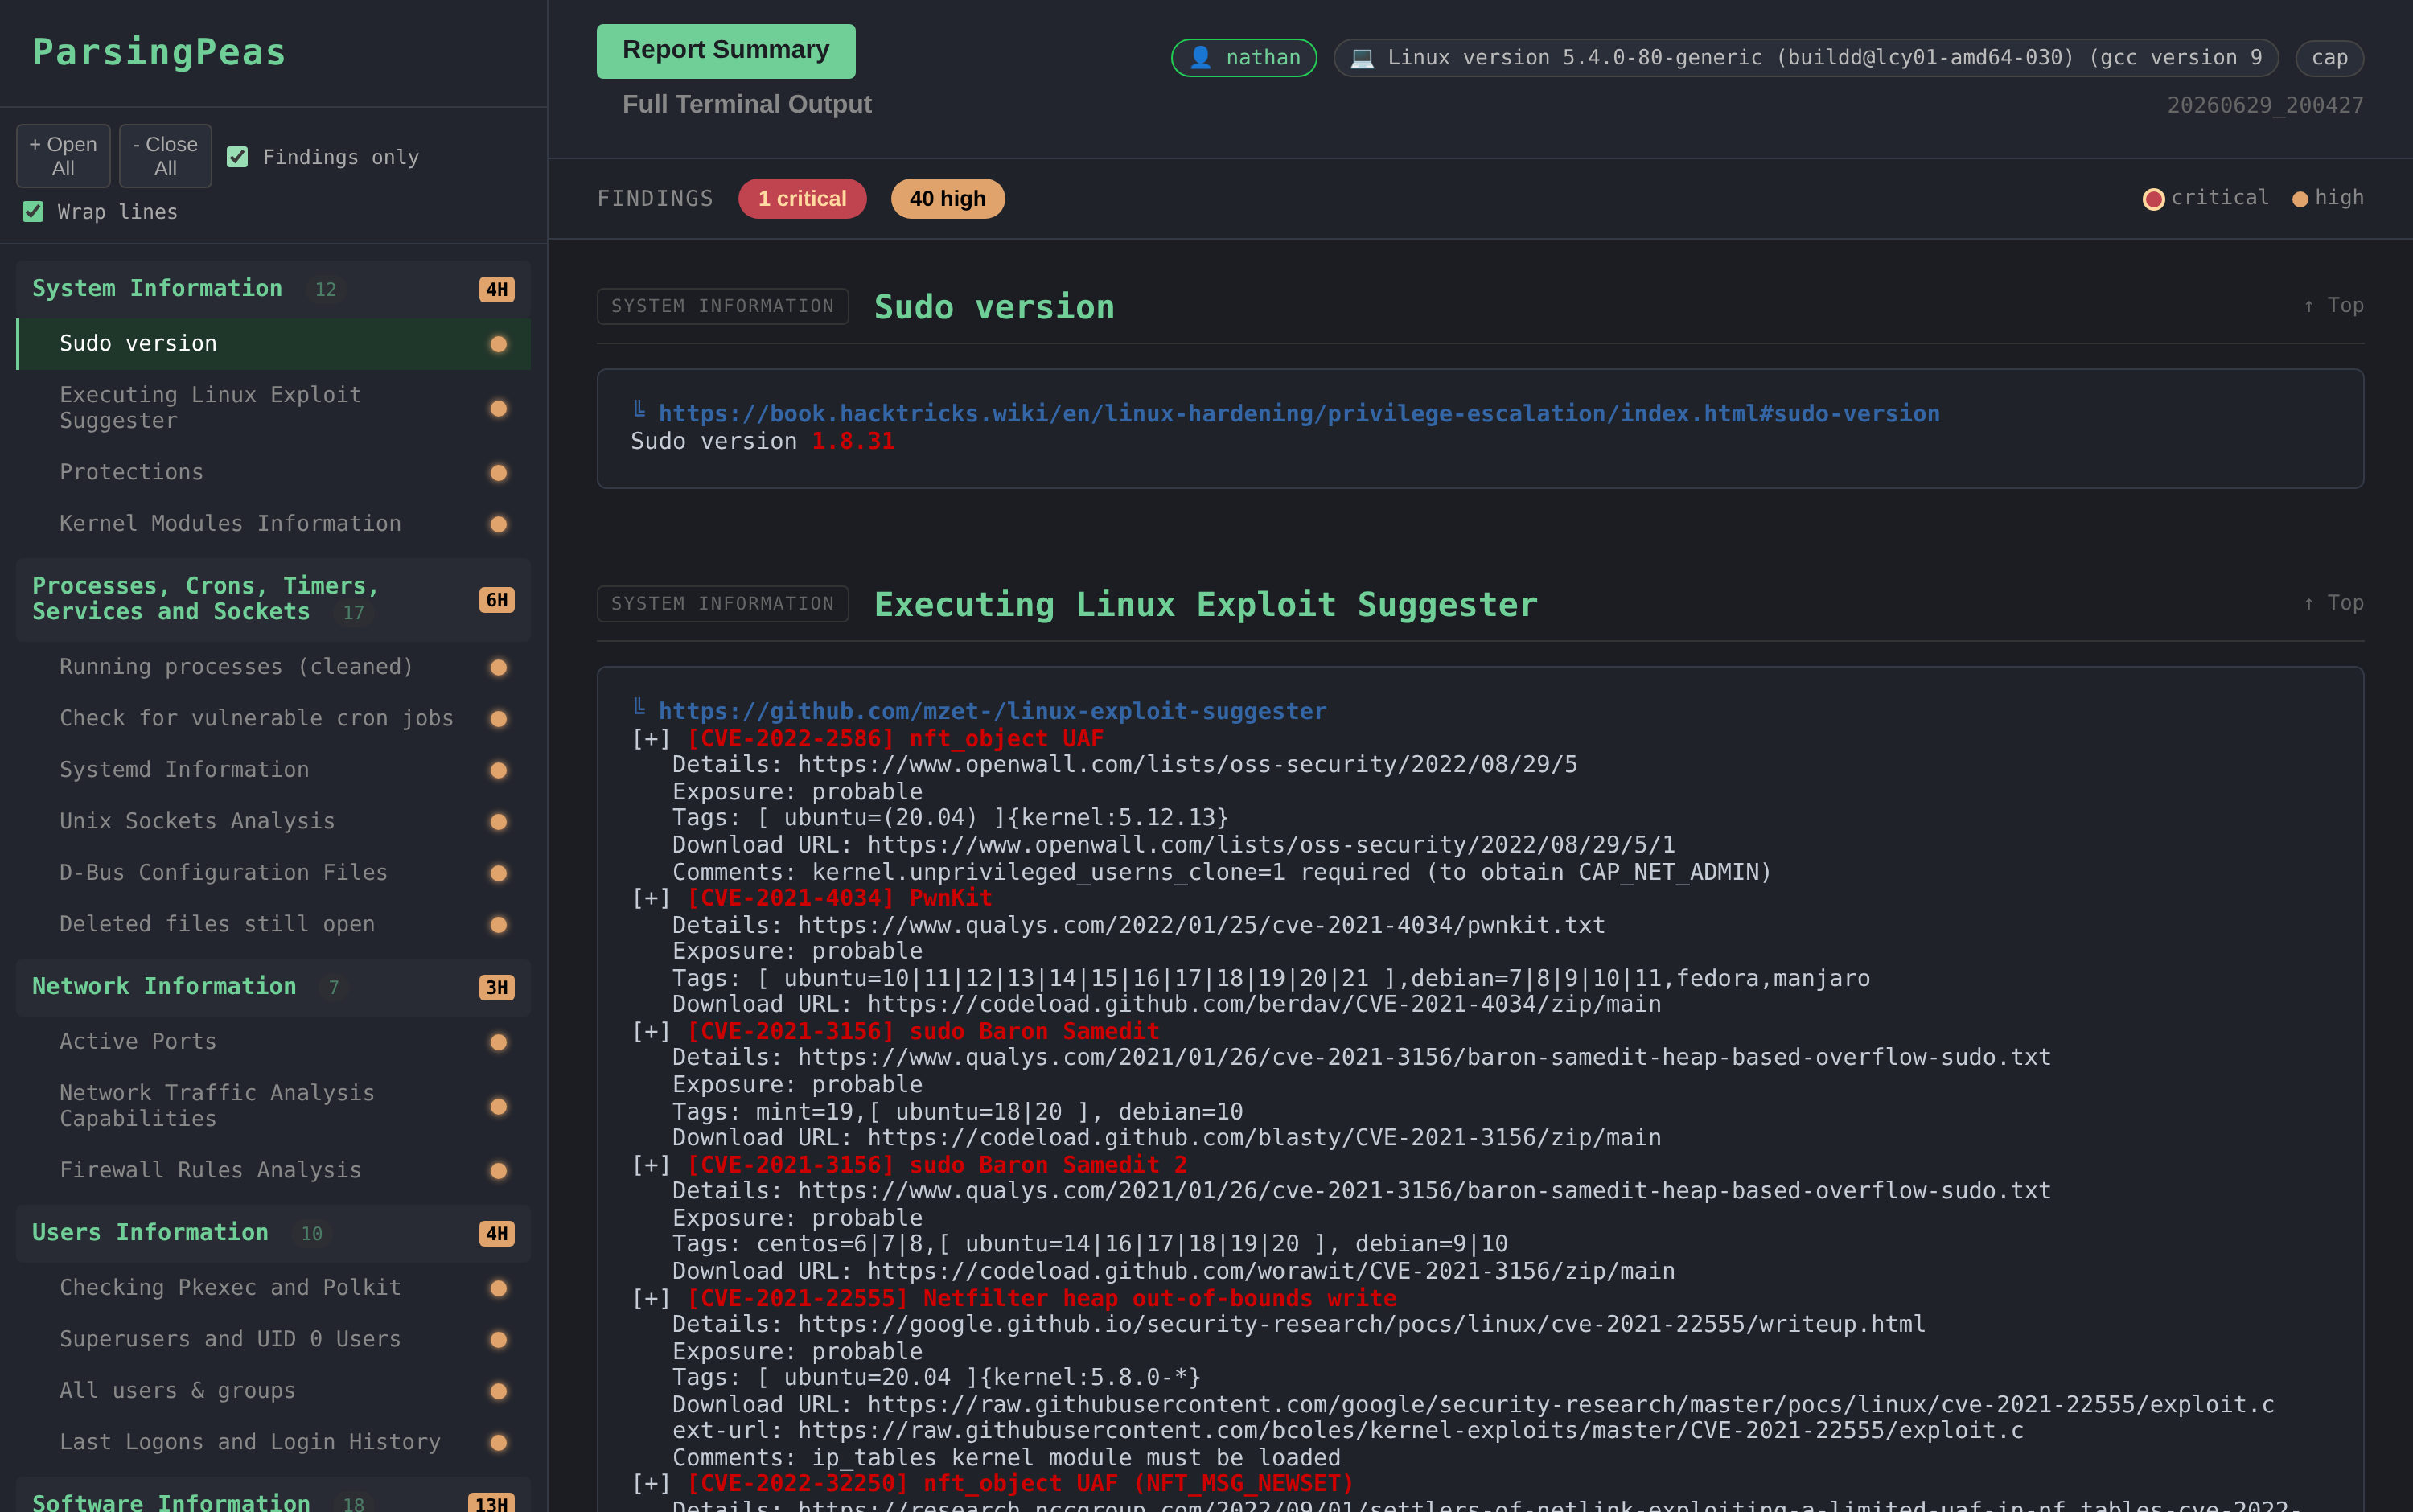 yuvalmil/parsingpeas
HTML parser for PEAS output with additional features
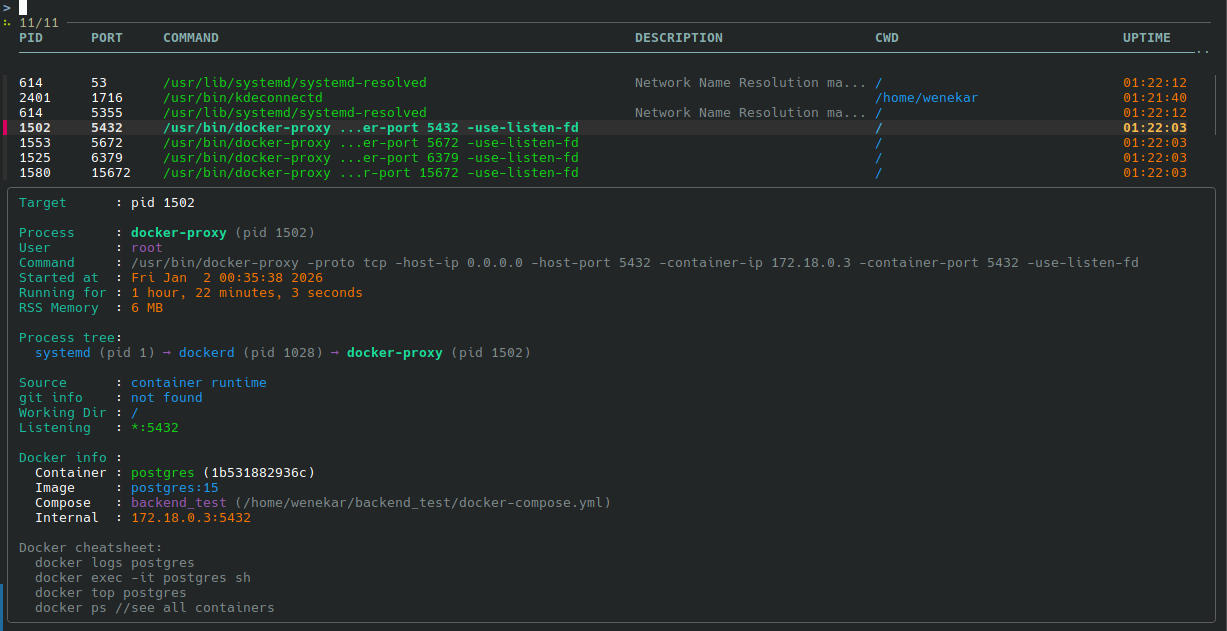 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 34zy/nerv0usr4bbit
Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool