

waf-checker
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
api-security-testingids-ips-evasioninformation-gathering+6
38
sech0us3/waf-checkerAutomated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
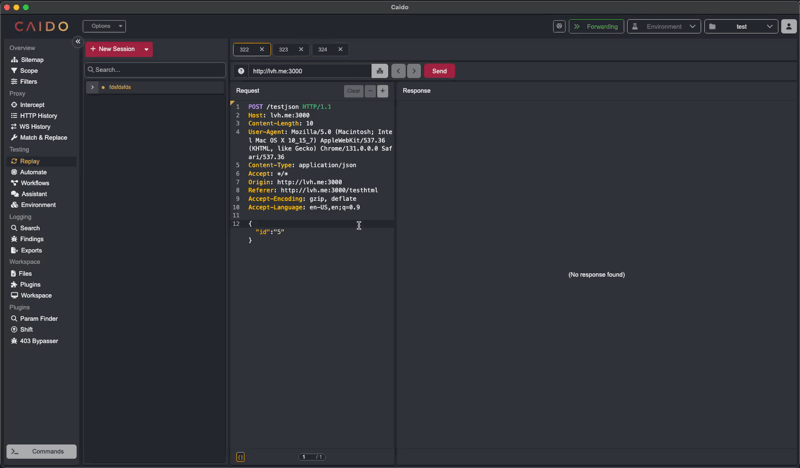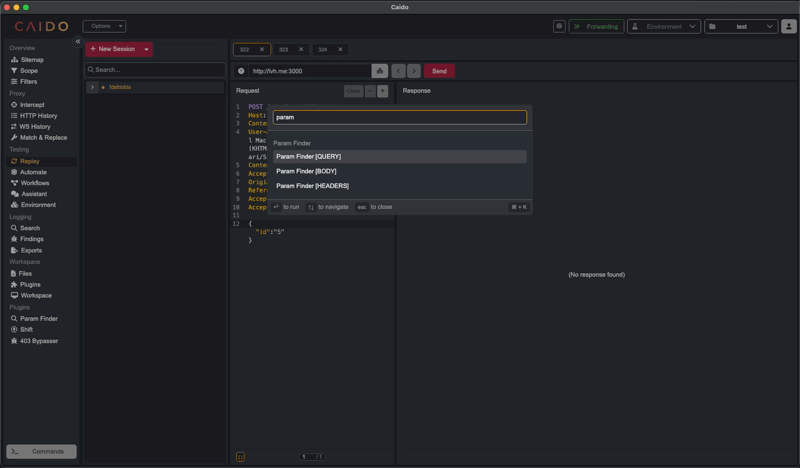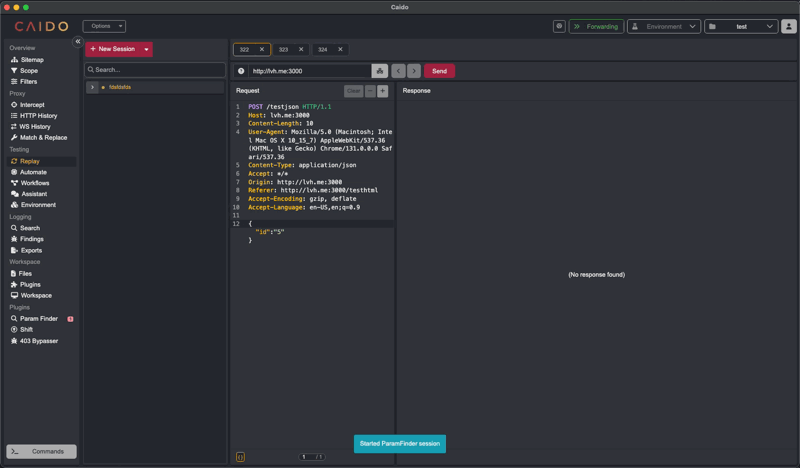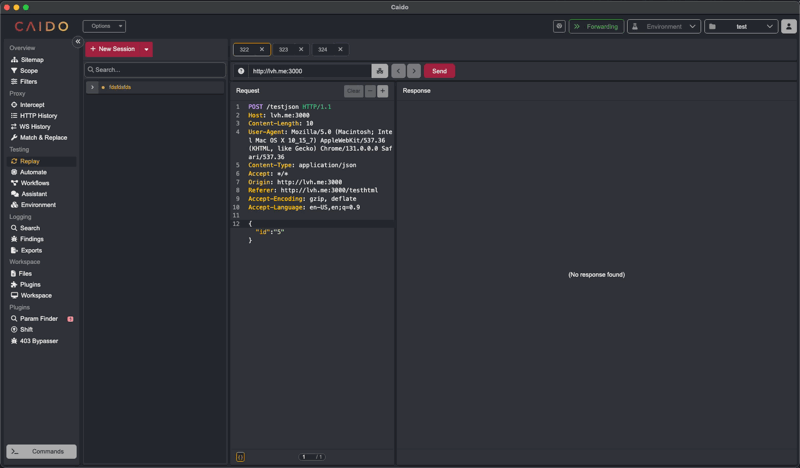 caido-community/paramfinder
Discover hidden parameters in Caido
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
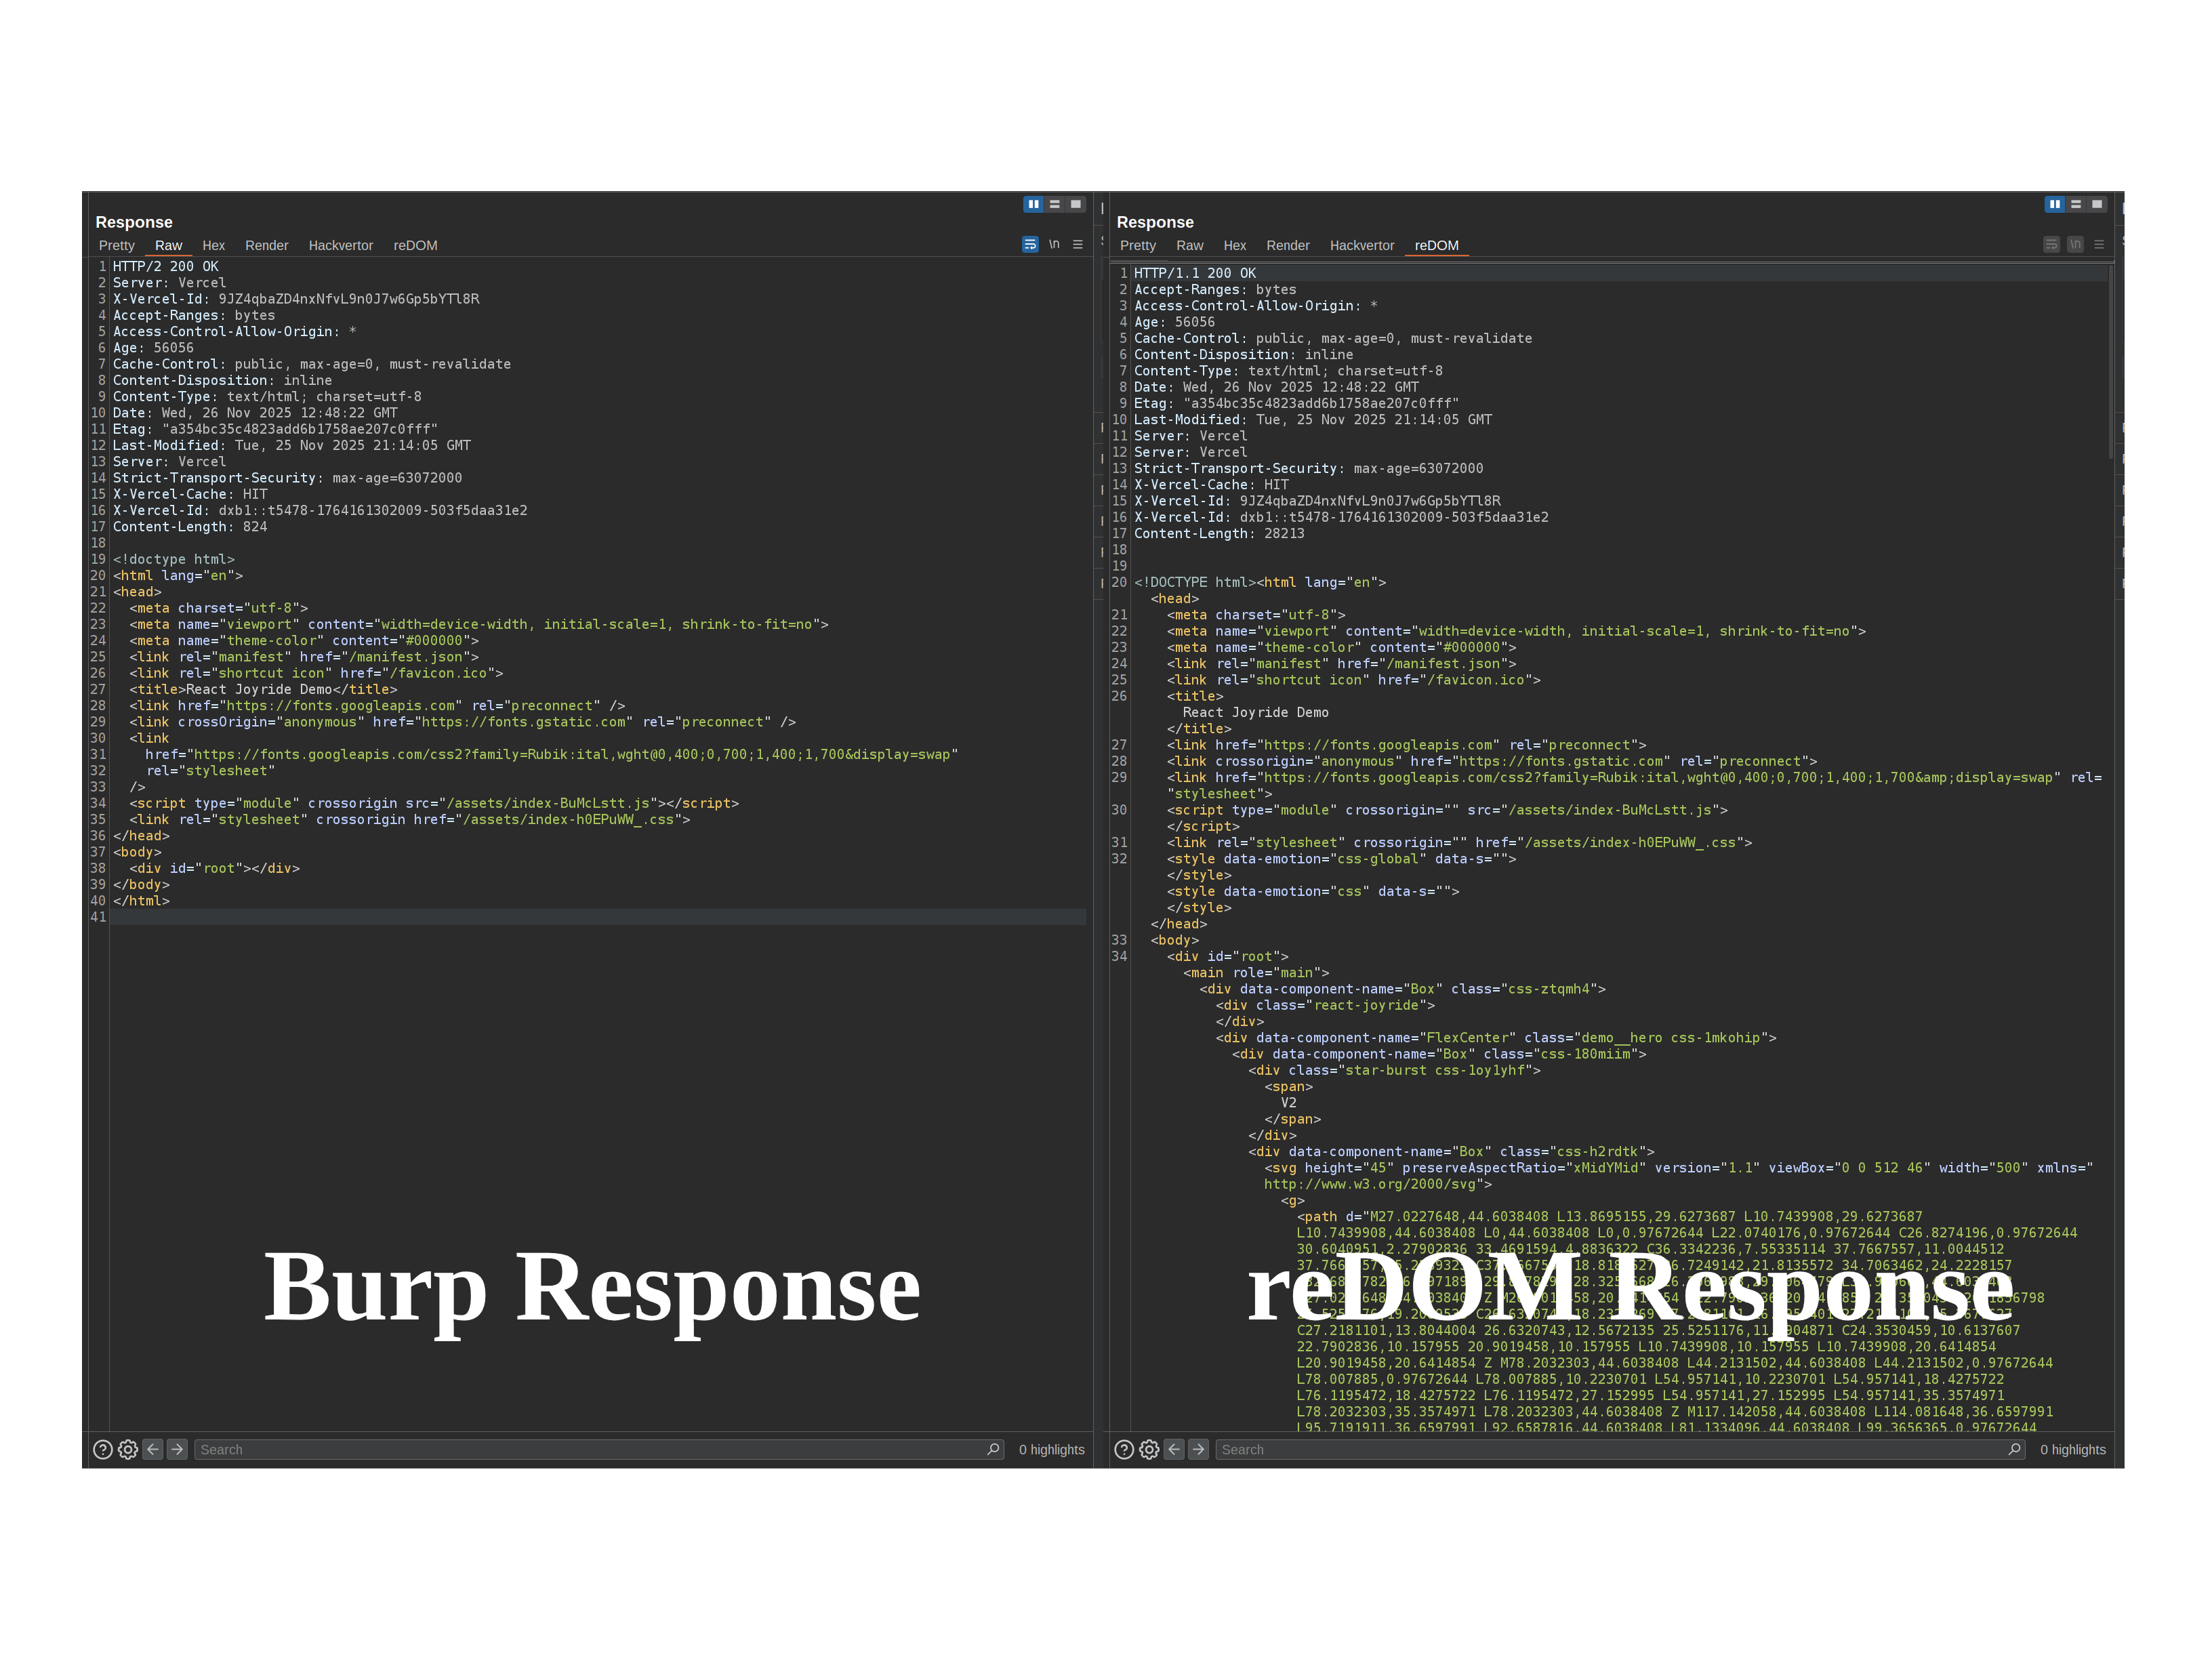 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
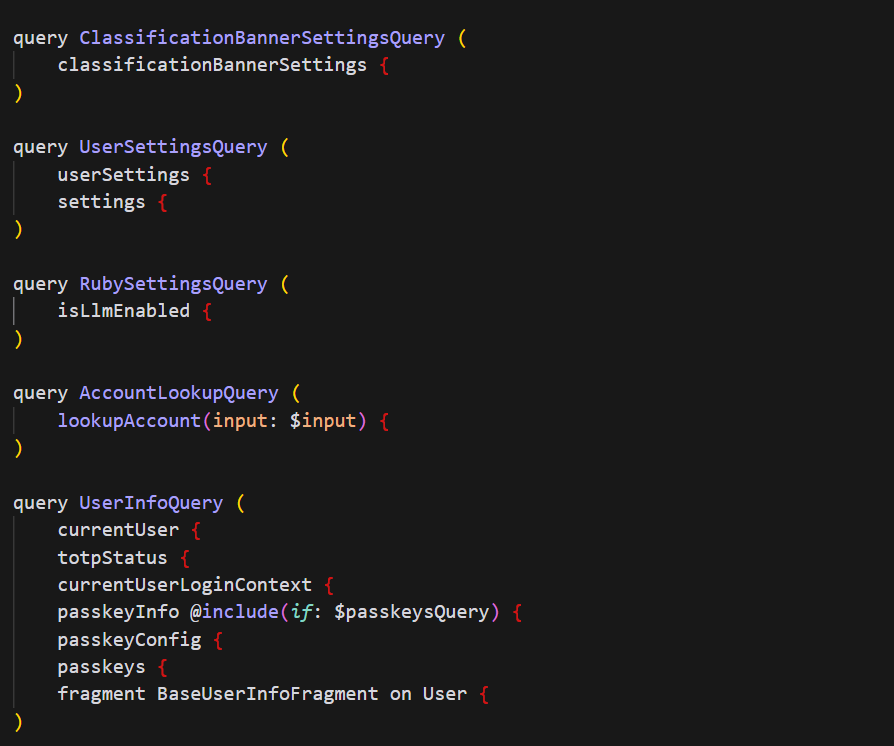 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
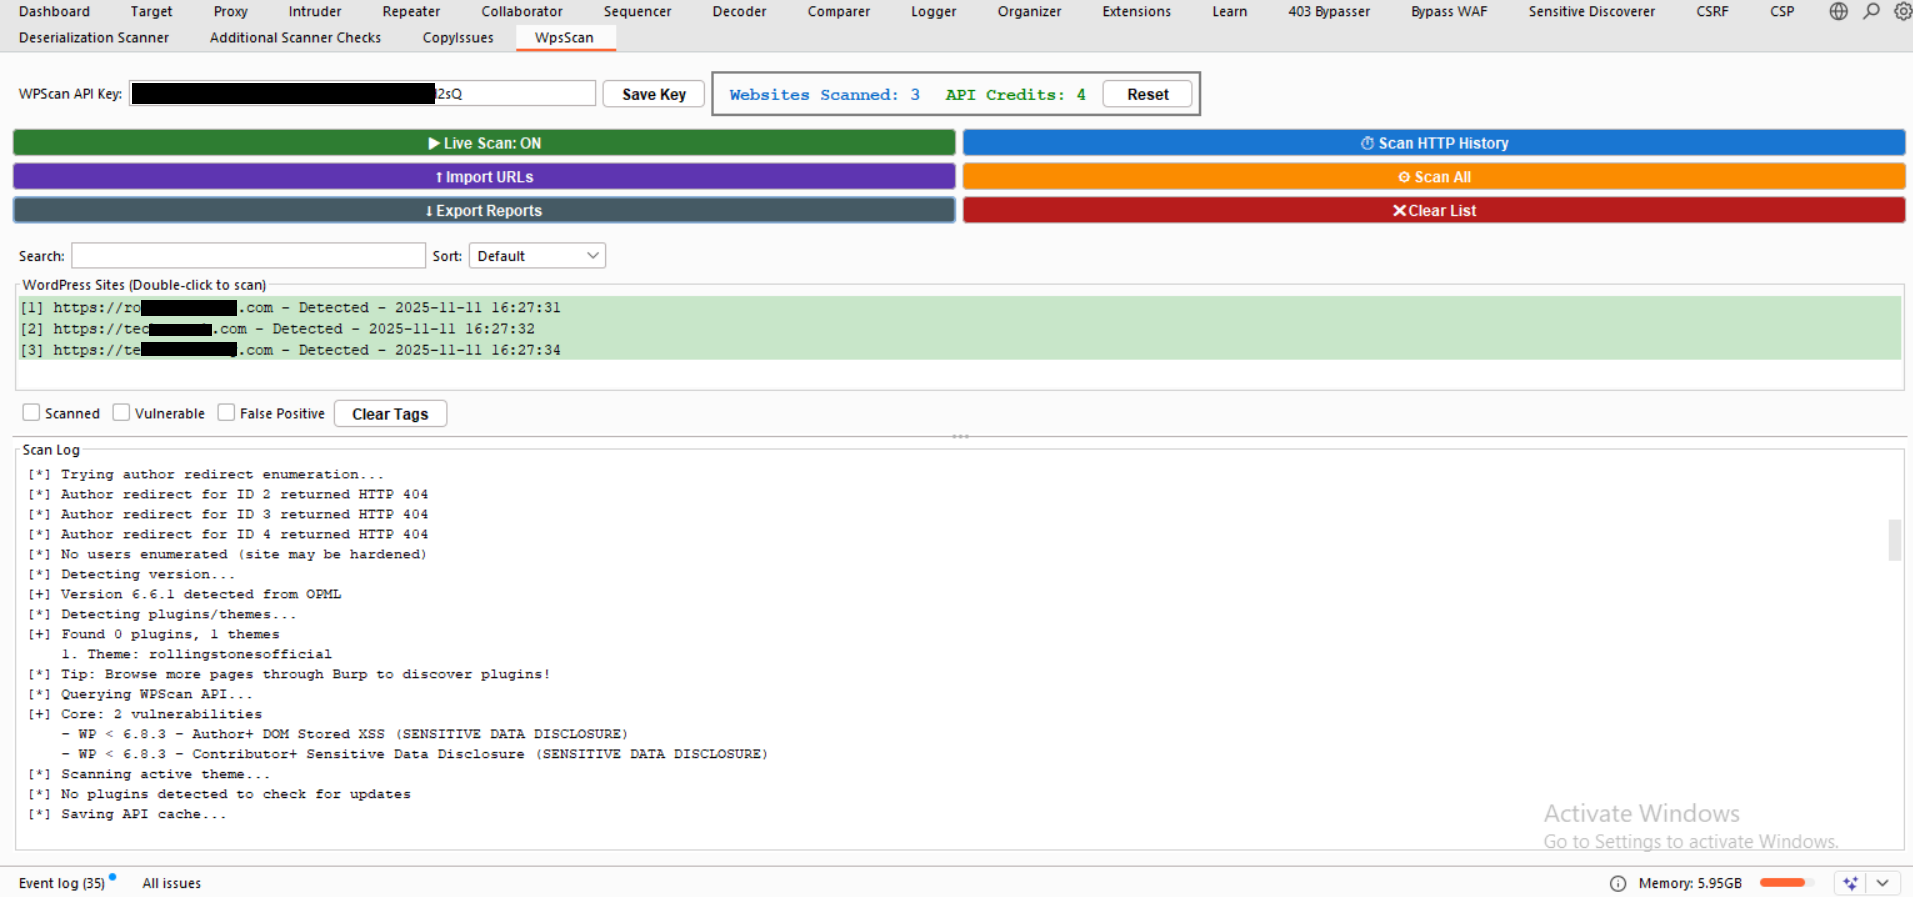 teycir/burpwpsscan
Burp extension for wordpress security scanning
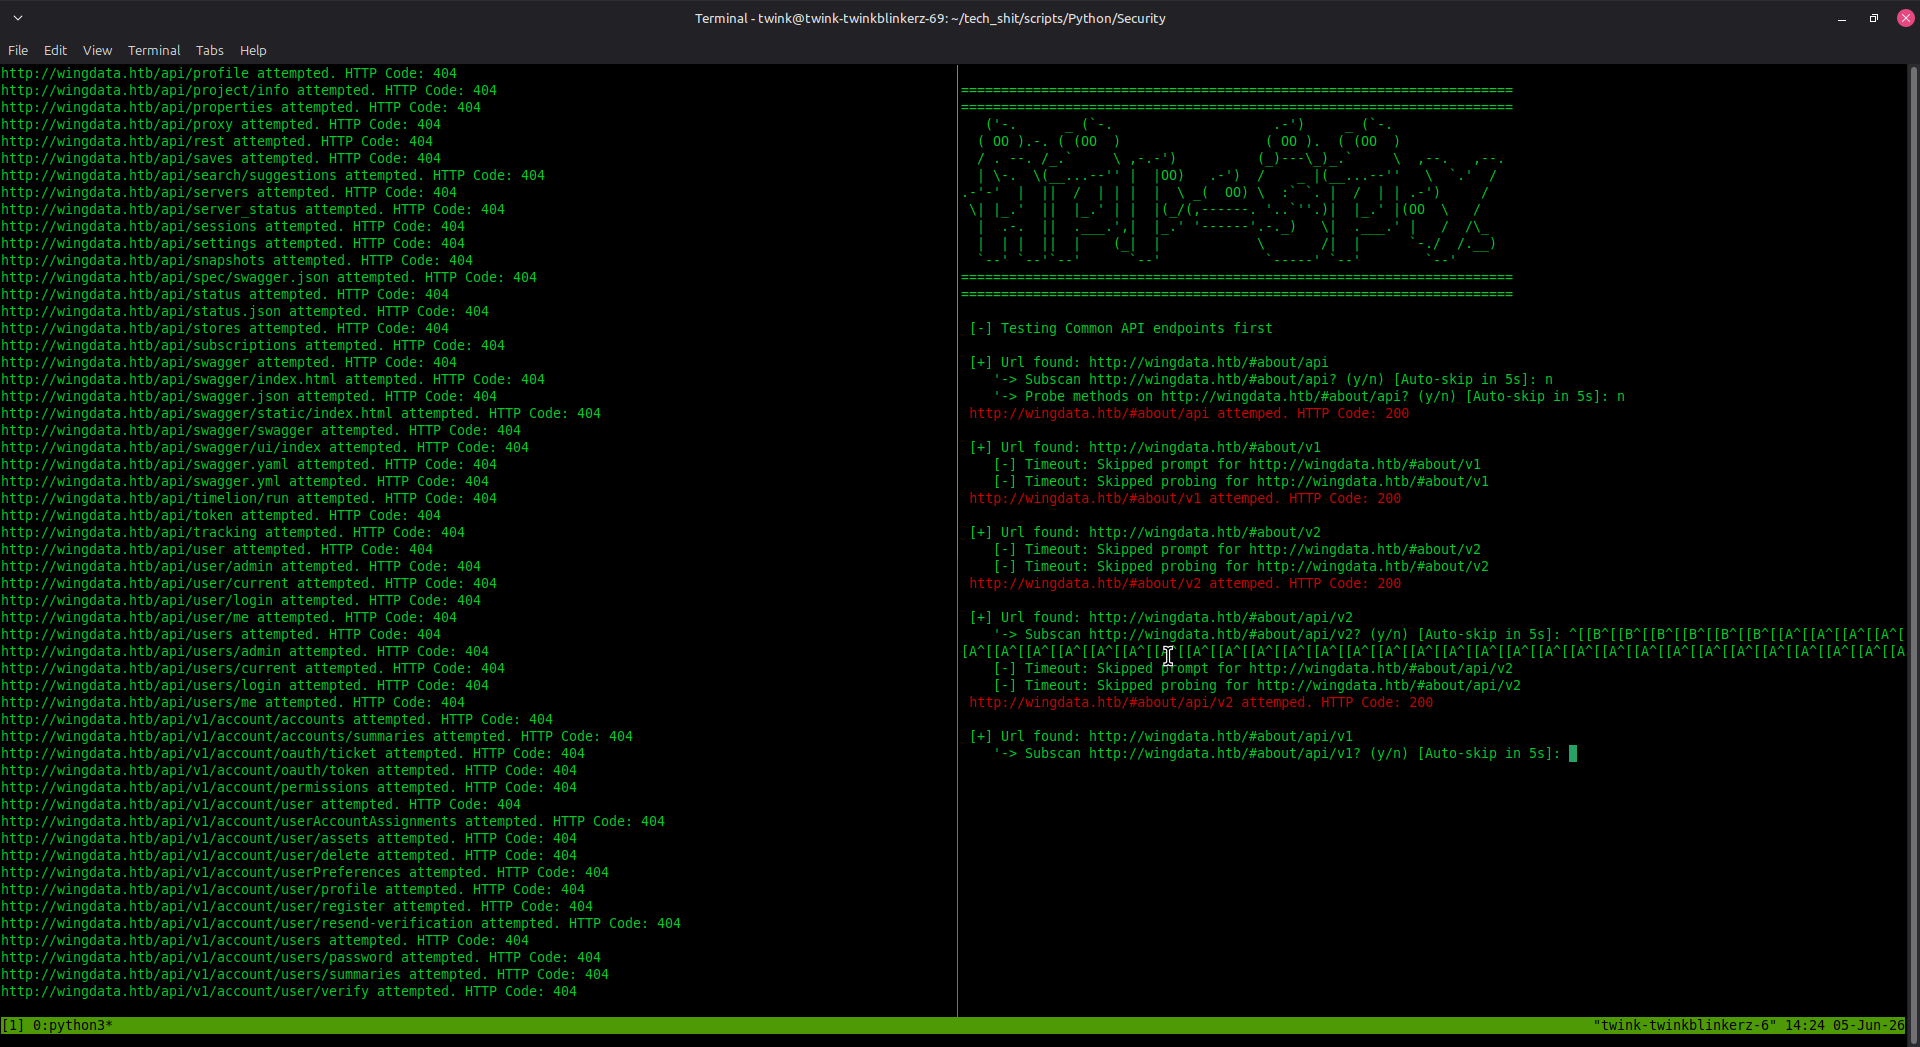 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 abraxas/moodle-grades-gradeitems
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_gradeitems lists hidden grade items
 c1ph3rx13/cve-2023-42442
CVE-2023-42442 JumpServer Session 录像任意下载漏洞
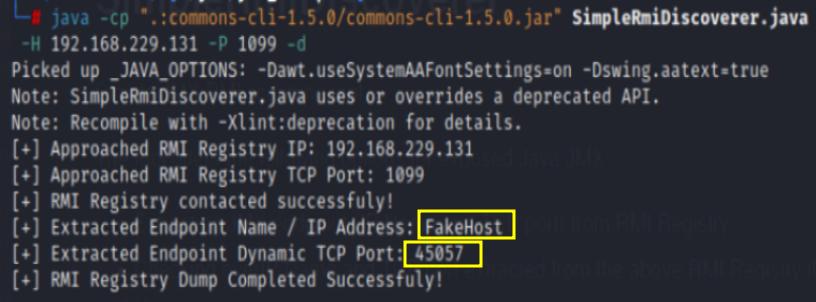 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 null200ok/cve-2026-27944
CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption