
Nest
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
api-securitycurated-resourceseducation+2
owasp/nestYour gateway to OWASP. Discover, engage, and help shape the future!
 abraxas/moodle-grades-gradeitems
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_gradeitems lists hidden grade items
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 owasp/www-community
OWASP Community Pages are a place where OWASP can accept community contributions for security-related content.
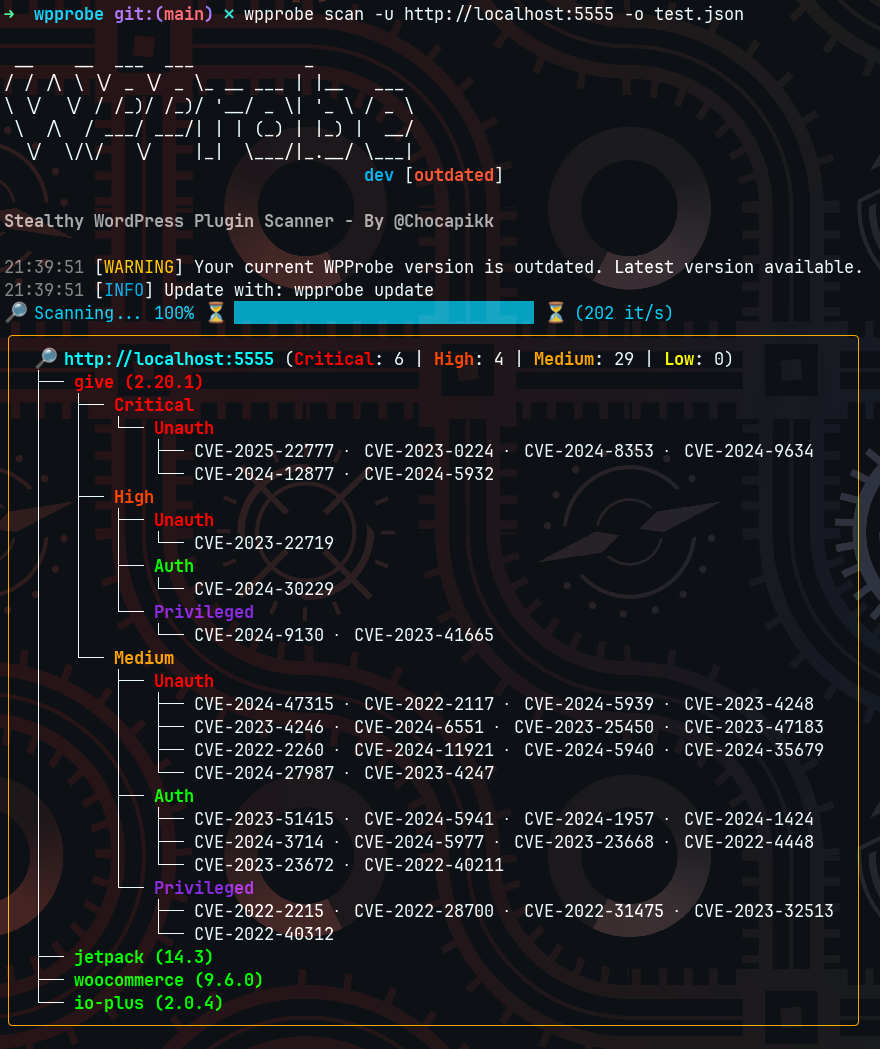 chocapikk/wpprobe
A fast WordPress plugin enumeration tool
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 owasp/decodebox
Client-side workbench that auto-detects, recursively decodes, and analyses unknown or layered data, extracting indicators and CWE-tagged security…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
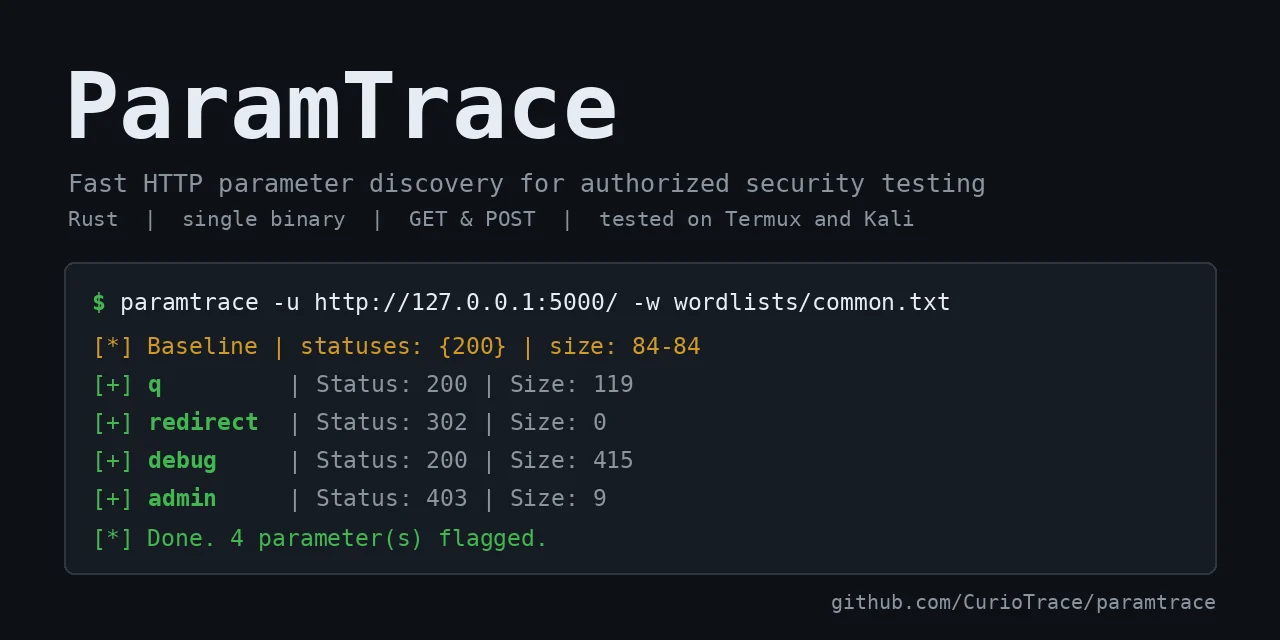 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).