

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 amibhai/spoofed
A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…
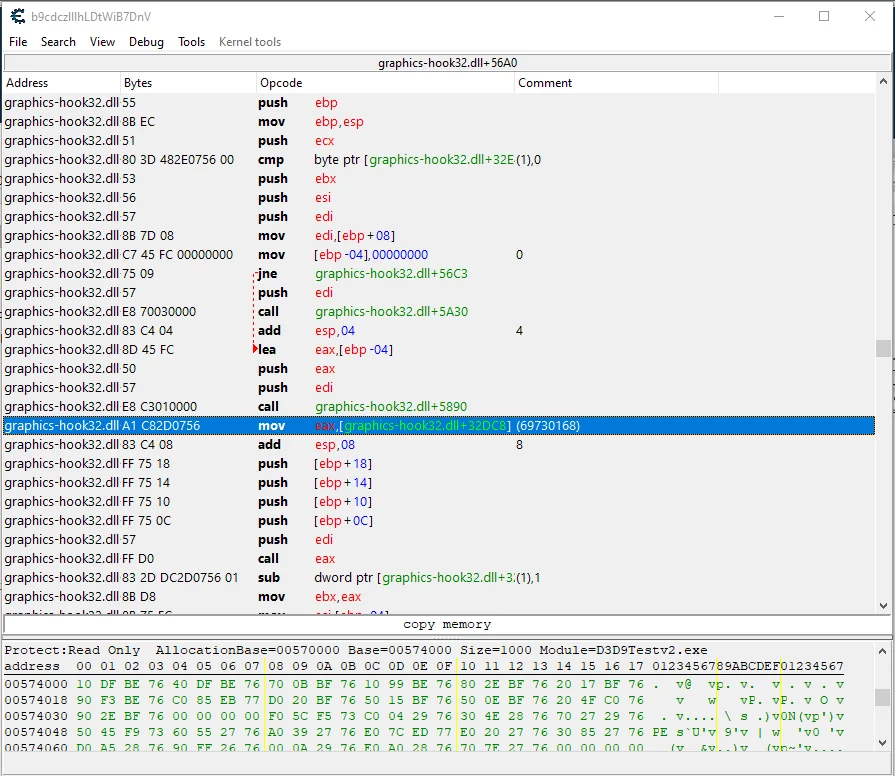 gmh5225/obs-graphics-hook32-hook
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
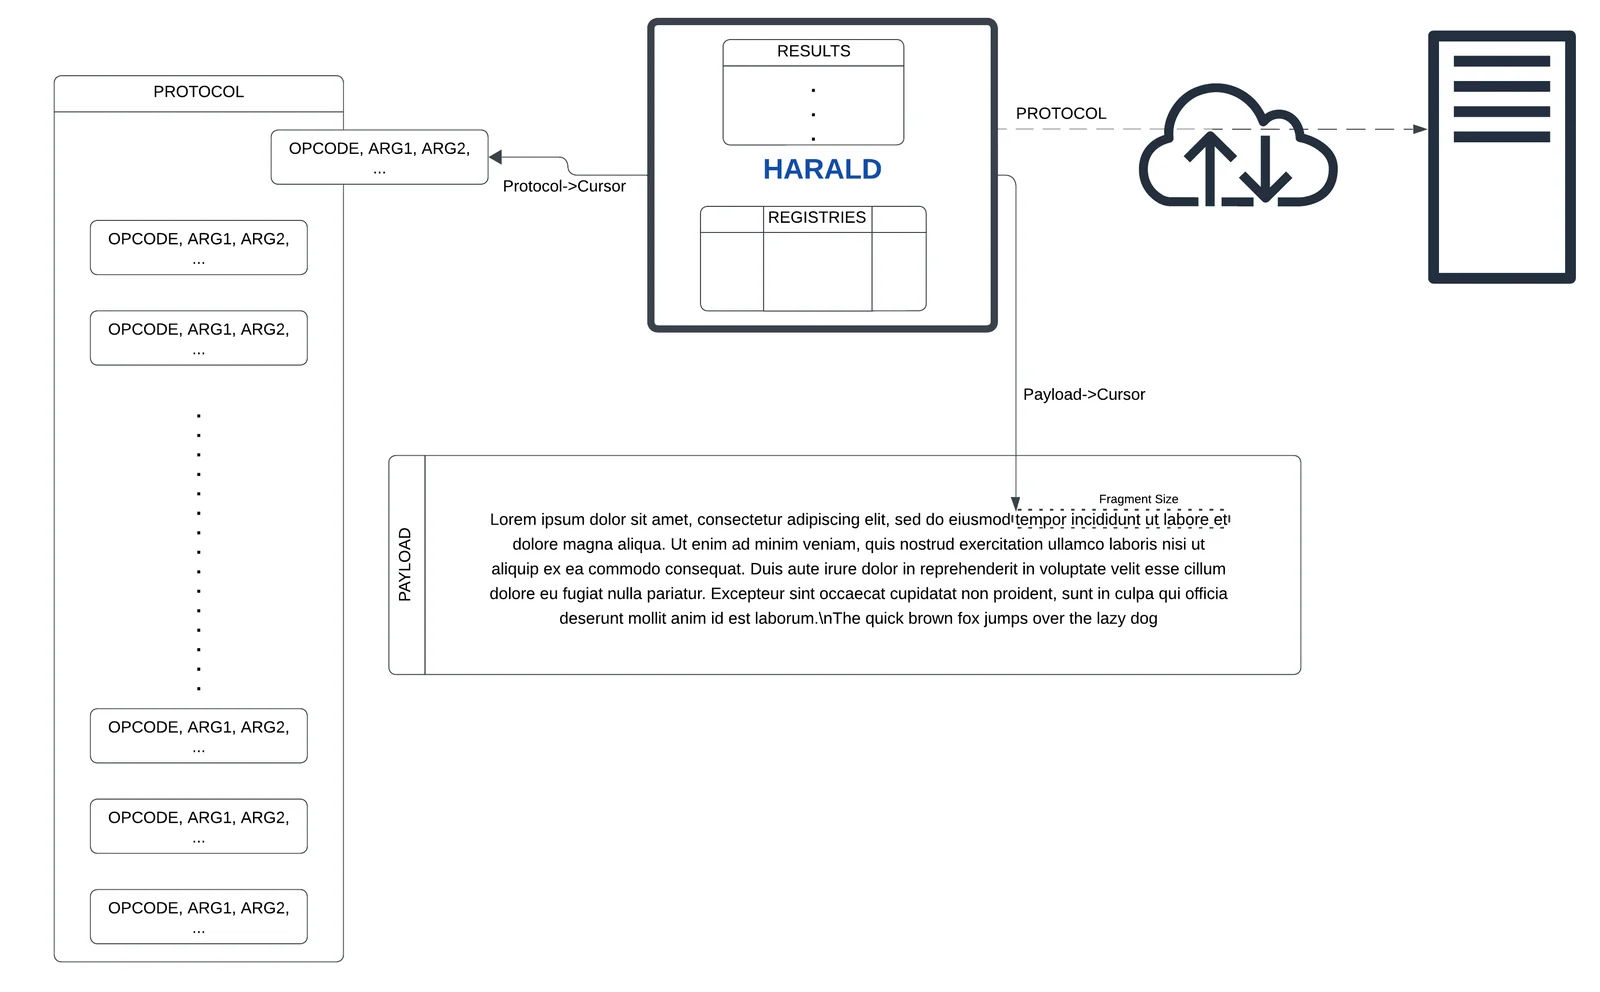 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 simoesctt/-ctt-nsp-convergent-time-theory---network-stack-projection-cve-2026-24858-
A Proof-of-Concept demonstrating the application of 3D Navier-Stokes CTT formulations to packet flow optimization and defensive bypass.
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 dovughs/mora-hwbp
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
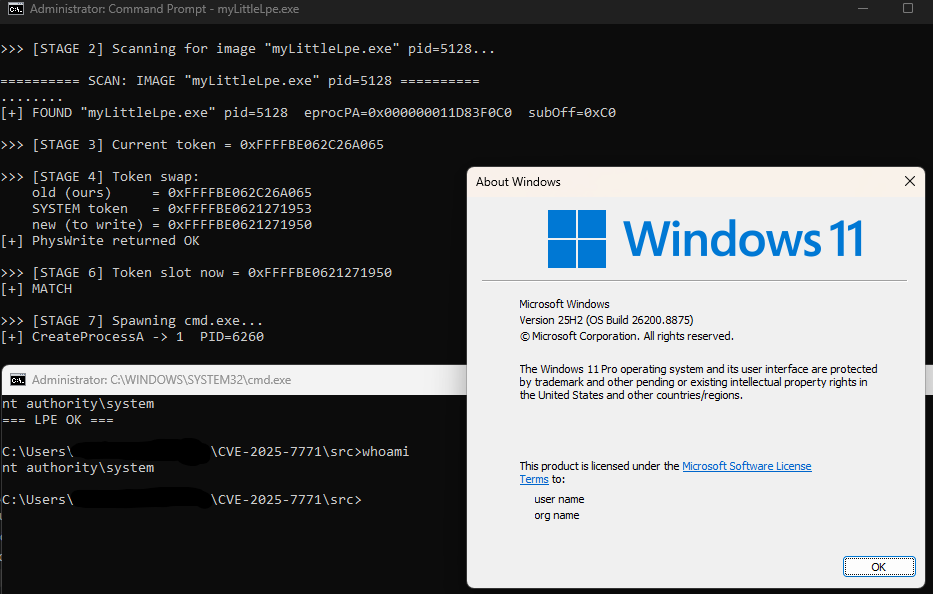 enessakircolak/cve-2025-7771
ThrottleStop.sys Arbitrary Physical Memory R/W
 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).