
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
lldp preview

lldp

GitHubwhispergate/lldp

C2 profile for Mythic tunneling encrypted peer-to-peer agent traffic through IEEE 802.1AB LLDP Organizationally Specific TLVs for covert Layer 2…
adversarial-attackcommand-and-controlids-ips-evasion+1
23
1 month ago
bedaisy-bypass preview

bedaisy-bypass

GitHubgmh5225/bedaisy-bypass

Kernel-mode hook that intercepts, decrypts, and nullifies BEDaisy-to-service report traffic to suppress anti-cheat detection on UEFI and non-UEFI…
adversarial-attackids-ips-evasionred-teaming
52 years ago
mora-hwbp preview

mora-hwbp

GitHubdovughs/mora-hwbp

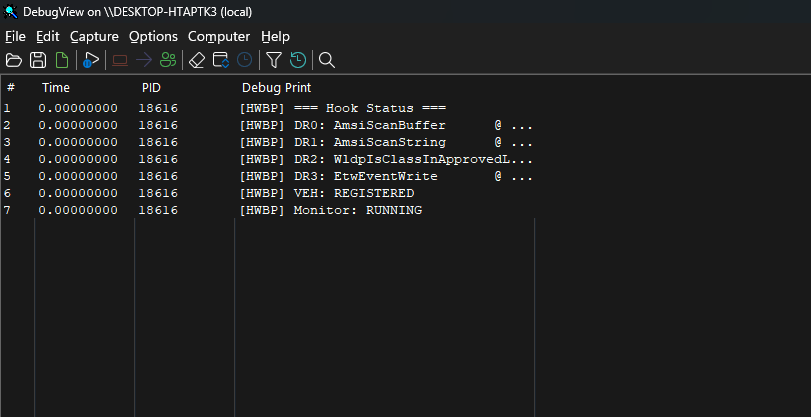
Hardware Breakpoint (DR0-DR7) based patch-less user-mode hooking & telemetry instrumentation engine (AMSI, WLDP & ETW PoC).
adversarial-attackdebuggersdefensive-tools+3
1811 days ago
xspawn preview

xspawn

GitHubcenobyte-vincit/xspawn

Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…

adversarial-attackids-ips-evasionpersistence-mechanisms+2
1 month ago
PSSW100AVB preview

PSSW100AVB

GitHubtihanyin/pssw100avb

A list of useful Powershell scripts with 100% AV bypass (At the time of publication).

ai-securitycommand-and-controlids-ips-evasion+5
1.4k4 months ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k27 days ago
FalsePositives preview

FalsePositives

GitHubdidierstevens/falsepositives

Tools that trigger False Positive AV alerts
adversarial-attackdefensive-toolsids-ips-evasion+3
591 year ago
BokuLoader preview

BokuLoader

GitHubxforcered/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!

adversarial-attackcommand-and-controlids-ips-evasion+4
3322 years ago
WTSRM preview

WTSRM

GitHubrad9800/wtsrm

WTSRM

adversarial-attackeducationids-ips-evasion+2
2134 years ago
CallMeWin32kDriver preview

CallMeWin32kDriver

GitHubgmh5225/callmewin32kdriver

Load your driver like win32k.sys

adversarial-attackids-ips-evasionpost-exploitation+1
2584 years ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9588 months ago
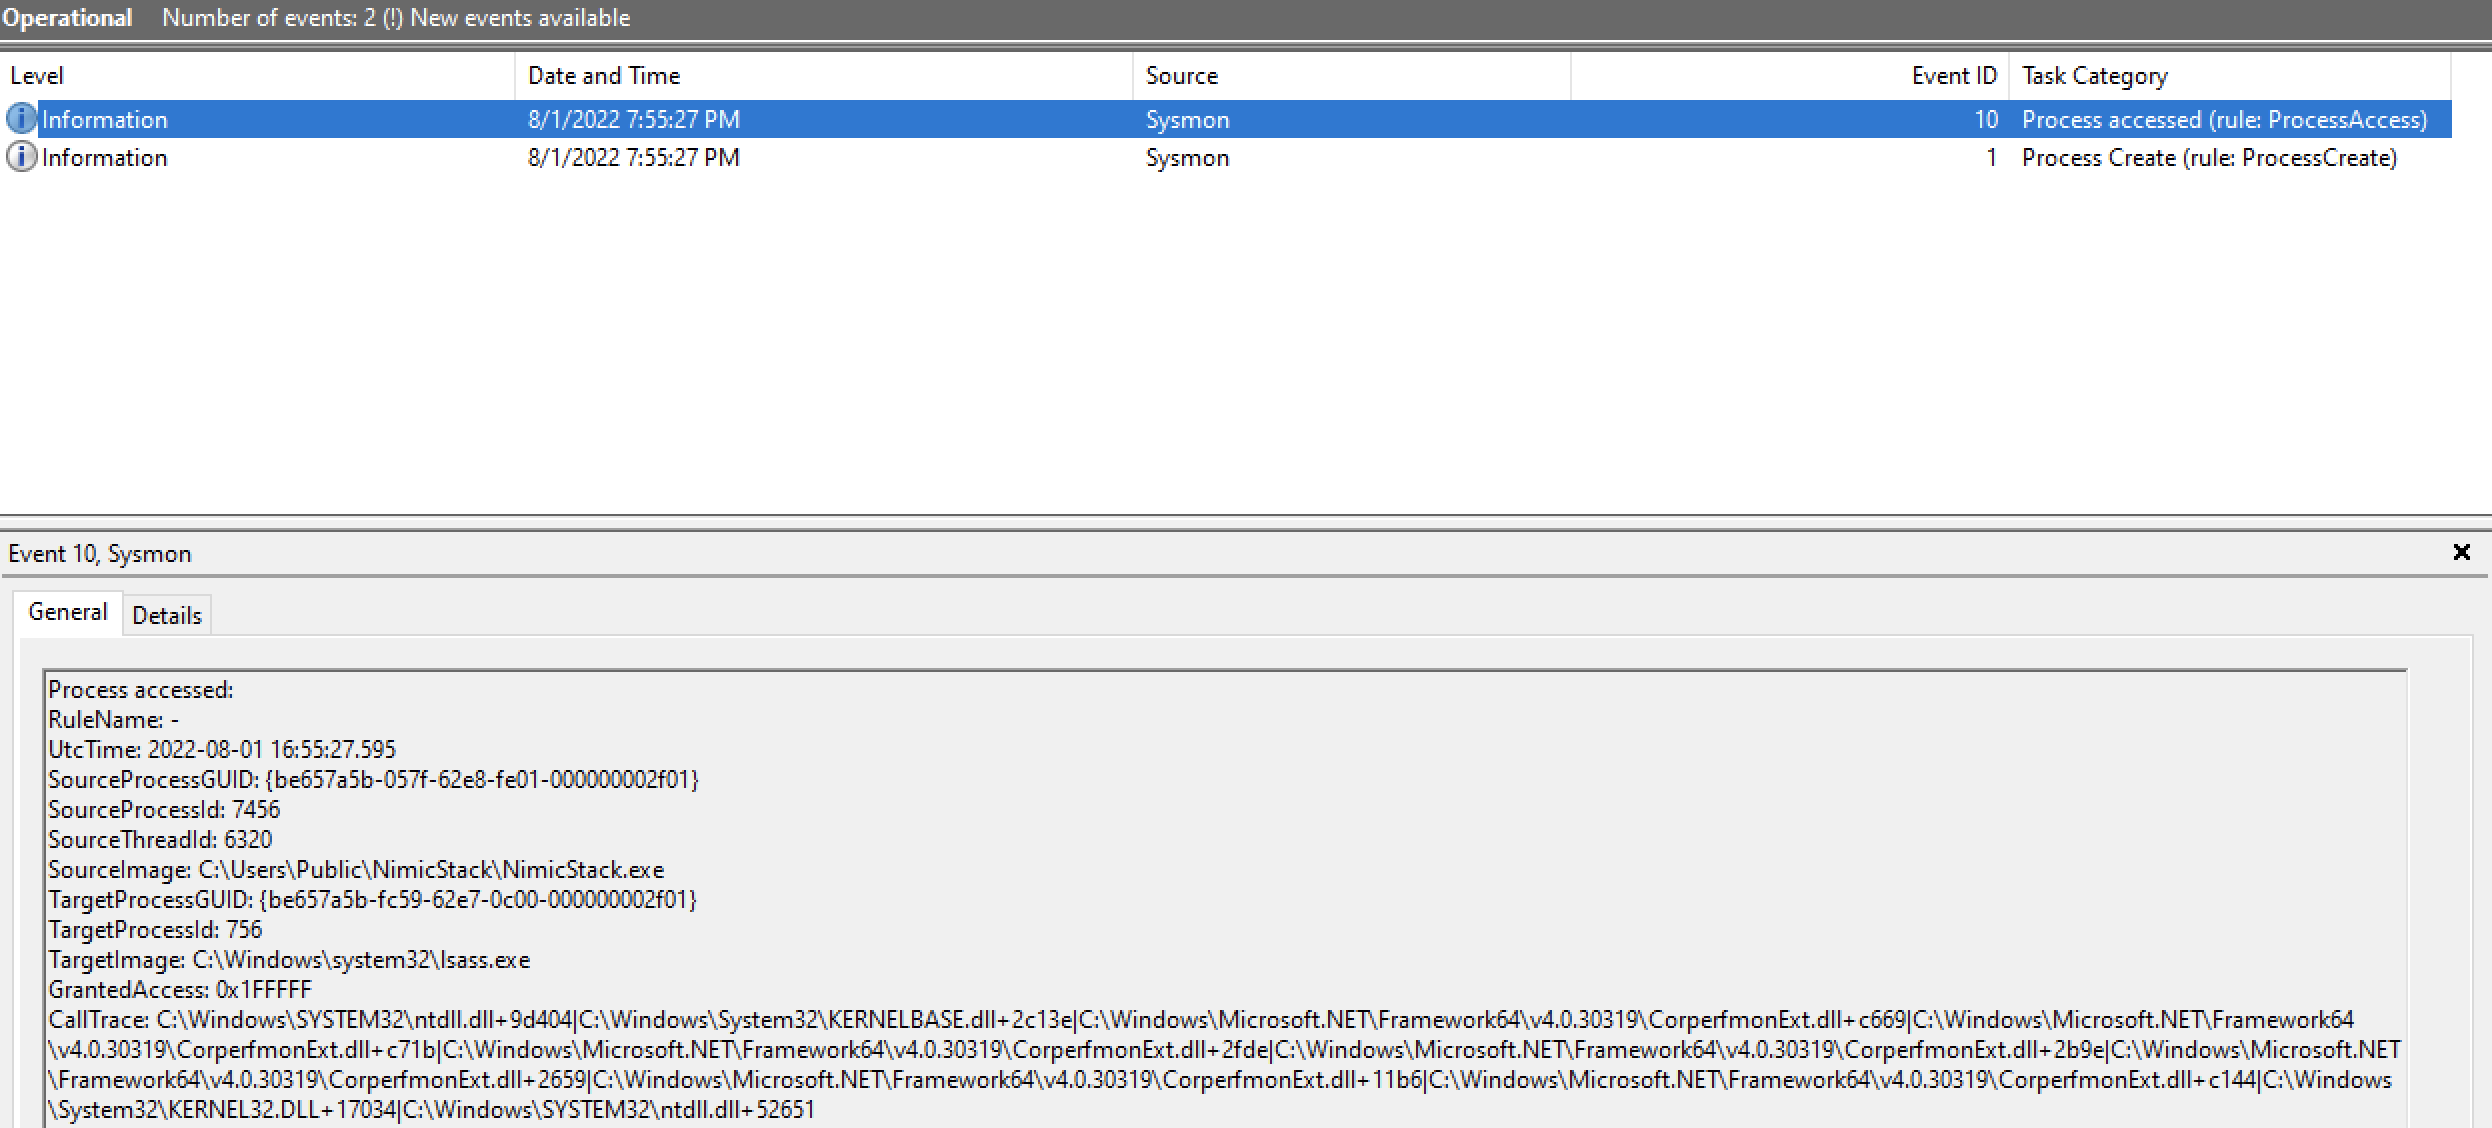
NimicStack preview

NimicStack

GitHubfrkngksl/nimicstack

NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs
adversarial-attackids-ips-evasionpost-exploitation+1
976 months ago
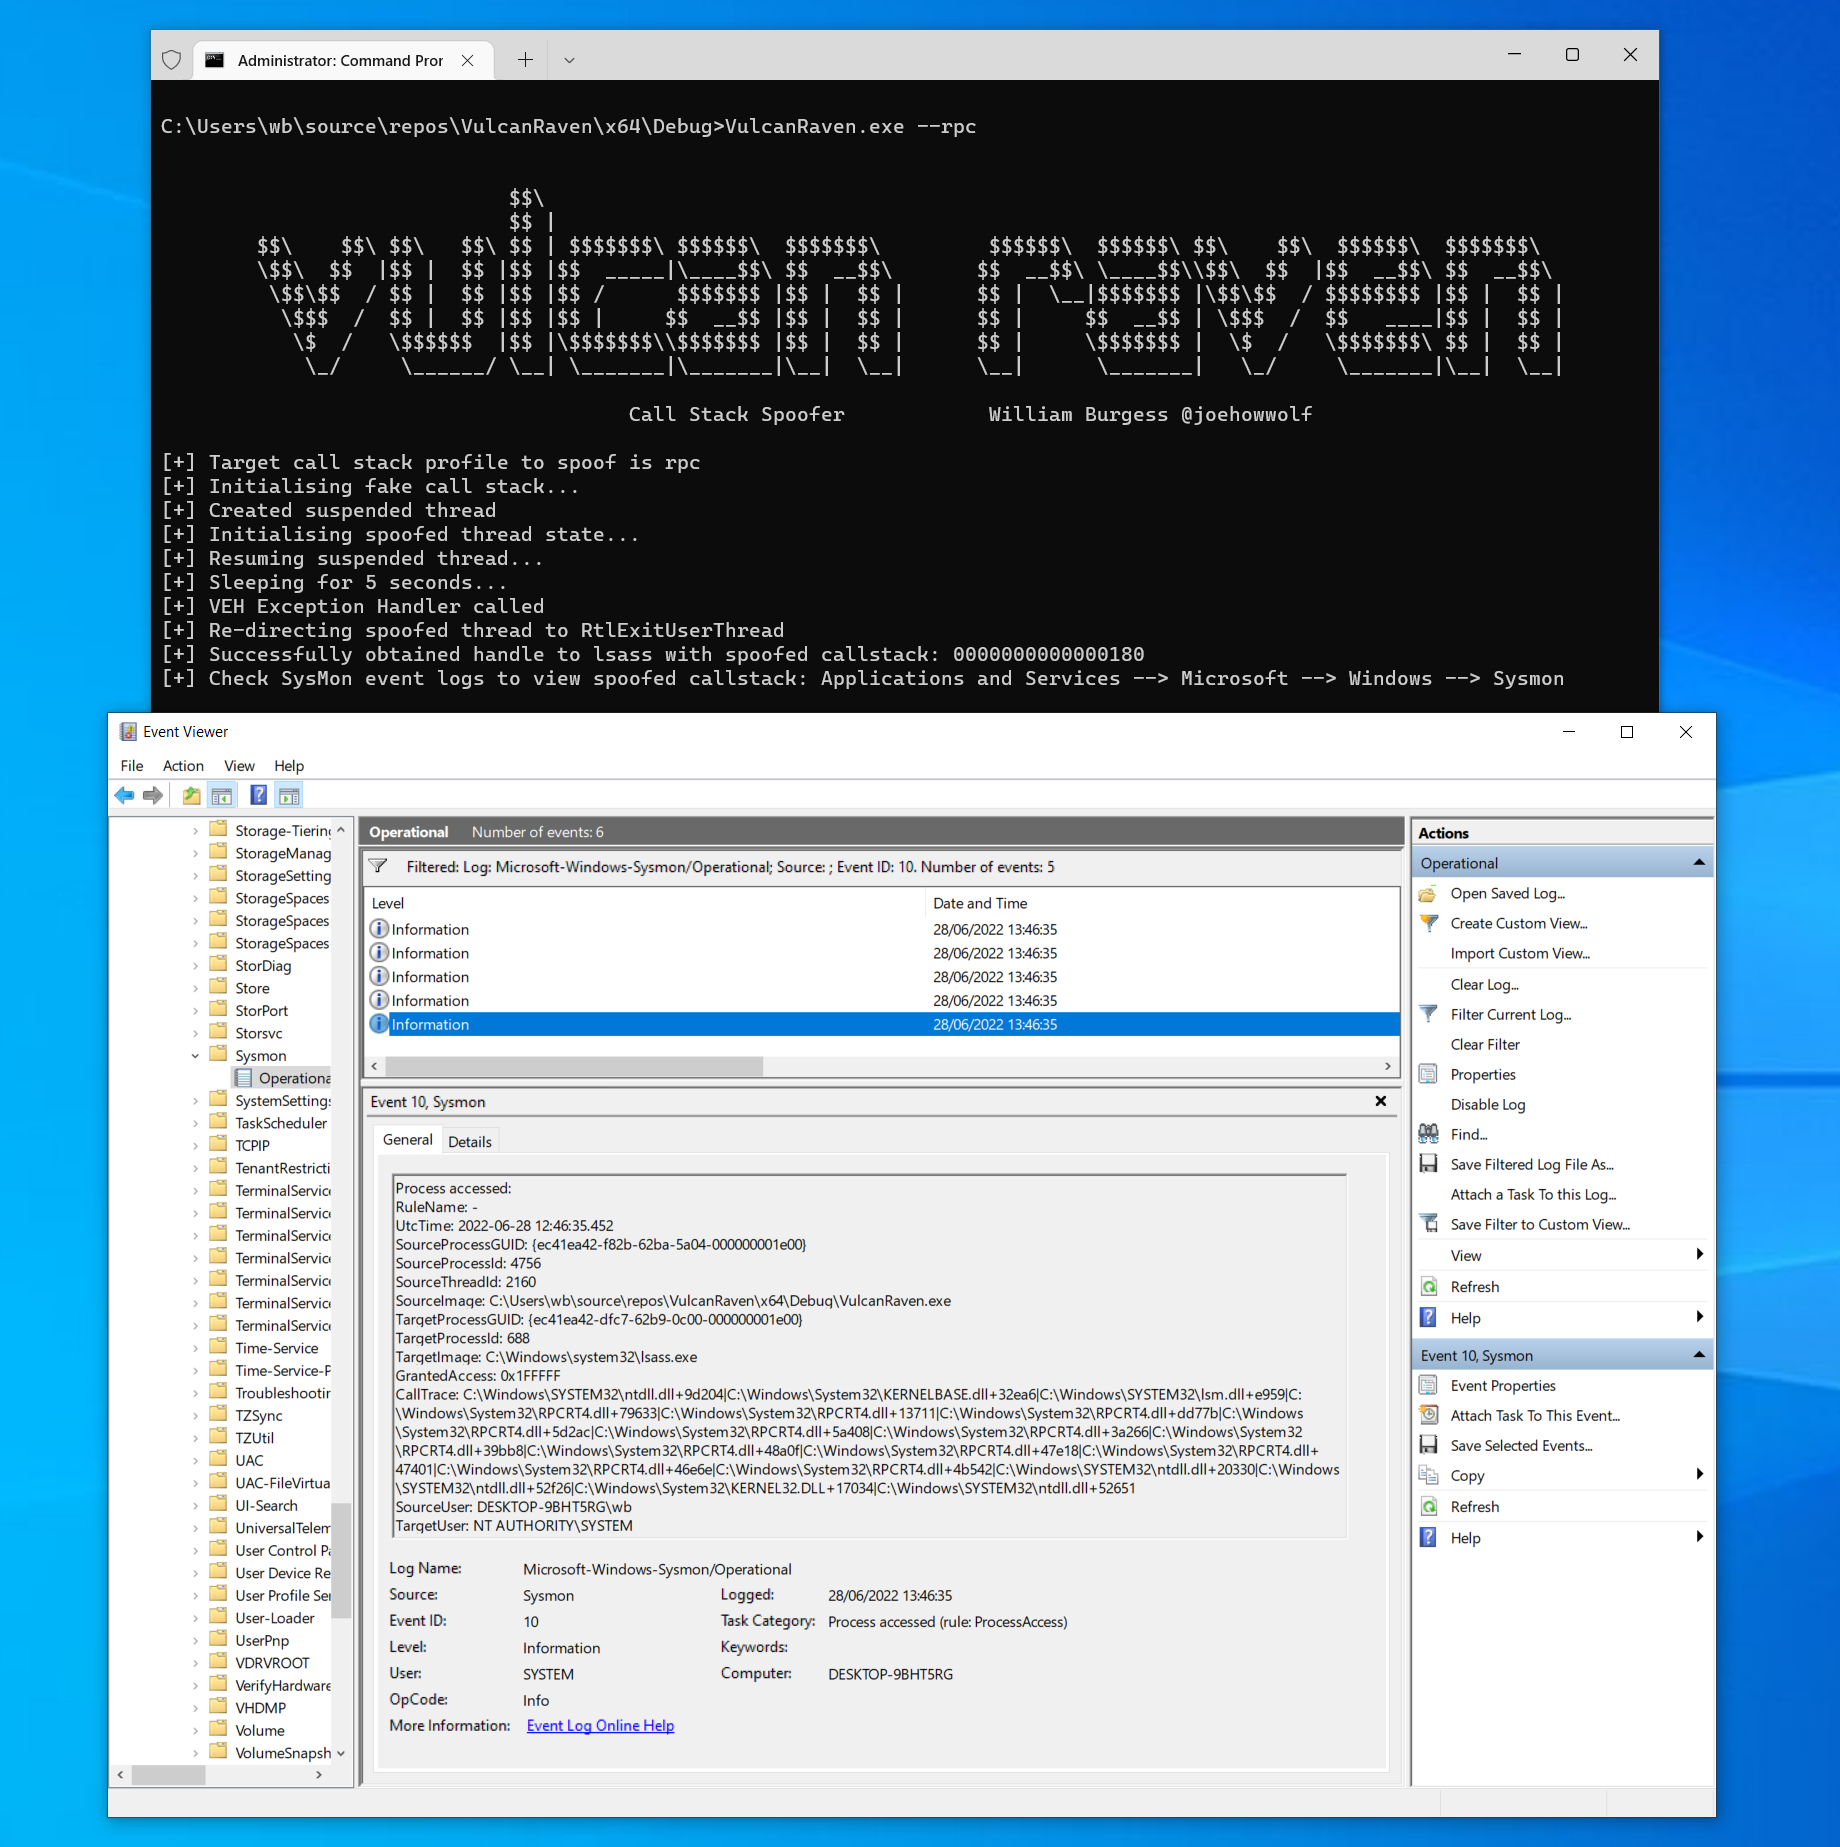
CallStackSpoofer preview

CallStackSpoofer

GitHubwithsecurelabs/callstackspoofer

A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)

adversarial-attackids-ips-evasionpost-exploitation+1
5981 year ago
Qemuno preview

Qemuno

GitHubsygnialabs/qemuno

Qemuno Framework

adversarial-attackids-ips-evasionpenetration-testing+2
244 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.

adversarial-attackbinary-analysiseducation+3
36410 months ago
Windows-SignedBinary preview

Windows-SignedBinary

GitHubmr-un1k0d3r/windows-signedbinary

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
adversarial-attackbinary-analysishash-analysis+4
2617 years ago
AMSI-ETW-Patch preview

AMSI-ETW-Patch

GitHubmr-un1k0d3r/amsi-etw-patch

Patch AMSI and ETW
adversarial-attackids-ips-evasionpost-exploitation+1
2502 years ago
Unwinder preview

Unwinder

GitHubkudaes/unwinder

Call stack spoofing for Rust

adversarial-attackids-ips-evasionpayload-development+2
3851 year ago
Previous1234Next