

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
NimicStack — NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs | Kitploit
Tools/GitHubGitHub/frkngksl/nimicstack
IDS/IPS EvasionPost-ExploitationRed TeamingAdversarial Attack
GitHubfrkngksl/nimicstack

NimicStack

NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs

View Repository
954387 months agoReviewed by Kitploit
Share

NimicStack

NimicStack is the pure Nim implementation of Call Stack Spoofing technique to mimic legitimate programs. Whole project is based on the PoC shared by WithSecure Labs

Compilation

You can directly compile the source code with the following command:

nim c -d=mingw --app=console --cpu=amd64 -o:NimicStack.exe .\Main.nim

In case you get the error "cannot open file", you should also install required dependencies:

nimble install ptr_math winim

Usage

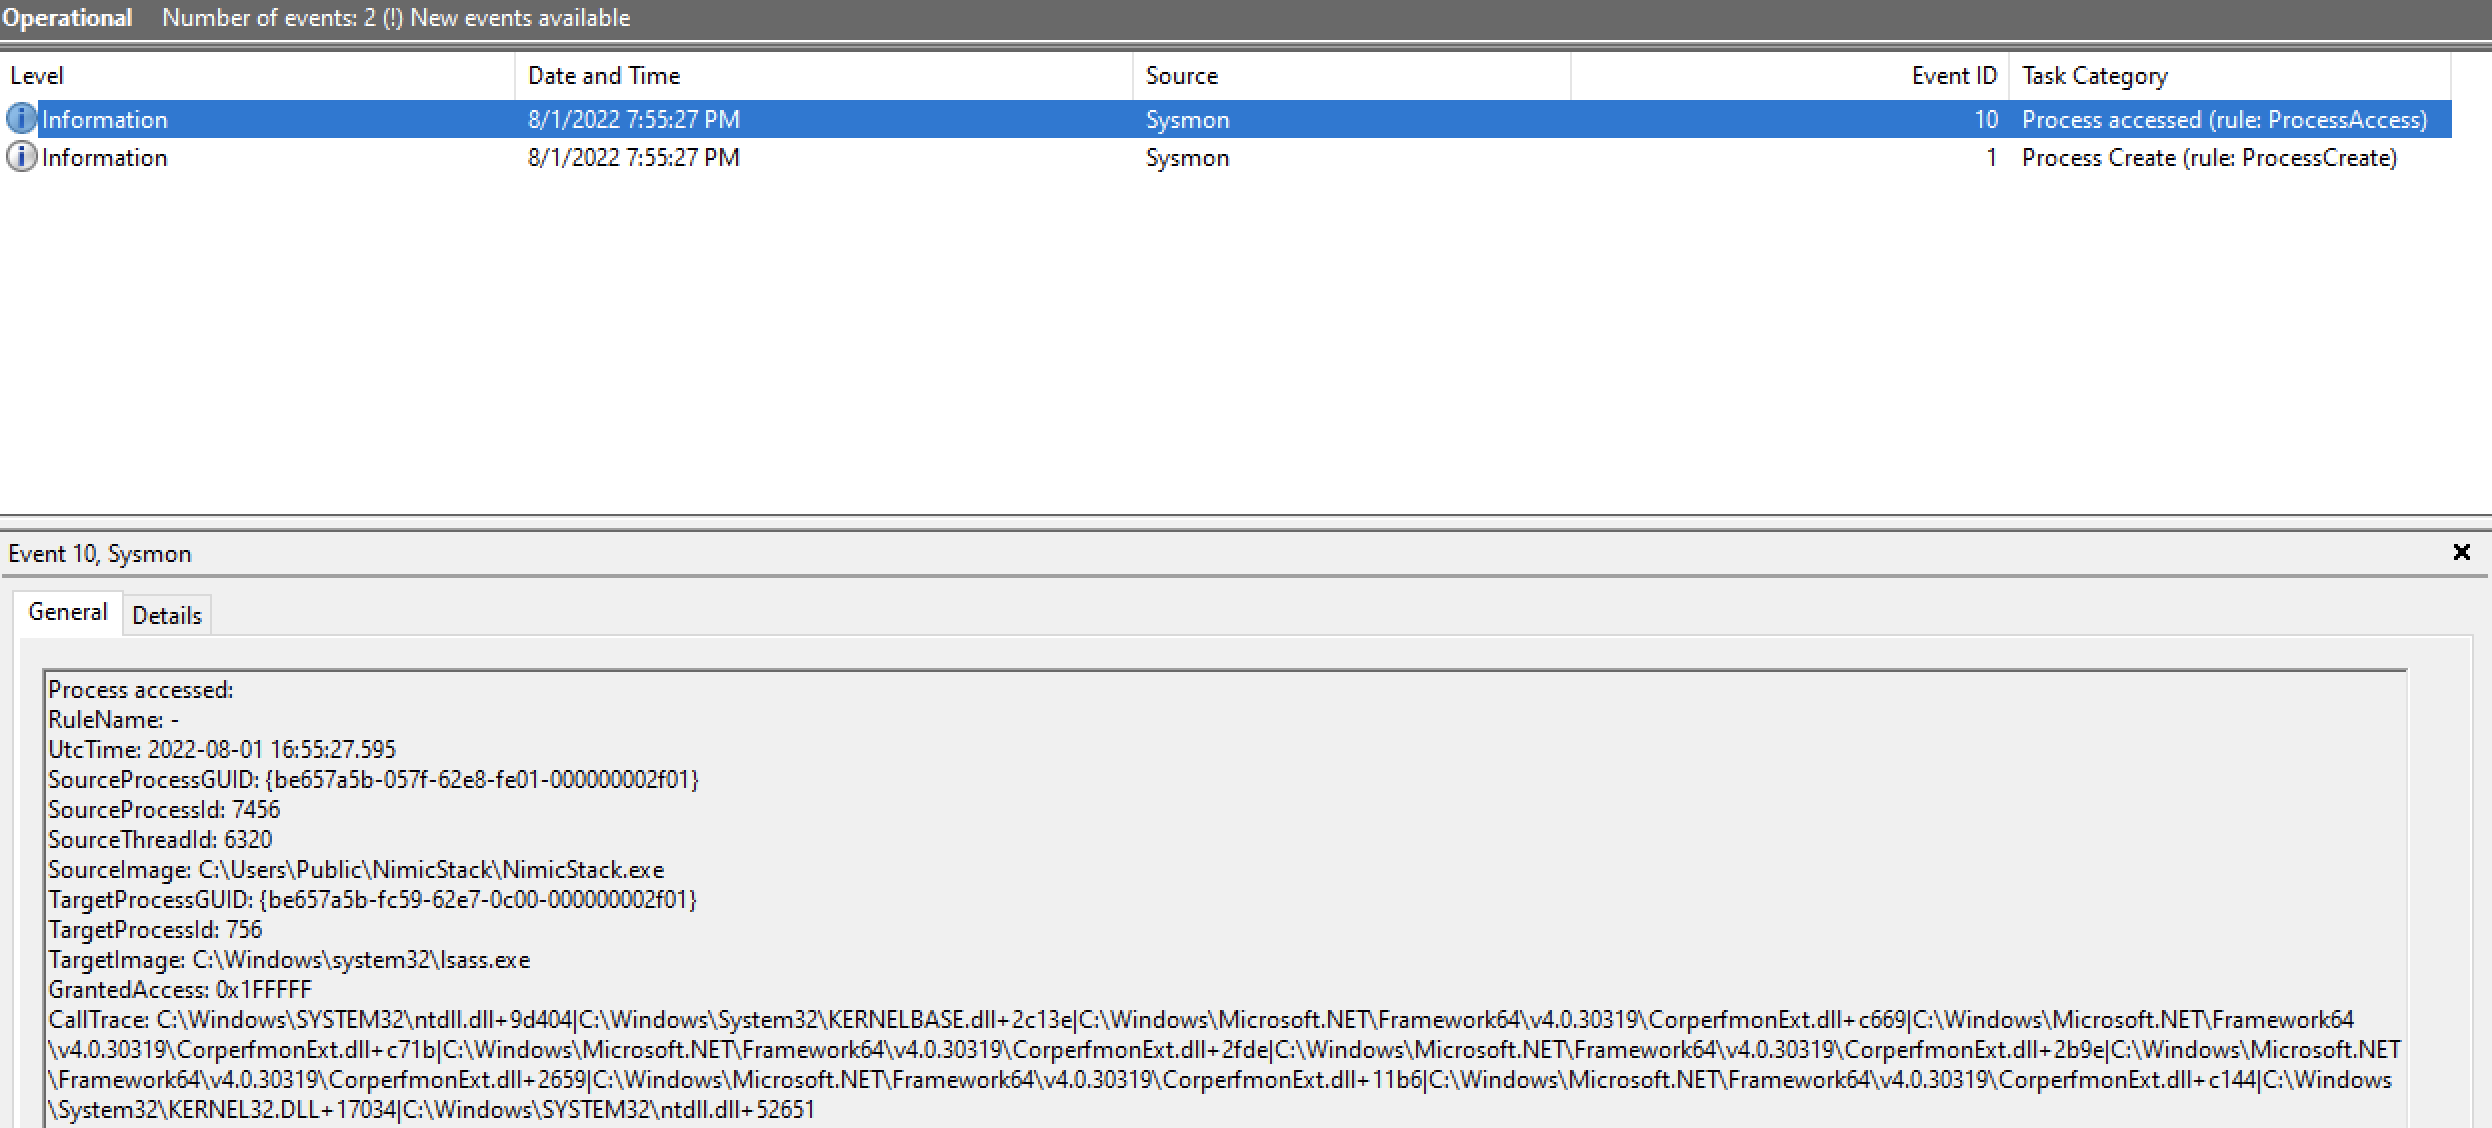
Like the reference project, NimicStack can mimic three example call stacks which are WMI, RPC and Svchost while opening the LSASS process.

.\NimicStack.exe <--wmi, --rpc, --svchost>

Example output for mimicked WMI call stack:

PS C:\Users\test\Desktop\NimicStack> .\NimicStack.exe --wmi

███╗   ██╗██╗███╗   ███╗██╗ ██████╗███████╗████████╗ █████╗  ██████╗██╗  ██╗
████╗  ██║██║████╗ ████║██║██╔════╝██╔════╝╚══██╔══╝██╔══██╗██╔════╝██║ ██╔╝
██╔██╗ ██║██║██╔████╔██║██║██║     ███████╗   ██║   ███████║██║     █████╔╝
██║╚██╗██║██║██║╚██╔╝██║██║██║     ╚════██║   ██║   ██╔══██║██║     ██╔═██╗
██║ ╚████║██║██║ ╚═╝ ██║██║╚██████╗███████║   ██║   ██║  ██║╚██████╗██║  ██╗
╚═╝  ╚═══╝╚═╝╚═╝     ╚═╝╚═╝ ╚═════╝╚══════╝   ╚═╝   ╚═╝  ╚═╝ ╚═════╝╚═╝  ╚═╝

                              @R0h1rr1m

[+] wmi frame is selected!
[+] Required libraries were imported for return address calculation!
[+] SeDebugPrivilege is enabled!
[+] Fake Call Stack was created!
[+] Trying to find LSASS pid...
[+] LSASS pid found!: 756
[+] Registers were set for NtOpenProcess call!
[+] VEH callback was set for the suspended thread!
[+] Thread is resuming...
[+] VEH callback was called!
[+] Redirecting thread to RtlExitUserThread...
[+] Spoof is successful! Handle is 356
[+] You can check the spoofed call stack from Sysmon!

And Sysmon output for this call:
image

References

  • https://labs.withsecure.com/blog/spoofing-call-stacks-to-confuse-edrs/
  • https://github.com/countercept/CallStackSpoofer

Disclaimer

For authorized security testing only. Misuse of this tool against systems without explicit permission is illegal.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →




