
CVE-2026-94095
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
embedded-systems-securityexploitationhardware-iot-security+5
1
hackspeak/cve-2026-94095PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
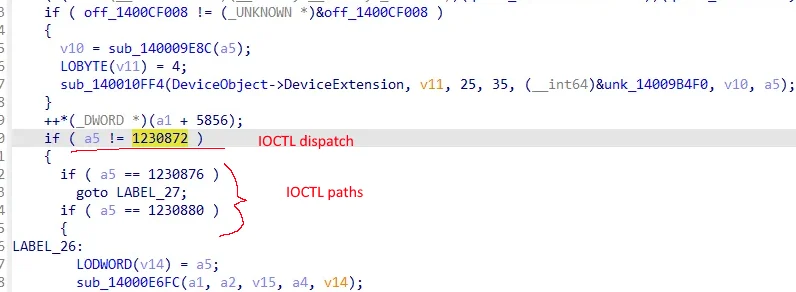 catforgor/cve-2026-51585
rt26cx21x64.sys exploit (Realtek PCIe GbE/2.5GbE/5GbE family)
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 v3ilsm1th/cve-2025-27840-wip
Work-in-progress PoC for CVE-2025-27840, an ESP32 Bluetooth vulnerability involving undocumented HCI commands enabling memory access and device…
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
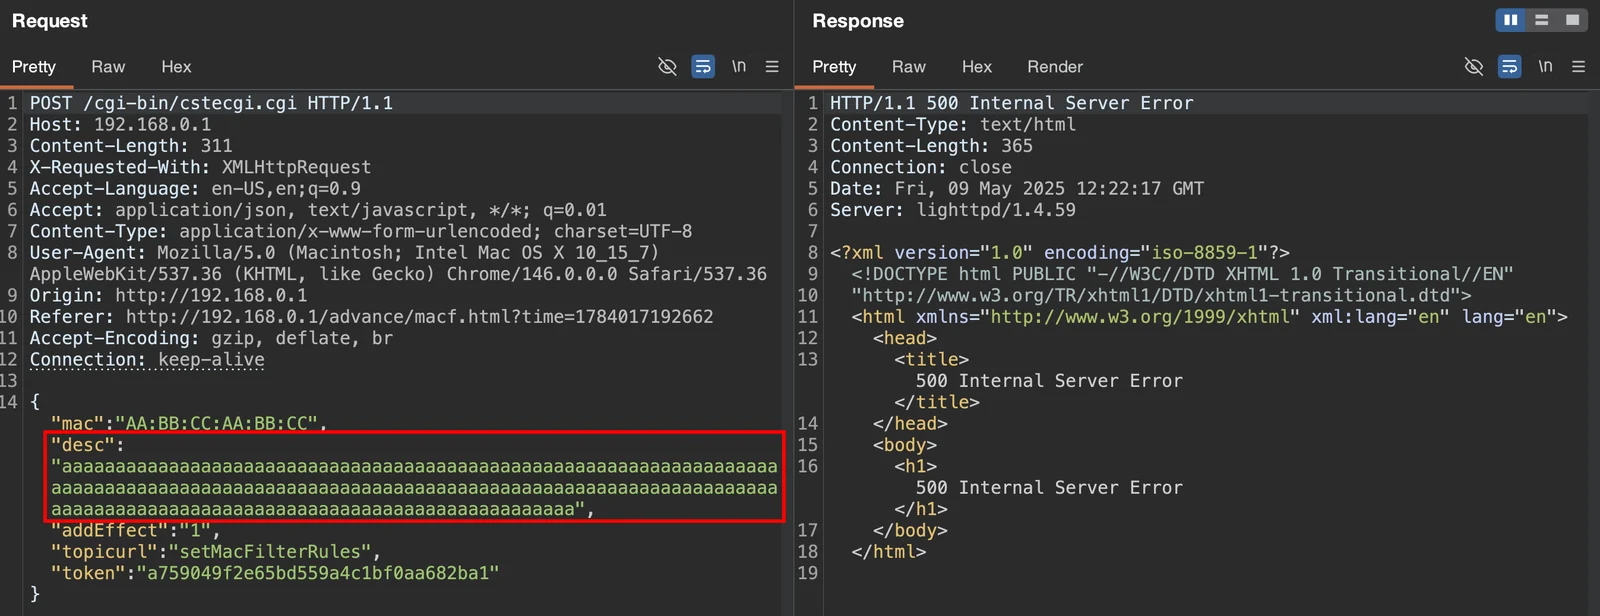 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 x41sec/cve-2021-34600
Proof-of-concept exploit for CVE-2021-34600, demonstrating a key generation vulnerability in Telenot access control systems using Proxmark3 RFID…
 tony102741/cve-2026-15469
Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…
 osy/webcamviewer
Proof-of-concept demonstrating CVE-2021-30731, allowing unauthorized USB webcam access on macOS. Built with libuvc, it previews connected webcams on…
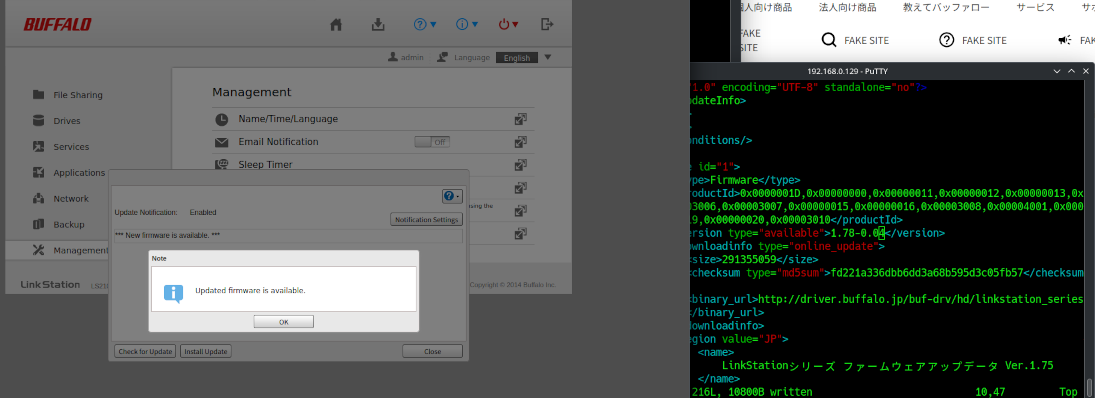 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 pazhanivel07/hardware_interfaces-a10_r33_cve-2021-0510
Exploit or analysis code for CVE-2021-0510, a vulnerability in Android hardware interfaces, targeting A10_r33 builds.
 0xqrx/cve-2024-6333
Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
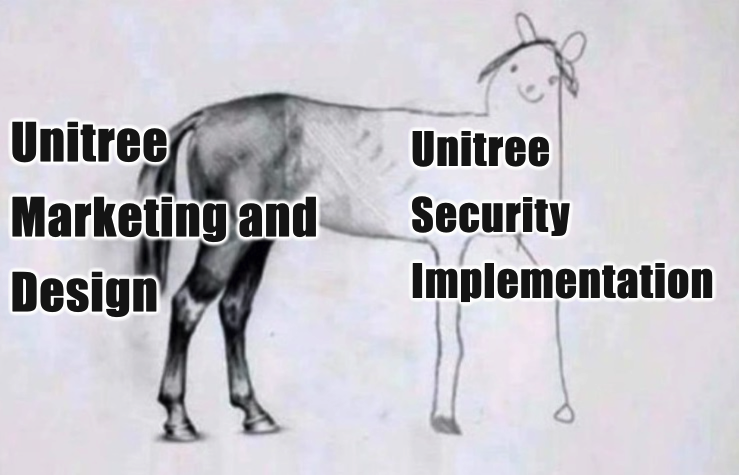 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 jasondoyle/google-nest-cam-bug-disclosures
PoC vulnerability disclosures for consumer IoT cameras, detailing BLE buffer overflow and WiFi disassociation attacks that can take devices offline.
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…