bettercap
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
19.8k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
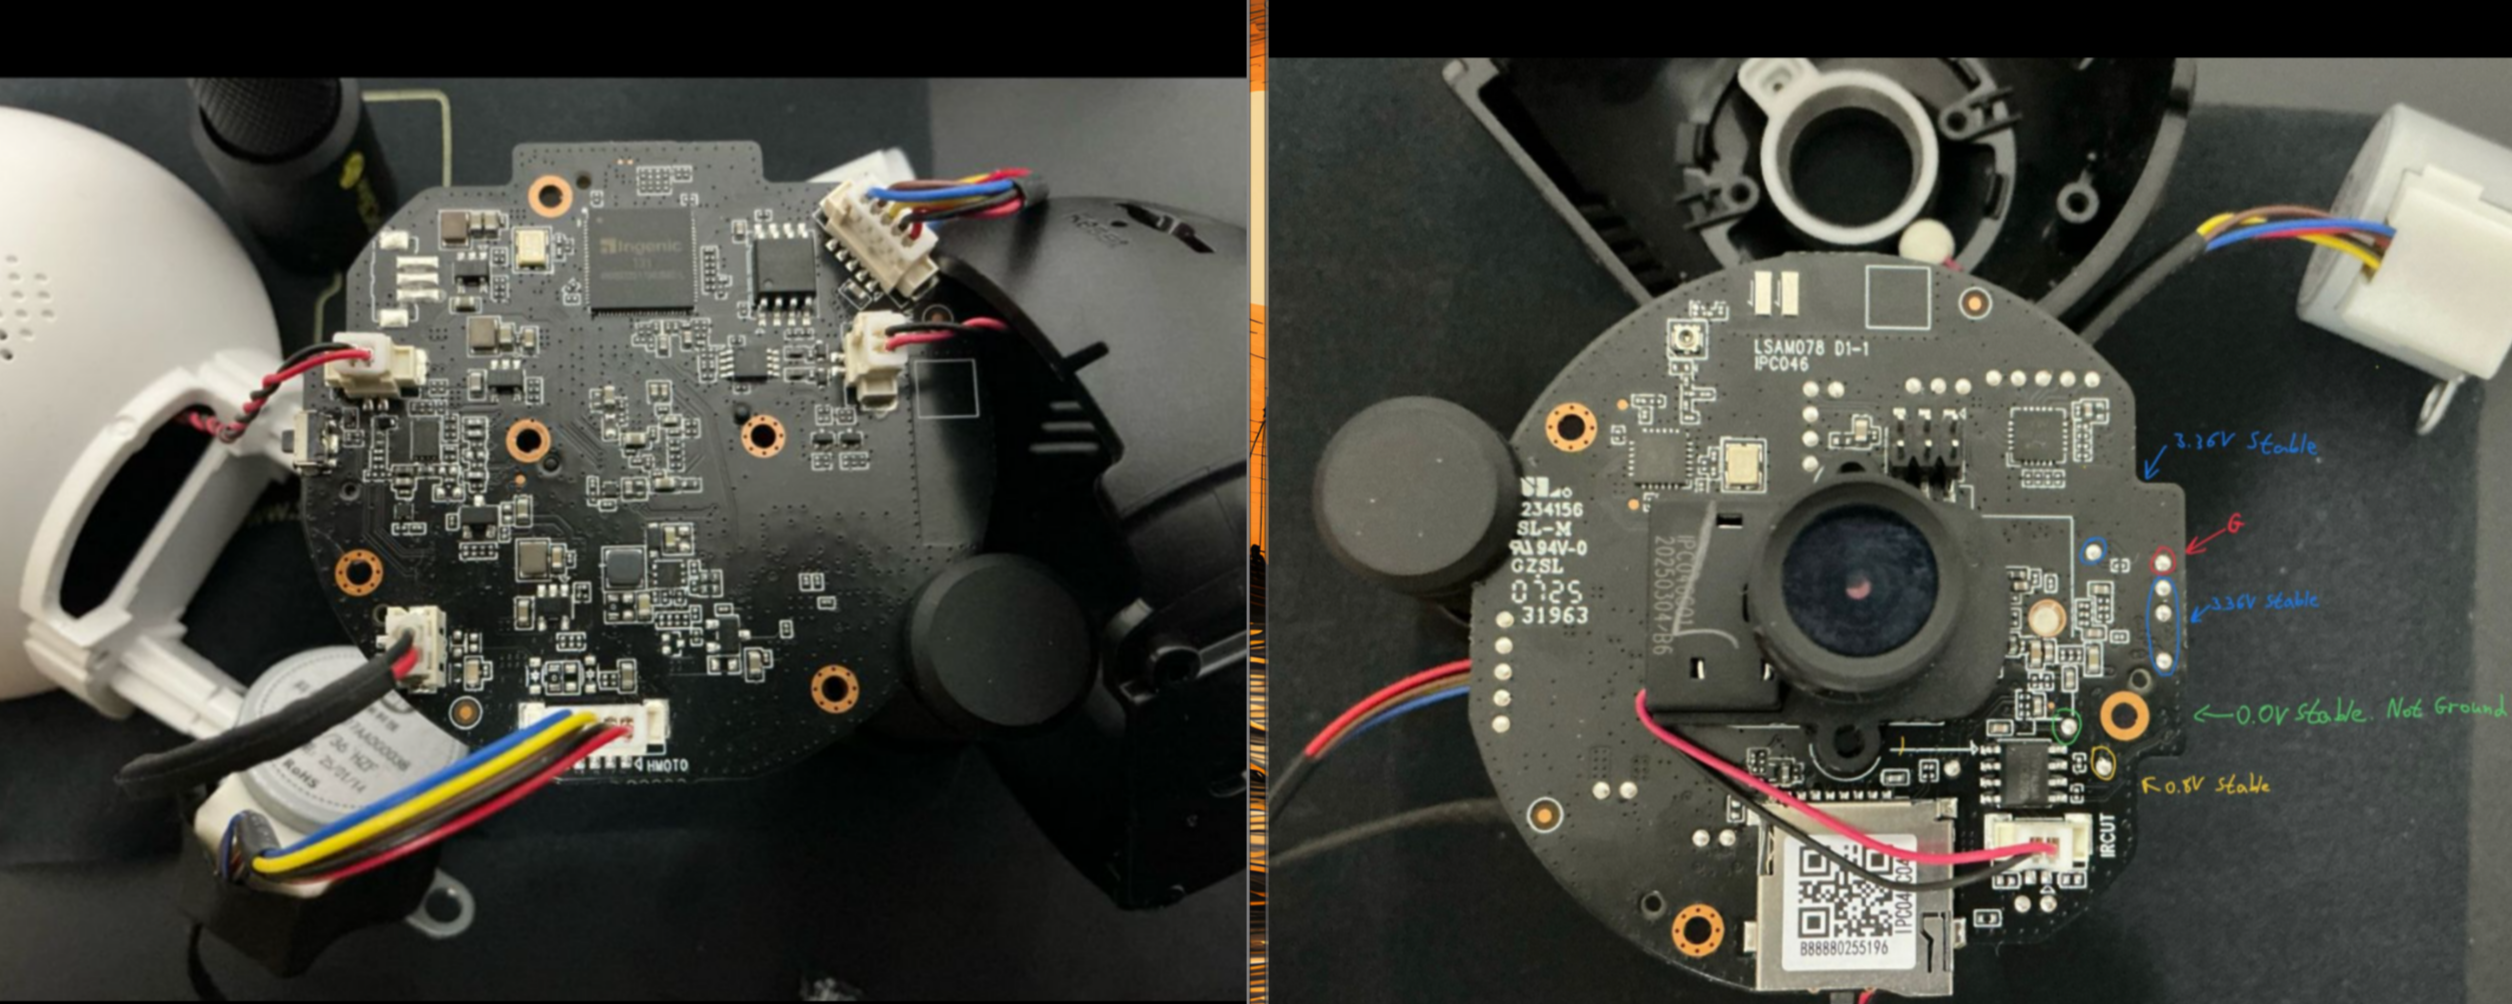 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 nfc-tools/milazycracker
Mifare Classic Plus - Hardnested Attack Implementation for SCL3711 LibNFC USB reader
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device

 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…