
Archived
peafl64
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
binary-analysisdynamic-code-analysisfuzzing+2
206
 amossys/memitm
Tool to make in memory man in the middle
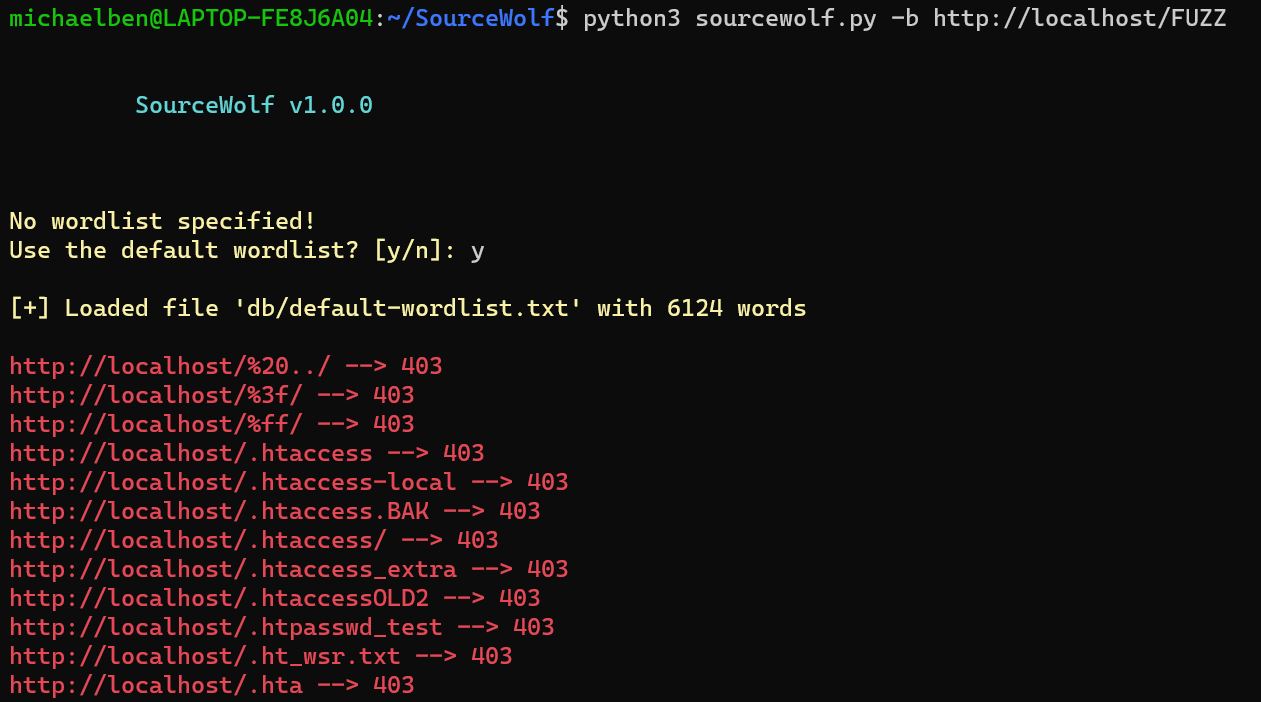 ksharinarayanan/sourcewolf
Amazingly fast response crawler to find juicy stuff in the source code! 😎🔥
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 dwisiswant0/ppfuzz
A fast tool to scan client-side prototype pollution vulnerability written in Rust. 🦀
 oxagast/ansvif
A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 pwndorei/cve-2024-22532
Proof-of-concept exploit for CVE-2024-22532: heap-based buffer overflow in XnView Classic 2.51.5 and NConvert 7.163 via crafted .xwd file, enabling…

 rust-fuzz/cargo-fuzz
Cargo subcommand for coverage-guided Rust fuzzing with libFuzzer: create and run fuzz targets, minimize failures and corpora, and report coverage.
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 rub-nds/pret
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
 0sec-labs/0
Open-source cybersecurity harness to build and deploy sovereign, persistent AI security agents (sentinels) that continuously find, prove and fix…