
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
53 results
turbo-intruder preview

turbo-intruder

GitHubportswigger/turbo-intruder

High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
fuzzingpenetration-testingvulnerability-analysis+1
1.8k
20 days ago
auto-repeater preview

auto-repeater

GitHubxnl-h4ck3r/auto-repeater

Automated HTTP Request Repeating With Burp Suite
fuzzingpenetration-testingweb-proxies-interception+1
383 years ago
crlfi-scanner preview

crlfi-scanner

GitHubcappricio-securities/crlfi-scanner

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
fuzzingpenetration-testingweb-application-exploitation+2
47 months ago
ColonelClustered preview

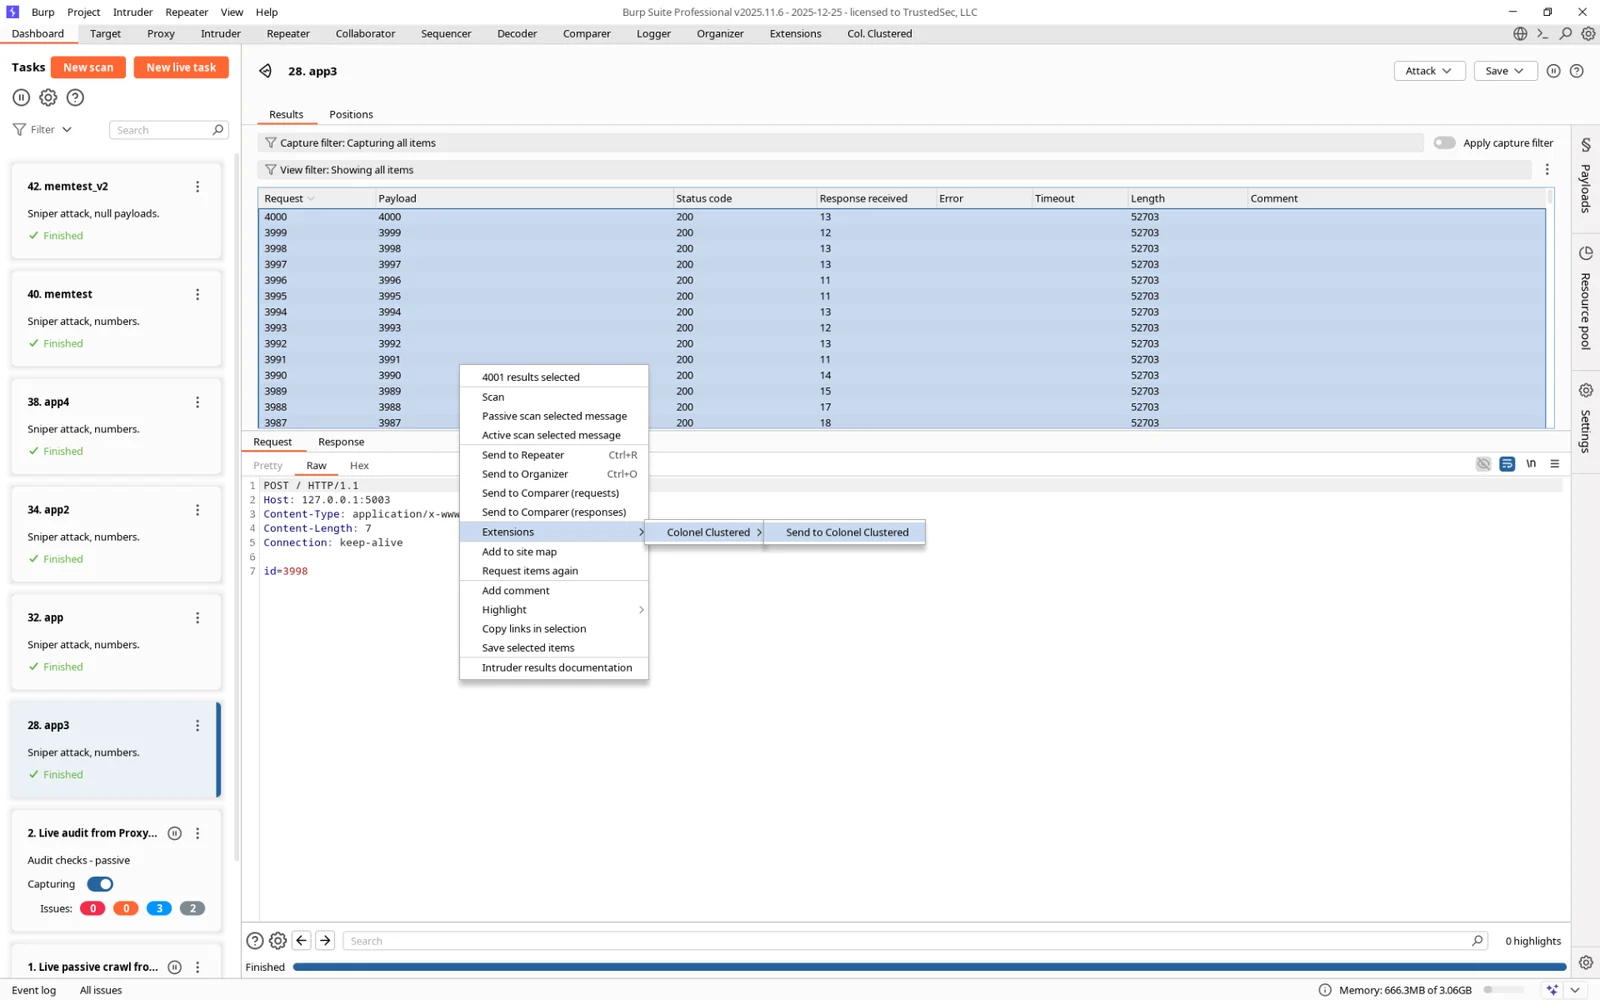
ColonelClustered

GitHubhoodoer/colonelclustered

A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
fuzzingmachine-learningpenetration-testing+5
121 month ago
wssip preview

wssip

GitHubnccgroup/wssip

Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.

fuzzingpenetration-testingweb-proxies-interception+1
4518 years ago
CrackQL preview

CrackQL

GitHubnicholasaleks/crackql

GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…

api-security-testingfuzzingpassword-attacks+2
3523 years ago
cats preview

cats

GitHubendava/cats

Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
api-security-testingfuzzingvulnerability-scanners+1
1.4k14h 32m ago
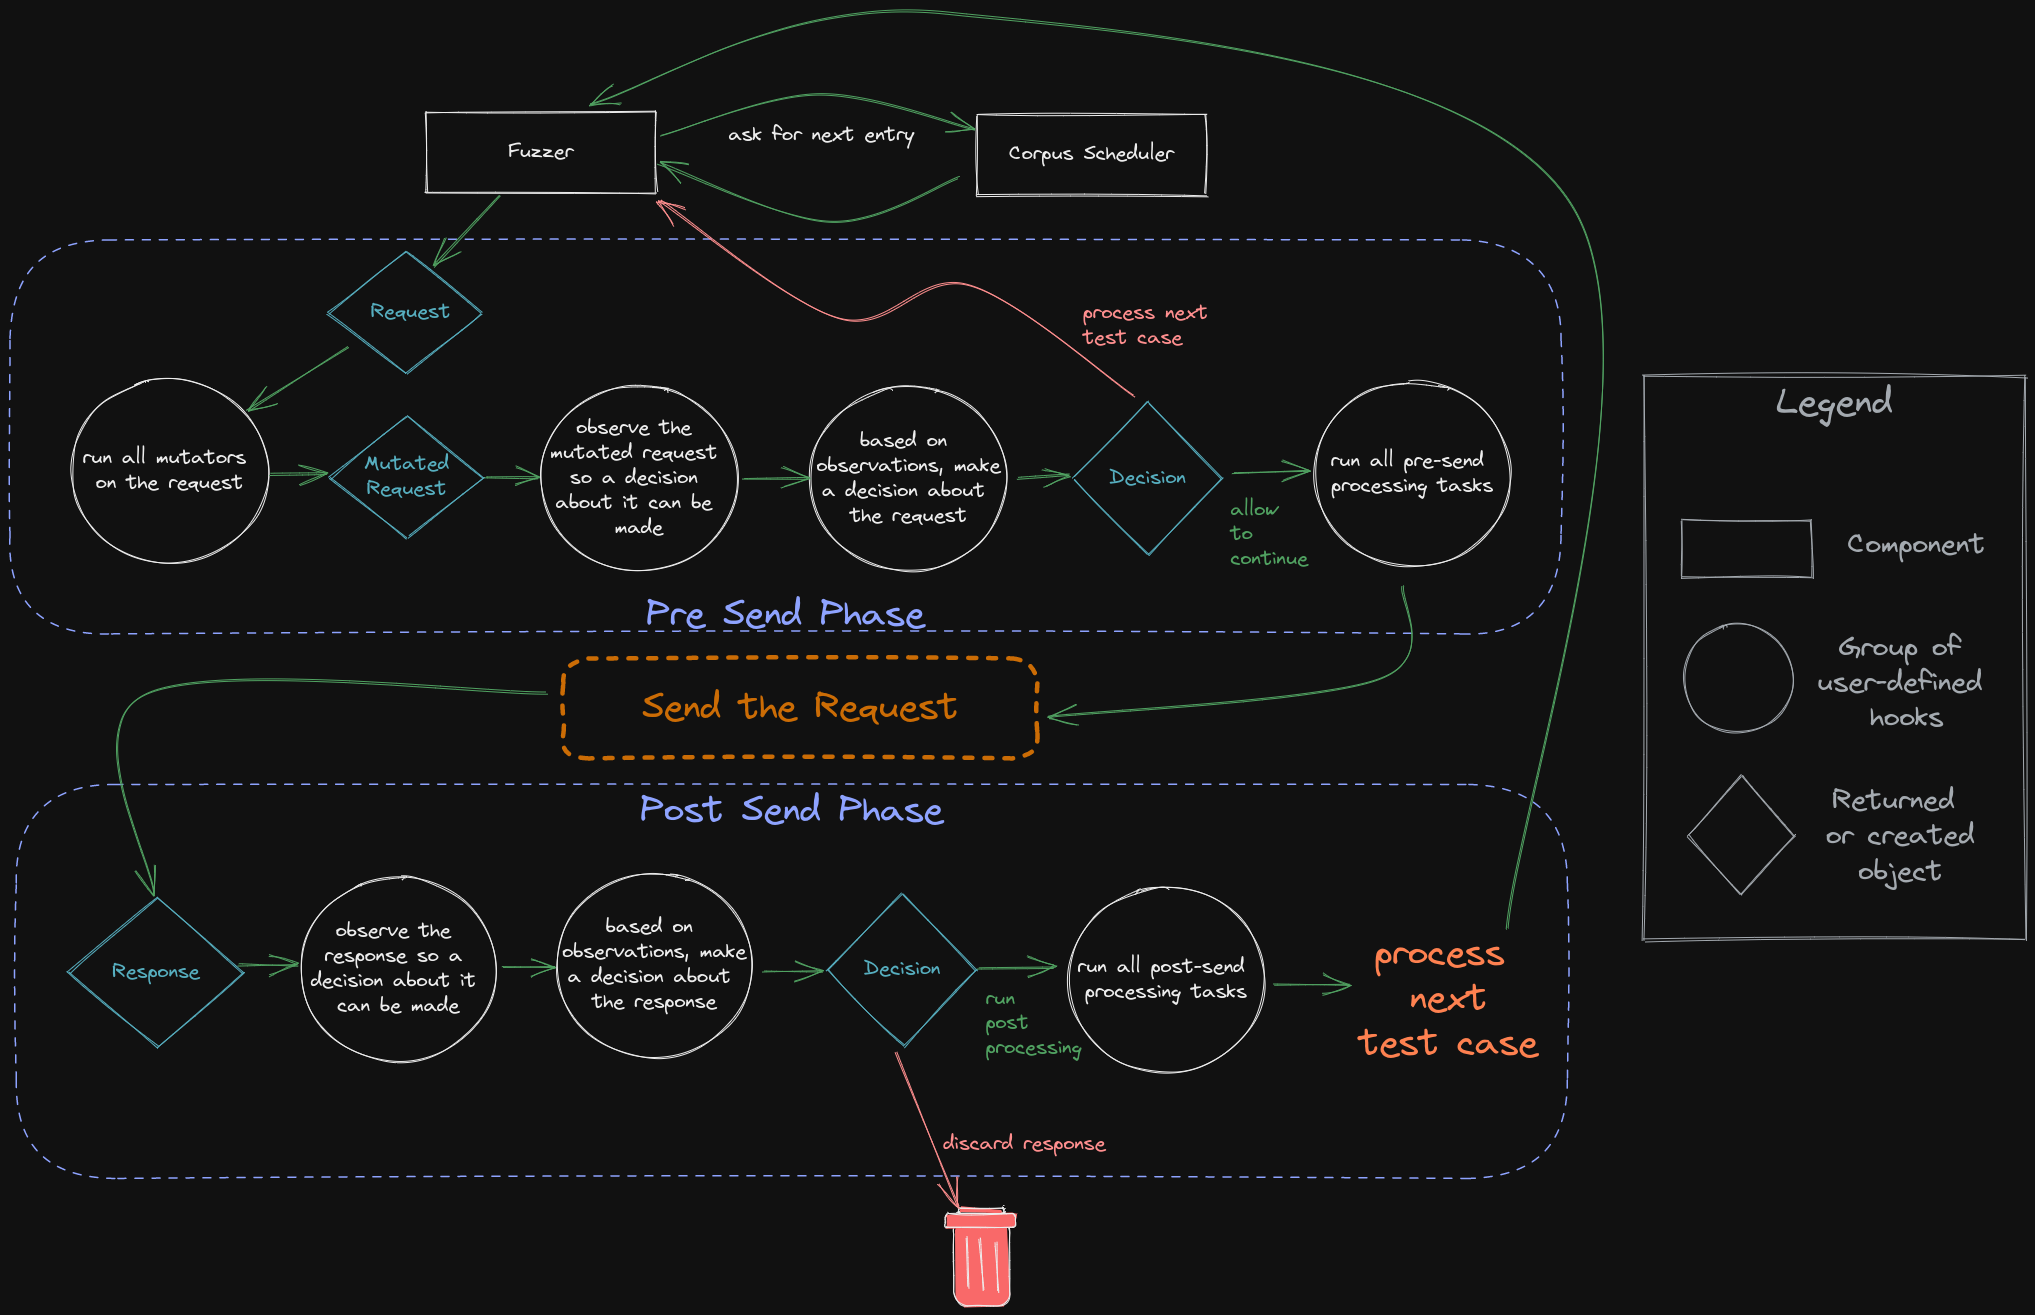
feroxfuzz preview

feroxfuzz

GitHubepi052/feroxfuzz

Build structure-aware black-box HTTP fuzzers in Rust with composable mutators, schedulers, observers, deciders, and processors for custom web and API…

api-security-testingfuzzingutilities-frameworks+1
2229 months ago
jwt_tool preview

jwt_tool

GitHubticarpi/jwt_tool

:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
api-securityapi-security-testingcryptography+5
6.8k1 year ago
restler-fuzzer preview

restler-fuzzer

GitHubmicrosoft/restler-fuzzer

RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…

api-security-testingcloud-securityfuzzing+2
3.0k8 months ago
ActiveScanPlusPlus preview

ActiveScanPlusPlus

GitHubalbinowax/activescanplusplus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
api-security-testingdefensive-toolsexploitation+7
6697 days ago
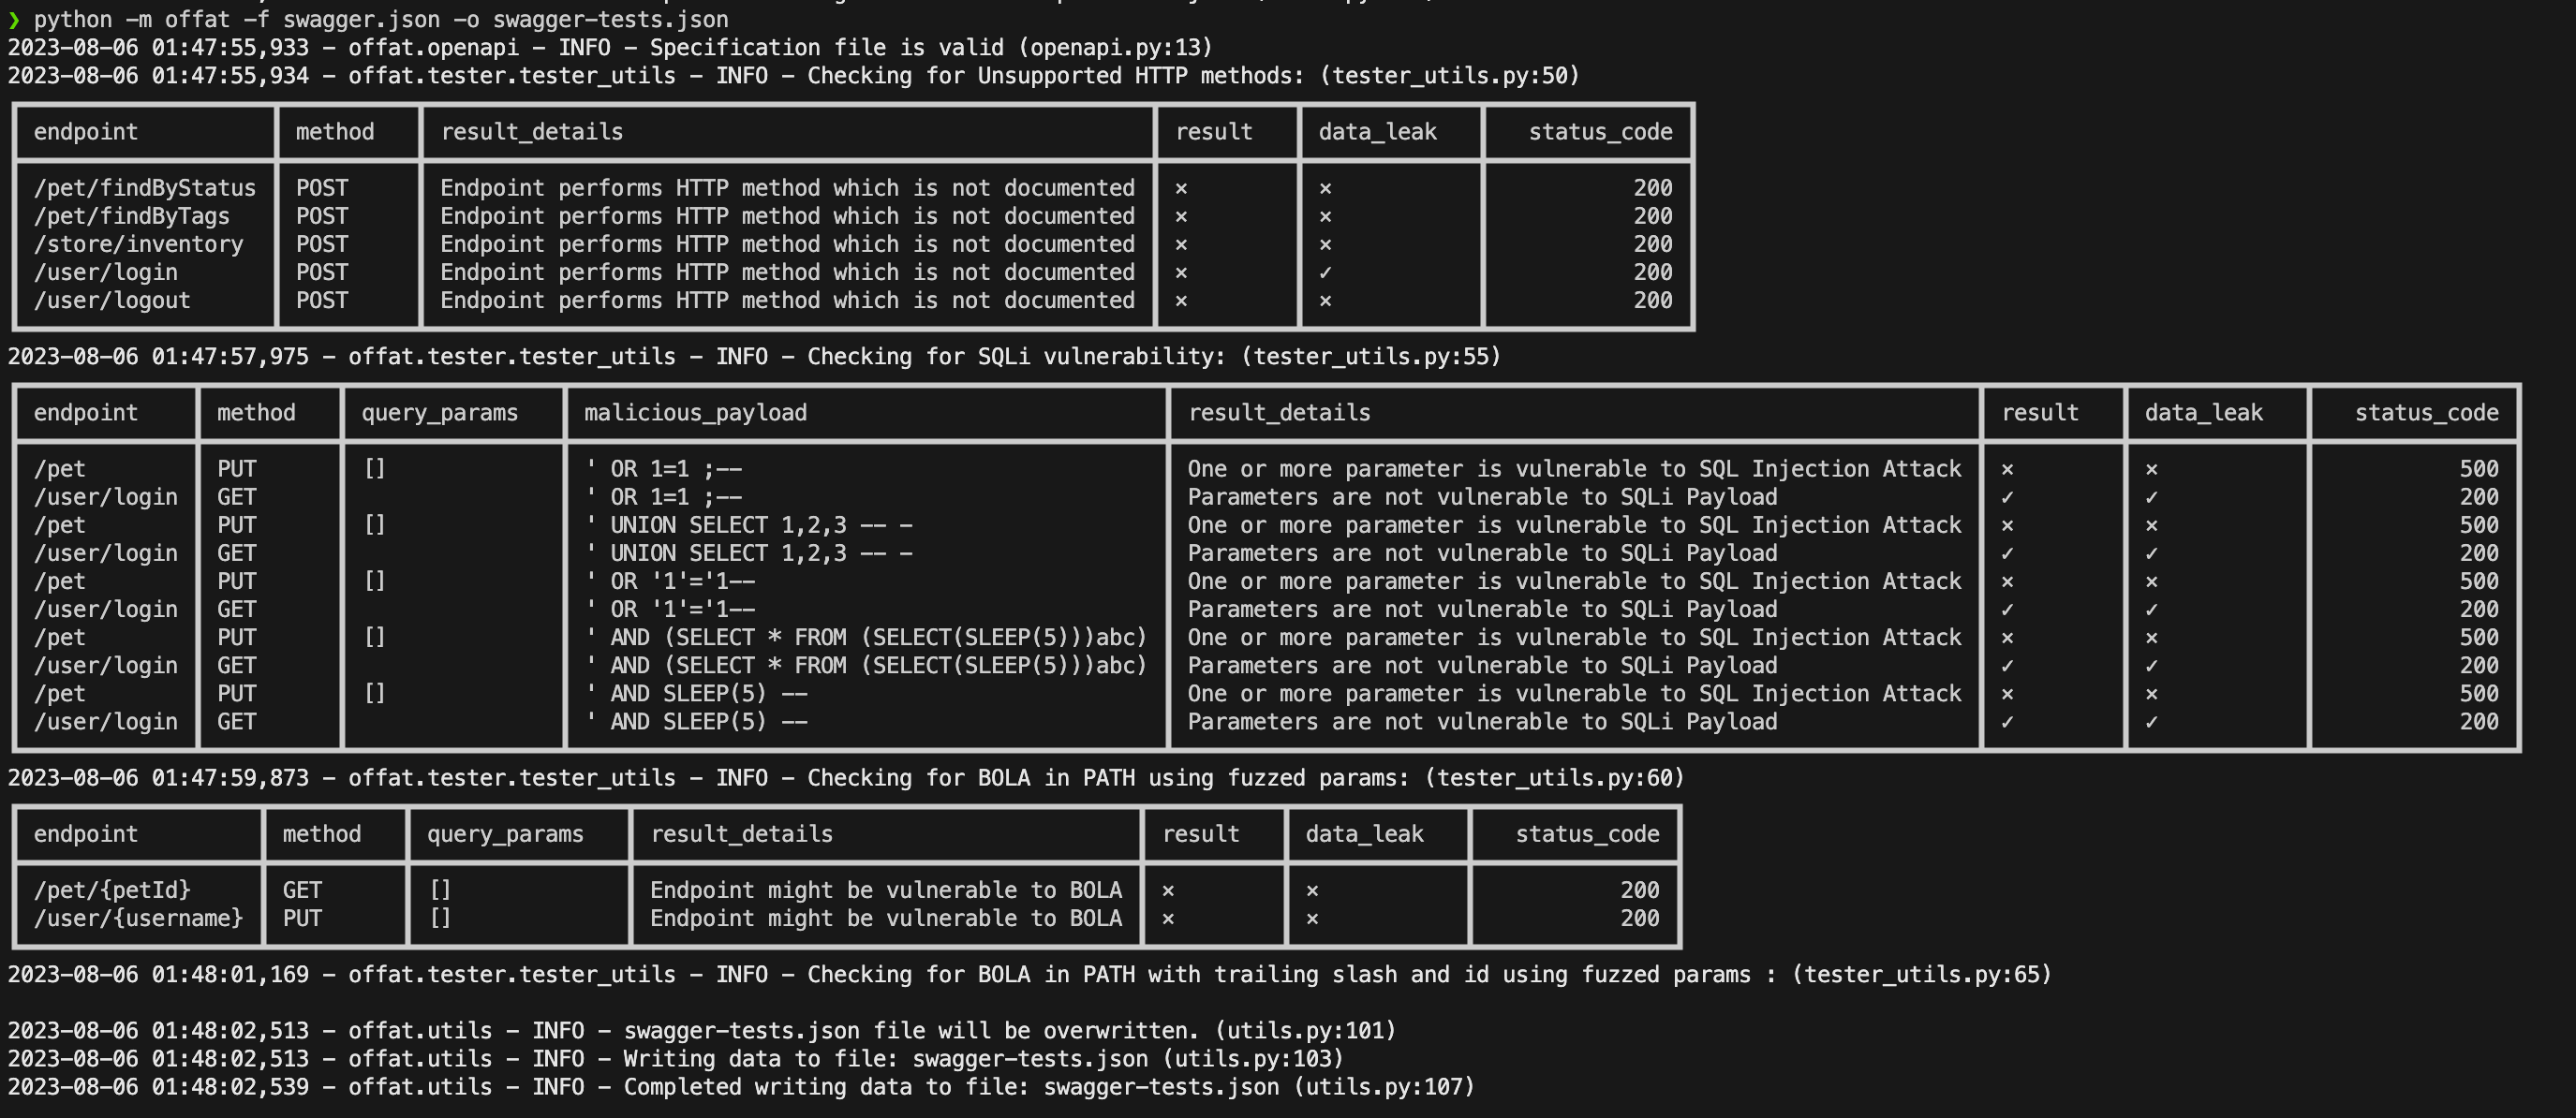
OFFAT preview

OFFAT

GitHubowasp/offat

Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…

api-securityapi-security-testingfuzzing+2
6774 days ago
BurpAPISecuritySuite preview

BurpAPISecuritySuite

GitHubteycir/burpapisecuritysuite

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
api-securityapi-security-testingfuzzing+4
3712 months ago
API-Wordlist preview

API-Wordlist

GitHubnet-hunter121/api-wordlist

Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.

api-security-testingcurated-resourcesfuzzing+3
2535 years ago
LLMMap preview

LLMMap

GitHubhellsender01/llmmap

Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.

ai-securityapi-security-testingdynamic-analysis-sandboxing+6
2057 months ago
reburp preview

reburp

GitHubforefy/reburp

A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI

ai-securityapi-security-testingfuzzing+7
1291 day ago
Http11Probe preview

Http11Probe

GitHubmda2av/http11probe

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…

api-security-testingfuzzingmisconfiguration+2
323 days ago
shadow-repeater preview

shadow-repeater

GitHubhackvertor/shadow-repeater

Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…

ai-securityapi-security-testingfuzzing+6
4311 months ago
Previous123Next